
Skip to content
Logo

Hackaday

  • Home
  • Blog
  • Hackaday.io
  • Contests
  • Submit
  • About

aac keys

1 Articles

Embedded RFID For Online Passwords

October 11, 2010 by Mike Szczys 33 Comments

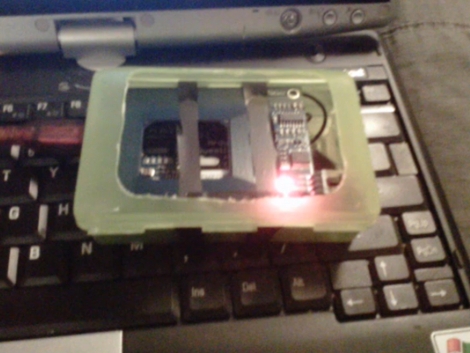
[Jair2K4] is using his unique RFID tag address as an online password. We’d bet that if you went far enough to get an implant in your hand you’d continually search for a reason to use it. Wanting to do more than just start his car with a wave of the hand, he built an interface module out of an Arduino and a Parallax RFID reader. Using a program called AAC Keys on Windows 7 he emulates a keyboard using the input from the Arduino. When it comes time to login he types his username and parks the cursor in the password box. By holding the RFID implant next the reader, the ID is dumped as the password, along with a newline (might be a carriage return, we’re not certain) character which submits the login. Take a look for yourself after the break.

On the one hand, nobody will be able to steal his tag as easily as they could steal one that is on a key ring. But we know RFID is rather notorious for a false sense of security. As long as you’re not using it for state secrets we think it’s a nice solution.

Update: After reading the comments on this feature, [Jair2K4] made some changes to his code. It now reads the tag and verifies it with stored data, then spits out whatever password you wish (making it easy to change passwords from time-to-time). He also added servo control to the sketch.


Continue reading “Embedded RFID For Online Passwords” →

Posted in Security HacksTagged aac keys, implant, login, password, rfid, windows 7

Search

Never miss a hack

Follow on facebook Follow on twitter Follow on youtube Follow on rss Contact us

Subscribe

If you missed it

  • The Sextant: Navigating The Old Way

    37 Comments
  • EV Batteries Are Proving Hardier Than Expected

    61 Comments
  • DeviceTree For Hackers: Intro

    21 Comments
  • Radon Active

    32 Comments
  • I Think We Should See Other SBCs

    76 Comments
More from this category

Our Columns

  • Hackaday Podcast Episode 394: Linux In Weird Places, Yet More Hidden SDRs, And A Supercon Wrapup

    1 Comment
  • This Week In Security: Four-Digit Patch Tuesday, SSH Exploited, GitBook Breach, Android GhostMap

    3 Comments
  • An INA219 board with a QWIIC connector and "female barrel jack to male barrel jack" cable soldered on. the qwiic end is plugged into the side of the Blepis PDA, with the screen showing a device found on the 0x40 address

    Just Use QWIIC Already

    20 Comments
  • FLOSS Weekly Episode 883: Telnet Broke Us

    3 Comments
  • CHIP 8: The Pong Game’s Afoot!

    8 Comments
More from this category

Search

Never miss a hack

Follow on facebook Follow on twitter Follow on youtube Follow on rss Contact us

Subscribe

If you missed it

  • The Sextant: Navigating The Old Way

    37 Comments
  • EV Batteries Are Proving Hardier Than Expected

    61 Comments
  • DeviceTree For Hackers: Intro

    21 Comments
  • Radon Active

    32 Comments
  • I Think We Should See Other SBCs

    76 Comments
More from this category

Categories

Our Columns

  • Hackaday Podcast Episode 394: Linux In Weird Places, Yet More Hidden SDRs, And A Supercon Wrapup

    1 Comment
  • This Week In Security: Four-Digit Patch Tuesday, SSH Exploited, GitBook Breach, Android GhostMap

    3 Comments
  • An INA219 board with a QWIIC connector and "female barrel jack to male barrel jack" cable soldered on. the qwiic end is plugged into the side of the Blepis PDA, with the screen showing a device found on the 0x40 address

    Just Use QWIIC Already

    20 Comments
  • FLOSS Weekly Episode 883: Telnet Broke Us

    3 Comments
  • CHIP 8: The Pong Game’s Afoot!

    8 Comments
More from this category

Recent comments

  • Senile Data Systems on Using A Toothbrush’s NFC Chip To Unlock A Computer
  • Gareth Davies on Keep That Old Radio Alive With An ESP32
  • RunnerPack on Borland C++ 2.0 Compiler Source Reconstructed
  • Pedro on Making CO₂ Sensors Fail Visibly, Not Silently
  • Hash on Baochip-1x: A Mostly-Open, 22nm SoC For High Assurance Applications
  • 110y6 on Hackaday Podcast Episode 394: Linux In Weird Places, Yet More Hidden SDRs, And A Supercon Wrapup
  • Peter on Making CO₂ Sensors Fail Visibly, Not Silently
  • Dani on NEMESIS Gives You Control Over Your Hyundai Head Unit
  • M on X Window System On The ESP32
  • Nerd Ralph on Drop-in Vintage CPU Replacements With The TranZPUter Project
Logo
  • Home
  • Blog
  • Hackaday.io
  • Video
  • Submit A Tip
  • About
  • Contact Us

Never miss a hack

Follow on facebook Follow on twitter Follow on youtube Follow on rss Contact us

Subscribe to Newsletter

Copyright © 2026 | Hackaday, Hack A Day, and the Skull and Wrenches Logo are Trademarks of Hackaday.com | Privacy Policy | Terms of Service | Digital Services Act | Do not sell or share my personal informationCookie Management
Powered by WordPress VIP
Loading Comments...







