This Week In Security: FBI Gets Hacked, Muse Vulnerable To ClickFix, Popular Rust Developers At Risk, And New Attacks Against RSA

The prolific ShinyHunters group has announced it used a zero-day vulnerability in Oracle PeopleSoft to exploit the FBI jobs website and gain access to the AWS GovCloud instances and dump 2 TB of employee data. GovCloud being a special, locked-down version of the Amazon Web Services cloud for US government users.

ShinyHunters has previously been involved in dozens of high-profile hacks and ransomware incidents.  Some of the highest-profile incidents include Jaguar-Land Rover, causing a measurable impact on the UK GDP, Grubhub, Carnival Cruise Lines, Rockstar Games, and multiple universities and educational institutions, casinos, and other government agencies.  ShinyHunters has also been credited with the hack of the Canvas educational program in the spring of 2026 where data including test results and chat logs of hundreds of millions of students, teachers, and staff was stolen.  ShinyHunters has generally been identified as an international group of criminals, often teenagers, who will demand a BitCoin ransom of several million US dollars, with the threat of the stolen data being leaked if the victims do not pay.

On May 15, 2026 the FBI released a bulletin on the activities of ShinyHunters, focusing on the Canvas educational hack.  In the report, the FBI said that the group uses “harassment strategies, sending threatening text messages and phone calls to victims and their family members”.  ShinyHunters says that this is not accurate, and that they will release the FBI employee data, including information of employees and their family members, if the agency does not retract the statements, telling The Register “I have been doing my very best to combat these allegations, and this is the best way to do it”.
Continue reading “This Week In Security: FBI Gets Hacked, Muse Vulnerable To ClickFix, Popular Rust Developers At Risk, And New Attacks Against RSA” →

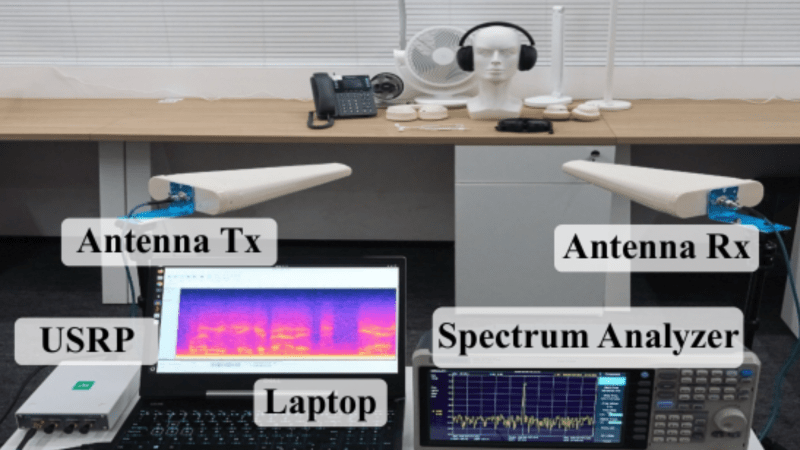
A laptop is shown set up on a desk next to a spectrum analyser, an SDR, and two antennas. The antennas are aimed toward assorted electronics, including headphones and a phone handset.

Reviving TEMPEST Attacks With An Injected Signal

TEMPEST attacks are often the most effective way to break air-gapped security: rather than directly accessing a computer, the attacker records the system’s unintended radio emissions and uses them to reconstruct its internal operations. This kind of attack was much more effective in the days of noisy, high-voltage CRT displays, and has gradually become less effective as electronics migrate to quieter, less powerful components. A group of researchers, however, has found that even modern electronics can become effective TEMPEST transmitters when irradiated with an RF signal.

The RF a device emits depends on the unintentional antennas in its internal structure. These are difficult to eliminate, and it’s usually not worth the effort; they’re usually small enough that they only effectively radiate at much higher frequencies than the electronics carry. The researchers’ technique, called InjectEave, radiated these electronics with a radio frequency tuned to their internal antennas, injecting that frequency into the circuit. Nonlinear electronic components, such as amplifiers, then mix the injected frequency with the internal signal, creating RF sidebands. This mixed signal then radiates out of the device and can be picked up and demodulated to recover the device’s internal signal.

Continue reading “Reviving TEMPEST Attacks With An Injected Signal” →

Laser Your Way Into Debug Mode On The RP2350

The RP2350 is actually a pretty secure chip, all things considered. It has secure boot, ARMv8’s TrustZone to split secure and non-secure execution, and you can permanently disable debug — the Pi Foundation even included glitch detection, meaning the traditional ‘zap the chip until it obeys’ technique is blocked. That’s why the [Ledger Donjon] security team went full Bond Villain and strapped everyone’s favourite fruit-flavoured microcontroller to a table with a slowly-approaching laser beam.

Continue reading “Laser Your Way Into Debug Mode On The RP2350” →

This Week In Security: Flock Cameras Are Old, Microsoft Patches Patches, And Researchers Attack SSH

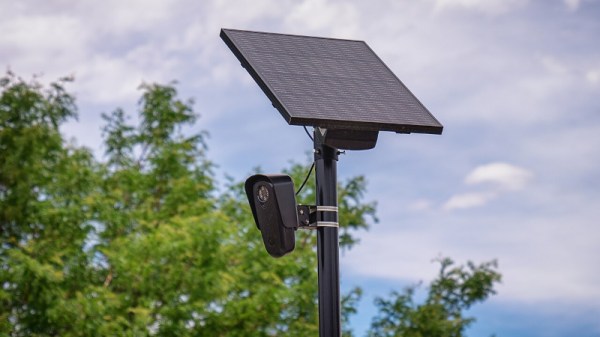
Leak site Distributed Denial of Secrets has released a dump of the filesystems of a Flock camera, and Micah Lee has published a dive into the contents.  Apparently the Flock security model did not include “angry citizens with a hacksaw in the middle of the night” in the physical security category.

The first thing Micah notes is that the Flock hardware runs Android 8.1 (for those not keeping track, the current Android release is Android 17 released in June 2026).  The version of Android running on the Flock camera was last patched in June of 2018, and the Linux kernel (3.18.71) is over nine years out of date, and the 3.18 series went end-of-life in 2019.

You might assume “wouldn’t an operating system this old have known vulnerabilities?”, and you’d be completely right.  Micah calls out two in particular, one in the Qualcomm GPU which allows any program to manipulate kernel memory and gain root (similar, yet simpler, than the spate of kernel vulnerabilities this year that allowed manipulating memory via the disk IO cache), and the “WrongZone” vulnerability which allows a process to escalate to root via socket handling errors.  You might also guess both of these have been patched, and again, you’d be right, in 2021 and 2018 respectively.

Digging deeper, Micah discovers that API keys with access into the Flock infrastructure appear to be hard-coded into the binaries.  Each camera appears to request credentials from an authentication server, using the MAC address of the camera.  After obtaining the credentials from an Okta Auth0 sign-in service, the Flock stores them, in plain text.

Also stored on the camera unencrypted are logs and position data:  The camera dumped to Distributed Denial of Secrets came from a suburb of Milwaukee. Continue reading “This Week In Security: Flock Cameras Are Old, Microsoft Patches Patches, And Researchers Attack SSH” →

Surveillance Camera Security? It’s Completely Flocked!

Surveillance cameras from Flock Safety have become a controversial privacy battleground, as the communities in which they are installed wake up to their sinister potential, and stories roll in of law enforcement professionals abusing their access. One has had its disk contents dumped, and we’ve been treated to some insights courtesy of [Micah Lee]. In short: their approach to security is deeply flawed.

It’s interesting to find that instead of a custom hardened OS, these devices run Android. Not just Android, but Android 8.1, a long out of support version originally released in 2017. This is is the year Flock Safety was founded, which may or may not be coincidental. Like any old version of a widely used operating system it has a host of known vulnerabilities, none of which are patched on this version.

The Android version is small beer compared to the revelation that they contain a hard-coded and very open-access API key that can be used by any mildly curious miscreant to reveal information from any Flock camera using its MAC address. One would hope that a product marketed for use by law enforcement might have paid attention to such a basic lapse, but it seems not. Whether or not this can be corrected by a software upgrade and the leaked key deactivated without turning off the network depends on whether thy can do upgrades tailored to specific devices, but either way we wouldn’t like to be the team tasked with fixing that one.

In a way it’s reassuring that the surveillance apparatus when it came was so incompetently managed, and we hope that these vulnerabilities will have moderated its effect. We’re sure more tasty discoveries will emerge as investigations proceed, and we’ve got the popcorn ready.

Image: Tony Webster, CC BY 2.0.

This Week In Security: It’s Patch Tuesday Again, TVs Spying, Supply Chain Worms Return, Prolonged Hack Impacts, Stolen IDs

Several times this summer, Microsoft’s Patch Tuesday, the monthly roundup of major security patches for Microsoft products, has included record-breaking numbers of security fixes. The August 2026 patch set actually seemed to catch up. Was this a sign of the bug apocalypse lessening? Ha, nope!

Brian Krebs at Krebs On Security once again brings his excellent roundup of Patch Tuesday events, with this months patch set absolutely crushing previous numbers with nearly 1,000 security fixes.

Two of the fixes are for zero-day vulnerabilities under active exploitation in the wild, both allowing privilege escalation on Windows. Privilege escalation bugs turn general vulnerabilities in applications and games into full administrator access to gain persistence and deploy ransomware, and generally make any vulnerability significantly worse.

Krebs also calls out a CVSS 9.8 (so close to a perfect 10!) vulnerability that allows remote code execution in the Windows shell with no user interaction and no authentication, a remotely exploitable DNS bug present since Windows Server 2012 and Windows 10 which will likely see exploitation in the wild soon, and over a hundred other bugs are ranked “Critical”.

How the sheer volume of vulnerabilities in this patch will fit with recent Microsoft recommendations that companies should apply the patches immediately remains to be seen. (Likely: not very well, depending on what new behavior and issues the fixes cause!)

Is Your LG TV Spying on You?

Gamers Nexus continues their trend of high-quality investigation, and they have posted another tremendous multi-hour investigatory video. This time Gamers Nexus focuses on the ecosystem of LG televisions and monitors.

It shouldn’t likely surprise many here that “smart” devices are usually more to the benefit of advertisers than consumers. Similarly, it shouldn’t be a surprise that a “smart” device harvests user data to sell to advertises. What may be surprising is the degree to which LG devices appear to collect data, how much data is sent even when collection is turned off, and how overt executives at the company are, with multiple executives making statements in pitches to advertisers that LG “owns the glass”, “owns the living room”, and is designed to correlate devices, inhabitants of the environment, and viewing habits so that ads can be served to the TV and mobile devices in the same room simultaneously.

With tracking enabled, the smart TV captures telemetry of what applications are used, as well as continually capturing the video displayed and reporting fingerprints to LG servers and ad partners. The screen content is tracked not only for TV, but for the HDMI inputs, including if the TV is used as a PC monitor. If voice control is enabled, the TV also records audio and analyzes it. The TV also continually scans the local network and nearby Wi-Fi networks, reporting all the devices it finds on the local network, including host name, MAC address, and sometimes software running depending on the MDNS advertisements. Near-by Wi-Fi networks are sufficient for very precise geolocation, so LG effectively knows the location of every customer, as well.

Continue reading “This Week In Security: It’s Patch Tuesday Again, TVs Spying, Supply Chain Worms Return, Prolonged Hack Impacts, Stolen IDs” →

This Week In Security: Baked-in Malware, Freezers Not Freezing, Zoom Snoops Clipboards, And AI Makes Things Worse, Faster

The AI platform ServiceNow which offers both hosted and on-premises versions just patched a trifecta of CVSS-10 vulnerabilities.

CVSS rankings are determined by the severity of a flaw, the ease of exploiting the bug, if authentication is required for exploitation, if the vulnerability exposes confidential data, and other criteria. A CVSS of 10 is as bad as it gets, and having three of them at once is certainly attention-getting. Of the three vulnerabilities fixed, one allowed unauthenticated modification of data in the hosted instance, a second allowed arbitrary code execution via the GraphQL interface, and the third allowed arbitrary SQL commands that could modify the database.

ServiceNow claims Adobe, Lenovo, Fedex, and Fujitsu among their high-profile customers. With luck, the vulnerabilities were patched before significant public exploitation could happen.

Router Malware

Previously in 2026 the US Government warned against embedded malware found in consumer routers, which may be linked to the FCC enacting bans against certification and import of foreign-made consumer devices. This week, the NVD (National Vulnerability Database) reported specific embedded malware in the Zbtlink and MoreQuick brands of devices.

Multiple versions of the firmware, for multiple lines of products, contain a backdoor service that uses unencrypted UDP to connect to a command and control (C2) service. The service, or anyone able to intercept the network traffic, since it’s unencrypted, can execute commands as root, allowing them to change configurations, open tunnels, or steal ISP credentials.

The malware is baked into the firmware, so removing it is impossible for most users: a factory reset wouldn’t do. In theory if third-party firmware like OpenWRT supports these devices, the hardware could be made safer with a custom install.

Given how commonly the same device is marketed under dozens of names, likely the same devices and firmware have yet to be identified under other brands. Continue reading “This Week In Security: Baked-in Malware, Freezers Not Freezing, Zoom Snoops Clipboards, And AI Makes Things Worse, Faster” →