
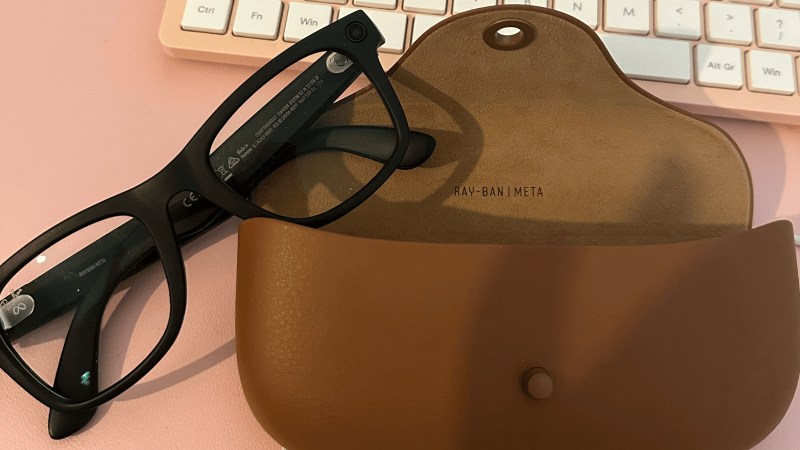
Meta’s Ray-Ban smart glasses have attracted plenty of controversy in the relatively short time they have been available, given their potential for covert and unvanted surveillance. But given the chance to examine one it would be churlish to pass up on the opportunity to test its defences. Which is what [p0pcycle] did when the opportunity came her way.
Given that hardware-probing was not an option, she followed the course of intercepting a software update. A little app decompilation led her to the full firmware, and she was able to probe its secrets. There’s a developer mode allowing applications to be written for the glasses, and it takes the form of an APK that loads the application code. An early firmware version would trust self-signed apps, so she could get arbitrary code on the device. From there after some trial and error she was able to expose a network listener, and there she had it.
The write-up is an interesting walkthrough of the process, and ends with her reporting it through their bug bounty program. So sadly the steps outlined above won’t work on newer firmwares, but we’re guessing that won’t stop others probing this device further.












Please be kind and respectful to help make the comments section excellent. (Comment Policy)