
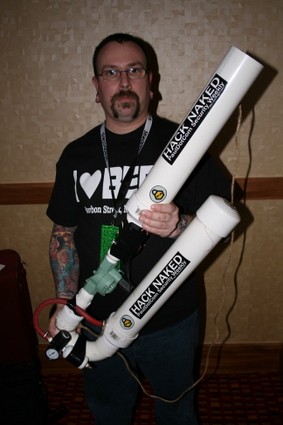
I caught up with [Larry] from pauldotcom.com and got a quick walk-through of his Shmooball gun. After several less successful attempts, this one worked pretty damn well and featured a distinctive sound that caused a notable glimmer of fear in the eyes of the speakers. *cough*[renderman]*cough*. Read on for the secrets of the Shmooball gun.
ShmooCon 2008: Hard Drive Highlights
Today wrapped up with a talk on recovering data from solid state hard drives by [Scott Moulton]. The talk focused on the differences in data storage between SSD and platter technology. I did come away with a few interesting bits of knowledge. In an effort to extend device life, flash based drives store changed data to a new location, leaving the old data intact until a garbage removal subroutine gets around to clearing it out. Probably the best way to recover data from them will be altering or replacing the controller chip so you can access old data.
Yesterday I caught an interesting talk on recovering passwords from drive images by [David Smith]. He found that he could take a system image, strip out all the strings that were stored by various programs and use them to build a dictionary of possible passwords. By limiting string lengths and matching for known password policies, he was able to further filter his dictionary for likely passwords.
Toaster Oven Reflow Controller
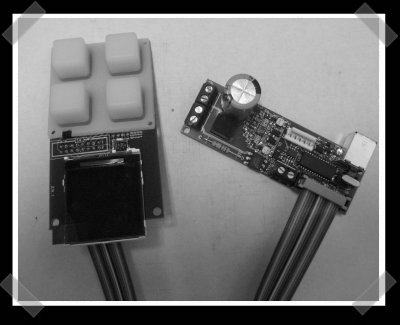
[Nathan] sent in his toaster oven reflow controller. He’s using a Triac to drive the heating elements, a thermocouple to monitor temperature and a PIC controller to run the show. I’m giving him extra points for style on the control pad. Hopefully he’ll have time to put out a complete write up when he’s got it finished. You can check out the project photos here.
ShmooCon 2008: Unauthorized Phishing Awareness Exercise
[Syn Phishus] presented a pretty interesting talk. At $former_company he prepared and executed a rogue internal exercise designed to heighten awareness of phishing scams. (That is, attempts to gather personal information from users with trickery.) After noting a certain lack of effort on the part of security policy implementation, he put together an official looking email, set up a simple phishing site that didn’t actually store any collected information and set loose the dogs of war. OK, he actually sent it to a select group within the company without warning anyone else ahead of time. He purposely didn’t store any of the results to protect the foolish, but he estimates that maybe 10% of the recipients fell for it.
ShmooCon 2008: Intercepting GSM Traffic
Back in August, [h1kari] presented an analysis of the A5 crypto spec used in GSM systems. Almost all GSM conversations in the US and Europe are encrypted using this standard. At the time they were still in the planning stages of building their rainbow table of shift register states. Today we heard an update on the progress. The whole space is 2^58 in size and would take a standard PC 33,235 years to calculate. Not being patient people they built a box containing 68 express card based FPGAs. Each one is capable of doing 72 billion operations per second. So far they’re one month into the 3 month process. Once the table is completed any person can crack a GSM conversation in 30 minutes using 1 FPGA and the 2TB table. They do have plans for building an optimal system that would be based on solid state drives and 16 FPGAs that should do the crack in just 30 seconds.
DIY 2.4ghz Spectrum Analyser
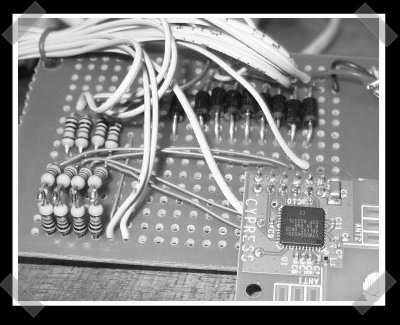
This project got some blog love last year, but it slipped past my radar. [jhecker] built a parallel port interfaced device based on a Cypress 2.4ghz transceiver module. The module is pretty complete, so as long as you can wield a soldering iron, you can pull this one off. The module is pretty cheap, so it could be just the thing for building your own signal detector.
[Ed Note, Stardate 2018: There seems to be some linkrot. Try this link instead.]
Shmoocon’s Coming
Just prepping up a bit before this spring’s Shmoocon. Things will definitely be colder this round, so bring your cold weather gear if don’t want to arrive in the form of a human popsicle. I’m a fan of Shmoo’s organization tactics. Running several single session talks keeps me from missing one great talk to attend another. [h1kari]’s GSM talk promises to be interesting. Not to mention VOIP penetration testing and solid state hard drive recovery. [Eliot] and I will see you there. Don’t worry, we’ll be reporting back for the guys that have to miss out this year









