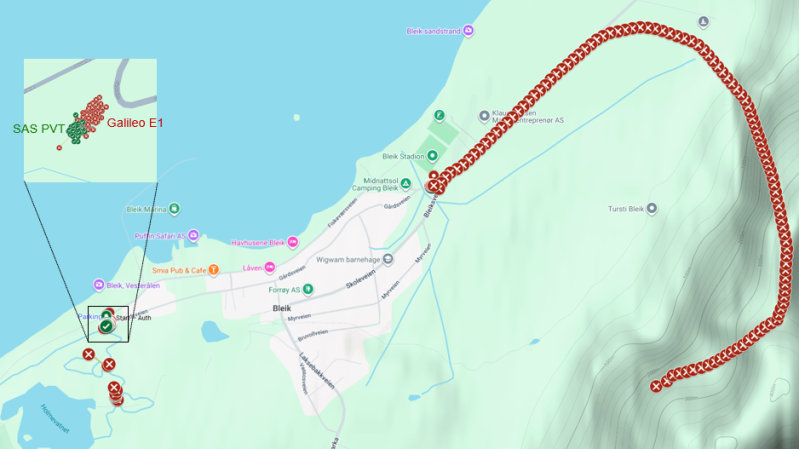
A digital map is shown with a series of red waypoints making a roughly C-shaped curve. A smaller group of green waypoints stays stationary near one of the corners of the map.

Defeating Satellite Spoofing With Galileo’s Encryption

Considering how important it is for everything from navigation to keeping clocks in sync, satellite navigation systems are surprisingly vulnerable to a variety of attacks, ranging from simple jamming to more sophisticated spoofing attacks. This may be changing, though, as Galileo, Europe’s GNSS, recently demonstrated its first cryptographically-secured position fix under spoofing conditions.

Most GNSS systems, including GPS, have no verification measures to keep an adversary from transmitting a false signal at a higher power and hijacking a receiver; since GNSS signals are extremely weak by the time they reach the ground, this presents no great difficulty to a moderately well-equipped attacker.

Galileo’s Signal Authentication System (SAS) aims to fix this. The Galileo ground station pre-selects signal spreading codes, which it then encrypts with a regularly-changing secret key and publishes. A receiver which anticipates needing a verified signal can then download these encrypted codes ahead of time and store them. Galileo satellites then transmit on the E6-C pilot signal, and the receiver records the signal. After transmitting a message block, it then transmits the decryption key on a separate signal, which the receiver uses to recover the spreading codes. The receiver then correlates these spreading codes with the recorded signal to find the satellite’s pseudorange.

It’s a rather complicated system, but it works: earlier this month in Andøya, Norway, the annual Jammertest GNSS testing event took place. For one week, a wide range of organizations tested the resilience of their GNSS systems against various attacks, including jamming, delayed retransmission, and spoofing. Using five Galileo satellites, the European Space Agency was able to obtain a stable lock on their receiver even during spoofing.

In principle, this method could be extended to other GNSS systems. There’s certainly motivation to do so; very large-scale attacks have been demonstrated recently.
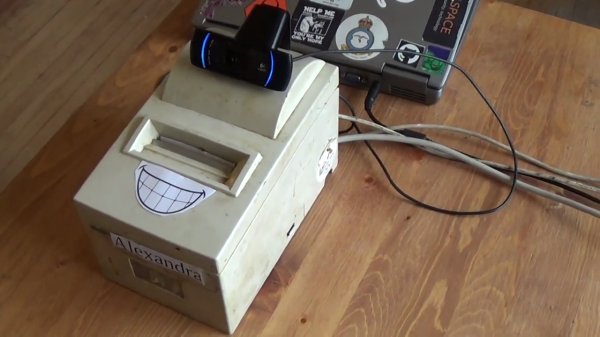
Cobbled together proof-of-concept vaccination verification system, showing a dot-matrix receipt printer, a webcam for QR code scanning, and an old laptop running the software

Manitoban Makes Open Software Demo Of Proprietary Vaccine Verification Systems

[Mark Jenkins] wasn’t impressed with the Covid 19 vaccination verification systems that restaurants in Manitoba are required to use. Patrons must present a QR code, which must be verified by a mobile app available only from Apple or Google. With help from his local hackerspace, he came up with a bash script solution requiring only kilobytes vs the 50 MB of the mobile apps. [Mark] isn’t pleased with the exclusivity of the apps availability and the lack of an open API. His concern isn’t entirely theoretical, either — Google mysteriously pulled their app from the Play Store for over a week.

The interim result, shown in the video below, is a demonstration system called Alexandra. It consists of a receipt printer, a webcam being used as a QR scanner, and a 2005-era laptop running the script. This is merely a proof of concept, as [Mark] clearly notes. There is still some work to be done — for example, the method used to authenticate with the Google server is transient. But eventually [Mark] hopes to have a free software alternative soon, suitable for restaurant owners to use in their establishments.

What kinds of vaccination verifications systems, if any, are used in your part of the world? Is the system open or proprietary? Let us know in the comments below.

Continue reading “Manitoban Makes Open Software Demo Of Proprietary Vaccine Verification Systems” →

search-console

Fooling Google Search Console With Tricky PHP

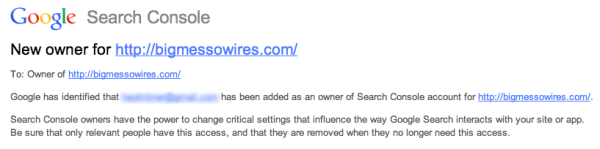
When [Steve] received a notice from Google that a new owner had been added to his Google Search Console account, he knew something was wrong. He hadn’t added anyone to his account. At first he thought it might be a clever phishing tactic. Maybe the email was trying to get him to click a malicious link. Upon further investigation, he discovered that it was legitimate. Some strange email address had been added to his account. How did this happen?

When you want to add a website to Google’s services, they require that you prove that you own the actual website as a security precaution. One method to provide proof is by uploading or creating an HTML file to your website with some specific text inside. In this case, the file needed to be called “google1a74e5bf969ded17.html” and it needed to contain the string “google-site-verification: googlea174e5bf969ded17.html”.

[Steve] logged into his web server and looked in the website directory but he couldn’t find the verification file. Out of curiosity, he tried visiting the web page anyways and was surprised to find that it worked. After some experimentation, [Steve] learned that if he tried to load any web page that looked like “googleNNNNNNN.html”, he would be presented with the corresponding verification code of “google-site-verification: googleNNNNNNNN.html”. Something was automatically generating these pages.

After further investigation, [Steve] found that some malicious PHP code had been added to his website’s index.php page. Unfortunately the code was obfuscated, so he couldn’t determine exactly what was happening. After removing the new code from the index.php file, [Steve] was able to remove the hacker’s email address from [Steve’s] Google account.

This is a very interesting hack, because not only did it allow this one hacker to add himself to [Steve’s] Google account, but it would also have allowed anyone else to do the same thing. This is because each new hacker would have been able to fool Google’s servers into thinking that they had uploaded the verification file thanks to the malicious PHP code. It makes us think that perhaps Google’s verification system should use a separate randomized string inside of the verification file. Perhaps one that can’t be guessed or calculated based on known variables such as the file name.