Defcon Day 1 – Lost In Translation – Christian Grothoff

Steganography is the art of hiding things in plain sight. When done correctly an observer shouldn’t be able to tell that there is a hidden message as opposed to cryptography where it is obvious that something is hidden. To do this using text you usually need a large piece of source material; say all of the works of Shakespeare. Since these works are known to most people steg can usually be broken using statistical analysis.

Christian’s solution is to use machine translated (MT) texts as the source material. It is hard to make a computer generate consistant semantically and rhetorically correct texts that mimic the original is very difficult. The technique presented here uses MT texts because translation errors are expected and common.

Continue reading “Defcon Day 1 – Lost In Translation – Christian Grothoff” →

Defcon Day 1 – My Next Big Project – Philip R. Zimmerman

Well the two big stories this week are the CISCO router problem and Philip “PGP” Zimmerman’s new project. Originally unveiled at Black Hat earlier this week his new crypted VOIP looks really interesting. Well it would have looked interesting if the demo had worked; eventually his partner just called on a cellphone. The goal is to return the “security” of land lines to the world of VOIP.

The app is based on the shtoom project (open source VOIP written in Python) and the crypto is strapped ontop. A nice feature of the protocol is hashing part of the previous conversation’s key into the current conversation. If you and the other person read the hash aloud and they match it means that this conversation and every previous one has been fully secure.

He’s shopping the project around to venture capital right now to make a commercial product written in C. The source will still be free though.

Most people have left by now, but they were able to get the demo going. It is funny to hear a secure call blasted over loud speakers. He’s got a switch in the software to switch off the packet decryption so you can hear what the wiretap hears

Defcon Day 1 – The Law, The Swag

swag-defcon01

Hey! The swag is already out and in full force. Defcon is great, but beware about photos, here’s what our man with the master plan Jason C. says:

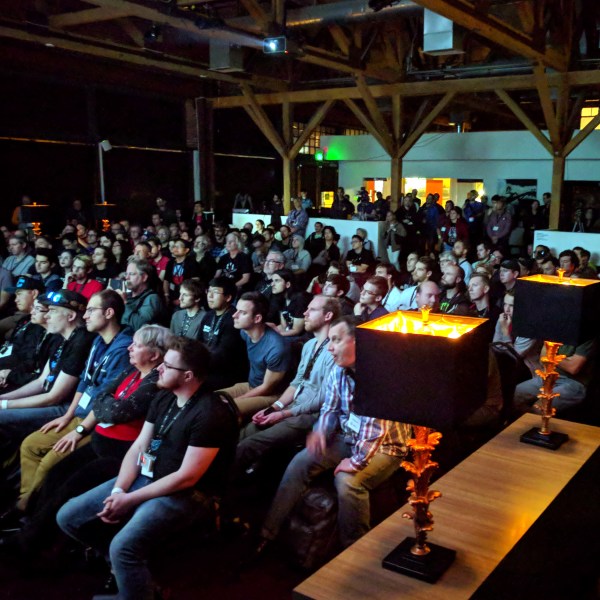
“We’re 10 minutes into the event and the first privacy/freedom of speech debate has started. The topic was, of course, photos. An organizer went off a long tirade about not taking pictures of the speakers or audience without their permission and that the press would have their film taken if they did. They did says that you could take pictures of the backs of people’s heads without permission. So, since many of you have always wanted to see the backs of 500 sweaty nerds in a tent

Wardriving Box

wrap box

Defcon isn’t the only hacker gathering starting up right now. If you are at What The Hack in the Netherlands you might catch a glimpse of this project. It’s a wardriving box based on the WRAP. The platform is similar to the Soekris boards and the site actually describes both. It isn’t a complete how to, but you’ll have a good idea of what’s in store for you if you want to attempt this.

[thanks ian]

Continue reading “Wardriving Box” →