The Weirdest Video Games Were Hacks

We were looking into the marvelous recent project by [Throaty Mumbo] to recreate and reimagine the forgotten world of VHS-tape-based video games. Wait, what? Yes, back in the day, when computer graphics were more primitive, there were attempts to mix the gameplay of video games with the graphics from a video cassette. Take the Action Max system. It worked with a light-gun that pointed at the screen while the video played, and you tried to shoot at things as they flew by. Think Duck Hunt, but in glorious VHS video quality with cheesy acting, and the same gameplay loop every time, because it’s on the tape.

The unreleased Control-Vision VHS gaming system, co-developed with none other than Steve Wozniak, took the idea a little further and ran simultaneous sub-videos, and your actions would choose which of the sub-tracks would play at any given time. This let them do things like switch between videos depending on whether you caught the bad guys or missed them entirely, for instance.

These games came in the late 1980s, though, and they were all derivatives of the seminal Dragon’s Lair, which is probably the least fun video game I’ve ever had the chance to play, but among the most entertaining in a weird way. Instead of a linear VHS tape, Dragon’s Lair, and the later but equally unplayable Space Ace, were based on the then-new video disc technology that could swap between entirely different tracks almost seamlessly.
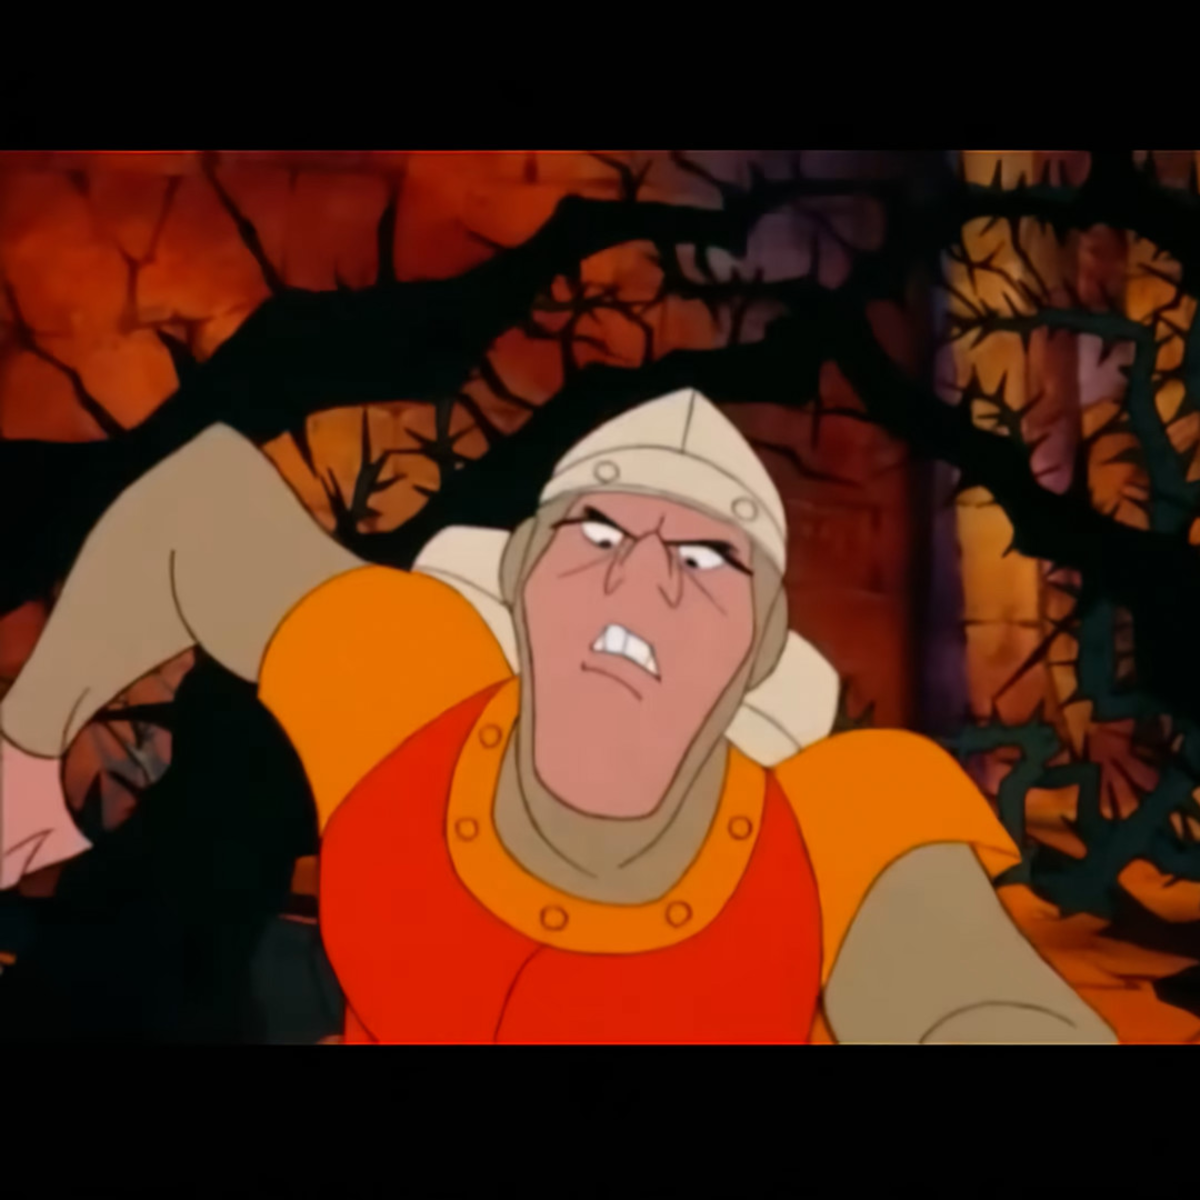
“Almost” is the key word here, though. Although the animations were absolutely marvelously cartoony, and looked stunning in an arcade up against video games of the time, there was a significant fraction of a second of delay between commanding an action with the joystick and the machine swapping up to the correct track. There were a couple of sections where back-to-back actions were necessary, and the challenge was to work around the game’s exact track-swapping-glitch time. As good as they looked, the gameplay was no fun.

But the game was influential, as evidenced by its VHS-based clones. If you’d like to give it a try, you’ll not be surprised to hear that there’s an emulator for Dragon’s Lair and its spin-off games.

What do all of these have to do with each other? We love how these games took a current technology – in this case video discs or video tapes – and tried to make it do something else: These games were all hacks. If you look at them in that light, maybe you can look past the horrible acting in Night Trap or the frustrating glitches in Dragon’s Lair. (Or maybe not. Give me Robotron: 2084 any day.)
This Week In Security: BugTraq, AI Hacks, And Being Dumb On Planes

After a multi-year hiatus, the venerable BugTraq mailing list is back!

For decades, BugTraq was the place where vulnerabilities were disclosed, from the early days when nearly all vendors viewed all security research as a hostile force, through to the modern era of working with vendors to coordinate disclosing bugs. With the rise of bug bounty programs and other social changes, the mailing list slowly died: what started in 1993 ended in 2021 is returning. The new maintainer, Jonathan Brossard, says in his announcement “The mission is unchanged: full disclosure, researcher-first, no corporate filter.”

Don’t Be Dumb on Planes

In the unlikely event anyone here needs to be told: Don’t do dumb things on planes.

It seems that someone coming home from from the DEF CON hacker conference in Las Vegas decided to mess with the in-plane WiFi, and is likely now in the “find out” phase of doing something dumb. There hasn’t been any public followup beyond the original reports: a passenger on a Delta flight leaving Las Vegas brought up a fake WiFi hotspot named “Delta WiFi FAST” to trick other passengers into connecting, and attempted to disable the in-flight WiFi using a denial of service attack.

Continue reading “This Week In Security: BugTraq, AI Hacks, And Being Dumb On Planes” →

Hackaday Podcast Episode 380: 3D Printing The Rainbow, IR And IP Camera Hacks, And Americium 241 On The Loose

Elliot Williams and Al Williams got together to compare notes on the most interesting posts this week on the site. As usual, there are just too many choices, so you’ll have to settle for just the few that can fit in a podcast. The guys were excited about 3D printing — both FDM and SLA — as well as a few camera projects. Ever wanted your own starship? They do, too, and you’ll hear about it along with portable radar and more.

Want to make flexible PCBs? Fill up a carbon dioxide tank? Or play Doom via regular expressions? Tune in, and you’ll find out about those stories and more.

Follow along with the links, and as always, tell us what you think about this episode in the comments! Better still, drop us a note in the mailbag, and you might hear your question on a future episode. You can record audio or send us a message, and one of the hosts will read it on your behalf.

Direct download in IR color-corrected DRM-free MP3.

Continue reading “Hackaday Podcast Episode 380: 3D Printing The Rainbow, IR And IP Camera Hacks, And Americium 241 On The Loose” →

Peripherals Hacks

Custom peripheral projects are among the most rewarding. Especially if you’re like me and you sit at the computer eight hours per day, anything that you can use on a daily basis is super satisfying. This topic of DIY peripherals came up on the podcast while chatting with Kristina, who is no stranger to odd inputs herself.

We were talking about a trackball that had been modified to read twisting gestures, by a clever hijacking of the twin mouse sensors inside. If you do a lot of 3D modeling, you can absolutely get by with just a mouse and shift-ctrl-alt as modifiers, but it’s so much more immediate to use a dedicated 3D input device. (I’ve got an ancient serial Space Mouse just under my left hand as I type this.)

My old favorite, which I haven’t used in ages, is the guts of a 5” hard-drive platter stack that I turned into a scroll wheel. Unfortunately, I don’t have space for it on my desk anymore, but it was just so pleasing to scroll through a document with something that had some real chonky momentum to it.

And it’s easier than ever to make your own. The classic blocky macropad is a great introduction, but as long as you’re doing the design yourself, why not extend it, or at least make it fit your hand? Or take your flights of fancy even further away from the mainstream. Consider the Bluetooth mouse ring, for instance.

Point is, the software side of almost any peripheral device you can imagine is sorted out already, and interfacing with the hardware is equally simple. Peripheral hacks have such a low barrier to entry, but afford so many creative hardware possibilities. And nothing says “Jedi” like building your own lightsaber.

This Week In Security: Annoyed Researchers, Dangling DNS, And Hacks That Could Have Been Worse

The author of the BlueHammer exploit, which was released earlier this month and addressed in the last Patch Tuesday, continues to be annoyed with the responses from the Microsoft security research and vulnerability response team, and has released another Windows zero-day attack against Windows Defender.

The RedSun exploit targets a logic and timing error in Windows Defender, convincing it to install the target file in the system, instead of quarantining the file and protecting the system. Not, generally, what you would hope would happen.

Since the RedSun attack requires local access in the first place, it seems unlikely Microsoft will release an out-of-sequence patch for it, however with public code available, we can probably expect to see malware leveraging it to establish higher permissions on an infected system.

Releasing exploits out of spite feels like a return to the late 1990s, and I almost don’t hate it.

University Domains Hijacked

Reported in Bleeping Computer, a group tracked as “Hazy Hawk” has been hijacking unmaintained DNS records of universities and government institutions to serve ad click spam.

The attack seems simple and doesn’t even require compromising the actual institution, using dangling DNS “CNAME” records. A “CNAME” entry in DNS acts essentially as an alias, pointing one domain name at another, which can be used to provide content from an official domain that is hosted on a cloud service where the IP address of the service might change.

A DNS “A” (or “AAAA” if you speak IPv6) record points a hostname – like “foo.example.com” – to an IP address – like “1.1.1.1”. A “CNAME” record points a hostname to another hostname, like “foo.some_cloud_host.com”. Scanning “high value” domains (like Ivy League universities) for “CNAME” records which point to expired domains (or domains on cloud hosted providers which no longer exist) lets anyone able to register that domain (or create an account with the proper naming scheme on the cloud host) to post any content they wish, and still appear to be the original name.

At least 30 educational institutions have been impacted, along with several government agencies including the CDC.

Continue reading “This Week In Security: Annoyed Researchers, Dangling DNS, And Hacks That Could Have Been Worse” →

When Clever Hardware Hacks Bite Back: A Password Keeper Device Autopsy

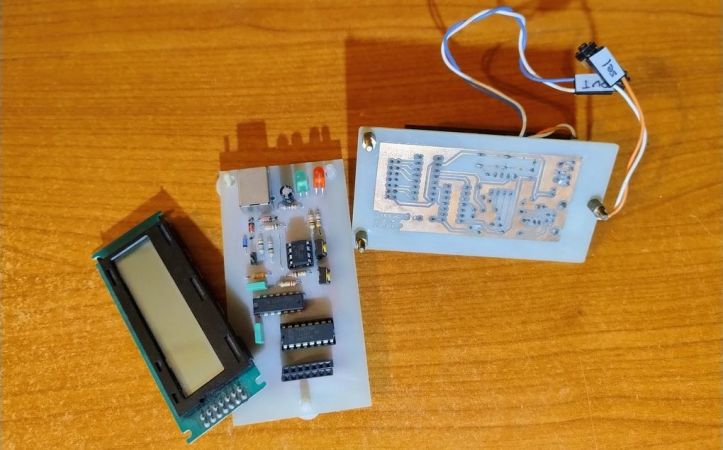
Sometimes you have this project idea in your mind that seems so simple and straightforward, and which feels just so right that you have to roll with it. Then, years later you stumble across the sad remnants of the tearful saga and the dismal failure that it portrays. Do you put it away again, like an unpleasant memory, or write it up in an article, as a tearful confession of past sins? After some coaxing by a friend, [Alessandro] worked up the courage to detail how he set about making a hardware-only password keeper, and why it failed.

The idea was so simple: the device would pretend to be a keyboard and type the passwords for you. This is not that unusual, as hardware devices like the Mooltipass do something similar. Even better, it’d be constructed only out of parts lying around, including an ATtiny85 and an HD44780 display, with bit-banged USB connectivity.

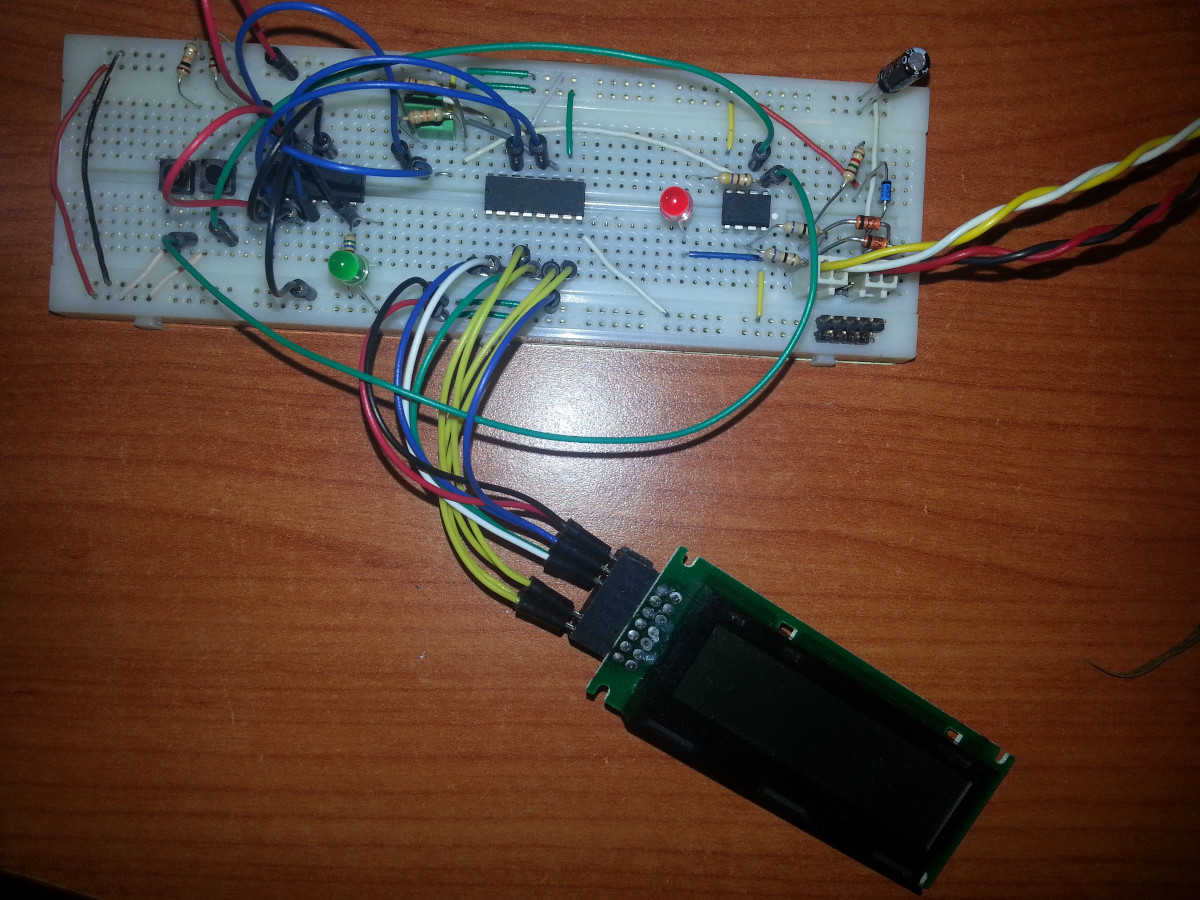
Prototyping the hardware on a breadboard.

Overcoming the challenge of driving the LC display with one pin on the MCU required adding a 74HC595 demultiplexer and careful timing, which sort of worked when the stars aligned just right. Good enough, but what about adding new passwords?

This is where things quickly skidded off the tracks in the most slapstick way possible, as [Alessandro] solved the problem of USB keyboard HID devices being technically ‘output-only’, by abusing the indicator statuses for Caps Lock, Num Lock, and Scroll Lock. By driving these from the host PC in just the right way you can use them as a sort of serial protocol. This incidentally turned out to be the most reliable part of the project.

Where the project finally tripped and fell down the proverbial flight of stairs was when it came to making the bit-banged USB work reliably. As it turns out, USB is very unforgiving with its timing unlike PS/2, making for an infuriating user experience. After tossing the prototype hardware into a box, this is where the project gathered dust for the past years.

If you want to give it a try yourself, maybe using an MCU that has more GPIO and perhaps even a USB hardware peripheral like the STM32F103, ESP32-S3 or something fruit-flavored, you can take a gander at the project files in the GitHub repository.

We’re always happy to see projects that (ab)use the Lock status indicators, it’s always been one of our favorite keyboard hacks.

Toybox Tractor: Plywood, Lathe Hacks, And 350W Of Fun

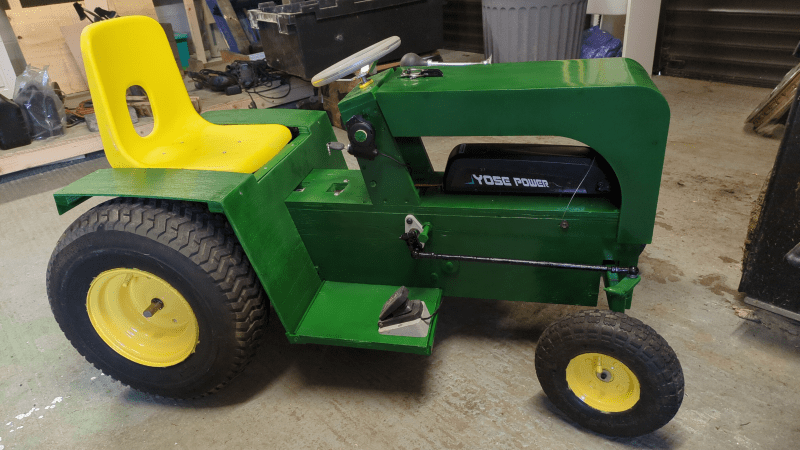
When you think of a toy tractor, what probably comes to mind is something with fairly simple lines, maybe the iconic yellow and green, big rear tires, small front ones. Well, that’s exactly what [James] built, with simple, clean lines and a sturdy build that will hold up to driving around off-road in the garden. This Tractor is a great build, combining CAD, metal and wood work, some 3D printing, and electronics.

Starting at the power plant for the build, [James] went with a 350W DC motor powered by a 36V Li-ion battery from an e-bike. The motor turns a solid rear axle he made on a mini-lathe, connected to a set of riding lawn mower wheels. The mini-lathe spindle bore was too small to accommodate the shaft, and the lathe was not long enough to use the tailstock, so [James] had to get creative, using a vice and a piece of wood to make a stand–in tailstock, allowing him to turn this custom rear axle. The signature smoothly curved bonnet was made possible with plywood and body filler, rather than the sheet metal found on full-sized tractors. In fact, most of the build’s frame used plywood, giving it plenty of strength and, once painted, helping give it the appearance of a toy pulled out of a toybox.

This build had a bit of many domains in it, and all combined into a fantastic final result that no doubt will bring a smile to any face that gets to take the Tractor for a ride. Thanks [James] for documenting your build process, the hacks needed to pull off the tough bits along the way in making this fun toy. If you found this fun, be sure to check out another tractor related project.