Laptop Containing 33,000 Clear Users Information Stolen

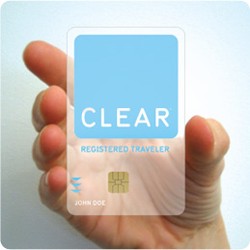
Security 101: Never put unencrypted sensitive information on a laptop and expect that it’s safe. Especially if you are the TSA. Recently, the TSA announced that a laptop was stolen from San Francisco International Airport containing “pre-enrollment records of approximately 33,000 customers” for the Clear Trusted Traveler Program. For $100 per year, the Clear Program enables travelers to get through airport security faster by showing TSA officers their Clear Registered Traveler Card and going through a special security line. While this program has no doubt saved many people valuable time getting through security, there are about 33,000 people who are now asking the question “Who has my personal information?”

[via schneier on security]

Edit: It looks like the laptop was found, however it is still unclear if the information on the laptop was compromised. In addition to basic personal information (Name, Address, Birthday, etc.), the laptop also contained drivers license, passport, green card information about clear users. You can check out the story here. Credits to [AudioCraz-Z] for the link.
DIY Kidney Machine Saves Girl


When the tool you need doesn’t exist, you must make one. That’s exactly what [Dr. Malcolm Coulthard] and kidney nurse [Jean Crosier] from Newcastle’s Royal Victoria Infirmary did two years ago.

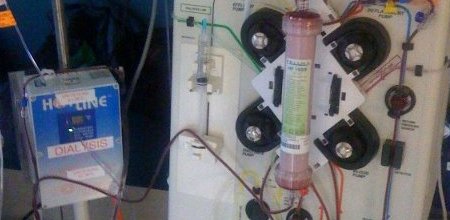
When a baby too small for the regular dialysis machine (similar to the one pictured above) needed help after her kidneys failed, the kind doctor designed and built a smaller version of the machine in his garage, then used it to save six-pound baby Millie Kelly’s life. Since then the machine has continued to be used in similar emergency situations.

[Photo: NomadicEntrepreneur]

The GIFAR Image Vulnerability


Researchers at NGS Software have come up with a method to embed malicious code into a picture. When viewed, the picture could send the attacker the credentials of the viewer. Social sites like Facebook and Myspace are particularly at risk, but the researchers say that any site which includes log ins and user uploaded pictures could be vulnerable. This even includes some bank sites.

The attack is simply a mashup of a GIF picture and a JAR (Java applet). The malicious JAR is compiled and then combined with information from a GIF. The GIF part fools the browser into opening it as a picture and trusting the content. The reality is, the Java VM recognizes the JAR part and automatically runs it.

The researchers claim that there are multiple ways to deal with this vulnerability. Sun could restrict their Virtual Machine or web applications could continually check and filter these hybrid files, but they say it really needs to be addressed as an issue of browser security. They think that it is not only pictures at risk, but nearly all browser content.
More details on how to create these GIFARs will be presented at this week’s Black Hat conference in Las Vegas.

Make: Television

Make Magazine, famous for the Maker Faire, among other things, has announced a new project called Make: television. The show will be coming to public television stations throughout the USA starting early 2009. The big news is that you can submit 2 minute long videos of your projects to be included in the show’s Maker Channel segment. The bigger news is that if your video is selected, they’ll send you a $50 gift certificate from the Maker Shed and a free year of Make Magazine.

Getting Around The Great Firewall Of China

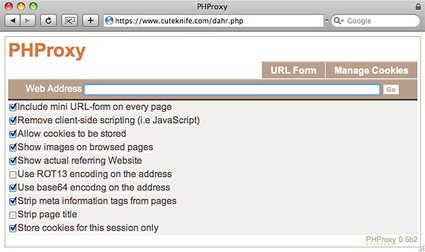
[Zach Honig] is a photographer in Beijing covering the Olympics. In light of recent allegations of the Chinese government installing monitoring software and hardware in foreign-owned hotels, the necessity of protecting one’s information has become vital and urgent, especially for journalists and photographers. [Honig] provides some suggestions for circumventing the infamous Great Firewall of China; surfing the internet through a secure VPN connection and using a proxy such as PHProxy will allow users to visit websites that have been banned within China. Such simple tricks could mean the difference between not being able to find necessary information, and the ability to surf the internet freely and openly.

[via Digg]

More Defcon 16 Events Announced


Defcon keeps announcing more and more interesting events for next week’s conference. A free workshop is planned for the soon to be released DAVIX live CD. DAVIX is a collection of tools for data analysis and visualization. They’ll be running through a few example packet dumps to demonstrate how the tools can help you make sense of it all. [Thomas Wilhelm] will be driving out from Colorado Springs in his Mobile Hacker Space. He’s giving a talk Sunday, but will be giving presentations a few hours every day at the van. Some researchers from NIST will be setting up a four node quantum network and demonstrating some of the possible vulnerabilities in the system. Finally, as part of an EFF fundraiser, Defcon will feature a Firearms Training Simulator. Conference attendees will participate in drills designed to improve their speed, accuracy, and decision making skills.

Iphone-dev Team Progress Update


The iphone-dev team hasn’t been resting on their laurels since releasing the iPhone Pwnage Tool 2.0 nearly two weeks ago and decided to update everyone on their progress. Despite the iPhone 2.0 jailbreak, there still isn’t a way to unlock a 3G phone. They’ve managed to do other things like downgrade a 3G to an older baseband firmware, which demonstrates their ability to bypass security checks and run unsigned code on the baseband. A nice side effect of all the downgrade work is that they’ve perfected the percautions they take to prevent bricking. The team has been following threads about using SIM proxy devices for unlocks as well, but concluded that the devices are a kludge at best and reliability can vary wildly depending on the phone’s location. They also pointed out the fine work that RiP Dev has been doing on Installer 4 which will help you install software that isn’t from the AppStore.