This Week In Security: Four-Digit Patch Tuesday, SSH Exploited, GitBook Breach, Android GhostMap

It’s the second Tuesday of the month, and that means another Microsoft Patch Tuesday. The new normal is that the numbers are hard to believe. Brian Krebs reports that this month’s release fixes nearly 1,100 vulnerabilities, 63 of them rated critical, and over 500 that let an attacker elevate their privileges. Only one is reported as actively exploited: CVE-2026-124194, a spoofing bug in Outlook. Microsoft has now shipped more than 5,100 security fixes this year, after more than 1,400 last month, compared to an average of around 100 a month last year. Obviously AI tools get the credit for the volume of bugs fixed, but also of course for the volume of bugs found.

Everyone else is busy too. Apple pushed out-of-cycle updates for at least nine vulnerabilities across its operating systems, including an iMessage flaw which could let a remote attacker join a group chat and read its messages, and backported the fixes to iOS 18. Chrome 157 fixes CVE-2026-125350, another Chrome zero-day, a week after a Chrome release which fixed more than 200 bugs, Firefox 160 fixes almost 100 CVEs, and Adobe fixed more than 110.

Also since last week, zlib 1.4 shipped with more than a dozen security fixes, eight more vulnerabilities were disclosed in the X.Org server and XWayland, and Microsoft’s own Azure Linux update lists more than 470 CVEs fixed across the open source packages it ships. And for a perfect encapsulation of 2026, last month’s Patch Tuesday included a remote code execution bug in Windows Paint (CVE-2026-83844), though its description admits the code runs locally. So now I guess you can pop Calc through Paint? Does this count as a win?

Despite the absolute firehose of vulnerabilities, the Krebs article notices that of the roughly 95,000 CVEs assigned this year, only around 200 made it into the CISA list of known expoited vulnerabilities (KEV). If you have to pick and choose which updates are the most critical, start there.

Continue reading “This Week In Security: Four-Digit Patch Tuesday, SSH Exploited, GitBook Breach, Android GhostMap” →

DeviceTree For Hackers: Intro

Raspberry Pi has just leaked information on the Pi Zero 3W. They did it by publishing a DeviceTree file that describes the hardware of the Pi Zero. This is how we know it has the BCM2711 (Pi 4 CPU), makes use of PCIe (maybe it’s even exposed!), has an onboard power button, an extra power LED, and an eMMC option. If I were to guess, this will be the first dual-sided Pi Zero board, and if I were to have hope, it finally has USB-C.

Don’t believe it? Go read the DeviceTree file for yourself — it’s exceptionally easy to read it between the lines. DeviceTree files tell the Linux kernel, or other OS kernels, what CPU to expect, what drivers to load, which interfaces are exposed on your board, and the devices connected to those interfaces. Sometimes a proper DeviceTree file is the only thing you need to make a modern Linux OS run on a neglected SBC you own.

There are DeviceTree files powering technology all around you. Your phone has one, so does your router, your ARM laptop, and not even to speak of your SBCs. Some DeviceTree files are evil, being merely a thin layer between the Linux kernel and proprietary drivers; you will find these in phones with CPUs made by evil corporations. Most DeviceTree files are simply there to do their job.

Continue reading “DeviceTree For Hackers: Intro” →

Proper Linux, On An ESP32

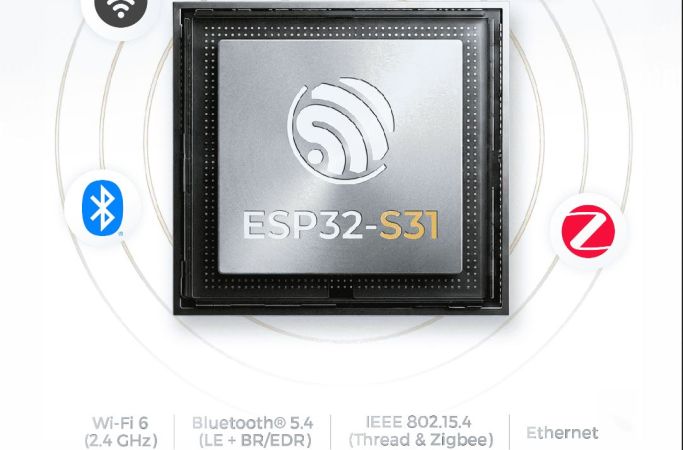
The ESP32 series of microcontrollers feature a lot on these pages, offering as they do a significantly powerful processor and in most cases, wireless connectivity. One recent member of the bewilderingly large family is the ESP32-S31, It’s a dual-core RISC-V unit with WiFi 6, and if that’s not interesting enough there’s the news that it runs Linux. Not -nommu Linux, but the full-fat version, as it has a memory management unit.

Before you imagine a superlative experience, it’s worth the reminder that the available resources will not give it much when it comes to computing power. But there’s an Espressif GitHub repository, and work on a port of a 6.x kernel, so you should be able to do something with it. A quick look on AliExpress finds dev boards at a range of prices, so the cost of experimenting shouldn’t be too high.

This moment at which the paths of microcontroller and full-fat SoC start to cross has been on the horizon for quite a while, and it’s exciting to see it finally arrive. Expect more similar chips in competition with this one, and more power too. Meanwhile see our noting the launch of the S31.

This Week In Security: More Linux Bugs, Biggest Crypto Theft Ever, Prusa Printers, Residential Proxies

Linux kernel bugs which can be triggered remotely, without any login, are rare. Most kernel vulnerabilities need an attacker to already be running code on the machine. CVE-2026-98432 is one of those: a use-after-free in the IPv4 TCP handshake code, rated CVSS 9.8, which Atlas has written up in detail. It goes all the way back to Linux 4.4.

A use-after-free is exactly what it sounds like: the program releases a chunk of memory, but some other code keeps using it. If an attacker can get their own data placed into that freed memory before it’s used again, they can influence what the kernel does next. In this case, when a server accepts a connection whose SYN packet carries IPv4 header options (a rarely used feature of IPv4), the kernel hands those options from the half-open connection to the full connection without copying them, then frees them while another CPU core may still be reading them. The fix is a four-line change, from “kfree()” to “kfree_rcu()”, which waits until every reader is done before freeing the memory. A lost race simply fails the handshake, so an attacker can keep trying.

The bug was reported by Xinyang Ge at Anthropic, and Anthropic says its Claude model wrote a working proof-of-concept that gets root on “Linux servers with a multipath TCP listener.” Multipath TCP (MPTCP) lets a single connection use several network paths at once, like WiFi and cellular, and you might assume almost nobody runs it on servers. Unfortunately, as Marcus Hutchins points out, Debian kernels enable MPTCP by default, and Go 1.24 and newer open MPTCP listening sockets by default when the kernel allows it, so anything built in Go (including the Caddy web server) is potentially exposed. Hutchins’ scans found about 2.1 million servers reachable over MPTCP on port 443, and he’s already seeing scanning from residential proxies and Russian VPNs which looks like it’s specifically hunting for this bug.

Upstream stable kernels were fixed in mid October, but as of October 31, Ubuntu and Red Hat were both still listed as vulnerable, with fixes in progress. If you can’t patch yet, you can check for MPTCP listeners with “ss -Mlnp”, and disable MPTCP with “sysctl net.mptcp.enabled=0”, but note that this doesn’t affect sockets which are already open, so you’ll need to restart any services using them. Red Hat and AlmaLinux have also published firewall rules which drop TCP packets carrying IPv4 options, which basically no legitimate traffic uses.

We haven’t seen bulk exploitation of this vulnerability yet, which might hint that it’s less trivial to trigger than the severity might indicate, but it’s a great time to get servers up to date. “Not exploited yet” has a nasty habit of turning into “every vulnerable server exploited in a day”.

Meanwhile, on the local side, OpenAI has published the results of pointing an automated pipeline, built on an unreleased “cyber-focused” model, at the kernel. In a run in mid October, it found 2,300 candidate bugs, reproduced 1,700 of them, and produced 948 working local privilege escalation exploits against a stock desktop Linux distribution, for about $1.2 million in API credits, or roughly $1,279 per root exploit. That’s not cheap, but for comparison, Pwn2Own has historically paid $20,000 for a single Linux kernel privilege escalation. Local privilege escalation is the step after an attacker gets a foothold: turning an ordinary user account, a compromised web app, or a sandboxed process into full control of the machine. Coupled with even a basic vulnerability in other code, it can allow an attacker to take full control of the system and hide the compromise much more effectively.

OpenAI says it’s working with the kernel community to report the bugs and submit patches, starting with the most critical, and that during the ten days the scan was running, more than 100 other kernel privilege escalation bugs were patched by other contributors, with about 300 more being discussed publicly. The most sobering line in the report is that, for now, a low-privileged account on an unpatched system “should be considered functionally equivalent to root access for a well-resourced threat actor.” It’s been quite a week for kernel developers, and it’s not going to slow down any time soon.

The flood of AI discovered vulnerabilities seems to continue unabated, and it’s easy to feel under attack from them. Consider, however, how often the open source community has called for companies using open source tools and libraries as core elements of their business to help support those tools and community. There’s still a significant burden placed on the community maintainers when almost 2000 bug reports land in a week, but over $1 million investment in securing Linux isn’t nothing, and the patches at least appear to be reasonably scoped and accurate. I’m pretty sure we’d see an article covering Linus’s response if they weren’t.

Continue reading “This Week In Security: More Linux Bugs, Biggest Crypto Theft Ever, Prusa Printers, Residential Proxies” →

Hiding Virtualization From Other Software

The Kernel-based Virtual Machine (KVM) allows Linux systems to function as hypervisors without needing any extra software, but VMs created with it don’t behave exactly like real hardware does. Sometimes that’s important, though, so [sandwich] built a tool called vfio-native that obscures the fact that software might be running in a virtual machine.

There are plenty of the ways that virtual hardware differs from bare metal. The VM may behave slightly differently for obscure instructions in ways that are measurable, it may take slightly longer to perform some tasks, or the hypervisor may simply announce itself directly. vfio-native includes some kernel patches that solve some bugs which address the different behaviors, changes the way that the kernel identifies itself, and attempts to force the CPUs to behave in ways that real hardware would behave. With all of this applied to the virtual machine, it scores a 1/85 against a VM detection tool, with a standard KVM virtual machine scoring 10/85.

For anyone looking to test this out, it’s available in the AUR for Arch Linux. Also, it’s probably worth mentioning that there are more reasons to use this than cheating at Counter-Strike. For example, security researchers testing malware need to know how that software behaves when it thinks its on real hardware, and some may behave in benign ways when confined to virtual machines. Some licensed software also may disable itself when it detects its running in a VM, which can be a nuisance for things like software controlling industrial tools which only run on operating systems that are no longer maintained or hardware that can’t be found anymore. Some other tools we’ve seen before perform similar tasks as well.

This Week In Security: Record Patch Tuesday, PHP’s Bad Time, The Oldest Vuln, AI Armies, And More

It’s no longer a proper month without Microsoft breaking its own record for security fixes, and October’s Patch Tuesday was no exception. Brian Krebs brings the roundup: more than 1,400 vulnerabilities fixed in a single batch, dwarfing September’s record of nearly 1,000, which itself was about ten times the normal monthly load. According to Tenable, Microsoft has now passed 4,000 CVEs for the year with two months still to go.

Only one of the fixes is for a vulnerability already being exploited in the wild: CVE-2026-96951, a security feature bypass in the Windows Shell affecting Windows 10, 11, and some Server versions. A .NET Framework bypass, CVE-2026-108398, was publicly disclosed before the patch, giving attackers a head start, and with modern AI tooling, it seems like not much of a head start is needed. At least 78 of the bugs are rated critical, and most of those allow remote code execution with little or no user interaction. Windows 10 holdouts can relax a little: Microsoft quietly extended free updates through October 2027.  Given the pace of exploitation, this is probably the only way to prevent an Internet-scale meltdown.

Microsoft credits LLM-driven bug hunting for the volume, which leaves the poor admins who have to test and deploy all of this in an unenviable spot. Fortra’s analysis shows that only 26 Microsoft vulnerabilities have landed in the CISA KEV catalog of actively exploited bugs so far this year, so start there. For the rest, the SANS Internet Storm Center and Cisco Talos have the usual breakdowns by severity. Or, you know, just patch everything and hope for the best, which is roughly what everyone does anyhow.

Continue reading “This Week In Security: Record Patch Tuesday, PHP’s Bad Time, The Oldest Vuln, AI Armies, And More” →

Trying To Get Linux Running On A Nokia E6

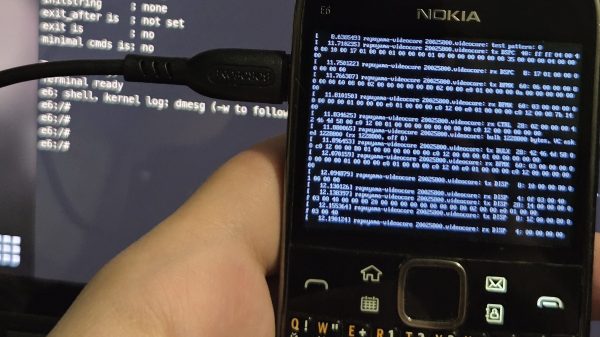
The Nokia E6 is a smartphone from back in the old days when Symbian was a thing. [fluffleswaffled] has been doing the work to get the ancient handset running Linux instead, because that’s ultimately cooler than what the phone shipped with out of the box.

There isn’t an unlocked bootloader on the E6, so instead, [fluffleswaffled] used an altogether different route to boot Linux. A Symbian app is used to load the kernel and device tree into RAM, at which point the MMU and caches are turned off and the device jumps into Linux. It’s a one-way trip, from which there is no way back to Symbian without a power cycle. The setup nets a terminal on the phone’s own screen, and the hardware keyboard and touchscreen are functional. The display is controlled by a Broadcom VideoCore III, with [fluffleswaffled] capturing messages from Nokia’s original display driver to create a custom kernel driver that replays them.

There’s an issue, though. The phone doesn’t stay in Linux land for long — it always resets within a couple minutes of booting into the alternative OS. [fluffleswaffled] believes this is because the phone’s baseband chip is supervising the application processor, and killing things once it’s detected that the Symbian mobile stack has stopped running. They’re hoping that someone with experience with Nokia basebands or the relevant hardware can point them in the right direction to get this hack running for more than 3.5 minutes at a time.

There probably isn’t a great deal of utility in getting Linux running on a 2011 smartphone, but we love the hustle nonetheless. We’ve seen this done before, though, and it’s always interesting to learn what it takes to get the OS booting on a new platform. If you’re whipping up similar hacks in your home lab, don’t hesitate to let us know on the tipsline.