
Critical Internet keys changed this week. Did you notice? The keys behind DNSSEC, the system for cryptographically validating DNS responses, rolled over on October 11 2026. This is the second time the DNSSEC keys have rotated since the system was implemented, and the first time in 2018 didn’t exactly go entirely smoothly.
DNS is what resolves a host name and turns it into an IP address. It underpins web browsing, email, and just about every other connection. It’s also a very early Internet protocol, written in both a simpler, less paranoid era, and an era where encryption was computationally expensive and legally problematic. DNS offers little protection against malicious actors spoofing responses, and the impacts range from phishing to redirecting email to just about any other manipulation of connections you can image.
DNSSEC addresses this by creating a chain of trust between DNS resolvers — the servers that forward the DNS query into the DNS infrastructure and return the results — and the global DNS servers. Part of this chain of trust is the root key that each resolver must have and trust, and this key is what changed this week. DNSSEC resolvers automatically watch for a new root of trust key, but the key must be signed by the previous root of trust, and is checked for at least 30 days before it is trusted. If someone were able to issue a bogus certificate, they would have to maintain control of the infrastructure for over a month before DNS resolvers would trust it.
The process of distributing the new key actually began more than a year ago, on January 11, 2025, to give DNSSEC resolvers time to get the new key. DNSSEC services should have had plenty of time to obtain and trust the new key, and unless DNS stopped working for you this week, they did their job.
The next major change for DNSSEC will require more profound changes to deploy a new signing algorithm that will be post-quantum secure.
Ransomware Recovery Company Didn’t Recover
BleepingComputer reports that the CEO of a company advertising services for recovering from ransomware attacks has been charged with fraud.
The company advertised that it could help with recovering from a ransomware attack by providing decryption services to unlock the ransomed files. Instead, the CEO of the company is accused of negotiating a ransom payment with the attackers and charging the victims a premium on top of the ransom.
In addition to fraudulent claims of decrypting the data without a ransom, this could fall foul of embargo laws against paying ransomware operators in some countries, or be against customer policy regarding payments.
The charges detail incidents in which the ransomware operators were paid $9,800, while the victims were charged $150,000 for “recovery”, and claim the company overall paid more than $8 million in ransom fees while charging customers $18 million.
More Refrigeration Hacks
Several weeks ago, commissaries operated by the United States military suffered a series of refrigeration failures. Units on multiple bases in multiple states and countries entered defrost mode, which activated heaters, spoiling food overnight. This week, hundreds of supermarkets in France have suffered the same issue, with units heating up and some even reportedly catching fire.
The attack started Sunday night, and not only triggers defrost mode, but seems to force the units to stay in defrost mode for a prolonged period. Losses are estimated to reach over $300,000. French prosecutors have called for investigations of the wide-spread attacks.
Clearly, a vulnerability has been found in the refrigeration controllers connected to the Internet, and fingers are being pointed at the Danfoss brand, which is also used by the US military bases. Researcher Kevin Beaumont points out that it may not even be a traditional vulnerability: Many of the units are directly connected to the Internet, with the username “admin”, and a password that changes daily. Unfortunately, the password changes to the current date. “Every single one is like this. You can just log in and change the temperature. Anybody can do it, easily.”
OpenAI employee charged with spying
An OpenAI employee was charged with spying after being caught placing “sophisticated listening devices” in meeting rooms, hidden in toilet paper: the most sophisticated of camouflage.
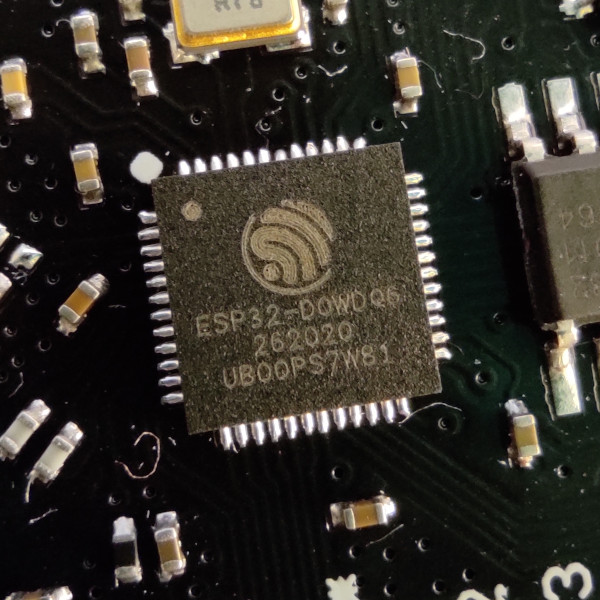
Employees discovered the device approximately two days after it was placed, according to the report. Ironically, logs indicate the employee used OpenAI’s own chatbot to help design the device and identify locations for it. Photos of the device look like it a SEEED Studio ESP32 device, a dev board likely very familiar to readers.
Stop & Shop and Hannaford hacked
The US supermarket chains Stop & Shop and Hannaford, which share a common owner, seem to have been hacked. There aren’t many details available yet, but multiple news sources in multiple states are reporting that the stores have taken their websites and online ordering completely offline, however stores remain open.
The company says it does not currently believe that customer payment details were part of the compromise.
Hardware wallets under attack
Kim Zetter brings the report of crypto thefts via hardware implanted in Ledger wallets.
Hardware wallets are offered as the panacea every time another crypto heist or supply-chain stealer makes the rounds. The idea is simple: private keys stay on the device and never touch your daily-driver, which is surely contaminated with keyloggers and trojans. The crypto transaction is built on the host and hands it to the device, the wallet device then solves it with the private keys and returns the signature. The only user interface is typically a screen display, which is exactly where the physical supply chain hack against Ledger happened.
The implants, found mainly in Ledger Nano X devices so far, sit dormant until the owner sets up the wallet. When the device shows the new recovery seed on its screen, the implant reads each character and sends the seed out through its own LTE modem, antenna, and eSIM. The implant never touches the host computer or the users WiFi network. The secure storage inside the wallet is never compromised: the hardware implant spies directly on the LCD to read the recovery keys as displayed to the user.
Blockchain analytics firm Bitquery links about 315 drained accounts, roughly $102 million in Bitcoin, Ethereum, Tron and others, to devices sold by CryptoBilis: that’s Ledger’s authorized reseller for Malaysia, Indonesia, and the Philippines.
[Joe Grand], a hardware hacker often featured here and the force behind many DEFCON conference badges, began looking in August 2025 after a Reddit post from someone who had bought a wallet on a Thai marketplace. [Joe] bought eight more Nano X units and found implants in four of them. This was reported to Ledger in March of 2026, but according to [Grand], Ledger didn’t follow up for months.
Then in September, Mark Karpelès, the former Mt. Gox CEO, published a teardown showing how the implants have evolved. The first generation used hand-soldered wires to the screen. The second used a transparent orange flex circuit laminated onto the board, with a smaller battery to make room. The third uses a black-coated flex with the part numbers scraped off and a custom antenna. A Japan-based researcher who examined ten Nano X and two Flex devices found five distinct implant designs. They traced the eSIM traffic to an Alibaba-managed data center in Hong Kong, with at least 90 implants reporting seeds there in June alone.
Ledger’s official position is that a “limited number” of devices came from a single seller. It says there is no sign that its own systems were compromised, and it has told resellers to buy only through authorized channels and “never to restock returned products. That last line points at a likely route: buy wallets, implant them, return them, and let them go back on the shelf.
Despite the claims of a single compromised seller, a user named [Johannes] found implants in two Nano X units bought at MediaMarkt stores in Europe, and MediaMarkt is a listed authorized reseller with around a thousand stores across ten countries. There are also reports of implanted Flex devices, and Stax reports that are still unverified. Trezor has started trimming its own authorized-seller list as a “preventive step.” Attribution is still unknown.
CryptoBilis changed ownership earlier this year under an NDA that only recently expired, which has raised eyebrows. Zetter is careful to note that there’s no evidence connecting CryptoBilis to the implants or the thefts.
The takeaway is uncomfortable for anyone who has told people to “just buy a hardware wallet”. The threat model always assumed the device itself was trustworthy, and “buy direct from the vendor” was advice for being extra careful. Now it’s the minimum. Tamper-evident packaging clearly isn’t enough against someone with a lamination process and a parts budget. The options get less fun from here: open the case and inspect the board, which voids the warranty, and good luck spotting a black flex on a black PCB, generate the seed somewhere you control and import it, or use multi-signing across vendors so one bad device can’t empty everything.
Crypto forces you to be your own security, and if you have enough money for someone to design an attack that would have only been expected of a nation-state a few years ago, your home-grown security has to be really, really good.











$300,000 in food at a time it’s already expensive. Some just want to see the world burn.
Danfos releasing a patch, making a vulnerability public, all be it not necessarily common knowledge, but as we know, it doesn’t have to be. Some didn’t run the update, but a fair few had older systems that were incompatible and couldn’t use the fix and those were the ones that got hit. It just goes to show that connecting everything to the internet isn’t better, especially when it comes to critical infrastructure.
Ease of use, security by obscurity, a similar story with all the IP cameras that sit with default settings one internet search query away.