This Week In Security: New Spectre Attacks, Crushing Quantity Of Linux Vulns, Google Gets Too Much AI, And Hacking Lawnmowers

Just-in-time, or JIT, compilation could be considered a fundamental backbone of modern computing.  JIT compilation turns scripting languages like JavaScript or intermediary binary forms like Web Assembly into native code on the fly, giving web apps, and things that are web apps under the covers like Electron-based tools, near native speed.  A new paper explores leveraging JIT systems to revive Spectre-v2 attacks against processors.

Most modern processors gain performance by using a trick called “speculative execution”.  The processor guesses the likely result of a compare, and begins executing some of the next instructions before the results are actually known.  If the processor guessed right, things continue and there is a speed gain because it can jump ahead, but if the processor guessed wrong, any instructions that were run and any side effects of running them are discarded and execution resumes on the actual path.  In theory, anyhow.

In practice, the Spectre class of attacks targets branch prediction. It was discovered that when the wrong branch was chosen, not all of the results were truly hidden; Patterns of failures in guessing branches can be used to leak behavior processing encryption keys and other activities. The attacks evolved with the research dubbed Spectre-V2, which showed that non-privileged contexts, like non-root users and virtual machines, could poison the instruction prediction and use it to read arbitrary memory.  Fixes to the Linux kernel and other platforms were required to mitigate the worst of the effects.

The paper shows that by using self-modifying code in the JIT, the processor can be tricked into loading cached versions of the instructions.  The fixes to the kernel to prevent Spectre attacks include identifying malicious code patterns that attack the branch prediction, and stopping or changing them:  By causing the CPU to execute the cached copy of instructions instead of the live copy, the attack ignores the fixed instructions entirely and can attack the branch prediction algorithm.

To prove the attack is feasible in the real world, the researchers targeted several JIT compilers, including the SpiderMonkey JavaScript engine used by Firefox, the eBPF JIT found in the Linux kernel, and GraalVM, the JIT used in Python.  They found success with each, demonstrating that the attack is at least plausible.

Research like this is unlikely to be an instant world-melter, and will help find possible mitigations in the future to prevent these sorts of attacks.  Operating systems that support a high-security “lock-down” mode, like macOS and iOS, often disable JIT entirely, out of concern about these sorts of attacks.  There’s probably no need to start disabling JIT on every system, but attacks like these have a tendency to evolve.
Continue reading “This Week In Security: New Spectre Attacks, Crushing Quantity Of Linux Vulns, Google Gets Too Much AI, And Hacking Lawnmowers” →

A Headset Fit For A Hackaday Writer

I started writing this from a commuter train passing at speed through the outskirts of London, and my headset had just broken. The flexible joint that attaches one earpiece to the headband has snapped, leaving the earpiece dangling on its cable. This is annoying on its own, but what is annoying me enough to write about it is that this isn’t the first time. This is only the latest in a succession of headsets I’ve taken on the road with me has broken, not because of rough treatment, but simply due to flimsy or bad design. What on earth can I do about this?

Failure Built-In

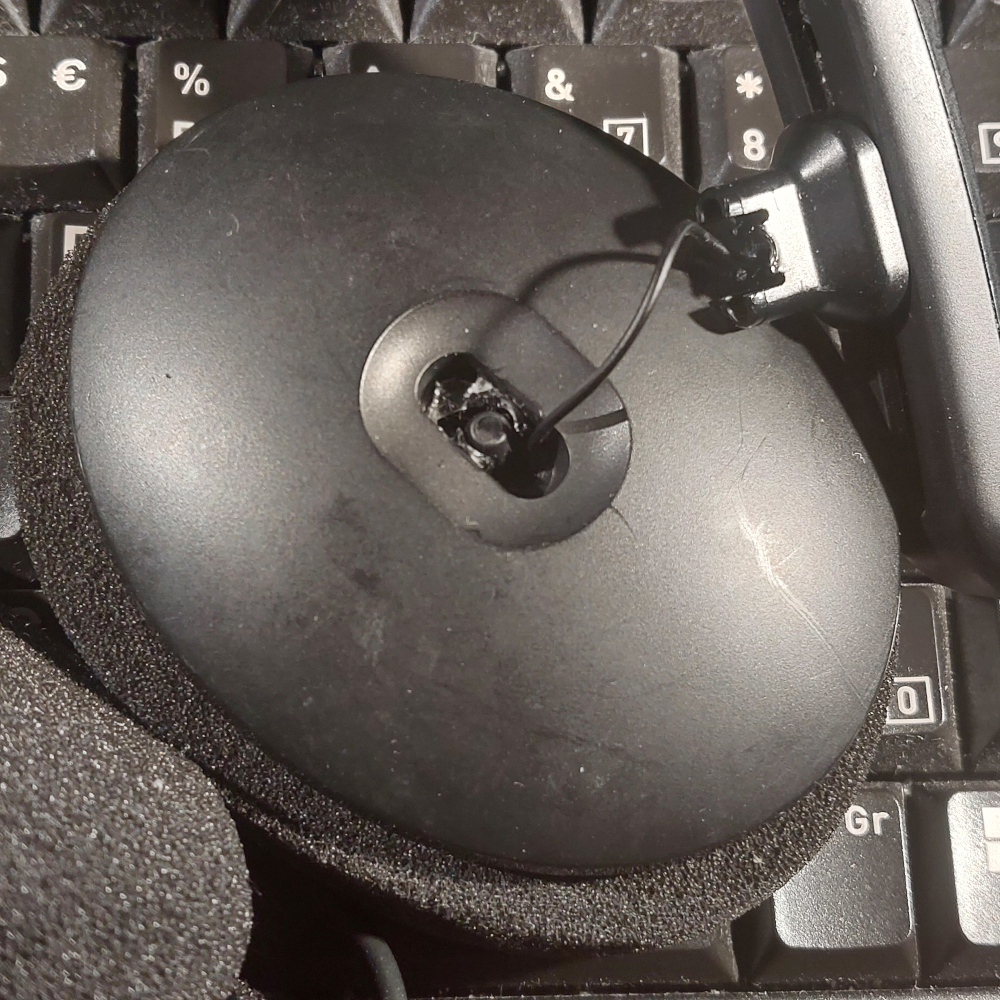
The earpiece of an EPOS headset, detached from its band.
Failure inevitable: the whole headset relied on a tiny piece of plastic in the centre.

The most recent three have been a JVC whose rotating joint allowing the earpiece to lie at a slight angle with my ear has failed, a quite expensive Logitech whose ear sponges failed closely followed by its USB cable, and now an EPOS whose ball joint has failed.

I repaired the JVC and got a bit more life out of it and I’ll have a go at repairing this EPOS, but that’s hardly the point. I’m paying not inconsequential money and I’m getting good sound quality and electronics, but I’m not getting anywhere near the mechanical quality I need. I could buy a set of tough DJ headphones such as the Sennheiser HD25, but they don’t come with a microphone, they’re not a headset.

So if I can’t buy a decent headset without spending military grade money on one from an F16 fighter, what can I do to make my own? I’m an engineer, damnit!

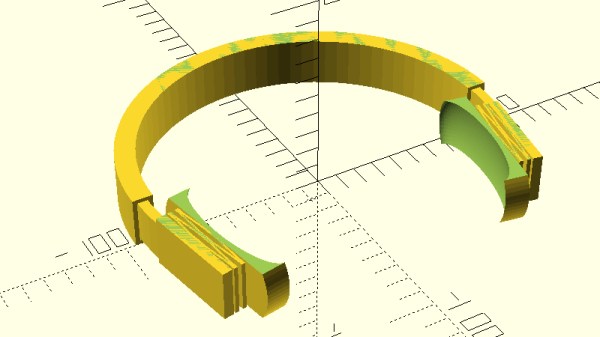
At its most basic, a headset is a springy band that goes over the head, with an earpiece at its end. But a human head is not a cube with vertical parallel sides, it’s a complex shape and every one is different. So those earpieces have to have some “give” in them in order to fit comfortably against the ear. In the simplest case this is achieved by giving the earpiece a soft surround that moulds itself to the ear, but most headsets incorporate some articulation. The earpiece must rotate a little around a vertical line parallel with the ear, and also with a horizontal line at right angles to the axis of the ear. The EPOS managed both axes by means of a ball joint, while the JVC had a stirrup with pins to achieve the horizontal motion, and a circular joint — the part which broke — for the vertical. In both case the weak point was a thin part of the plastic moulding which broke, on the EPOS a short stalk for the ball in the ball joint, and in the JVC a similar stalk for the circular joint. Any design I come up with must avoid this type of weak point, and spread the load of an earpiece over considerably more material than my broken headset. Continue reading “A Headset Fit For A Hackaday Writer” →

The FPGA Chronicles: Open Source It

Last time, we looked at getting started with the GOWIN tools and a Tang Nano 20K FPGA. The software from GOWIN isn’t bad, but it isn’t open source, and there are a few oddities about it. In addition, simulation is through a third-party simulation package that has undergone some changes since an acquisition. There are tons of free simulation programs that are extremely good, and there is an open-source toolchain for the FPGA.

You could go grab everything you need piece by piece. But you don’t have to. There are several efforts to produce a toolchain from all the different pieces. We’re going to look at APIO.

APIO

APIO isn’t so much an FPGA toolchain project as it is an aggregator of toolchain projects. It reminded us of PlatformIO, and notes that it was inspired by it. It updates the tools you need, includes its own libraries, and gives you a common workflow across the FPGAs it supports.

You can download it for the command line, but you can also install it as a Visual Studio Code extension, which is what I did. You have to create a simple file that describes your project, and that’s about it.

Install Problems

Since APIO has its own libraries, it is possible that you will find some conflicts with your system libraries. In my case, the libreadline.so.8 file (in ~/.apio/bin/_internal) was causing problems that prevented anything from working. I simply renamed it out of the way, or you can just delete it. That took care of the problem.

Keep in mind that APIO just orchestrates a bunch of other tools like Yosys and GTKWave. Even if you have your own versions, APIO expects to use its private copies. For example, GTKWave on my system is a different version than the APIO copy, and if I try to read wave files without using APIO, I get error messages. You can, however, open a shell from the Tools/Misc menu of the APIO panel in Visual Studio Code.

Continue reading “The FPGA Chronicles: Open Source It” →

Hackaday Links Column Banner

Hackaday Links: October 3, 2026

If you’re interested in aerospace, there’s an excellent chance you’ve heard the rumor that NASA is trying to get its SR-71 flying again. Or at the very least, they are interested in what exactly it would take to bring the iconic Mach 3+ spy plane back online.

The story started a couple of weeks ago when NASA Administrator Jared Isaacman announced the agency would be reinvesting in their famed “X-Plane” experimental aircraft program in an effort to get “back in the business of flying high and fast again.” Not long after, keen-eyed observers noted that the SR-71 that had been sitting on the tarmac at the Armstrong Flight Research Center in California had been moved to an unknown location. Several individuals who worked on the plane while it was operational have since claimed NASA representatives contacted them about potentially refurbishing it.

Continue reading “Hackaday Links: October 3, 2026” →

Hackaday Podcast Episode 389: Spinning Lightfield Displays, And Jenny Visits A Blast Furnace

Another all-European podcast for you this week, as Elliot Williams is joined by Jenny List for an evening looking at the past week in Hackaday. And this week there is a particularly good selection to look at.

A while back we showed you a project that put synthetic aperture radar on a drone, generating extremely detailed imaging of the terrain beneath it. This week we had an update, in which an ingenious positioning accuracy fix gave it an astonishing increase in resolution. On top of that project we have 3D lightfield image display with the unexpected help of a Nipkow mechanical TV scanning drum. Geting your own microprocessor manufactured, DOOM in a database server, and a comprehensive array of unusual sensors in a tricorder project complete the picture.

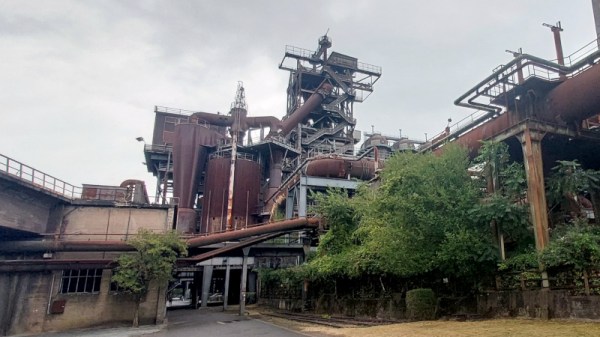
Finally we have a couple of space stories and Jenny describing the preserved industrial delights of the Ruhr valley in Germany. You’ll want to go there, but first you’ll want to listen to the podcast.

Download it yourself in MP3. It’s wafer thin.

Continue reading “Hackaday Podcast Episode 389: Spinning Lightfield Displays, And Jenny Visits A Blast Furnace” →

This Week In Security: ShinyHunters Won’t Dox The FBI, Pentagon Data Stolen, And OBS Vulnerable

404 Media reports that the ShinyHunters group who stole multiple terabytes of FBI employee data say they do not plan to release the data.

Known for ransomware and extortion of innumerable companies and government agencies, ShinyHunters used a zero-day vulnerability in Oracle PeopleSoft to compromise the employment site of the FBI and pivot into scraping the content of FBI AWS instances, claiming to have the full employment and health data of all FBI agents, employees, and spouses.

The hacker group took exception to an FBI press release that claimed that the group over-stated stolen data and that they directly harass victims and victim’s families.  The group publicized the FBI data breach, demanding a retraction of the statements, and it was generally assumed that the group would follow their typical methods of releasing the data publicly if the demands were not met.

The group has told 404 media that they had always agreed internally to not release the stolen data, saying “This was all a marketing campaign to protect our business and actively combat disinformation”.  Meanwhile the FBI continues the investigation, and Shiny Hunters may be hoping to defer some of the ire.

Continue reading “This Week In Security: ShinyHunters Won’t Dox The FBI, Pentagon Data Stolen, And OBS Vulnerable” →

Places To Visit: Landschaftspark Duisburg-Nord

There are many benefits to spending time in the park, but perhaps few of them have a Hackaday angle. There’s a park in Germany you might want to make an exception for, and it lies in the Ruhrpott city of Duisburg.

I was lucky enough last month to join a friend as she toured Germany for the first time with a caravan. It’s a large country with many beautiful places, so her choice might seem unexpected at first sight. The Ruhrpott, or Ruhr area, is a loose conurbation of industrial cities that loosely follows the river Ruhr on its trip to the Rhine on the western edge of the country. It’s close to  deposits of coal and iron ore, so just like similar areas in other countries, it became a centre for heavy industry. Today that continues, but as you might expect it’s also dotted with the remains of former industries. It’s one of those which is our subject for today, and it offers a very unusual opportunity.

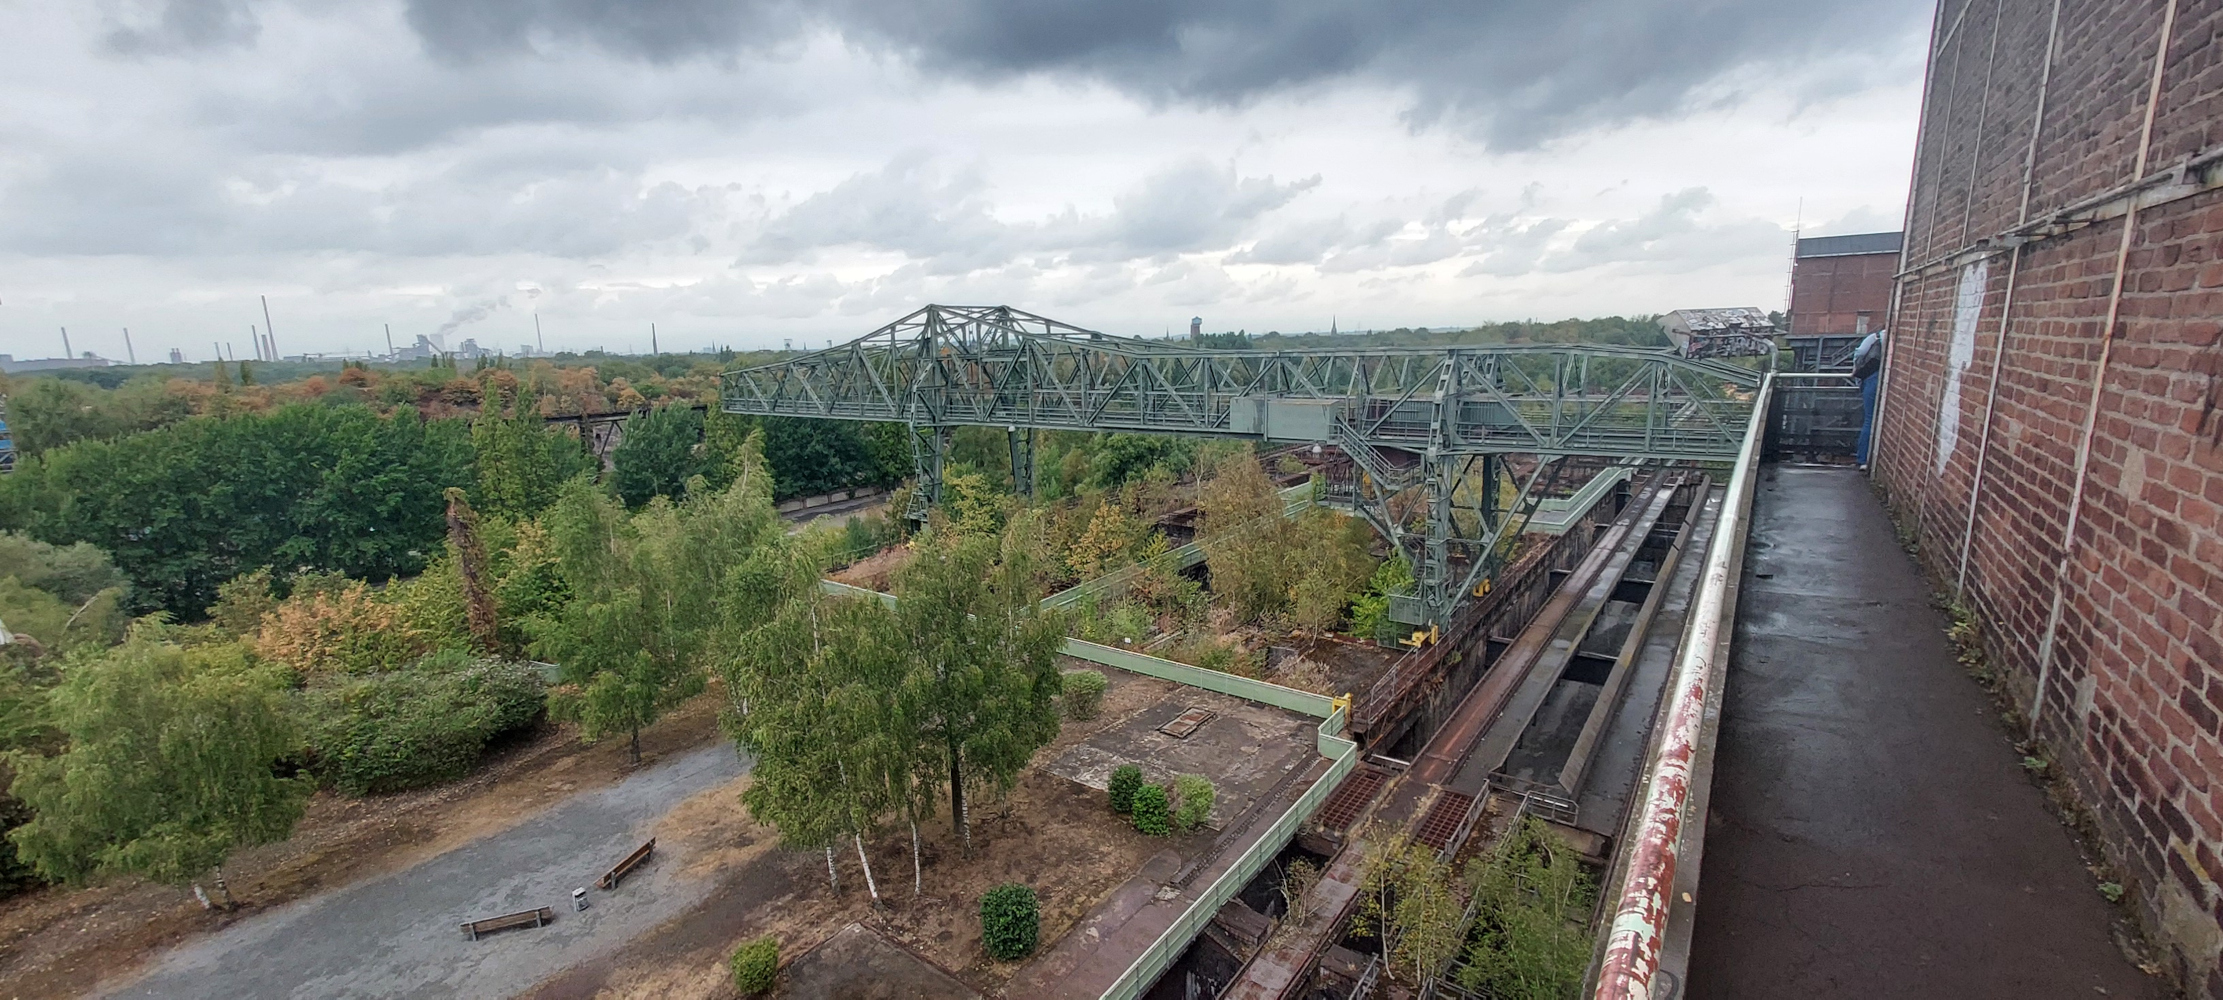
A view out over a wooded post industrial landscape against a grey cloudy sky. In the foreground is a hiuge traverser crane.
Looking out over the former ore bunkers shows just how huge this site is.

Landschaftspark Duisburg-Nord is a forest park on the northern side of the city of Duisburg. But of course that’s not the whole story, because until 1985 it was the site of the Thyssen ironworks. In rehabilitating the site they chose to keep the main structures of the ironworks intact as they reclaimed the surrounding polluted industrial land, so today it may be one of the few places in the world where you can free of charge get up-close and personal with a fully-intact and preserved blast furnace. The site has three of them remaining along with their associated ore and gas processing plants, and the largest and newest, blast furnace number 5, is a structure you can climb to its top. If you’ve ever been curious about iron smelting, this is the place to come. Continue reading “Places To Visit: Landschaftspark Duisburg-Nord” →