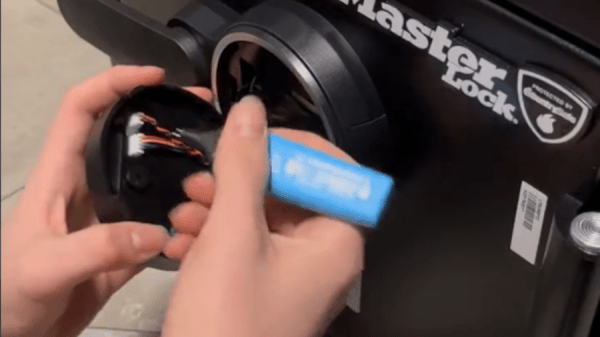
A light blue marker with a two-pin header replacing the tip, being pressed against the back of the keypad baord that's removed from the safe

Anyone Can Be The Master Of This Master Lock Safe

[Etienne Sellan] got one of these lovely $5 logic analyzers. As with any shiny new tool, he started looking for things to investigate with it, and his gaze fell on a Sentry Safe (produced by Master Lock). On the surface level, this keypad-equipped safe is designed decently when it comes to privilege separation. You can take the keypad board off and access its backside, but the keypad doesn’t make any decisions, it merely sends the digits to a different board embedded behind the safe’s door. The solenoid-connected board receives the PIN, verifies it, and then controls the solenoid that unlocks the safe.

[Etienne] hooked up a logic analyzer to the communication wire, which turned out to be a UART channel, and logged the keypad communication packets — both for password entry and for password change. Then, he wrote some Arduino code to send the same packets manually, which worked wonders. Bruteforcing wasn’t viable, however, due to rate limitation in the solenoid controller. Something drew his attention from there – if you want to change the password, the keypad requires you enter the factory code, unique to each safe and supplied in the instruction manual. That code entry is a separate kind of packet from the “change password” one.

More after the break…

Continue reading “Anyone Can Be The Master Of This Master Lock Safe” →
This Week In Security: Follina, Open Redirect RCE, And Annoyware

Depending on who you ask, there’s either 2 vulnerabilities at play in Follina, only one, or according to Microsoft a week ago, no security problem whatsoever. On the 27th of last month, a .docx file was uploaded to VirusTotal, and most of the tools there thought it was perfectly normal. That didn’t seem right to [@nao_sec], who raised the alarm on Twitter. It seems this suspicious file originated somewhere in Belarus, and it uses a series of tricks to run a malicious PowerShell script.
Continue reading “This Week In Security: Follina, Open Redirect RCE, And Annoyware” →

3D Printed Protection Against “Under-Door” Attacks

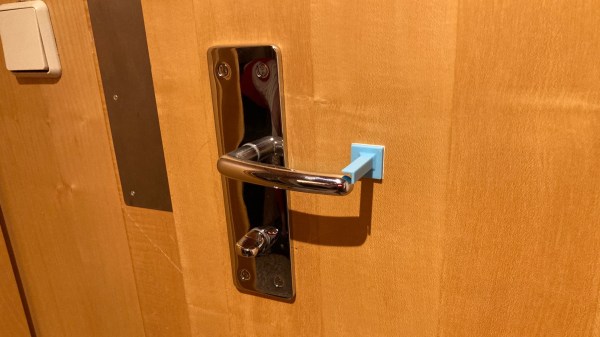
“Under-door” style attacks are when an attacker slides a tool through the gap underneath a door, hooks the interior handle from below, and opens the door by pulling the handle downward. This kind of attack works on the sort of doors and locks commonly found in hotels, where turning the handle from the inside always results in an open door. [Michal Jirků] found himself in a hotel room with a particularly large gap underneath the door, and decided to quickly design and print a door guard to protect against just such an attack.

It’s a simple object, and twenty minutes of printing and a little double-sided tape is all it takes to deploy. Because an attacker performs an under-door attack with a sizable mechanical disadvantage, it doesn’t take much to frustrate the attempt, and that’s exactly what the object does. Physical security in hotels is especially important, after all, and crooks have been known to exploit known flaws like the face-palmingly bad Onity key card lock exploit.

If you’re having trouble picturing how it all works, this video demonstrates an under-door attack in action, so you can see how blocking the space by the handle would easily prevent the tool from getting where it needs to go.

The Great Euro Sat Hack Should Be A Warning To Us All

Military officials and civilian security researchers have been warning us for years: cyberattacks are becoming a very real part of modern warfare. Far from being limited to military targets, cyberattacks can take out everything from vital public infrastructure to commercial and industrial operations, too.

In the early hours of February 24, as the Russian invasion force began raining missiles on Ukrainian cities, another attack was in progress in the digital realm. Suddenly, satellite terminals across Europe were going offline, with many suffering permanent damage from the attack.

Details remain hazy, but researchers and military analysts have pieced together a picture of what happened that night. The Great Euro Sat Hack prove to be the latest example of how vulnerable our digital infrastructure can be in wartime.

Continue reading “The Great Euro Sat Hack Should Be A Warning To Us All” →

Expired Certificate Causes German Payment Meltdown

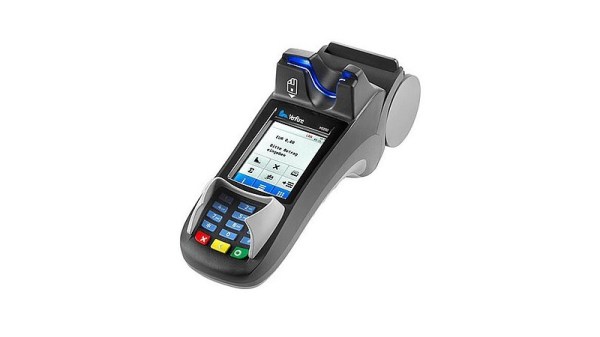
For most Hackaday readers the process of buying groceries this weekend has been a relatively painless one, however we’re guessing some of our German friends will have found their cards unexpectedly declined. The reason? A popular model of payment card terminal, the Verifone H5000, has suffered what has been described as a “software malfunction”. So exactly what has happened? The answer is as simple as it is unfortunate: a security certificate for German transaction processing stored on the device has expired.

The full story exposes the flaws in assuming that a payment terminal is an appliance rather than a computer and its associated software that needs updating like any other. The H5000 is an old terminal that ceased production back in the last decade and has reached end-of-life, however it has remained in use and perhaps more seriously, remained in the supply chain to merchants buying a terminal. With updates requiring a site visit rather than an over-the-air upgrade, it’s likely that the effects of this mess could last a while.

In case the hardware for this type of equipment interests you, we’ve had a teardown on another Verifone terminal in the past.

A modified Ghostbusters Proton Pack

Track Down Ghosts In Your WiFi With The Pwnton Pack

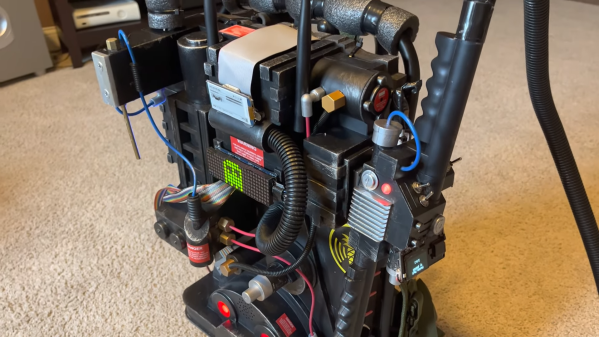
If there’s something weird in your Network Neighborhood, who you gonna call? If you want your WiFi troubles diagnosed in style, try calling [Travis Kaun] — he might just show up wearing the amazing Pwnton Pack. Built from a replica Proton Pack similar to those used in the 1984 classic Ghostbusters, it’s a portable wireless security diagnostics kit that should be able to pinpoint any weaknesses in your wireless network.

Inside, it’s got a Mark VII WiFi Pineapple, which is a portable device designed for security testing purposes, as well as a Raspberry Pi running Pwnagotchi: a deep learning-based WiFi sniffer that aims to capture those network packets that help maximize your chances of brute-forcing the WPA key. These two devices are connected to an array of antennas, including a cool rotating 5 GHz panel antenna to scan the surrounding area.

Naturally, the Pwnton Pack also includes a Neutrona Wand, which in this case contains a 2.4 GHz Yagi antenna hooked up to an ESP32 programmed to perform deauthentication attacks. An Arduino Nano drives an LED matrix that shows scrolling Pac-Man ghosts, while a dedicated sound board provides movie sound effects. The whole system is powered by three LiPo battery packs, and can even be remotely operated if desired.

Sadly, it doesn’t come with one of those ghost traps to suck up wayward WiFi networks, but the range of tools available should help to catch any kind of weird phantoms hiding in your system. We’ve spotted a few Proton Packs before, but never one with such advanced functionality. Security testing systems tend to be a bit less conspicuous, after all. Continue reading “Track Down Ghosts In Your WiFi With The Pwnton Pack” →

This Week In Security: Good Faith, Easy Forgery, And I18N

There’s a danger in security research that we’ve discussed a few times before. If you discover a security vulnerability on a production system, and there’s no bug bounty, you’ve likely broken a handful of computer laws. Turn over the flaw you’ve found, and you’re most likely to get a “thank you”, but there’s a tiny chance that you’ll get charged for a computer crime instead. Security research in the US is just a little safer now, as the US Department of Justice has issued a new policy stating that “good-faith security research should not be charged.”

While this is a welcome infection of good sense, it would be even better for such a protection to be codified into law. The other caveat is that this policy only applies to federal cases in the US. Other nations, or even individual states, are free to bring charges. So while this is good news, continue to be careful. There are also some caveats about what counts as good-faith — If a researcher uses a flaw discovery to extort, it’s not good-faith.
Continue reading “This Week In Security: Good Faith, Easy Forgery, And I18N” →