
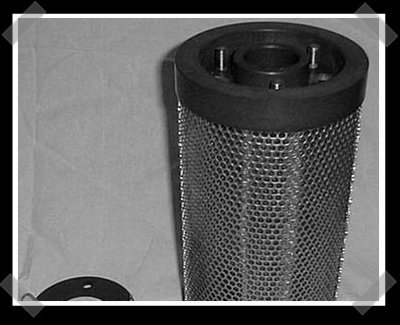
Most people fear refilling their own ink cartridges. [Skipbreather] made his own CO2 scrubber refill for his rebreather. (Modern rebreathers are damn impressive.) The build is fairly straight forward, but requires some machining. I had to laugh when I found out that part of his build involved toilet seat hold down bolts.
How-To: Scavenge A Mouse For Parts
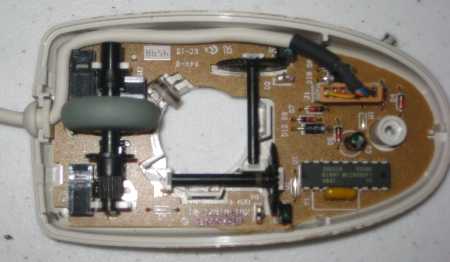
Chris Kiick posted about swarm robotics earlier in the week and today publishes his first Hack-A-Day How-To.
Old computer mice are being abandoned in droves. They’re tossed out because of dirt, obsolescence, or for being entirely too beige. Anyone who has a computer usually has more than one mouse and you can get them for pennies, if not free just for asking. Fortunately for the discriminating (read: cheap) hacker, these little widgets are chock-full of project parts. Today’s How-To will dissect a computer mouse, extract the useful parts, and give some ideas about how to use them.
Syringe Logic Probe
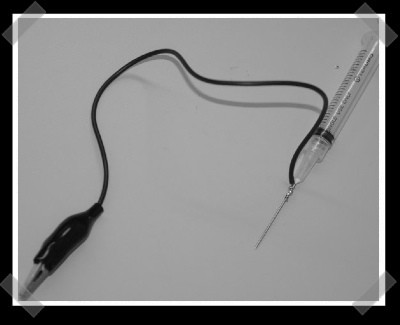
[Travis] sent in his oh so simple(why didn’t I think of that) syringe logic probe. that he put together for his version of the sump logic analyzer. Real probes tend to be pretty expensive. With some effort, you can probably fit an led/diode/resistor in there and make a simple 5v logic probe. If you’d like a nice logic analyzer, Spartan-3 board that it’s based on is only $99.
The World’s Spookiest Weapons
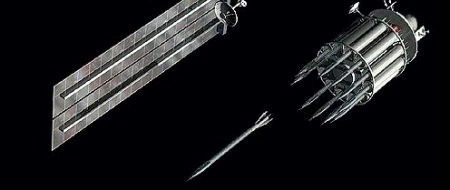
As purveyors of a fine hacks, we often get pitched on what are generally considered very bad ideas. Luckily, most of these ideas die on the drawing board due to a lack of time and energy or maybe having a shred of moral accountability. There’s nothing that government funding can’t fix though. Popular Science has put together a gallery of The World’s Spookiest Weapons. It’s a who’s who of real and speculative engineering that could lead to our eventual destruction. Opening with the atomic bomb, it moves quickly into more bizarre territory, everything from heat rays, to rail guns, to gassing people with elephant tranquilizers. Our personal favorite is The Rods from God. Imagine getting smote by a precisely targeted metal power pole dropped from space that has accelerated to 36,000 feet per second thanks solely to gravity. What a wondrous world we live in.
[via Acidus]
DefCon CTF 2008 Qualifier
Kenshoto is back again to run the Capture the Flag competition at DefCon. CTF is a multiteam competition featuring creative attack and defense of servers and lasts the entirety of DefCon. Unreleased exploits are often seen during the competition. As in previous years, Kenshoto will be narrowing the field with a qualification round. Quals will start the evening of May 30th and run for 48 hours. NOPS-R-US has a solution guide for the previous two years so you can get some idea of what you’re getting yourself into. They’ve even got a couple write ups for last year’s final. The competition should prove entertaining even if you don’t make the final cut.
[via Midnight Research Lab]
Bruce Schneier’s Opinion On Everything
Honestly, we were originally sent this Q&A with famed cryptographer [Bruce Schneier] as a restaurant recommendation (112 Eatery, Minneapolis). Posted last fall on NYTimes’ Freakonomics blog it covers [Bruce]’s opinion on nearly everything. Here are a few items in particular that really stuck out to us:
The most immediate threat to the average person is crime – in particular, fraud. And as I said before, even if you don’t store that data on your computer, someone else has it on theirs. But the long-term threat of loss of privacy is much greater, because it has the potential to change society for the worse.
What you’re really asking me is about the security. No one steals credit card numbers one-by-one, by eavesdropping on the Internet connection. They’re all stolen in blocks of a million by hacking the back-end database. It doesn’t matter if you bought something over the Internet, by phone, by mail, or in person – you’re equally vulnerable.
We already knew he doesn’t secure his WiFi (neither do we) and you’ll find many other interesting discussions in the article. If you want Bruce Schneier facts though, you’ll have to look elsewhere.
Interfacing Your Laptops Onboard I2c
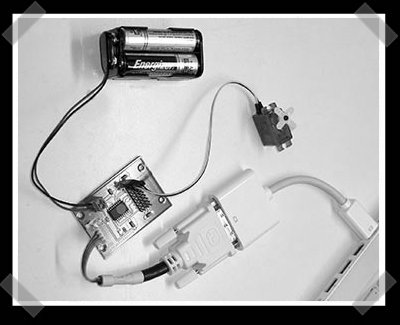
[ladyada] ran across this excellent hack by [phillip]. Apparently there’s a clock, data, 5v and ground connection available in most modern video connections. (He even notes HDMI cable pins) He wrote some drivers and can now control i2c hardware directly from the PC Mac. [Ladyada] notes that most laptops use an i2c bus for extra sensors as well. For now, the code only works on Mac OS X.








