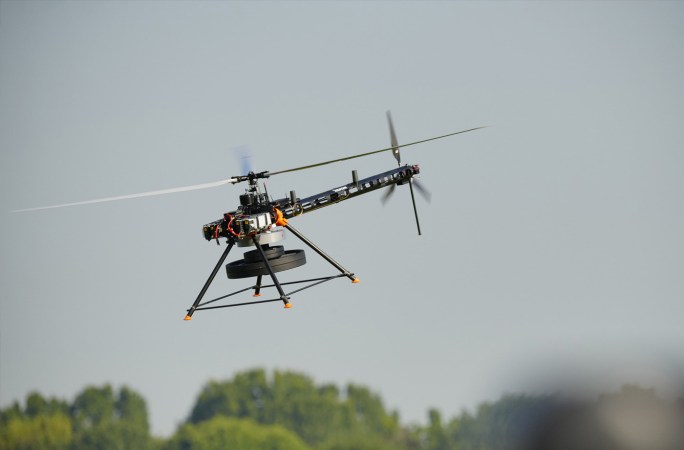
AVIDdrone's winning entry: a helicopter.

DARPA Lift Challenge Won By Helicopter

America’s mad scientists all have one dream: DARPA money. DARPA, the Defense Advanced Research Projects Agency, regularly throws round sweet, sweet tax dollars to push the envelope on any number of things, leading to such spinoffs as the very network carrying these words to you. Not every DARPA project ends in revolution though– like the latest DARPA Lift Challenge, whose goal was to see the creation of a vehicle that could perform Vertical Take Off And Landing with a payload 4x its own weight. We’ve embedded the ‘look back’ video below.

We hoped for something revolutionary, something bizzare, something really, really cool– and there were absolutely entries on the field that met all of those superlatives. Unfortunately, sometimes conventional designs are the convention for a reason , and the overall winner by AVIDrone, Inc. was just a very well made electric helicopter. One big lift rotor, one little tail rotor– aside from clever details in the solid-state batteries and carbon-fiber construction, it is a totally normal aircraft… albeit one that could lift 3.84x its dry weight, or 112 lb of payload. Interestingly a battery-powered hexrotor drone took home second place with a 3.64:1 lift ratio. Perhaps the big shock was not seeing combustion engines until third place: another helicopter, this time with a turbine engine. So much for energy density!

Some of the other more bizzare– if less performant–entries did get prizes to further their development, so we’ll likely see them back for the 2028 version of the challenge. Some of the concepts visible were covered here on Hackaday, like turning the drone body into a giant lift rotor , so perhaps one of you will have the bright idea that brings home a million in the next round of the contest.

Continue reading “DARPA Lift Challenge Won By Helicopter” →

Motorola’s Password Pill Was Just One Idea

Let’s face it; remembering a bunch of passwords is the pits, and it’s just getting worse as time goes on. These days, you really ought to have a securely-generated key-smash password for everything. And at that point you need a password manager, but you still have to remember the password for that.

Well, Motorola is sympathetic to this problem, or at least they were in 2013 when they came up with the password pill. Motorola Mobility, who were owned by Google at the time, debuted it at the All Things Digital D11 tech conference in California. This was a future that hasn’t come to pass, for better or worse, but it was a fun thought experiment in near-futurism.

Continue reading “Motorola’s Password Pill Was Just One Idea” →

This Week In Security: The AI Hacker, FortMajeure, And Project Zero

One of the hot topics currently is using LLMs for security research. Poor quality reports written by LLMs have become the bane of vulnerability disclosure programs. But there is an equally interesting effort going on to put LLMs to work doing actually useful research. One such story is [Romy Haik] at ULTRARED, trying to build an AI Hacker. This isn’t an over-eager newbie naively asking an AI to find vulnerabilities, [Romy] knows what he’s doing. We know this because he tells us plainly that the LLM-driven hacker failed spectacularly.

The plan was to build a multi-LLM orchestra, with a single AI sitting at the top that maintains state through the entire process. Multiple LLMs sit below that one, deciding what to do next, exactly how to approach the problem, and actually generating commands for those tools. Then yet another AI takes the output and figures out if the attack was successful. The tooling was assembled, and [Romy] set it loose on a few intentionally vulnerable VMs.

As we hinted at up above, the results were fascinating but dismal. This LLM successfully found one Remote Code Execution (RCE), one SQL injection, and three Cross-Site Scripting (XSS) flaws. This whole post is sort of sneakily an advertisement for ULTRARED’s actual automated scanner, that uses more conventional methods for scanning for vulnerabilities. But it’s a useful comparison, and it found nearly 100 vulnerabilities among the collection of targets.

The AI did what you’d expect, finding plenty of false positives. Ask an AI to describe a vulnerability, and it will glad do so — no real vulnerability required. But the real problem was the multitude of times that the AI stack did demonstrate a problem, and failed to realize it. [Romy] has thoughts on why this attempt failed, and two points stand out. The first is that while the LLM can be creative in making attacks, it’s really terrible at accurately analyzing the results. The second observation is one of the most important observations to keep in mind regarding today’s AIs. It doesn’t actually want to find a vulnerability. One of the marks of security researchers is the near obsession they have with finding a great score. Continue reading “This Week In Security: The AI Hacker, FortMajeure, And Project Zero” →

Hackaday Links Column Banner

Hackaday Links: January 22, 2023

The media got their collective knickers in a twist this week with the news that Wyoming is banning the sale of electric vehicles in the state. Headlines like that certainly raise eyebrows, which is the intention, of course, but even a quick glance at the proposed legislation might have revealed that the “ban” was nothing more than a non-binding resolution, making this little more than a political stunt. The bill, which would only “encourage” the phase-out of EV sales in the state by 2035, is essentially meaningless, especially since it died in committee before ever coming close to a vote. But it does present a somewhat lengthy list of the authors’ beefs with EVs, which mainly focus on the importance of the fossil fuel industry in Wyoming. It’s all pretty boneheaded, but then again, outright bans on ICE vehicle sales by some arbitrary and unrealistically soon deadline don’t seem too smart either. Couldn’t people just decide what car works best for them?

Speaking of which, a man in neighboring Colorado might have some buyer’s regret when he learned that it would take five days to fully charge his brand-new electric Hummer at home. Granted, he bought the biggest battery pack possible — 250 kWh — and is using a standard 120-volt wall outlet and the stock Hummer charging dongle, which adds one mile (1.6 km) to the vehicle’s range every hour. The owner doesn’t actually seem all that surprised by the results, nor does he seem particularly upset by it; he appears to know enough about the realities of EVs to recognize the need for a Level 2 charger. That entails extra expense, of course, both to procure the charger and to run the 240-volt circuit needed to power it, not to mention paying for the electricity. It’s a problem that will only get worse as more chargers are added to our creaky grid; we’re not sure what the solution is, but we’re pretty sure it’ll be found closer to the engineering end of the spectrum than the political end.

Continue reading “Hackaday Links: January 22, 2023” →

NASA Mission Off To Rough Start After Astra Failure

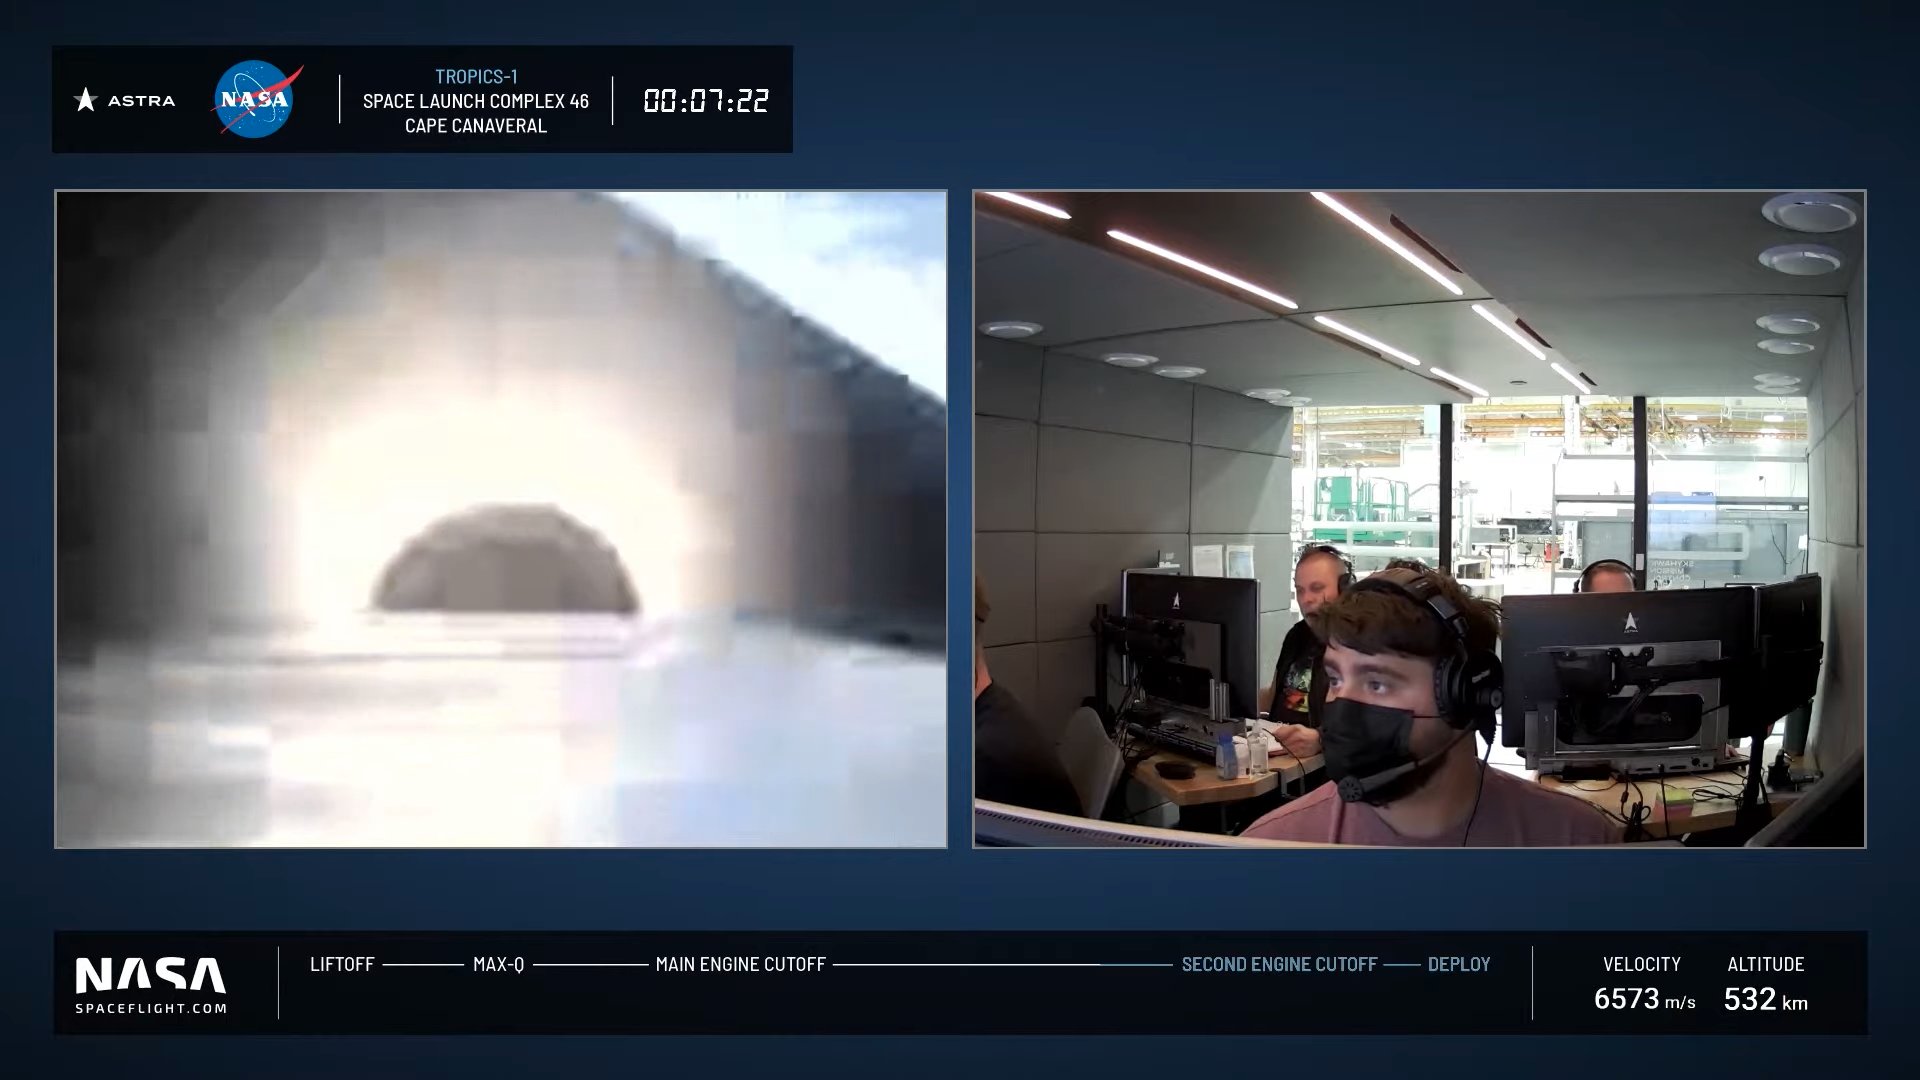
When Astra’s diminutive Rocket 3.3 lifted off from its pad at the Cape Canaveral Space Force Station on June 12th, everything seemed to be going well. In fact, the mission was progressing exactly to plan right up until the end — the booster’s second stage Aether engine appeared to be operating normally until it abruptly shut down roughly a minute ahead of schedule. Unfortunately, orbital mechanics are nothing if not exacting, and an engine burn that ends a minute early might as well never have happened at all.

According to the telemetry values shown on-screen during the live coverage of the launch, the booster’s upper stage topped out at a velocity of 6.573 kilometers per second, well short of the 7.8 km/s required to attain a stable low Earth orbit. While the video feed was cut as soon as it was clear something had gone wrong, the rigid physics of spaceflight means there’s little question about the sequence of events that followed. Without the necessary energy to stay in orbit, the upper stage of the rocket would have been left in a sub-orbital trajectory, eventually reentering the atmosphere and burning up a few thousand kilometers downrange from where it started.

An unusual white plume is seen from the engine as it shuts down abruptly.

Of course, it’s no secret that spaceflight is difficult. Doubly so for startup that only has a few successful flights under their belt. There’s no doubt that Astra will determine why their engine shutdown early and make whatever changes are necessary to ensure it doesn’t happen again, and if their history is any indication, they’re likely to be flying again in short order. Designed for a Defense Advanced Research Projects Agency (DARPA) competition that sought to spur the development of cheap and small rockets capable of launching payloads on short notice, Astra’s family of rockets have already demonstrated unusually high operational agility.

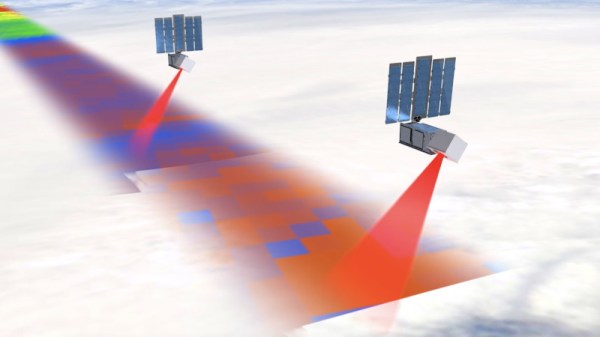
Astra, and the Rocket 3.3 design, will live to fly again. But what of the payload the booster was due to put into orbit? That’s a bit more complicated. This was the first of three flights that were planned to assemble a constellation of small CubeSats as part of NASA’s TROPICS mission. The space agency has already released a statement saying the mission can still achieve its scientific goals, albeit with reduced coverage, assuming the remaining satellites safely reach orbit. But should one of the next launches fail, both of which are currently scheduled to fly on Astra’s rockets, it seems unlikely the TROPICS program will be able to achieve its primary goal.

So what exactly is TROPICS, and why has NASA pinned its success on the ability for a small and relatively immature launch vehicle to make multiple flights with their hardware onboard? Let’s take a look.

Continue reading “NASA Mission Off To Rough Start After Astra Failure” →

Hackaday Links Column Banner

Hackaday Links: November 15, 2020

Now that we drive around cars that are more like mobile data centers than simple transportation, there’s a wealth of data to be harvested when the inevitable crashes occur. After a recent Tesla crash on a California highway, a security researcher got a hold of the car’s “black box” and extracted some terrifying insights into just how bad a car crash can be. The interesting bit is the view of the crash from the Tesla’s forward-facing cameras with object detection overlays. Putting aside the fact that the driver of this car was accelerating up to the moment it rear-ended the hapless Honda with a closing speed of 63 MPH (101 km/h), the update speeds on the bounding boxes and lane sensing are incredible. The author of the article uses this as an object lesson in why Level 2 self-driving is a bad idea, and while I agree with that premise, the fact that self-driving had been disabled 40 seconds before the driver plowed into the Honda seems to make that argument moot. Tech or not, someone this unskilled or impaired was going to have an accident eventually, and it was just bad luck for the other driver.

Last week I shared a link to Scan the World, an effort to 3D-scan and preserve culturally significant artifacts and create a virtual museum. Shortly after the article ran we got an email from Elisa at Scan the World announcing their “Unlocking Lockdown” competition, which encourages people to scan cultural artifacts and treasures directly from their home. You may not have a Ming Dynasty vase or a Grecian urn on display in your parlor, but you’ve probably got family heirlooms, knick-knacks, and other tchotchkes that should be preserved. Take a look around and scan something for posterity. And I want to thank Elisa for the link to the Pompeiian bread that I mentioned.

The Defense Advanced Research Projects Agency (DARPA)has been running an interesting challenge for the last couple of years: The Subterranean (SubT) Challenge. The goal is to discover new ways to operate autonomously below the surface of the Earth, whether for mining, search and rescue, or warfare applications. They’ve been running different circuits to simulate various underground environments, with the most recent circuit being a cave course back in October. On Tuesday November 17, DARPA will webcast the competition, which features 16 teams and their autonomous search for artifacts in a virtual cave. It could make for interesting viewing.

If underground adventures don’t do it for you, how about going upstairs? LeoLabs, a California-based company that specializes in providing information about satellites, has a fascinating visualization of the planet’s satellite constellation. It’s sort of Google Earth but with the details focused on low-earth orbit. You can fly around the planet and watch the satellites whiz by or even pick out the hundreds of spent upper-stage rockets still up there. You can lock onto a specific satellite, watch for near-misses, or even turn on a layer for space debris, which honestly just turns the display into a purple miasma of orbiting junk. The best bit, though, is the easily discerned samba-lines of newly launched Starlink satellites.

A doorbell used to be a pretty simple device, but like many things, they’ve taken on added complexity. And danger, it appears, as Amazon Ring doorbell users are reporting their new gadgets going up in flame upon installation. The problem stems from installers confusing the screws supplied with the unit. The longer wood screws are intended to mount the device to the wall, while a shorter security screw secures the battery cover. Mix the two up for whatever reason, and the sharp point of the mounting screw can find the LiPo battery within, with predictable results.

And finally, it may be the shittiest of shitty robots: a monstrous robotic wolf intended to scare away wild bears. It seems the Japanese town of Takikawa has been having a problem with bears lately, so they deployed a pair of these improbable looking creatures to protect themselves. It’s hard to say what’s the best feature: the flashing LED eyes, the strobe light tail, the fact that the whole thing floats in the air atop a pole. Whatever it is, it seems to work on bears, which is probably good enough. Take a look in the video below the break.

Continue reading “Hackaday Links: November 15, 2020” →

Wheels Or Legs? Why Not Both?

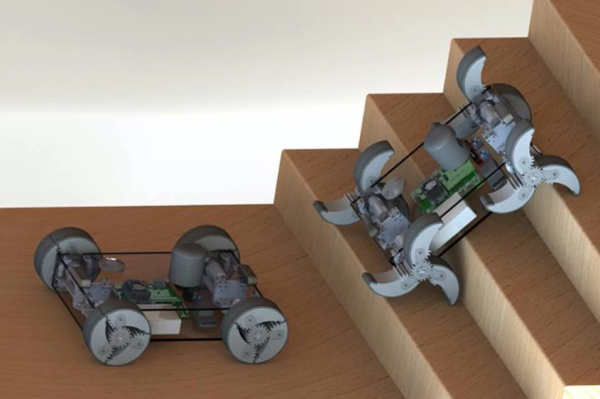
Out of the thousands of constraints and design decisions to consider when building a robot, the way it moves is perhaps one of the most fundamental. The method of movement constrains the design and use case for the robot perhaps more than any other parameter. A team of researchers at Texas A&M led by [Kiju Lee] is trying to have their cake and eat it too by building a robot with wheels that transform into legs, known as a-WaLTR (Adaptable Wheel-and-Leg Transformable Robot).

a-WaLTR was designed to conquer one of wheeled robots’ biggest obstacles: stairs. By adding a bit of smarts to determine whether a given terrain is better handled by wheels or legs, a-WaLTR can convert its segmented wheels into simple legs. Rather than implemented complex and error-prone articulated legs, the team stuck with robust appendages that remind us a little of whegs.

The team will show off their prototype at DARPA OFFSET Sprint-5 in February 2021, which is a program focused on building robots that can form adaptive human-swarm teams.

Thanks to the rise of 3D printers and hobbyist electronics there are more open-source experimental robot designs than ever. We’ve seen smaller versions of the famous Boston Dynamics’ Spot as well as simpler quadruped bots with more servos. a-WaLTR isn’t the first transforming robot we’ve seen, but we’re looking forward to seeing more unique takes on robotic locomotion in the future.

Thanks to [Qes] for sending this one in!