34C3: Ultimate Apollo Guidance Computer Talk

While it might not be as exciting as the Saturn V rocket itself, the Apollo Guidance Computer (AGC) was one of the most important developments of the entire Apollo program. While comically underwhelming compared to modern hardware, the AGC was nothing short of revolutionary when it was developed in the 1960’s. Before the AGC, the smallest computers were about the size of a refrigerator and consumed hundreds of watts; both big problems if you’re trying to pack them into a relatively tiny space capsule with limited resources. Not only did the AGC get humanity to the Moon and back, but it also redefined the state of the art for microcomputers, paving the way for the desktop systems of the 1970’s.

That said, the design and operation of the AGC is downright bizarre to modern eyes; it comes from a time of limitations we can hardly fathom. With this in mind, [Michael Steil] and [Christian Hessmann] put together “The Ultimate Apollo Guidance Computer Talk” forĀ 34C3.

This hour-long presentation walks viewers through every aspect of not only the AGC itself, but how it interacted with the Saturn V rocket and the overall lunar mission. Even if you aren’t enough of a vintage computing aficionado to appreciate the complexities of core rope memory, the presentation gives a fascinating look at the gritty details of one of humanity’s greatest achievements.
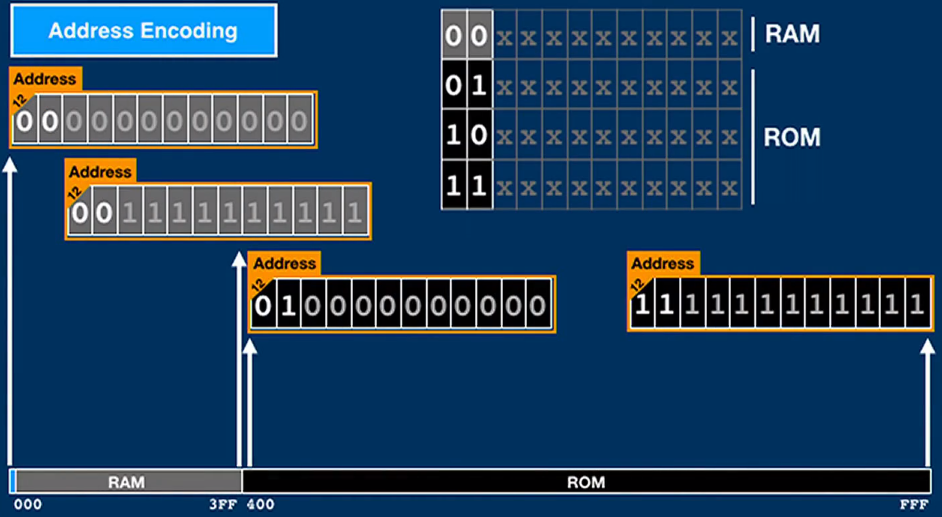
Though very slick and easy to understand graphics, [Michael] and [Christian] break down the alien world of the AGC. Even if a lot of this part of the presentation goes over your head, just listen for the sounds of laughter or applause from the audience: that’s when you’re looking at something really off-the-wall.

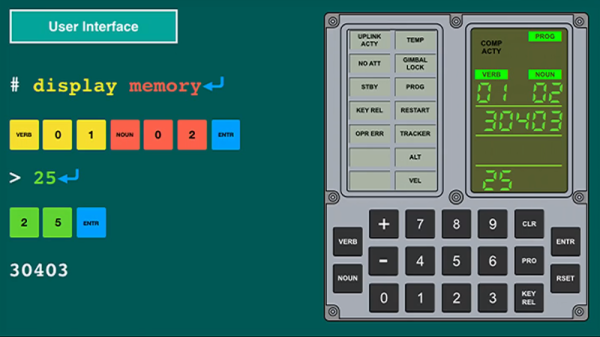
Of particular note during this presentation is the explanation of how the astronauts actually interacted with the AGC. The AGC’s display and keyboard (referred to as DSKY) may seem rather obtuse even to those who used to hack on a VT100, butĀ [Michael] and [Christian] explain how it’s not quite as complex as it seems. Comparing the input and output of the DSKY with what we would see on a more contemporary command line interface, the presentation makes the case that it’s actually a very straightforward way of talking to the computer.

There’s also a complete breakdown of the different phases of the Apollo mission from launch to landing, explaining what the AGC would be doing at any given time. The DSKY is overlaid on actual footage from the Apollo missions, giving a unique perspective as to what the astronauts would see on their computer during iconic moments such as stage separation or lunar touchdown.

If this presentation has you hungry for more Apollo-era computer technology, we’ve covered plenty of projects to keep you occupied. From building a replica DSKY to leisurely paging through the printed version of the AGC’s source code.
34C3: Hacking Into A CPU’s Microcode

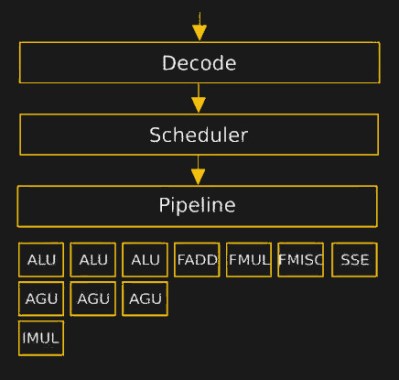
Inside every modern CPU since the Intel Pentium fdiv bug, assembly instructions aren’t a one-to-one mapping to what the CPU actually does. Inside the CPU, there is a decoder that turns assembly into even more primitive instructions that are fed into the CPU’s internal scheduler and pipeline. The code that drives the decoder is the CPU’s microcode, and it lives in ROM that’s normally inaccessible. But microcode patches have been deployed in the past to fix up CPU hardware bugs, so it’s certainly writeable. That’s practically an invitation, right? At least a group from the Ruhr University Bochum took it as such, and started hacking on the microcode in the AMD K8 and K10 processors.

The hurdles to playing around in the microcode are daunting. It turns assembly language into something, but the instruction set that the inner CPU, ALU, et al use was completely unknown. [Philip] walked us through their first line of attack, which was essentially guessing in the dark. First they mapped out where each x86 assembly codes went in microcode ROM. Using this information, and the ability to update the microcode, they could load and execute arbitrary microcode. They still didn’t know anything about the microcode, but they knew how to run it.
So they started uploading random microcode to see what it did. This random microcode crashed almost every time. The rest of the time, there was no difference between the input and output states. But then, after a week of running, a breakthrough: the microcodeĀ XOR’ed. From this, they found out the syntax of the command and began to discover more commands through trial and error. Quite late in the game, they went on to take the chip apart and read out the ROM contents with a microscope and OCR software, at least well enough to verify that some of the microcode operations were burned in ROM.

The result was 29 microcode operations including logic, arithmetic, load, and store commands — enough to start writing microcode code. The first microcode programs written helped with further discovery, naturally. But before long, they wrote microcode backdoors that triggered when a given calculation was performed, and stealthy trojans that exfiltrate data encrypted or “undetectably” through introducing faults programmatically into calculations. This means nearly undetectable malware that’s resident inside the CPU. (And you think the Intel Management Engine hacks made you paranoid!)

[Benjamin] then bravely stepped us through the browser-based attack live, first in a debugger where we could verify that their custom microcode was being triggered, and then outside of the debugger where suddenly xcalc popped up. What launched the program? Calculating a particular number on a website from inside an unmodified browser.

He also demonstrated the introduction of a simple mathematical error into the microcode that made an encryption routine fail when another particular multiplication was done. While this may not sound like much, if you paid attention in the talk on revealing keys based on a single infrequent bit error, you’d see that this is essentially a few million times more powerful because the error occurs every time.

The team isn’t done with their microcode explorations, and there’s still a lot more of the command set left to discover. So take this as a proof of concept that nearly completely undetectable trojans could exist in the microcode that runs between the compiled code and the CPU on your machine. But, more playfully, it’s also an invitation to start exploring yourself. It’s not every day that an entirely new frontier in computer hacking is bust open.

Hackaday Superconference Talk: Cory Grosser

When we look at a product or project here at Hackaday it is likely that our interest has been caught by its internal technology, or perhaps by its functionality. It is easy to forget that there is another angle to each and every item that graces these pages, and it is every bit as important as those we have already mentioned. Aesthetic design, the look and feel of a product, is something that is so often overlooked.

One of the speakers at the Hackaday Superconference was [Cory Grosser], one of America’s leading independent product designers, and the designer of the Supplyframe Design Lab in which the Superconference was being held. In his talk he covered some of the principles of design, touching on its psychology and its purpose in creating a successful product. In doing so he delivered a fascinating talk full of insights into the design of products both famous and somewhat obscure.

Continue reading “Hackaday Superconference Talk: Cory Grosser” →

34C3: The First Day Is A Doozy

It’s 5 pm, the sun is slowly setting on the Leipzig conference center, and although we’re only halfway through the first day, there’s a ton that you should see. We’ll report some more on the culture of the con later — for now here’s just the hacks. Continue reading “34C3: The First Day Is A Doozy” →

Hackaday At 34C3

It’s that time of year. While the rest of the Christmas-celebrating world sits around and plays with the toys that they got out from under the tree, German nerds head off to the biggest European hacker con: the 34th annual Chaos Communications Congress, running Dec. 27th through 30th.

The CCC is both a grandparent among hacker cons, and the most focused on using technology to improve the world and bringing folks together. (The “communications” in the name is a dead giveaway.) This year’s motto, “tuwat!” is slangy-dialecty for “do something!” and is call to get up off the couch and use your super-powers for good.

If you can’t get over to Leipzig to join us, you’ll be able to read our extensive coverage starting up shortly after the opening ceremonies, and probably stretching well into 2018. And since the CCC media folks manage to stream every talk, hackers all over the world can follow along live. Most talks are in English, so get together with folks in your hackspace and have a video night!

And if you are in Leipzig, be on the lookout for [Elliot] who will be wandering around, attending workshops, and writing down as much as possible. Show me something cool, rave about a particularly good talk, or just say “hi”.

Fairy Dust clipart courtesy [sonoftroll].

Mike Harrison At The Superconference: Flying LCD Pixels

Mike Harrison, perhaps better known to us as the titular Mike of YouTube channel mikeselectricstuff, is a hardware hacking genius. He’s the man behind this year’s Superconference badge, and his hacks and teardowns have graced our pages many times. The best thing about Mike is that his day job is designing implausibly cool one-off hardware for large-scale art installations. His customers are largely artists, which means that they just don’t care about the tech as long as it works. So when he gets together with a bunch of like-minded hacker types, he’s got a lot of pent-up technical details that he just has to get out. Our gain.

He’s been doing a number of LCD installations lately. And he’s not using the standard LCD calculator displays that we all know and love, although the tech is exactly the same, but is instead using roughly 4″ square single pixels. His Superconference talk dives deep into the behind-the-scenes cleverness that made possible a work of art that required hundreds of these, suspended by thin wires in mid-air, working together to simulate a flock of birds. You really want to watch this talk.


Continue reading “Mike Harrison At The Superconference: Flying LCD Pixels” →

Alan Yates: Introduction To Vacuum Technology

When we mention vacuum technology, it’s not impossible that many of you will instantly turn your minds to vacuum tubes, and think about triodes, or pentodes. But while there is a lot to interest the curious in the electronics of yesteryear, they are not the only facet of vacuum technology that should capture your attention.

When [Alan Yates] gave his talk at the 2017 Hackaday Superconference entitled “Introduction To Vacuum Technology”, he was speaking in a much more literal sense. Instead of a technology that happens to use a vacuum, his subject was the technologies surrounding working with vacuums; examining the equipment and terminology surrounding them while remaining within the bounds of what is possible for the experimenter. You can watch it yourself below the break, or read on for our precis.

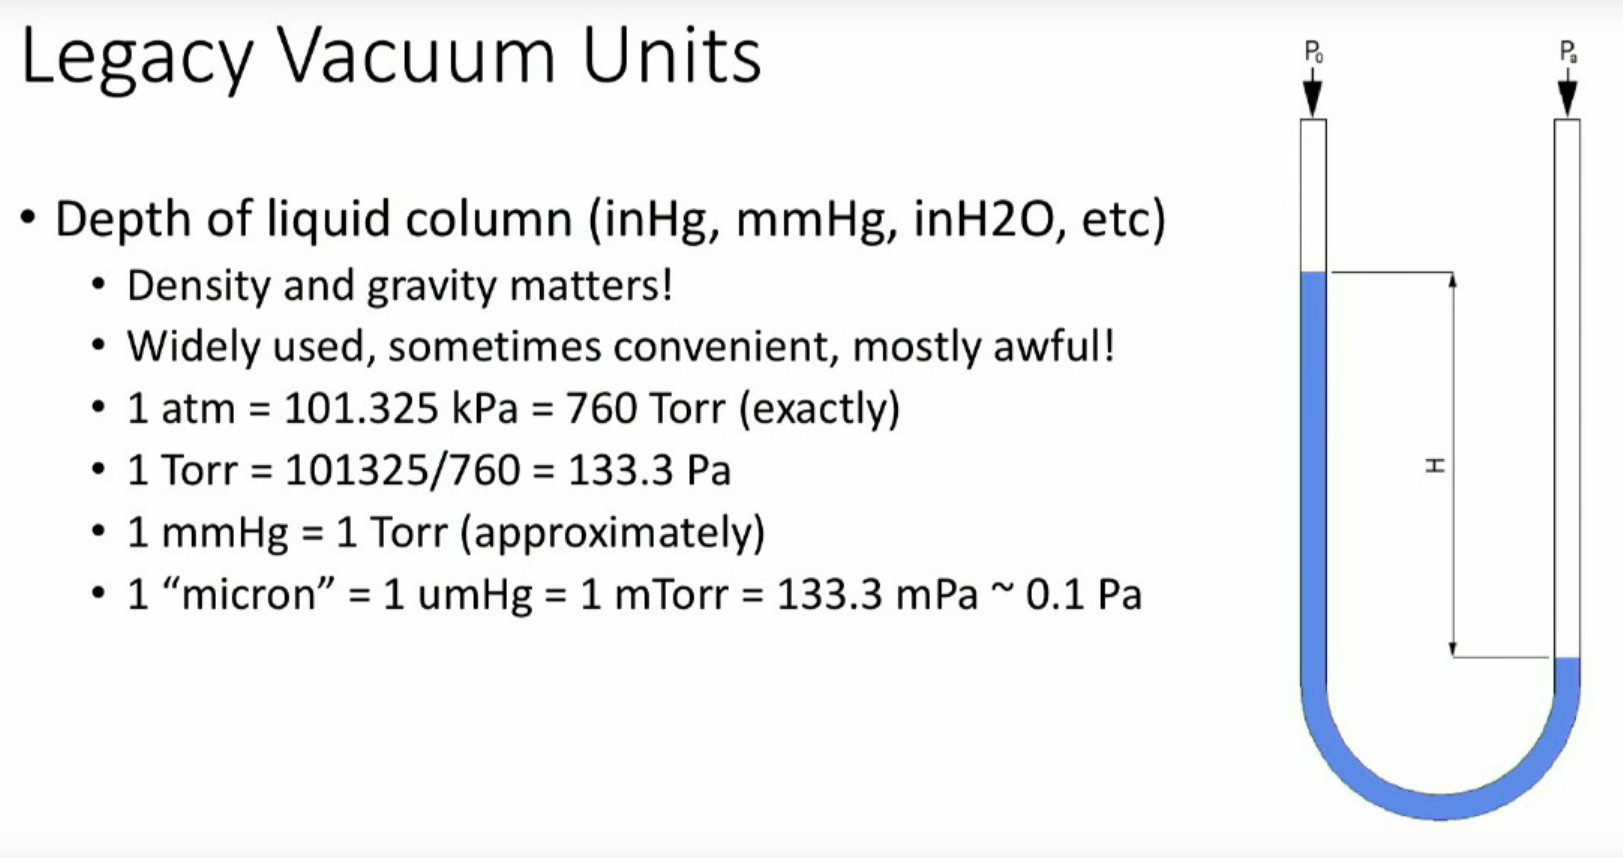
In the first instance, he introduces us to the concept of a vacuum, starting with the work of [Evangelista Torricelli] on mercury barometers in the 17th century Italy, and continuing to explain how pressure, and thus vacuum, is quantified. Along the way, he informs us that a Pascal can be explained in layman’s terms as roughly the pressure exerted by an American dollar bill on the hand of someone holding it, and introduces us to a few legacy units of vacuum measurement.

In classifying the different types of vacuum he starts with weak vacuum sources such as a domestic vacuum cleaner and goes on to say that the vacuum he’s dealing with is classified as medium, between 3kPa and 100mPa. Higher vacuum is beyond the capabilities of the equipment available outside high-end laboratories.

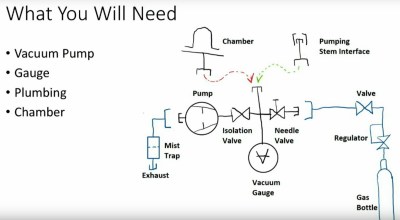
Introduction over, he starts on the subject of equipment with a quick word about safety, before giving an overview of the components a typical small-scale vacuum experimenter’s set-up. We see the different types of vacuum gauges, we’re introduced to two different types of service pumps for air conditioning engineers, and we learn about vacuum manifolds. Tips such as smelling the oil in a vacuum pump to assess its quality are mentioned, and how to make a simple mist trap for a cheaper pump. There is a fascinating description of the more exotic pumps for higher vacuums, even though these will be out of reach of the experimenter it is still of great interest to have some exposure to them. He takes us through vacuum chambers, with a warning against cheap bell jars not intended for vacuum use, but suggests that some preserving jars can make an adequate chamber.

We are then introduced to home-made gas discharge tubes, showing us a home-made one that lights up simply by proximity to a high voltage source. Something as simple as one of the cheap Tesla coil kits to be found online can be enough to excite these tubes, giving a simple project for the vacuum experimenter that delivers quick results.

Finally, we’re taken through some of the tools and sundries of the vacuum experimenter, the different types of gas torches for glass work, and consumables such as vacuum grease. Some of them aren’t cheap, but notwithstanding those, he shows us that vacuum experiments can be made within a reasonable budget.

Continue reading “Alan Yates: Introduction To Vacuum Technology” →