On Chip Debug For (Some) MicroPython

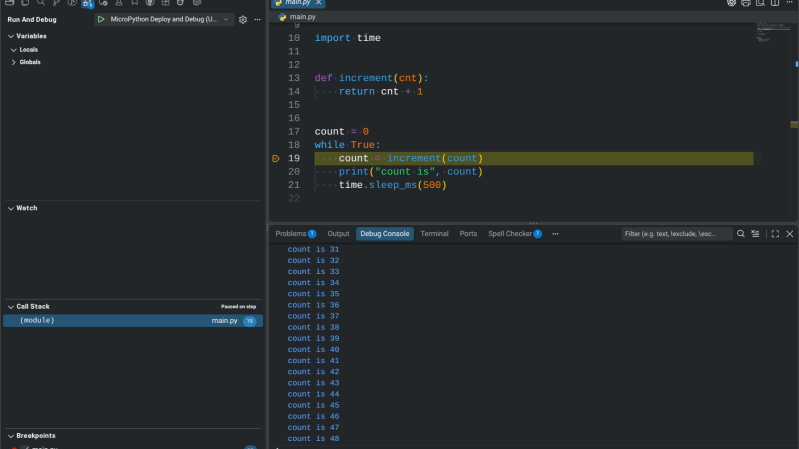
If you’ve used MicroPython much, you know that debugging usually amounts to printing a few things out, trying your code out, and then repeating. But [ghi-electronics] wants you to have full on-chip source-code debugging in Visual Studio. You don’t need anything special to use it — just a supported MicroPython host and the same USB cable you program with now.

The downside is that you either have to build a custom MicroPython image and flash it or use one that they include. They support several Raspberry Pi Pico versions and ESP32 chips, as well. However, at least one “odd” Pico we had lying around wouldn’t take the firmware. A stock one did, and it worked as you would expect. A little more investigation showed the odd Pico (an RP2040 GEEK) probably did take the firmware; it just produced an error during setup. There is a known problem with Linux and the ESP32-S3 having similar behavior.

Continue reading “On Chip Debug For (Some) MicroPython”

This Week In Security: Microsoft On Microsoft, Register Your Domains, Linux On ARM, And FreeBSD Joins The File Cache Club

Supply chain attacks continue, with Microsoft’s own open source Azure repositories being automatically disabled by GitHub following a compromise of the packages by the Miasma worm.

OpenSourceMalware reports that the infection resulted in 73 Microsoft-related package repositories being flagged and taken offline in a little over a minute by the GitHub automated security system, with over 40 repositories being related to Azure and the rest distributed across the Microsoft organization.

The center of the infection appears to be the Microsoft Durabletask package, which was previously compromised in May and used to push infected packages to PyPi. Considering that all of the supply chain worms also steal credentials for every service they can find in the build or developer environment they infect, it seems likely that credentials stolen in the original attack were never properly disabled.

Disabling the repositories can help stem the infected packages and GitHub actions from spreading and infecting more organizations, but of course any build processes depending on those packages will not function. In May, the Durabletask package showed over 400,000 downloads per month.

The OpenSourceMalware report includes a full list of the impacted repositories.

Microsoft Fixes GitHub Token Exploit

Microsoft has finally fixed a bug in GitHub which could steal a GitHub authentication token with access to all of an accounts repositories via the embedded web-based VSCode editor which is part of GitHub itself.

Ammar Askar discovered the bug and discusses it on their blog; by manipulating the sandboxed VS Code into treating an embedded web view as user keyboard strokes, it is possible to to cause it to install a VS Code extension which is then used to exfiltrate the GitHub authentication tokens of the user using the embedded VS Code instance.

Continue reading “This Week In Security: Microsoft On Microsoft, Register Your Domains, Linux On ARM, And FreeBSD Joins The File Cache Club”

This Week In Security: AI Generated Reports, More AI Generated Reports, GitHub Chaos, And More Linux Vulnerabilities

Google’s Project Zero demonstrates a new zero-click exploit for the Pixel 10 phones, showing a full escalation from remote to kernel without user interaction. During the investigation Project Zero found unprotected memory access from userspace in the Tensor G5 video processing chip driver, which allows direct write access to kernel memory.

Using previously discovered flaws in media decoding components — in this case CVE-2025-54957 in the Dolby digital audio decoder — Project Zero modified a Pixel 9 attack to work on the Pixel 10, despite newer protections built into the hardware to harden the system against memory corruption.

The author’s takeaway is mixed. Once the bug on Pixel 9 was reported, one could hope that the Android team would look into similar bugs in their newer systems. On the positive side, though, Project Zero reported the vulnerabilities to the Android team in November 2025 and they were patched in February of 2026, 71 days later. That’s 19 days short of the 90-day timeline.

Continue reading “This Week In Security: AI Generated Reports, More AI Generated Reports, GitHub Chaos, And More Linux Vulnerabilities”