This Week In Security: New Spectre Attacks, Crushing Quantity Of Linux Vulns, Google Gets Too Much AI, And Hacking Lawnmowers

Just-in-time, or JIT, compilation could be considered a fundamental backbone of modern computing.  JIT compilation turns scripting languages like JavaScript or intermediary binary forms like Web Assembly into native code on the fly, giving web apps, and things that are web apps under the covers like Electron-based tools, near native speed.  A new paper explores leveraging JIT systems to revive Spectre-v2 attacks against processors.

Most modern processors gain performance by using a trick called “speculative execution”.  The processor guesses the likely result of a compare, and begins executing some of the next instructions before the results are actually known.  If the processor guessed right, things continue and there is a speed gain because it can jump ahead, but if the processor guessed wrong, any instructions that were run and any side effects of running them are discarded and execution resumes on the actual path.  In theory, anyhow.

In practice, the Spectre class of attacks targets branch prediction. It was discovered that when the wrong branch was chosen, not all of the results were truly hidden; Patterns of failures in guessing branches can be used to leak behavior processing encryption keys and other activities. The attacks evolved with the research dubbed Spectre-V2, which showed that non-privileged contexts, like non-root users and virtual machines, could poison the instruction prediction and use it to read arbitrary memory.  Fixes to the Linux kernel and other platforms were required to mitigate the worst of the effects.

The paper shows that by using self-modifying code in the JIT, the processor can be tricked into loading cached versions of the instructions.  The fixes to the kernel to prevent Spectre attacks include identifying malicious code patterns that attack the branch prediction, and stopping or changing them:  By causing the CPU to execute the cached copy of instructions instead of the live copy, the attack ignores the fixed instructions entirely and can attack the branch prediction algorithm.

To prove the attack is feasible in the real world, the researchers targeted several JIT compilers, including the SpiderMonkey JavaScript engine used by Firefox, the eBPF JIT found in the Linux kernel, and GraalVM, the JIT used in Python.  They found success with each, demonstrating that the attack is at least plausible.

Research like this is unlikely to be an instant world-melter, and will help find possible mitigations in the future to prevent these sorts of attacks.  Operating systems that support a high-security “lock-down” mode, like macOS and iOS, often disable JIT entirely, out of concern about these sorts of attacks.  There’s probably no need to start disabling JIT on every system, but attacks like these have a tendency to evolve.
Continue reading “This Week In Security: New Spectre Attacks, Crushing Quantity Of Linux Vulns, Google Gets Too Much AI, And Hacking Lawnmowers” →

This Week In Security: ShinyHunters Won’t Dox The FBI, Pentagon Data Stolen, And OBS Vulnerable

404 Media reports that the ShinyHunters group who stole multiple terabytes of FBI employee data say they do not plan to release the data.

Known for ransomware and extortion of innumerable companies and government agencies, ShinyHunters used a zero-day vulnerability in Oracle PeopleSoft to compromise the employment site of the FBI and pivot into scraping the content of FBI AWS instances, claiming to have the full employment and health data of all FBI agents, employees, and spouses.

The hacker group took exception to an FBI press release that claimed that the group over-stated stolen data and that they directly harass victims and victim’s families.  The group publicized the FBI data breach, demanding a retraction of the statements, and it was generally assumed that the group would follow their typical methods of releasing the data publicly if the demands were not met.

The group has told 404 media that they had always agreed internally to not release the stolen data, saying “This was all a marketing campaign to protect our business and actively combat disinformation”.  Meanwhile the FBI continues the investigation, and Shiny Hunters may be hoping to defer some of the ire.

Continue reading “This Week In Security: ShinyHunters Won’t Dox The FBI, Pentagon Data Stolen, And OBS Vulnerable” →

This Week In Security: FBI Gets Hacked, Muse Vulnerable To ClickFix, Popular Rust Developers At Risk, And New Attacks Against RSA

The prolific ShinyHunters group has announced it used a zero-day vulnerability in Oracle PeopleSoft to exploit the FBI jobs website and gain access to the AWS GovCloud instances and dump 2 TB of employee data. GovCloud being a special, locked-down version of the Amazon Web Services cloud for US government users.

ShinyHunters has previously been involved in dozens of high-profile hacks and ransomware incidents.  Some of the highest-profile incidents include Jaguar-Land Rover, causing a measurable impact on the UK GDP, Grubhub, Carnival Cruise Lines, Rockstar Games, and multiple universities and educational institutions, casinos, and other government agencies.  ShinyHunters has also been credited with the hack of the Canvas educational program in the spring of 2026 where data including test results and chat logs of hundreds of millions of students, teachers, and staff was stolen.  ShinyHunters has generally been identified as an international group of criminals, often teenagers, who will demand a BitCoin ransom of several million US dollars, with the threat of the stolen data being leaked if the victims do not pay.

On May 15, 2026 the FBI released a bulletin on the activities of ShinyHunters, focusing on the Canvas educational hack.  In the report, the FBI said that the group uses “harassment strategies, sending threatening text messages and phone calls to victims and their family members”.  ShinyHunters says that this is not accurate, and that they will release the FBI employee data, including information of employees and their family members, if the agency does not retract the statements, telling The Register “I have been doing my very best to combat these allegations, and this is the best way to do it”.

Continue reading “This Week In Security: FBI Gets Hacked, Muse Vulnerable To ClickFix, Popular Rust Developers At Risk, And New Attacks Against RSA” →

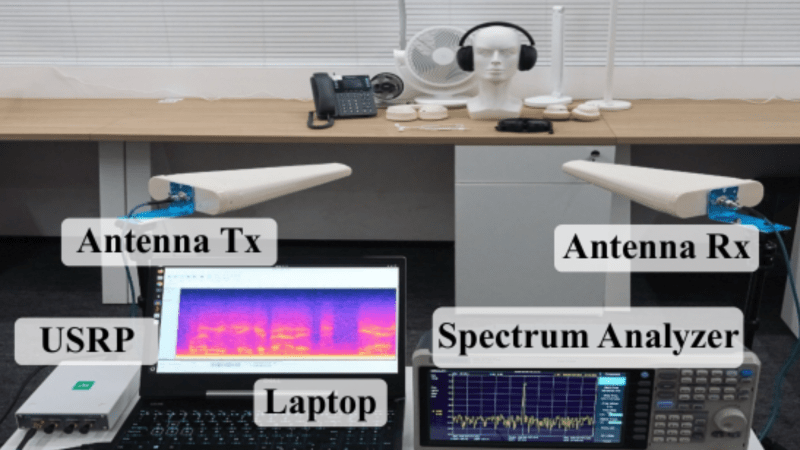
A laptop is shown set up on a desk next to a spectrum analyser, an SDR, and two antennas. The antennas are aimed toward assorted electronics, including headphones and a phone handset.

Reviving TEMPEST Attacks With An Injected Signal

TEMPEST attacks are often the most effective way to break air-gapped security: rather than directly accessing a computer, the attacker records the system’s unintended radio emissions and uses them to reconstruct its internal operations. This kind of attack was much more effective in the days of noisy, high-voltage CRT displays, and has gradually become less effective as electronics migrate to quieter, less powerful components. A group of researchers, however, has found that even modern electronics can become effective TEMPEST transmitters when irradiated with an RF signal.

The RF a device emits depends on the unintentional antennas in its internal structure. These are difficult to eliminate, and it’s usually not worth the effort; they’re usually small enough that they only effectively radiate at much higher frequencies than the electronics carry. The researchers’ technique, called InjectEave, radiated these electronics with a radio frequency tuned to their internal antennas, injecting that frequency into the circuit. Nonlinear electronic components, such as amplifiers, then mix the injected frequency with the internal signal, creating RF sidebands. This mixed signal then radiates out of the device and can be picked up and demodulated to recover the device’s internal signal.

Continue reading “Reviving TEMPEST Attacks With An Injected Signal” →

Laser Your Way Into Debug Mode On The RP2350

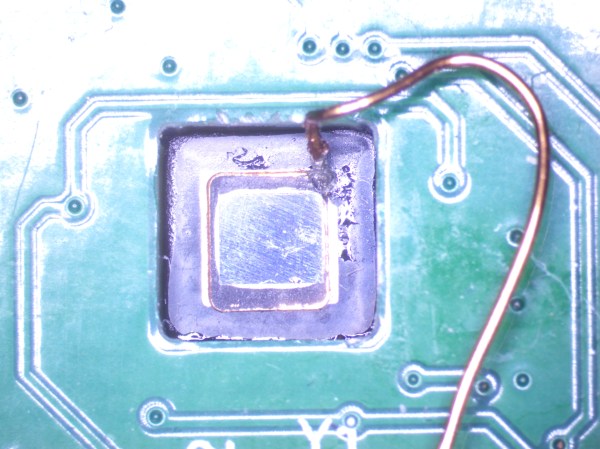
The RP2350 is actually a pretty secure chip, all things considered. It has secure boot, ARMv8’s TrustZone to split secure and non-secure execution, and you can permanently disable debug — the Pi Foundation even included glitch detection, meaning the traditional ‘zap the chip until it obeys’ technique is blocked. That’s why the [Ledger Donjon] security team went full Bond Villain and strapped everyone’s favourite fruit-flavoured microcontroller to a table with a slowly-approaching laser beam.

Continue reading “Laser Your Way Into Debug Mode On The RP2350” →

This Week In Security: Flock Cameras Are Old, Microsoft Patches Patches, And Researchers Attack SSH

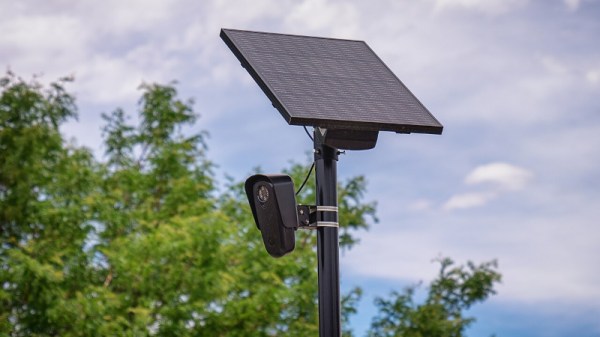
Leak site Distributed Denial of Secrets has released a dump of the filesystems of a Flock camera, and Micah Lee has published a dive into the contents.  Apparently the Flock security model did not include “angry citizens with a hacksaw in the middle of the night” in the physical security category.

The first thing Micah notes is that the Flock hardware runs Android 8.1 (for those not keeping track, the current Android release is Android 17 released in June 2026).  The version of Android running on the Flock camera was last patched in June of 2018, and the Linux kernel (3.18.71) is over nine years out of date, and the 3.18 series went end-of-life in 2019.

You might assume “wouldn’t an operating system this old have known vulnerabilities?”, and you’d be completely right.  Micah calls out two in particular, one in the Qualcomm GPU which allows any program to manipulate kernel memory and gain root (similar, yet simpler, than the spate of kernel vulnerabilities this year that allowed manipulating memory via the disk IO cache), and the “WrongZone” vulnerability which allows a process to escalate to root via socket handling errors.  You might also guess both of these have been patched, and again, you’d be right, in 2021 and 2018 respectively.

Digging deeper, Micah discovers that API keys with access into the Flock infrastructure appear to be hard-coded into the binaries.  Each camera appears to request credentials from an authentication server, using the MAC address of the camera.  After obtaining the credentials from an Okta Auth0 sign-in service, the Flock stores them, in plain text.

Also stored on the camera unencrypted are logs and position data:  The camera dumped to Distributed Denial of Secrets came from a suburb of Milwaukee. Continue reading “This Week In Security: Flock Cameras Are Old, Microsoft Patches Patches, And Researchers Attack SSH” →

Surveillance Camera Security? It’s Completely Flocked!

Surveillance cameras from Flock Safety have become a controversial privacy battleground, as the communities in which they are installed wake up to their sinister potential, and stories roll in of law enforcement professionals abusing their access. One has had its disk contents dumped, and we’ve been treated to some insights courtesy of [Micah Lee]. In short: their approach to security is deeply flawed.

It’s interesting to find that instead of a custom hardened OS, these devices run Android. Not just Android, but Android 8.1, a long out of support version originally released in 2017. This is is the year Flock Safety was founded, which may or may not be coincidental. Like any old version of a widely used operating system it has a host of known vulnerabilities, none of which are patched on this version.

The Android version is small beer compared to the revelation that they contain a hard-coded and very open-access API key that can be used by any mildly curious miscreant to reveal information from any Flock camera using its MAC address. One would hope that a product marketed for use by law enforcement might have paid attention to such a basic lapse, but it seems not. Whether or not this can be corrected by a software upgrade and the leaked key deactivated without turning off the network depends on whether thy can do upgrades tailored to specific devices, but either way we wouldn’t like to be the team tasked with fixing that one.

In a way it’s reassuring that the surveillance apparatus when it came was so incompetently managed, and we hope that these vulnerabilities will have moderated its effect. We’re sure more tasty discoveries will emerge as investigations proceed, and we’ve got the popcorn ready.

Image: Tony Webster, CC BY 2.0.