Oracle CSO To Customers: Leave The Vulnerabilities To Us

[Mary Ann Davidson], chief security officer of Oracle, is having a bad Tuesday. The internet has been alight these past few hours over a blog post published and quickly taken down from oracle’s servers. (archive) We’re not 100% sure the whole thing isn’t a hack of some sort. Based on [Mary’s] previous writing though, it seems to be legit.

The TL;DR version of Mary’s post is that she’s sick and tired of customers reverse engineering Oracle’s code in an attempt to find security vulnerabilities. Doing so is a clear violation of Oracle’s license agreement. Beyond the message, the tone of the blog says a lot. This is the same sort of policy we’re seeing on the hardware side from companies like John Deere and Sony. Folks like [Cory Doctorow] and the EFF are doing all they can to fight it. We have to say that we do agree with [Mary] on one point: Operators should make sure their systems are locked down with the latest software versions, updates, and patches before doing anything else.

[Mary] states that “Bug bounties are the new boy band”, that they simply don’t make sense from a business standpoint. Only 3% of Oracles vulnerabilities came from security researchers. The rest come from internal company testing. The fact that Oracle doesn’t have a bug bounty program might have something to do with that. [Mary] need not worry. Bug Bounty or not, she’s placed her company squarely in the cross-hairs of plenty of hackers out there – white hat and black alike.

All The Unofficial Electronic Badges Of DEF CON

2015 was the year of the unofficial hardware badge at DEF CON 23. There were a ton of different hardware badges designed for the love of custom electronics and I tried to catch up with the designer of each different badge. Here is the collection of images, video demos, and build details for each one I saw this weekend.

Whiskey Pirates

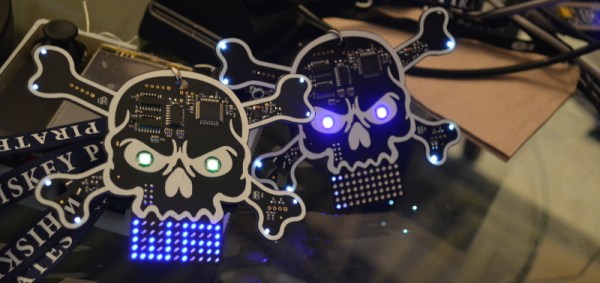
[TrueControl] did a great job with his badge design this year for the Whiskey Pirate Crew. This is a great update from the badge he designed last year, keeping the skull and bones outline. It uses a PSOC4 chip to control a ton of LEDs. The eyes are RGB pixels which are each on their own PCB that is soldered onto the back of the badge, with openings for the LED to show through. Two AA batteries power the board which has a surface-mount LED matrix. The user controls are all capacitive touch. There is a spinner around one eye, and pads for select and back. The NRF24L01 radio operates at 2.4GHz. This badge is slave to commands from last year’s badge. When the two are in the same area the 2015 badges will scroll the nickname of the 2014 badge it “sees”. The piezo element also chirps many different sounds based on the interactions with different badges.

[True] makes design an art form. The matte black solder mask looks fantastic, and he took great care in use of font, size, alignment, and things like letting copper show through for a really stunning piece of hardware art.

Keep reading for ten more great badges seen over the weekend.

Continue reading “All The Unofficial Electronic Badges Of DEF CON” →

amazon dash button

Hacking The Amazon Dash Button To Record Whatever You Want

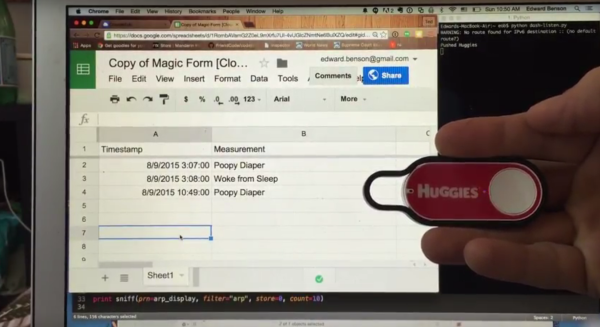
We’re still not too sure if the Amazon Dash button is a brilliant marketing and advertising ploy, or is just downright stupid. But what we do know, is for $5, it’s a lot of hackable tech that could be used for more… useful purposes. The big A sells these dash buttons for one purpose — you push the button and whichever product is assigned to it shows up on your doorstep in a few days. [Ted Benson] wanted them to do more than that so he turned a few dash buttons into a way of tracking his baby’s health!

Apparently, data acquisition of your baby’s wake-up times and poops is useful to identify health patterns. [Ted] tried using some phone apps to keep track of this stuff, but found it would be a lot easier if there was just a big button on the wall or something… which is where he got the idea to make use of the Amazon Dash button.

It’s actually really simple to do. Buy the dash button, do the setup with Amazon… but don’t do the final step: selecting the product you want to order. If you don’t select anything, you won’t order anything…

Continue reading “Hacking The Amazon Dash Button To Record Whatever You Want” →

Millions Of Satellite Receivers Are Low-Hanging Fruit For Botnets

Satellite television is prevalent in Europe and Northern Africa. This is delivered through a Set Top Box (STB) which uses a card reader to decode the scrambled satellite signals. You need to buy a card if you want to watch. But you know how people like to get something for nothing. This is being exploited by hackers and the result is millions of these Set Top Boxes just waiting to form into botnets.

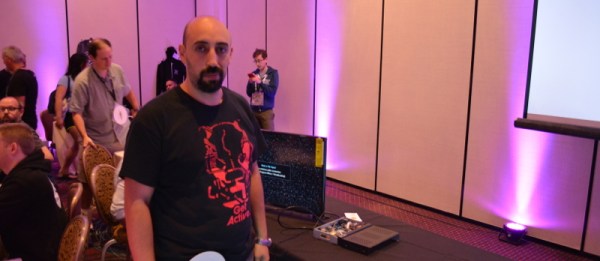
This was the topic of [Sofiane Talmat’s] talk at DEF CON 23. He also gave this talk earlier in the week at BlackHat and has published his slides (PDF).

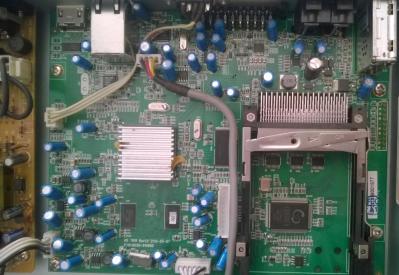
stb-hardwareThe Hardware in Satellite receivers is running Linux. They use a card reader to pull in a Code Word (CW) which decodes the signal coming in through the satellite radio.
An entire black market has grown up around these Code Words. Instead of purchasing a valid card, people are installing plugins from the Internet which cause the system to phone into a server which will supply valid Code Words. This is known as “card sharing”.

On the user side of things this just works; the user watches TV for free. It might cause more crashes than normal, but the stock software is buggy anyway so this isn’t a major regression. The problem is that now these people have exposed a network-connected Linux box to the Internet and installed non-verified code from unreputable sources to run on the thing.

[Sofiane] demonstrated how little you need to know about this system to create a botnet:

  • Build a plugin in C/C++
  • Host a card-sharing server
  • Botnet victims come to you (profit)

It is literally that easy. The toolchain to compile the STLinux binaries (gcc) is available in the Linux repos. The STB will look for a “bin” directory on a USB thumb drive at boot time, the binary in that folder will be automatically installed. Since the user is getting free TV they voluntarily install this malware.

Click through for more on the STB Hacks.

Continue reading “Millions Of Satellite Receivers Are Low-Hanging Fruit For Botnets” →

Cory Doctorow Rails Against The Effect Of DRM And The DMCA

If you weren’t at [Cory Doctorow’s] DEF CON talk on Friday you missed out. Fighting Back in the War on General Purpose Computing was inspiring, informed, and incomparable. At the very lowest level his point was that it isn’t the devices gathering data about us that is the big problem, it’s the legislation that makes it illegal for us to make them secure. The good news is that all of the DEF CON talks are recorded and published freely. While you wait for that to happen, read on for a recap and to learn how you can help the EFF fix this mess.

Continue reading “Cory Doctorow Rails Against The Effect Of DRM And The DMCA” →

BeagleBone Green Hands-On: Lower Price, Same Horsepower

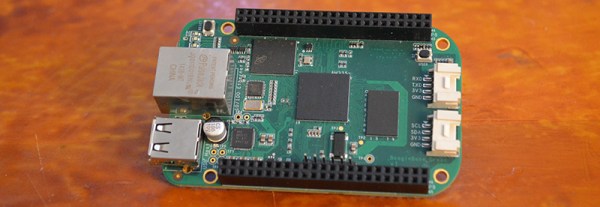
Although the BeagleBone Green was announced at the Bay Area Maker Faire last May, there hasn’t been much said about it on the usual forums and IRC channels. Now, it’s finally out and I got my hands on one of them. Through a cooperation between the BeagleBoard foundation and Seeed Studios, the best small Linux board for doing real work with small Linux boards is now cheaper, a little more modern, and green.

The BeagleBone Green is an update to the venerable BeagleBone Black, the dev board based on a TI ARM Cortex-A8. It’s an extremely capable machine with a few interesting features that make it the perfect device for embedded applications. With the BeagleBone Green, the BB Black gets a small hardware refresh and a drastic reduction in price. If you want to do real work on a Linux board, this is the one to get. Check out the review below for everything that’s been updated, everything that’s the same, and why this is one of the most interesting developments in small Linux boards in recent memory.

Continue reading “BeagleBone Green Hands-On: Lower Price, Same Horsepower” →

Tindie Becomes A Part Of The Hackaday Family

A little over two years ago, we announced that Hackaday became a part of Supplyframe. This was a natural fit: both sides are comprised of hardware engineers, computer scientists and hackers alike. We immediately pooled forces and set out to make Hackaday bigger, with a broader mission. So far, it has been an amazing journey: Hackaday.io is approaching 100,000 registered users, The Hackaday Prize is in its second year, and the Hackaday Store is about to fulfill its 5,000th order.

The main theme behind all of this is fostering collaboration, learning, and providing incentives for everyone in the community to stop procrastinating and try to build something amazing. Hackaday.com is here to inspire, Hackaday.io to help develop projects in the open, and the Hackaday Store is to provide a way to turn passion projects into a self-sustainable lifestyle. While the road to community-powered innovation might not be easy, it’s something we’re all incredibly passionate about, and will continue investing in to further this goal.

With that in mind, we’re very excited to announce that everyone’s favorite hardware marketplace – Tindie, has been acquired by Supplyframe and will be joining the Hackaday family! Apart from the fact that most of us are personal fans of the website, we believe that Tindie fills an important gap in helping projects cross the chasm between prototype and initial production. Crowdfunding provides access to capital for some (and access to laughs for others), but it’s not always the way to go. You might not be ready to quit your day job or take on a project full-time. You might be working on rev1 of the project and want to try the “lean manufacturing” thing. Or maybe you’re building something for your own purposes and have some extras lying around. Tindie is a platform that has helped launch many such projects, and we’re incredibly lucky to have it be a part of Hackaday.

Now what?

Naturally, the question that’s on everyone’s mind is, what happens next? Are we going to mess things up? Paint Tindie in black? Change the fee structure? While we have ideas on things that we could help with, our main goal will be making sure that the Tindie community continues to thrive. The only changes we’re interested in are the ones that make the community stronger. We are fascinated with the challenges surrounding the supply chain and will be looking into tools to help sellers improve margins and ship better products. Hackaday.io and Tindie combined represent the world’s largest repository of (working) Open Hardware products, so we will be looking into more closely integrating the two. We will also make efforts to grow the overall Tindie audience, as every new buyer helps move the community forward.

All of these are some of the ideas, but we’re ultimately looking at you for guidance: things we should do, problems we should attack, dreams of future capabilities.

Wish us luck in this new adventure.

Aleksandar Bradic
CTO
Supplyframe