AI Book Scanning: Just What Is A Rare Book?

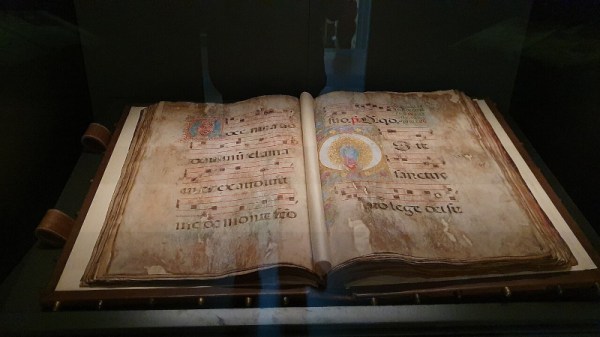
One of the stories of the last few weeks has been that AI companies have been scanning books in very large numbers in order to train their models with content guaranteed to have been written before 2002, and thus AI free. It’s caused some outrage, because of the size of the operation, and because the scanning process is destructive. In particular the phrase being bandied around is that these are rare books, and it’s this phraseology I find problematic. I think it’s time to unpack why that is the case.

It’s Not Book Burning, Folks

Before I worked for Hackaday I had a long career in and around the publishing industry, mostly on the electronic side, but from time to time crossing paths with my colleagues in the world of paper-based publishing. I understand the appeal of a good book, I’ve spend a lot of my life among bibliophiles, and let’s just say I own a few books myself. In particular I understand the symbolism of destroying books, bringing to mind as it does the actions of repressive regimes. I have stood in Bebelplatz in Berlin where the photo of Nazi student organisation members burning the library of Magnus Hirschfeld’s institute was taken in 1933, and if you know me, you’ll have an idea why that’s close to home. But for all that, what the AI companies are doing is not the same thing.

In this case they’re destroying the books for two reasons. Firstly, as I remember from a previous employer in the publishing world, it’s much easier to digitise a stack of papers than it is a bound book. Thus I’m pretty sure that’s one reason they remove the binding before digitising the pages. Then secondly, as I understand it it’s a copyright issue. If they buy a book, digitise it, and destroy the physical copy, they can legitimately claim that only one copy of it exists, and they hope, sidestep copyright claims from publishers. Continue reading “AI Book Scanning: Just What Is A Rare Book?” →
Artificial Intelligence As It Once Was

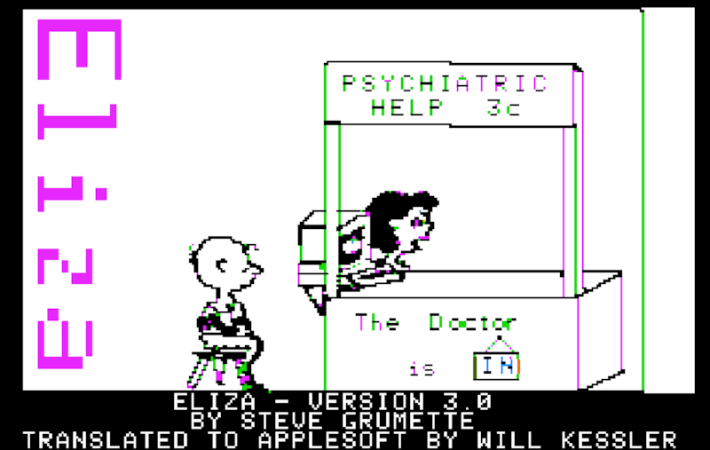
One day, people will look back at what we call Artificial Intelligence and laugh. We do the same thing today, as chat bots totally outstrip what the computer industry called AI up until pretty recently. This didn’t escape curators at the Internet Archive, apparently, and [Jason Scott] tells us about a recent collection, “Vintage Artificial Intelligence.”

These are old software titles that will run for you in emulated machines right in your browser, ranging from somewhere in the 1970s to the 1990s. There’s Eliza, of course. Actually, there are several copies of Eliza. Given how simple it was to write Eliza, it did a pretty good job. Then there are adventure games that are pretty conversational, Lisp, Prolog, which was going to spawn expert systems to replace us all, and Racter, which tried to write fiction.

There was even Alter Ego that was supposed to help you explore life decisions, maybe? There are a couple different versions of even a few versions of Conway’s Game of Life. We aren’t sure that’s ever really been AI, but perhaps it depends on your definition. We’re happy to see Sargon, the chess program, represented.

We didn’t see Hexapawn, which is a shame. We also didn’t see Parry (the paranoid counterpart to Eliza) or that elusive software we remember but can never find that built word chains from text called George.

We’ve written about Eliza before. If you want to experiment with Prolog and you like Pokémon, you’ll appreciate this tutorial.

Machine Learning COFFIES “Hears” Sunspots Before We Can See Them

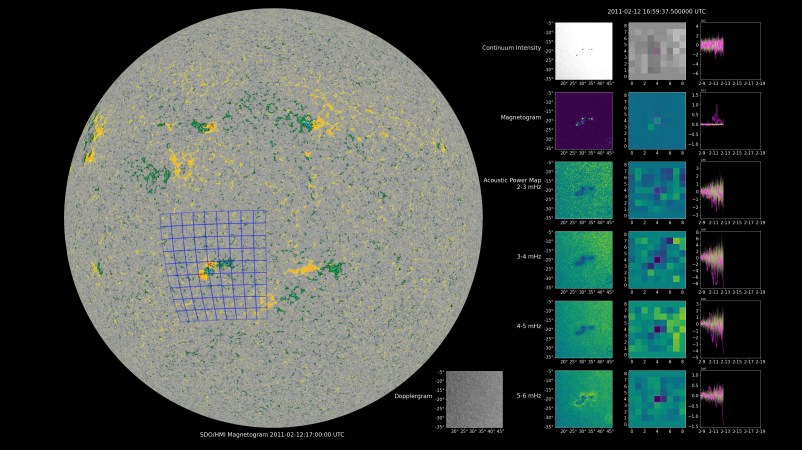
In this age of neural net “AI”, even the most skeptical of Butlerians have to agree that these machine learning models can be very, very good at pattern recognition if nothing else. NASA is on the same page, and to take advantage of that pattern recognition, they’ve built a machine learning module called COFFIES, which stands for Consequence Of Fields and Flows in the Interior and Exterior of the Sun, because at NASA everything is an acronym, or at least a backronym. Like most such names, this one is at least vaguely descriptive: the model is trying to predict what’s going on in the material flows and magnetic fields deep within our local star, and using those inferences is able to predict active regions– that’s sunspots to us chickens — up to 12 hours before they visibly form.

Continue reading “Machine Learning COFFIES “Hears” Sunspots Before We Can See Them” →

This Week In Security: BugTraq, AI Hacks, And Being Dumb On Planes

After a multi-year hiatus, the venerable BugTraq mailing list is back!

For decades, BugTraq was the place where vulnerabilities were disclosed, from the early days when nearly all vendors viewed all security research as a hostile force, through to the modern era of working with vendors to coordinate disclosing bugs. With the rise of bug bounty programs and other social changes, the mailing list slowly died: what started in 1993 ended in 2021 is returning. The new maintainer, Jonathan Brossard, says in his announcement “The mission is unchanged: full disclosure, researcher-first, no corporate filter.”

Don’t Be Dumb on Planes

In the unlikely event anyone here needs to be told: Don’t do dumb things on planes.

It seems that someone coming home from from the DEF CON hacker conference in Las Vegas decided to mess with the in-plane WiFi, and is likely now in the “find out” phase of doing something dumb. There hasn’t been any public followup beyond the original reports: a passenger on a Delta flight leaving Las Vegas brought up a fake WiFi hotspot named “Delta WiFi FAST” to trick other passengers into connecting, and attempted to disable the in-flight WiFi using a denial of service attack.

Continue reading “This Week In Security: BugTraq, AI Hacks, And Being Dumb On Planes” →

Musing On AI From 1964

[Irving John Good] was at Trinity College, Oxford back in 1964. His paper, “Speculations Concerning the First Ultraintelligent Machine” could have been a topic for today, as we deal with machines that aren’t really ultraintelligent, but appear smart and think they are even smarter. He starts off with a bold thesis: “The survival of man depends on the early construction of an ultraintelligent machine.”

He also admits that we’ll need to understand more about the human brain and human thought to make a breakthrough. This is still true today. However, we still don’t fully understand how our brains work, but it seems unlikely that we are just super-large LLMs. Not that [Good] anticipated the modern chatbot. Perhaps his comments will apply more to a future AI software that actually thinks like a human, if there will ever be such a thing.

Then again, there are many parallels. One theme in the paper is that a smart machine will design a smarter machine. Unless, of course, it is afraid of being replaced. If a machine were actually sentient, what are the ethics of turning it off and tearing it apart?

Continue reading “Musing On AI From 1964” →

This Week In Security: Escaping Linux VMs, Vulnerable Solar, Confusing AI (Again), And Confusing NPM Malware

The Januscape vulnerability allows a user in a guest VM managed by the Linux Kernel Virtual Machine (KVM) to corrupt memory in the host system and break out of isolation.

KVM virtualization is used by major hosting platforms like Amazon AWS, Google GCP, Digital Ocean, and many more. All of the shared hosting platforms count on virtualization to isolate untrusted guest systems from the physical hardware and each other; being able to corrupt memory for all guests or break isolation presents a major threat.

The bug report says the error has been present for 16 years, which is nearly the entire lifetime of the KVM subsystem in Linux. Fixes are available in mainline, and major hosting providers who count on KVM are likely already updating.

Vulnerabilities In Balcony Solar

Micro solar, or “balcony solar”, installs have been gaining traction in Europe as a way to offset rising electrical costs by connecting solar and battery systems to a house or apartment power system.

Vulnerabilities have been found in the popular Hoymiles micro-inverter, which uses a proprietary RF radio protocol to manage the devices. Unfortunately, it looks like this protocol has no encryption or authentication beyond validating the serial number, and the serial number is also available over a wireless probe command.

Armed with a Nordic nRF radio researchers were able to discover nearby inverters in the wild and collect the serial numbers, though of course they stopped short of issuing commands to random users.

The wireless management control allows controlling the device power and output levels, as well as setting a lockout PIN, which the researchers suspect could be used to disable devices and lock the legitimate owners out completely.

There are an estimated 500,000 units in use, and currently the only known mitigation is to unplug the device entirely and disconnect the solar panels, though the team suggests that setting an anti-theft PIN may also help – or at least prevent an unknown PIN being set.

Be sure to check out the link for an in-depth analysis of the protocol and the surprising lack of protection.

Continue reading “This Week In Security: Escaping Linux VMs, Vulnerable Solar, Confusing AI (Again), And Confusing NPM Malware” →

Browser-Based Image Inpainting Runs Locally, If One Doesn’t Mind A Big Download

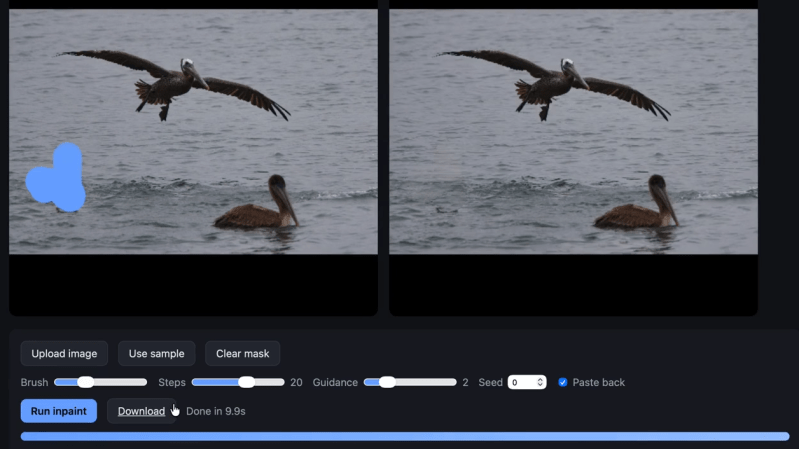
[Simon Willison] ported the Moebuis 0.2B image inpainting model to run locally in a web browser.  The web tool simply requires a user to provide an image, mark a section of it to be removed, and the model will do it’s best to patch up the missing area. The project was handled by Claude Code as an experiment in how things in the AI coding world have evolved, but more on that in a moment.

The existence of this tool shows that it’s possible for this kind of image editing to be done on the client side, running entirely locally with no reliance on remote services or server-side GPU resources. The online demo (GitHub repository here) is available if you want to try it out, but be warned it triggers a 1.27 gigabyte download of the required model on the first run.

What’s also interesting is [Simon]’s write-up, because he used the project as an opportunity to learn what has changed in the realm of AI coding agents. [Simon] is a software developer but in this project he didn’t personally write any of the code. One may think that means he didn’t learn anything other than how to use the tools, but that’s not quite true.

He learned it’s possible to convert a PyTorch-based model to ONXX, that the converted model can run in supported browsers using local WebGPU acceleration, and that the CacheStorage API will work on large files. Last but not least, he learned Claude Opus 4.8 is capable of handling such a project pretty much autonomously, and even created an informative document explaining the underlying architecture.

One may consider AI coding agents to be disasters waiting to happen, but it’s also true that the landscape is changing quickly, and write-ups like [Simon]’s give a helpful peek at those developments.