Hackaday Europe 2026: Space Oddities

If you’re in motorsport, or maritime, or mining fields, you can always call on a technician to come down and fix something when it’s broken. You can lay hands on the parts, reconfigure things, make repairs, and get something working again. In space, that’s seldom possible. If you’re lucky enough to have a manned mission, you might be able to make some running repairs; if you’re working with an unmanned robot, probe, or satellite, your options are altogether more limited. If you can’t find a fix, it’s game over—a particularly brutal result when huge budgets and years of work are on the line.

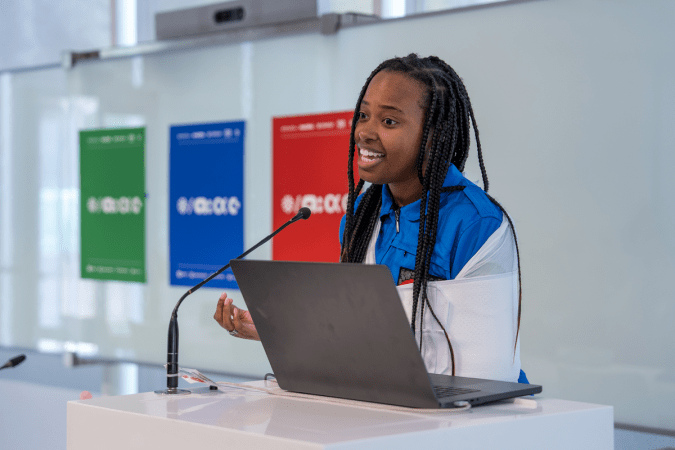
Janelle Wellons came down to Hackaday Europe to talk about space. More particularly, the engineering and debugging operations that keep all sorts of space programs alive. Her talk dives into some of the creative solutions engineers have had to come up with to save million-dollar missions from becoming unrecoverable boondoggles.

Continue reading “Hackaday Europe 2026: Space Oddities”

Rosy Retrocomputing

Most of us are guilty of romanticizing the past. Do you long to be the captain of a tall ship? Just as long as you don’t mind weevils in your food, vitamin deficiencies, and death from an infection when there were no antibiotics. Want to be a medieval knight? Even worse. But surely, retrocomputing is as fun as we remember, right? Turn your computer on, and it comes up with BASIC! Ready for you to write your own programs. None of this GUI foolishness. Of course, this is just another example of rosy retrospection.

Even if you like BASIC or a similar language today, things have changed. You have a nice text editor, a fast computer, debugging tools, along with things like named functions, no line numbers, and modern control structures. None of those things were very common in the 1980s. At least, not on a hobby-grade computer.

Why am I thinking about this? Well, the Hackaday Retrocomputing Challenge is on, and it occurred to me that I wanted to work with some young students in glorious MBASIC on a CP/M machine I built and modified from a Hackaday project. Perfect, right? Many of us started that way, so why shouldn’t they?

But it quickly got old. Even a simple program gets bogged down with GOTOs and GOSUBs to mysterious line numbers. It made me remember the time back in the early 1980s, or maybe even the late 1970s, that I wrote a BASIC preprocessor to scan BASIC with no line numbers and produce proper source, converting labels to line numbers in two passes.

Continue reading “Rosy Retrocomputing”

Hackaday Links Column Banner

Hackaday Links: September 13, 2026

We try to steer clear of politics and societal issues here at Hackaday, so a protest is not usually the sort of thing we’d cover. But we figure it’s safe enough to bend the rules a bit when the ones doing the protesting happen to be robots.

About 30 bots gathered — or at least were commanded to gather by the event organizers — in Warsaw to spur discussion about the impact AI and robots will have on the labor market. Beyond getting public and media attention, the demonstration was also designed to raise awareness of what modern humanoid robots can do. While we appreciate the idea of showing robots taking the “jobs” of the protesters, it does seem somewhat ironic that marching around and chanting for hours is exactly the sort of repetitive work that most people would be happy to see taken over by machines.

Although we hope these protests remain peaceful, there’s always a chance things can turn violent when tensions are high. Should things go south, take comfort in the knowledge that a company in Japan has introduced a robot ambulance service. It’s probably more accurate to compare it with roadside assistance, as the goal is to repair the robot on-site. That said, if the fault is more serious, they can bring the damaged bot back to HQ. Of course, the major difference between this program and a traditional ambulance service is that they’ll be able to bring along a spare robot that can take over the patient’s job while repairs are being made. Should anyone start doing that for humans, expect a few more protests.

Continue reading “Hackaday Links: September 13, 2026”

Hackaday Podcast Episode 386: Doomscroll Tamagotchis, Clavichords, And Vibrotrucks

In this specially-numbered podcast episode that lines up quite nicely with our Retrocomputing Challenge, Elliot Williams and Kristina Panos met over surprisingly low latency and loud beverages to bring you the best of the previous week’s hacks.

But first, the news. German company Isar Aerospace can now claim that they’ve launched the first spacecraft into orbit from Europe. Be sure to check out the in-link, where we reported on the building of the spaceport.

In Hackaday news, the aforementioned Retrocomputing Contest had 64 entries at last check, which is just perfect for Episode 386. Will yours be the 65th?

Supercon Ten tickets are selling out, and per Elliot, the talks have been chosen, pending approval by each submitter.  Keep an eye on the blog for the official announcement!

After reviewing the news, Elliot reached into the ol’ Mailbag and found two missives, including another from [Vik Olliver] regarding the printing of LEGO. The other is from [Mendel Munkis], who has been enjoying Wikipedia offline since 2018, thanks to a 32-bit ARM9 processor. Then, it was on to the hacks.

Check out the links below if you want to follow along, and as always, tell us what you think about this episode in the comments!

Download in lovely MP3.

Continue reading “Hackaday Podcast Episode 386: Doomscroll Tamagotchis, Clavichords, And Vibrotrucks”

This Week In Security: It’s Patch Tuesday Again, TVs Spying, Supply Chain Worms Return, Prolonged Hack Impacts, Stolen IDs

Several times this summer, Microsoft’s Patch Tuesday, the monthly roundup of major security patches for Microsoft products, has included record-breaking numbers of security fixes. The August 2026 patch set actually seemed to catch up. Was this a sign of the bug apocalypse lessening? Ha, nope!

Brian Krebs at Krebs On Security once again brings his excellent roundup of Patch Tuesday events, with this months patch set absolutely crushing previous numbers with nearly 1,000 security fixes.

Two of the fixes are for zero-day vulnerabilities under active exploitation in the wild, both allowing privilege escalation on Windows. Privilege escalation bugs turn general vulnerabilities in applications and games into full administrator access to gain persistence and deploy ransomware, and generally make any vulnerability significantly worse.

Krebs also calls out a CVSS 9.8 (so close to a perfect 10!) vulnerability that allows remote code execution in the Windows shell with no user interaction and no authentication, a remotely exploitable DNS bug present since Windows Server 2012 and Windows 10 which will likely see exploitation in the wild soon, and over a hundred other bugs are ranked “Critical”.

How the sheer volume of vulnerabilities in this patch will fit with recent Microsoft recommendations that companies should apply the patches immediately remains to be seen. (Likely: not very well, depending on what new behavior and issues the fixes cause!)

Is Your LG TV Spying on You?

Gamers Nexus continues their trend of high-quality investigation, and they have posted another tremendous multi-hour investigatory video. This time Gamers Nexus focuses on the ecosystem of LG televisions and monitors.

It shouldn’t likely surprise many here that “smart” devices are usually more to the benefit of advertisers than consumers. Similarly, it shouldn’t be a surprise that a “smart” device harvests user data to sell to advertises. What may be surprising is the degree to which LG devices appear to collect data, how much data is sent even when collection is turned off, and how overt executives at the company are, with multiple executives making statements in pitches to advertisers that LG “owns the glass”, “owns the living room”, and is designed to correlate devices, inhabitants of the environment, and viewing habits so that ads can be served to the TV and mobile devices in the same room simultaneously.

With tracking enabled, the smart TV captures telemetry of what applications are used, as well as continually capturing the video displayed and reporting fingerprints to LG servers and ad partners. The screen content is tracked not only for TV, but for the HDMI inputs, including if the TV is used as a PC monitor. If voice control is enabled, the TV also records audio and analyzes it. The TV also continually scans the local network and nearby Wi-Fi networks, reporting all the devices it finds on the local network, including host name, MAC address, and sometimes software running depending on the MDNS advertisements. Near-by Wi-Fi networks are sufficient for very precise geolocation, so LG effectively knows the location of every customer, as well.

Continue reading “This Week In Security: It’s Patch Tuesday Again, TVs Spying, Supply Chain Worms Return, Prolonged Hack Impacts, Stolen IDs”

Tech In Plain Sight: Meet The Robot That Does CPR

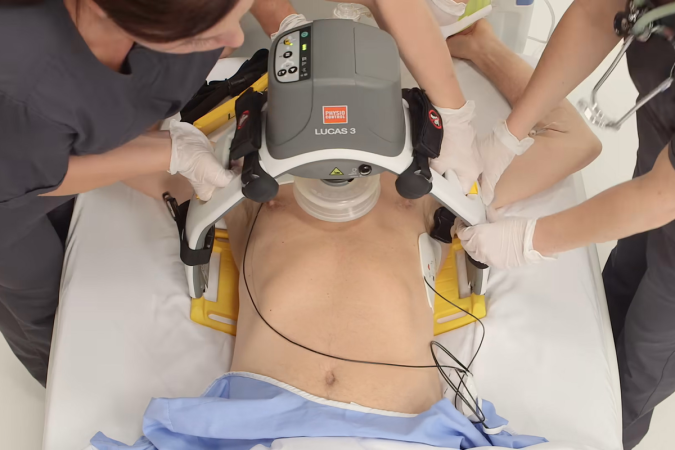
Usually in Tech In Plain Sight, we talk about technology you probably see every day, even if you don’t notice it. But we hope you don’t get to see one of the latest crop of medical robots, such as the LUCAS chest compression system. If you watch the popular TV series “The Pitt”, though, you may have caught a glimpse of one of these medical marvels. They aren’t fiction. They are very real devices.

Calling them robots might be stretching the definition a little. They don’t roam the halls looking for patients. But once attached to someone in cardiac arrest, they can take over one of the most important — and physically demanding — parts of CPR: chest compressions.

Keep The Blood Moving

When someone’s heart stops pumping blood, time is critical. CPR doesn’t normally restart the heart on its own. Instead, chest compressions produce enough blood flow to keep oxygen reaching the brain and heart while rescuers work on the underlying problem and, when appropriate, use a defibrillator.

Doing that well is harder than it looks on television. Current American Heart Association guidelines call for adult chest compressions 100 to 120 times per minute, at least 5 cm deep but generally no deeper than 6 cm, while allowing the chest to recoil fully between compressions. Interruptions should be kept to a minimum.

That’s hard physical work. In fact, studies show compression depth begins to fall after only about 90 to 120 seconds, which is one reason CPR teams normally swap compressors every two minutes. But a robot doesn’t get tired.

Continue reading “Tech In Plain Sight: Meet The Robot That Does CPR”