South Korea’s KSLV-2 Rocket Delivers Payloads To Orbit

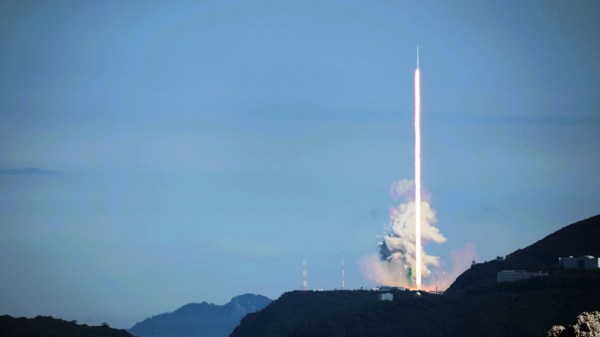
South Korea’s domestically developed KSLV-2 “Nuri” rocket successfully placed six payloads into low Earth orbit Tuesday, after lifting off from from Naro Space Center at 4 PM KST. This follows an earlier attempt in October which failed to reach orbit after the booster’s third stage engine shutdown prematurely. The flight followed an initial trajectory over the East China Sea, after which the upper stage steered out towards the Philippine Sea, finally placing the payload in the desired orbital inclination of 98 degrees. This less-than-ideal path wasted energy, but ensured that the first and second stages fell into the ocean and not onto people. Success was confirmed shortly after launch as the vehicle passed over South Korea’s King Sejong Station in Antarctica.

The payload on this test flight was primarily a mass simulator of 1.3 metric tons, but a small Performance Verification Satellite (PVSAT) was included, for a grand total of 1.5 metric tons. The PVSAT itself monitors vehicle performance, but also serves as a carrier for four CubeSats. These were developed by engineering teams at various local universities and will be deployed in the coming days.

If you’re inclined to track these, the launch has been given COSPAR ID 2022-065 and the first three objects (third stage, dummy mass, and PVSAT) have been assigned the NORAD catalog numbers 52894, 52895, and 52896. It’s too early to tell which is which at this point, but as more data about their respective orbits are collected, it should be possible to tell them apart. The next four catalog numbers, 52897 – 52900, have been reserved for the CubeSats once they are released.

With this launch, South Korea has become the 10th nation to put a payload into space using its own domestic technology, and the 7th to loft a payload of more than one ton to orbit — joining the ranks of the United States, Russia, Japan, China, France, and India.

Continue reading “South Korea’s KSLV-2 Rocket Delivers Payloads To Orbit”
Plastic CPUs Will Bend To Your Will

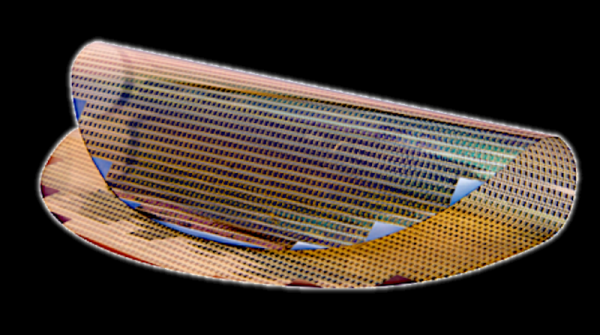
As microcontroller prices drop, they appear in more things. Today you will find microcontrollers in your car, your household appliances, and even kid’s toys. But you don’t see them often embedded in things that are either super cheap or have to flex, such as for example a bandage. Part of the reason is the cost of silicon chips and part of the reason is that silicon chips don’t appreciate bending. What if you could make CPUs for less than a penny out of flexible plastic? What applications would that open up? PragmatIC — a company working to make this possible — thinks it would open up a whole new world of smart items that would be unthinkable today. They worked with a team at the University of Illinois Urbana-Champaign to create prototype plastic CPUs with interesting results.

This is still the stuff of research and dreams, but a team of researchers did work to produce 4-bit and 8-bit processors using IGZO –indium gallium zinc oxide — semiconductor technology. This tech can be put on plastic and will work even if you bend it around a radius as small as a few millimeters.

Continue reading “Plastic CPUs Will Bend To Your Will”

Teensy Spectrum Analyzer Has 170 Channels

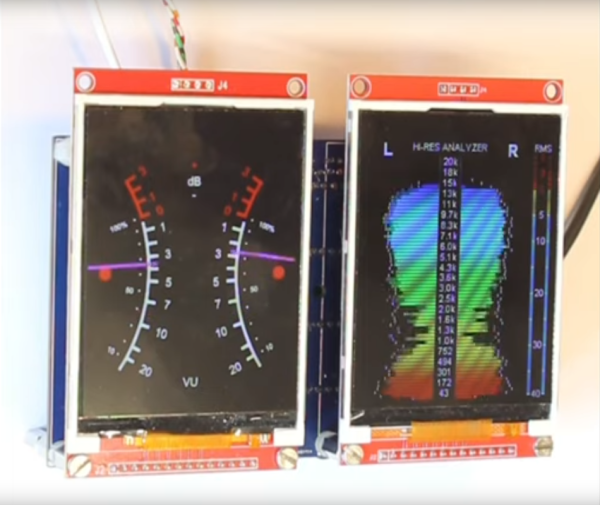
While high-fidelity audio has come a long way in the past several decades, a lot of modern stereo equipment is still missing out on some of the old analog meters that were common on amplifiers and receivers of the 60s through the 80s. Things like VU meters don’t tend to be common anymore, but it is possible to build them back in to your sound system with the help of some microcontrollers. [Mark] shows us exactly how to reclaim some of the old-school functionality with this twin audio visualizer display.

Not only does this build include two displays, but the microcontroller is keeping up with 170 channels in real-time in order to drive the display. What’s more impressive is that it’s being done all on a Teensy 4.1. To help manage all of the data and keep the speed as fast as possible it uses external RAM soldered to the board, and a second Teensy audio board is used to do the real time FFT analysis. Most of the channels are sent to the display hosting the spectrum analyzer but two are reserved for left and right stereo VU meters on the second display.

The project from [Mark] is originally based on this software from [DIYLAB] so everything is open-source. While it was originally built for a specific piece of hardware, [Mark] has it set up with a line in and line out plus a microphone input so it can be used for virtually any audio hardware now. For another take on the classic VU meter, take a look at this design based on an Arudino instead.

Continue reading “Teensy Spectrum Analyzer Has 170 Channels”

3D Printed Concrete Beam Improves Sustainability

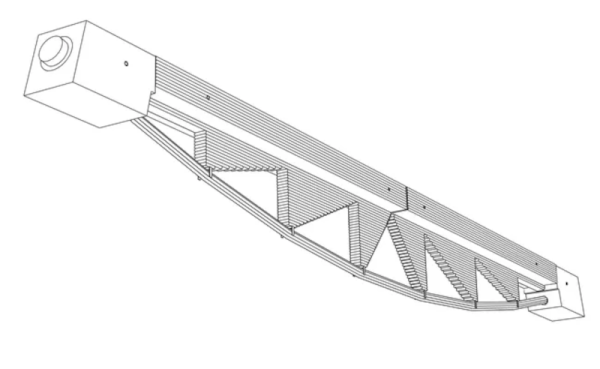
Many of the 3D printed houses and structures we’ve seen use concrete and are — frankly — a little underwhelming. Making big squares out of concrete isn’t that hard and while we are sure there is some benefit, it isn’t overwhelming. [Andy Coward] apparently felt the same way and set out to find ways that 3D printing could offer unique benefits in building structures. The result: a beam that would be difficult to create with conventional techniques but is easy to make with a printer. The advantage is that it uses 78% less concrete than a conventional beam with the same properties.

The key is that in a normal beam, not much of the concrete is bearing a significant load. It is simply there because you need some concrete on one side of the beam and then some more on the other side. In the center, surprisingly little of the concrete actually supports anything. The new beam takes advantage of this along with a steel reinforcement at a strategic point. Still, it uses 70% less steel than a typical reinforced beam.

Continue reading “3D Printed Concrete Beam Improves Sustainability”

Can A Drone Push A Bike?

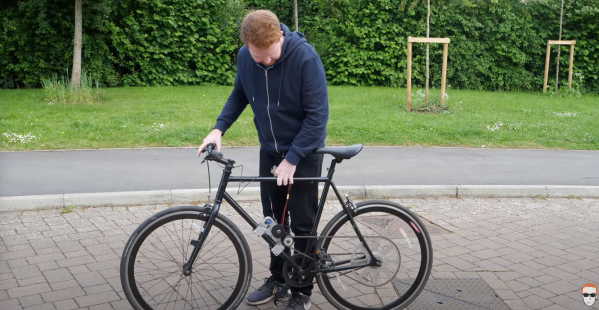
It sounds like a rhetorical question that a Midwestern engineer might ask, something on the order of ‘can you fix this bad PCB spin?’ [Tom Stanton] sets out to answer the title question and ends up building a working e-bike with a drone motor.

You might be thinking, a motor is a motor; what’s the big deal? But a drone motor and a regular e-bike motor are made for very different purposes. Drone motors spin at 30,000 RPM, and an e-bike hub motor typically does around 200-300 RPM while being much larger. Additionally, a drone motor goes in short spurts with a large fan blowing right on it, and an e-bike motor can run almost continuously.

The first step was to use gears and pulleys to reduce the RPM on the motor to provide more torque. A little bit of CAD and 3D printing later, [Tom] had a setup ready to try. However, the motor quickly burned out. With a slightly bigger motor and more gear reduction, version 2 performed remarkably well. After the race between a proper e-bike and the drone bike, the coils were almost melted.

If you’re thinking about making your bike electric, we have some advice. We’ll throw in a second piece of advice for free: use a larger motor than the drone motor, even though it technically works. Video after the break.

Continue reading “Can A Drone Push A Bike?”

Screenshot of the Insteon's new blog post, showing the Insteon logo in the header, the "A New Day for Insteon!" title, and some of the intro paragraph of the blog post

Insteon Gets Another Chance

It would appear that, sometimes, miracles happen. A few days ago, an update graced the website of Insteon, a company whose abrupt shuttering we covered in detail two months ago. An entity described as “small group of passionate Insteon users” has bought what was left of the company, and is working on getting the infrastructure back up. Previously, there was no sign of life from the company’s APIs. Now, Insteon hubs are coming back to life — or perhaps, they’re Inste-online again.

We’ve explained that revival of these devices without acquiring the company IP would’ve been tricky because of stuff like certificate pinning, and of course, a pile of proprietary code. Buying a company that’s undergoing a liquidation is not exactly end-user-friendly, but it would seem that someone sufficiently business-savvy got it done. The new CEO, as reported by [CNX Software], is a member of an investment committee — it’s fair to assert that this would help. A more sustainable funding source rather than ‘sell hardware and then somehow provide indefinite services’ is promised; they are moving to a subscription model, but only for Insteon Hub users. Recurring payments don’t sound as bad when it comes to paying developers and covering operational costs, and we hope that this revival succeeds.

Nothing is mentioned about moving towards openness in software and hardware — something that protects users from such failures in the first place. The new company is ultimately vulnerable to the same failure mode, and may leave the users in the dark just as abruptly as a result. However, we have our fingers crossed that the updated business model holds, purely for users’ sake. At least, unlike with the Wink hub, Insteon’s transition to a subscription model is better than the Inste-off alternative.

We thank [Itay] for sharing this with us! Via [CNX Software].

This Week In Security: Pacman, Hertzbleed, And The Death Of Internet Explorer

There’s not one, but two side-channel attacks to talk about this week. Up first is Pacman, a bypass for ARM’s Pointer Authentication Code. PAC is a protection built into certain ARM Processors, where a cryptographic hash value must be set correctly when pointers are updated. If the hash is not set correctly, the program simply crashes. The idea is that most exploits use pointer manipulation to achieve code execution, and correctly setting the PAC requires an explicit instruction call. The PAC is actually indicated in the unused bits of the pointer itself. The AArch64 architecture uses 64-bit values for addressing, but the address space is much less than 64-bit, usually 53 bits or less. This leaves 11 bits for the PAC value. Keep in mind that the application doesn’t hold the keys and doesn’t calculate this value. 11 bits may not seem like enough to make this secure, but keep in mind that every failed attempt crashes the program, and every application restart regenerate the keys.

What Pacman introduces is an oracle, which is a method to gain insight on data the attacker shouldn’t be able to see. In this case, the oracle works via speculation attacks, very similar to Meltdown and Spectre. The key is to attempt a protected pointer dereference speculatively, and to then observe the change in system state as a result. What you may notice is that this requires an attack to already be running code on the target system, in order to run the PAC oracle technique. Pacman is not a Remote Code Execution flaw, nor is it useful in gaining RCE.

One more important note is that an application has to have PAC support compiled in, in order to benefit from this protection. The platform that has made wide use of PAC is MacOS, as it’s a feature baked in to their M1 processor. The attack chain would likely start with a remote execution bug in an application missing PAC support. Once a foothold is established in uprivileged userspace, Pacman would be used as part of an exploit against the kernel. See the PDF paper for all the details.

Continue reading “This Week In Security: Pacman, Hertzbleed, And The Death Of Internet Explorer”