Discovering SDRs Everywhere

To quote commenter [douyarou], “It’s like our little version of a Precambrian explosion”. A bunch of hackers have discovered, independently and building on each other’s work, software-defined radio (SDR) capabilities in more places than you can shake a stick at.

It all started with [Espargos] and [h0m3us3r] apparently independently discovering that the ESP32 family of chips had a “secret” debug mode that allowed direct access to the radio that’s normally used for WiFi. While the 2.4 GHz radio signal is almost always immediately converted into data by the MAC hardware, here they found a way to listen in upstream, to the raw IQ data.

Seeing this, folks were immediately inspired to find out if they could transmit as well. [marble] not only got transmit functionality working, but integrated the part in with the standard osmosdr data flow, which meant that a whole bunch of existing tools were ready to go. We didn’t know about it at the time, but apparently [jochenhammes] and [z1000biker] concurrently had their TX-capable hacks up and running: here and here.

At this point, folks have already started to use the capabilities for broadcasting digital TV signals, voice signals, FM Hell, and other hijinks. This reminds us of the early days of the RTL-SDR project, when a competent, if receive-only, SDR functionality was found in a bunch of USB TV-tuner dongles. Once the hardware capabilities were sussed out, people started writing all sorts of useful software, and it gave rise to all manner of radio projects, from simply poking at domestic wireless devices to tracking all the airplanes in the world as they fly by.

[Tom] and I were discussing this on the podcast, and he remarked that of course there are SDRs hidden everywhere there is a radio unit these days, and the question is just whether or not we could hack them into usability. And before the podcast was even finally edited, [Samson1te] told us about his find in the LR2021 LoRa chip. This is a radio that’s designed to be a radio, with 16-bit resolution, and covering lower frequencies from 150 MHz to 960 MHz.

Compared to the RTL-SDR revolution, this is all happening at incredible speed. Each of these hacks will enable us to use different slices of radio spectrum with different degrees of ease, but it’s clear that the cost of entry into playing around with digital radio has just dropped precipitously. We will see hundreds of new signals hacks in the next few months – the floodgates have been opened.
Three-Axis Camera Slider From 3D Printer Parts

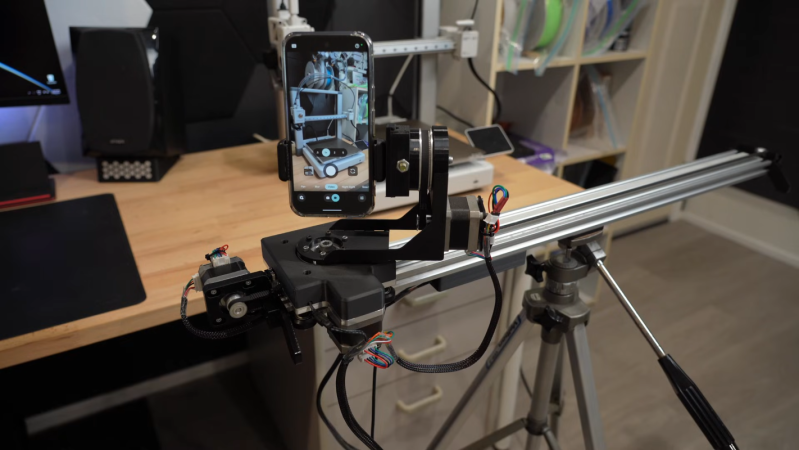
There’s a great reason 3D printers are made with things like extruded aluminum rails and other commodity, off-the-shelf parts. These things are designed not only for ease of construction and prototyping, but they’re also fairly strong especially given how modular they are. And they are excellent platforms for other projects as well. [CNCDan] has been using plenty of on-hand 3D printer parts to build a three-axis camera slider to film parts of his other projects, and this video documents his build and the latest upgrades to this platform.

After sorting out some issues with underpowered motors by improving their gear ratios, he found that many of the sizes and clearances on the existing platform changed enough that he needed to redo other parts of the carrier, including the mounting plate. He cut a new plate from steel and pressed bearings in, and then started putting together the other axes including a quick release mechanism for his camera. With a camera that weighs about 1.4 kg, getting the motors to move the camera smoothly was its own challenge. He re-worked all of his driver code over the course of a few weeks and eventually got his new system working much better than the original version.

With everything said and done, the camera slider can be controlled wirelessly with a GUI on another computer. Everything runs on an ESP32, and the slider can support other cameras besides his heavier one, including smartphones. He notes that this wasn’t the easiest way to build a project like this, but worked for him eventually because he had the parts and tools on hand to make it work. He’s also put the project files up on a GitHub page for anyone interested. Camera sliders like these have some niche uses as well; take a look at this high-speed camera slider for some examples.

Continue reading “Three-Axis Camera Slider From 3D Printer Parts” →

DIY Smart Button Gets Surprisingly Complicated

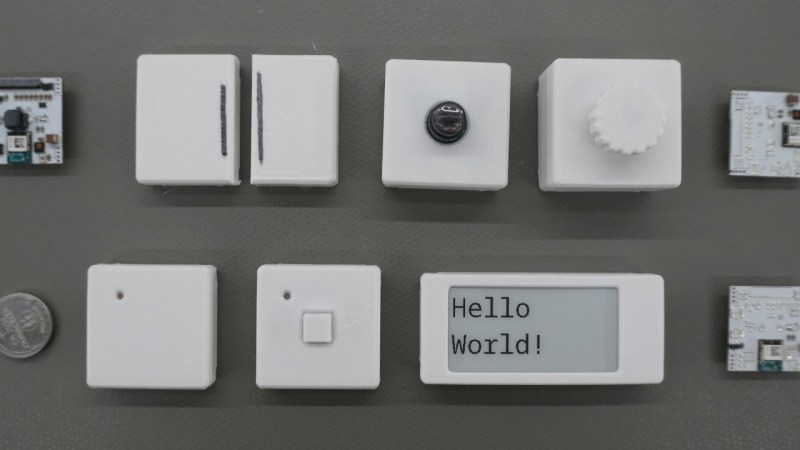
There’s a reason that the standards specifications for various wireless communications protocols are extremely long and detailed. [Made by Dennis] found this out first hand when he decided to build a wireless button from scratch.

The major issues with wireless devices is one of power consumption. If reliable power is available from a wall plug or solar panel, this isn’t as serious of a concern. But [Dennis] is using batteries for his buttons, so minimizing power consumption is a priority. He’s going with the nRF52, a microcontroller designed for low power and which has a built in wireless radio, and configuring it in a way that uses the least amount of energy possible.

From there, [Dennis] turns to the wireless communication. He goes into detail about how the microcontroller is woken up, how it sends its data packets to another wireless-enabled microcontroller, and how they handle handshakes and acknowledgements of data. For something as simple as a button press, it gets quickly more complicated especially when adding some basic encryption and security to the communications protocol.

With all the design decisions out of the way, the system can be built. [Dennis] has created custom PCBs for his devices, and also included some expansion I/O for other sensors and peripherals beyond just a pushbutton. All of the schematics and code are available on the project’s GitHub page and the STL files can be found at Printables.

For those new to offline home automation or who are turning away from cloud-based services lately, there are some easy entry points that don’t require much extra hardware or expenditure.

Continue reading “DIY Smart Button Gets Surprisingly Complicated” →

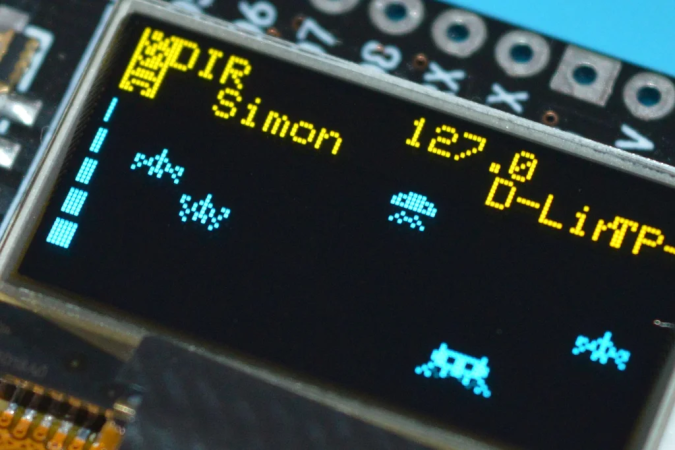
Legally Distinct Space Invaders Display WiFi Info

In the early 00s there was a tiny moment before the widespread adoption of mobile broadband, after the adoption of home WiFi, and yet before the widespread use of encryption. For this brief time a unique practice arose called wardriving — where people would drive around, document, and use these open wireless networks.

Although the pursuit has diminished with the rise of mobile broadband and WPA encryption, there are still a few use cases for the types of hardware a wardriver would have used. [arduinocelentano] recently built a Wi-Fi strength monitor in this style but with a unique theme.

Continue reading “Legally Distinct Space Invaders Display WiFi Info” →

Overengineered Freezer Monitor Fills Market Void

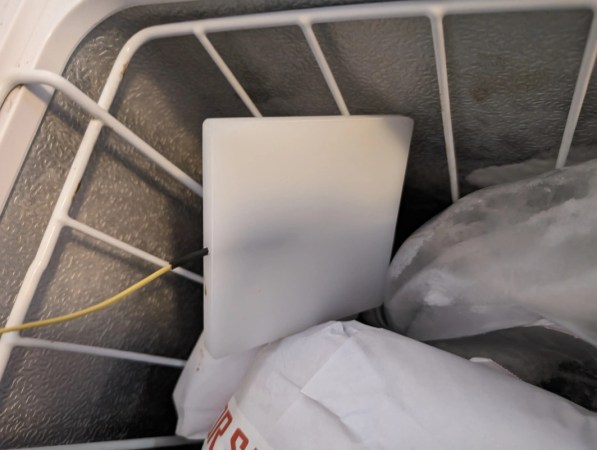
A lot of projects we see around here are built not just because they can be built, but because there’s no other option available. Necessity is the mother of invention, as they say. And for [Jeff] who has many thousands of dollars of food stowed in a chest freezer, his need for something to keep track of his freezer’s status was greater than any commercial offering available. Not only are freezers hard on batteries, they’re hard on WiFi signals as well, so [Jeff] built his own temperature monitor to solve both of these issues.

The obvious solution here is to have a temperature probe that can be fished through the freezer in some way, allowing the microcontroller, battery, and wireless module to operate outside of the harsh environment. [Jeff] is using K-type thermocouples here, wired through the back of the freezer. This one also is built into a block of material which allows him to get more diffuse temperature readings than a standard probe would provide. He’s also solving some other problems with commercially available probes here as well, as many of them require an Internet connection or store data in a cloud. To make sure everything stays local, he’s tying this in to a Home Assistant setup which also allows him to easily make temperature calibrations as well as notify him if anything happens to the freezer.

Although the build is very robust (or, as [Jeff] himself argues, overengineered) he does note that since he built it there have been some additional products offered for sale that fit this niche application. But even so, we always appreciate the customized DIY solution that avoids things like proprietary software, subscriptions, or cloud services. We also appreciate freezers themselves; one of our favorites was this restoration of a freezer with a $700,000 price tag.

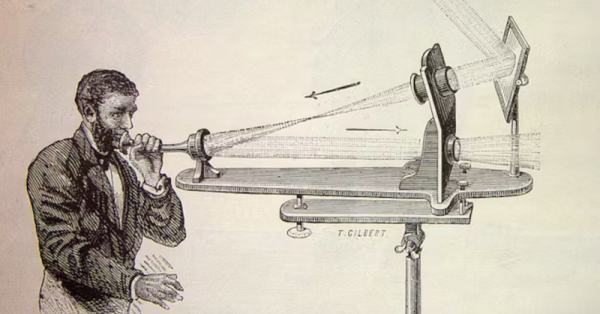
Engraving of Alexander Graham Bell's photophone, showing the receiver and its optics

Replica Of 1880 Wireless Telephone Is All Mirrors, No Smoke

If we asked you to name Alexander Graham Bell’s greatest invention, you would doubtless say “the telephone”; it’s probably the only one of his many, many inventions most people could bring to mind. If you asked Bell himself, though, he would tell you his greatest invention was the photophone, and if the prolific [Nick Bild] doesn’t agree he’s at least intrigued enough to produce a replica of this 1880-vintage wireless telephone. Yes, 1880. As in, only four years after the telephone was patented.

It obviously did not catch on, and is not the sort of thing that comes to mind when we think “wireless telephone”. In contrast to the RF of the 20th century version, as you might guess from the name the photophone used light– sunlight, to be specific. In the original design, the transmitter was totally passive– a tube with a mirror on one end, mounted to vibrate when someone spoke into the open end of the tube. That was it, aside from the necessary optics to focus sunlight onto said mirror. [Nick Bild] skips this and uses a laser as a handily coherent light source, which was obviously not an option in 1880. As [Nick] points out, if it was, Bell certainly would have made use of it.

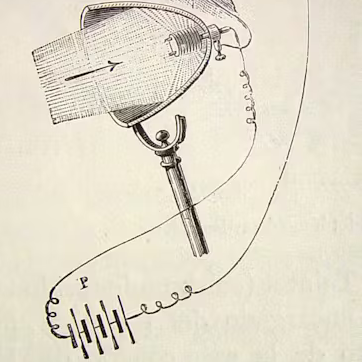
Bell's selenium-based photophone receiver.
The photophone receiver, 1880 edition. Speaker not pictured.

The receiver is only slightly more complex, in that it does have electronic components– a selenium cell in the original, and in [Nick’s] case a modern photoresistor in series with a 10,000 ohm resistor. There’s also an optical difference, with [Nick] opting for a lens to focus the laser light on his photoresistor instead of the parabolic mirror of the original. In both cases vibration of the mirror at the transmitter disrupts line-of-sight with the receiver, creating an AM signal that is easily converted back into sound with an electromagnetic speaker.

The photophone never caught on, for obvious reasons — traditional copper-wire telephones worked beyond line of sight and on cloudy days–but we’re greatful to [Nick] for dredging up the history and for letting us know about it via the tip line. See his video about this project below.

The name [Nick Bild] might look familiar to regular readers. We’ve highlighted a few of his projects on Hackaday before.

Continue reading “Replica Of 1880 Wireless Telephone Is All Mirrors, No Smoke” →

38C3: Towards An Open WiFi MAC Stack On ESP32

At the 38th Chaos Communications Congress, [Frostie314159] and [Jasper Devreker] gave us a nice update on their project to write an open-source WiFi stack for the ESP32. If you’re interested in the ESP32 or WiFi in general, they’ve also got a nice deep dive into how that all works.

On the ESP32, there’s a radio, demodulator, and a media access controller (MAC) that takes care of the lowest-level, timing-critical bits of the WiFi protocol. The firmware that drives the MAC hardware is a licensed blob, and while the API or this blob is well documented — that’s how we all write software that uses WiFi after all — it’s limited in what it lets us do. If the MAC driver firmware were more flexible, we could do a lot more with the WiFi, from AirDrop clones to custom mesh modes.

The talk starts with [Jasper] detailing how he reverse engineered a lot of Espressif’s MAC firmware. It involved Ghidra, a Faraday cage, and a lucky find of the function names in the blob. [Frostie] then got to work writing the MAC driver that he calls Ferris-on-Air. Right now, it’s limited to normal old station mode, but it’s definite proof that this line of work can bear fruit.

This is clearly work in progress — they’ve only been at this for about a year now — but we’ll be keeping our eyes on it. The promise of the ESP32, and its related family of chips, being useful as a more general purpose WiFi hacking tool is huge.