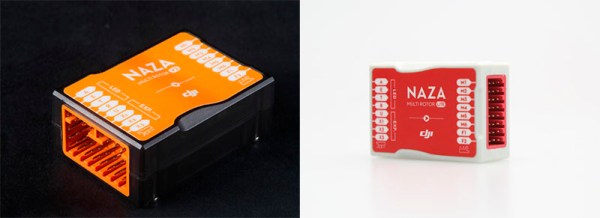
Upgrading DJI Flight Controllers

DJI, the company that gave us the far too popular Phantom line of quadcopters, doesn’t just make the most popular line of FPV quads. Their top of the line flight controller, The Naza V2, is very good, able to connect to flight planning software that will set waypoints, talk to peripherals over a CAN bus, and has improved flight algorithms. On the other hand, their ‘reduced price’ model, the Naza Light, can’t connect to these nifty CAN bus peripherals and has a bit of a problem with drifting the quad from one side or another.

The Naza V2 sells for around $300, and the Naza Light sells for about $170, both with a GPS module. The hardware inside the V2 and Light is exactly the same. We all know how this is going to go down, right?

[udnham] over on the RC Groups forum figured out a way to load the more capable Naza V2 firmware on the Naza Light, giving the cheaper flight controller features that were, until now, only found in the more expensive V2 hardware. The upgrades include better algorithms for GPS position and altitude hold, the ability to connect to DJI peripherals including the Bluetooth module, the iOSD, and camera gimbals, Octocopter support, the DJI datalink modem, and a bunch of other features.

Even though DJI is using the same hardware in the $170 Naza Light and the $300 Naza V2, upgrading the firmware requires an Internet connection to the DJI servers. [udnham] wrote a utility that modifies the /etc/hosts file on your computer, runs a service, and allows you to upgrade your firmware on the Naza Light. It’s basically a $130 firmware upgrade for a DJI flight controller that’s a single download away.

[udnham] set up a site where you can download the firmware flashing tool with a few videos showing the upgrade process and the improvement over the stock firmware. You can check those out below.
Continue reading “Upgrading DJI Flight Controllers” →

Reverse-Engineering A Superior Chinese Product

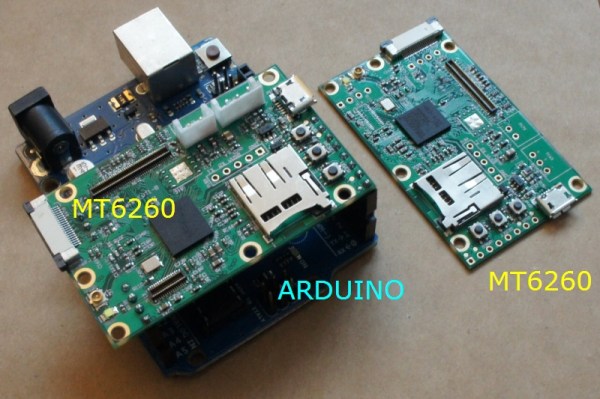
It makes an Arduino look like a 555.  A 364 Mhz, 32 bit processor. 8 MB RAM. GSM. Bluetooth. LCD controller. PWM. USB and dozens more. Smaller than a Zippo and thinner than corrugated cardboard. And here is the kicker: $3. So why isn’t everyone using it? They can’t.

Adoption would mandate tier after tier of hacks just to figure out what exact hardware is there. Try to buy one and find that suppliers close their doors to foreigners. Try to use one, and only hints of incomplete documentation will be found. Is the problem patents? No, not really.

[Bunnie] has dubbed the phenomenon “Gongkai”, a type of institutionalized, collaborative, infringementesque knowledge-exchange that occupies an IP equivalent of bartering. Not quite open source, not quite proprietary. Legally, this sharing is only grey-market on paper, but widespread and quasi-accepted in practice – even among the rights holders. [Bunnie] figures it is just the way business is done in the East and it is a way that is encouraging innovation by knocking down barriers to entry. Chinese startups can churn out gimmicky trash almost on whim, using hardware most of us could only dream about for a serious project.

Continue reading “Reverse-Engineering A Superior Chinese Product” →

Hacking Education; Project-Based Learning Trumps The Ivory Tower

Project-based learning, hackathons, and final projects for college courses are fulfilling a demand for hands-on technical learning that had previously fallen by the wayside during the internet/multi-media computer euphoria of the late 90’s. By getting back to building actual hardware yourself, Hackers are influencing the direction of education. In this post we will review some of this progress and seek your input for where we go next.

Continue reading “Hacking Education; Project-Based Learning Trumps The Ivory Tower” →

Towards The Perfect Coin Flip: The NIST Randomness Beacon

Since early evening on September 5th, 2013 the US National Institute of Standards and Technology (NIST) has been publishing a 512-bit, full-entropy random number every minute of every day. What’s more, each number is cryptographically signed so that you can easily verify that it was generated by the NIST. A date stamp is included in the process, so that you can tell when the random values were created. And finally, all of the values are linked to the previous value in a chain so that you can detect if any of the past numbers in the series have been altered after the next number is published. This is quite an extensive list of features for a list of random values, and we’ll get into the rationale, methods, and uses behind this scheme in the next section, so stick around.

Continue reading “Towards The Perfect Coin Flip: The NIST Randomness Beacon” →

Home Computers Behind The Iron Curtain

I was born in 1973 in Czechoslovakia. It was a small country in the middle of Europe, unfortunately on the dark side of the Iron Curtain. We had never been a part of Soviet Union (as many think), but we were so-called “Soviet Satellite”, side by side with Poland, Hungary, and East Germany.

My hobbies were electronics and – in the middle of 80s – computers. The history of computers behind the Iron Curtain is very interesting, with a lot of unusual moments. For example – communists at first called cybernetics as “bourgeois’ pseudoscience” (as well as sociology or semiotics), “used to enslave a mankind by machines”. But later on they understood the importance of computers, primarily for science and army. So in 50s the Eastern Bloc started to build its own computers, separately and “in its own way.”

The biggest problem was a lack of modern technologies. There were a lot of skilled and clever people in eastern countries, but they had a lot of problems with the elementary technical things. Manufacturing of electronics parts was divided into diverse countries of Comecon – The Council for Mutual Economic Assistance. In reality, it led to an absurd situation: You could buy the eastern copy of Z80 (made in Eastern Germany as U880D), but you couldn’t buy 74LS00 at the same time. Yes, a lot of manufacturers made it, but “it is out of stock now; try to ask next year”. So “make a computer” meant 50 percent of electronics skills and 50 percent of unofficial social network and knowledge like “I know a guy who knows a guy and his neighbor works in a factory, where they maybe have a material for PCBs” at those times.

Continue reading “Home Computers Behind The Iron Curtain” →

Downloading Data Through The Display

HIPAA – the US standard for electronic health care documentation – spends a lot of verbiage and bureaucratese on the security of electronic records, making a clear distinction between the use of records by health care worker and the disclosure of records by health care workers. Likewise, the Federal Information Security Management Act of 2002 makes the same distinction; records that should never be disclosed or transmitted should be used on systems that are disconnected from networks.

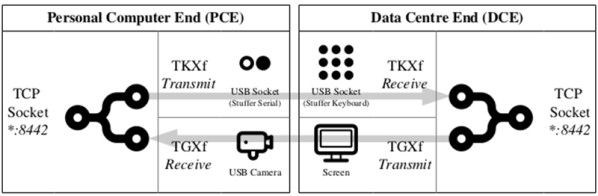
This distinction between use and disclosure or transmission is of course a farce; if you can display something on a screen, it can be transmitted. [Ian Latter] just gave a talk at Kiwicon that provides the tools to do just that. He calls it ThruGlassXfer (TGXf), and it does exactly what it says on the tin: anything that can be displayed on a screen can be transmitted. All you need are the right tools.

Continue reading “Downloading Data Through The Display” →

Reverse Engineering Capcom’s Crypto CPU

There are a few old Capcom arcade titles – Pang, Cadillacs and Dinosaurs, and Block Block – that are unlike anything else ever seen in the world of coin-ops. They’re old, yes, but what makes these titles exceptional is the CPU they run on. The brains in the hardware of these games is a Kabuki, a Z80 CPU that had a few extra security features. why would Capcom produce such a thing? To combat bootleggers that would copy and reproduce arcade games without royalties going to the original publisher. It’s an interesting part of arcade history, but also a problem for curators: this security has killed a number of arcade machines, leading [Eduardo] to reverse engineering and document the Kabuki in full detail.

While the normal Z80 CPU had a pin specifically dedicated to refreshing DRAM, the Kabuki repurposed this pin for the security functions on the chip. With this pin low, the Kabuki was a standard Z80. When the pin was pulled high, it served as a power supply input for the security features. The security – just a few bits saved in memory – was battery backed, and once this battery was disconnected, the chip would fail, killing the game.

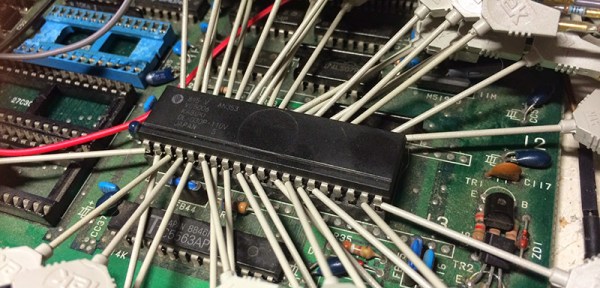
Plugging Kabuki into an old Amstrad CPC 6128 without the security pin pulled high allowed [Eduardo] to test all the Z80 instructions, and with that no surprises were found; the Kabuki is fully compatible with every other Z80 on the planet. Determining how Kabuki works with that special security pin pulled high is a more difficult task, but the Mame team has it nailed down.

The security system inside Kabuki works through a series of bitswaps, circular shifts, XORs, each translation different if the byte is an opcode or data. The process of encoding and decoding the security in Kabuki is well understood, but [Eduardo] had a few unanswered questions. What happens after Kabuki lost power and the memory contents – especially the bitswap, address, and XOR keys – vanished? How was the Kabuki programmed in the factory? Is it possible to reprogram these security keys, allowing one Kabuki to play games it wasn’t manufactured for?

[Eduardo] figured being able to encrypt new, valid code was the first step to running code encrypted with different keys. To test this theory, he wrote a simple ‘Hello World’ for the Capcom hardware that worked perfectly under Mame. While the demo worked perfectly under Mame, it didn’t work when burned onto a EPROM and put into real Capcom hardware.

That’s where this story ends, at least for the time being. The new, encrypted code is valid, Mame runs the encrypted code, but until [Eduardo] or someone else can figure out any additional configuration settings inside the Kabuki, this project is dead in the track. [Eduardo] will be back some time next week tearing the Kabuki apart again, trying to unravel the mysteries of what makes this processor work.