This Week In Security: What’s In A Name, The AI Bugpocalypse Hits Everyone, OpenWRT Flaws, And Duress Passwords

The great thing about standards is there’s so many to pick from, right?. (Insert obligatory XKCD #927 here.) Several companies have developed naming schemes to refer to groups of attacks, and now Google has too.

Sometimes, malware, ransomware, or exploit groups name themselves: “Shinyhunters”, “LapSus$”, “Cl0p”, “Lockbit”, and so on. For the groups that don’t advertise their presence, identification and naming can be more difficult. Mostly state-run affairs that didn’t want to draw attention to themselves, these Advanced Persistent Threats (APT) groups were originally simply given numbers. APT28 refers to the Russian GRU Intelligence Directorate suspected of hacking the Democratic Party email servers, APT38 is a North Korean governmental agency involved in financial and crypto currency theft.

Multiple companies and agencies have developed naming schemes to make referring to threat groups easier, typically including a regional identifier as well. CrowdStrike naming uses name groups like “Bear” group for suspected Russian actors, “Panda” for China, “Spider” for unattributed crime groups, while Microsoft uses “Blizzard”, “Typhoon”, and “Tempest”.

Google, deciding there weren’t enough classifications already, now introduces “RELIC”, “CASTLE”, and “COMET”. Of course, each naming organization has dozens of other classification groups as well, but now the next time you hear about an attack being attributed to “Scattered Spider” you know it’s the CrowdStrike name for a crime group.

Critical OpenWRT DHCP Flaw Fixed

The Hacker News reports on a major release of OpenWRT which includes fixes to the odhcpd server, the embedded DHCPv4 and DHCPv6 server written by OpenWRT.

The bug is a straight-forward stack style attack where a buffer is allocated, but not length-checked against the data required to reply to a malformed request. OpenWRT runs on a wide range of devices, but one of the most popular legacy platforms still in use, the MIPS processor architecture, lacks most modern security protections against stack-based attacks, making this attack sting more than it might on other architectures.

The latest OpenWRT releases also fix issues in the uhttpd embedded web server, multiple issues in the LUCI web configuration interface that allowed attackers to inject cross-site scripting content and Linux kernel security fixes. If you run a direct OpenWRT build on your equipment, update! These bugs will have an extremely long tail however, with tens of thousands, or likely more, OpenWRT-based devices that will never see updates.

The company behind several of the findings, Hacker House, say they used multiple AI tools and both open and frontier models to discover the bugs, then manual review and testing to confirm before reporting.

Cisco to Stop Assigning (some) CVEs

Cisco has announced it is moving to a twice-monthly patch cycle. Additionally, Cisco will no longer assign CVEs to each bug in the release.

Cisco says this is in reaction to the rapid increase in bugs found by AI tools, and that “Assessing security risk CVE-by-CVE and applying point mitigations is no longer fit for purpose.” Cisco will still assign a CVE to a bug that “requires compensating controls” or is known to be exploited.

It seems like it will be business as usual for the most severe bugs, but it will be interesting to see what happens when exploits are found for bugs which did not get a CVE in a prior release.

Microsoft Suggests Three-Day Patch Race

Microsoft is now recommending a 3 day patch window for new patches. This is, to say the least, an “aggressive” schedule for applying new patches, given the recent track record of issues introduced by patches.

A update that crashes is inconvenient on a home computer — even more so if it’s your parent’s computer — but could be catastrophic when it brings down an entire corporate fleet. Most large organizations have their own internal patch schedules and internal testing requirements before patches are deployed, delaying the patch process further.

Systems like the CISA KEV database, a list of vulnerabilities known to be actively exploited, are in place to help identify the most important issues. With repeated record-breaking numbers of vulnerabilities pushed in Patch Tuesday and the decreasing support of the KEV and related vulnerability indexing systems, the load on IT departments and administrators is becoming impossible.

The AI “bugpocalypse” is finding record numbers of vulnerabilities, while also closing the timeline between bug to exploit to hours in some cases. The time between bug and exploit then drives the patch cycle, which means less testing. With less testing, the patches are less stable, leading to less trust in rapidly installing them.

Oracle Patches Almost 1500 CVEs

Moving directly from the impacts of the flood of Microsoft security issues, the July 2026 patch set from Oracle included fixes for 1499 security issues and 1434 CVEs over 334 Oracle products.

Oracle is also pressuring administrators to move to a monthly patch cycle, but acknowledges “transitioning to a monthly security patching cadence may require updates to existing operational processes”. Not to worry – there is a Oracle consulting service you can hire to help you patch your Oracle problems.

Linux Patches 323 CVEs in Two Days

After announcing over 400 CVEs in the Linux kernel last week, Linux mainters have announced an additional 323 in the last three days alone. The vulnerabilities cover Bluetooth, Ethernet, USB gadget mode, WiFi drivers, virtualization systems, SMB file sharing, and of course more.

One benefit to the architecture of the Linux kernel is that typically all the fixes will arrive in a single kernel update, but when almost every week brings critical updates and a new kernel, patch fatigue is a real thing. Either users stop applying every update, or the uptime and testing requirements of a company prohibits constantly updating and changing servers.

Duress Passwords Aren’t Necessarily a Good Thing

The security-hardened Android variant Graphene, is in the news this week for the use of duress passwords.

A duress password is a mechanism where a second PIN or password can be used to initiate a device wipe. The hope is that in a situation where you are compelled to unlock a device, providing a password which then wipes the device is a preferable option.

The legality of a duress password depends on the environment it is used in. The United States Customs and Border Patrol claims that by wiping a device during an inspection at the US border, Samuel Tunick destroyed evidence and property in violation of federal laws. The issue is compounded because the stop happened at a border, where many US laws against search, seizure, and the availability of a lawyer are suspended, even for US citizens.

The inclusion of duress passwords, and their cousin hidden encrypted volumes, can sound like a good idea, but can place users in serious danger when in situations with less strict rules of law. Having the ability to wipe data sounds great in isolation, but protestors, human rights workers, and other targeted groups have faced direct and physical threats under some regimes. Facing retaliation for wiping a device, or facing physical violence before providing an unlock code out of fear that it might wipe a device, can be a real risk for some.

FreeBSD Fixes a WireGuard Bug

FreeBSD has issued a security update pertaining to the WireGuard VPN implementation.

WireGuard is a modern VPN with excellent performance even on low-end systems, and which has implementations on basically every platform. The FreeBSD implementation, however, didn’t fully validate VPN packets, accepting packets without checking one of the cryptographic validation measures.

Attackers are able to inject data to a FreeBSD WireGuard implementation if they are able to guess some attributes of the connection, and able to fully modify the data in the VPN if they are able to intercept the packets.

The bug impacts any FreeBSD user of WireGuard. FreeBSD has released updated kernels.
Keyboard Lights As An Airgap Attack Vector

What do you do when you need to get data into an airgapped machine? Well, you might find yourself limited to basic input devices to interact with the computer in question. As [Nikolay Valentinovich Repnitskiy] demonstrates, though, you can do some fun stuff amidst such limitations.

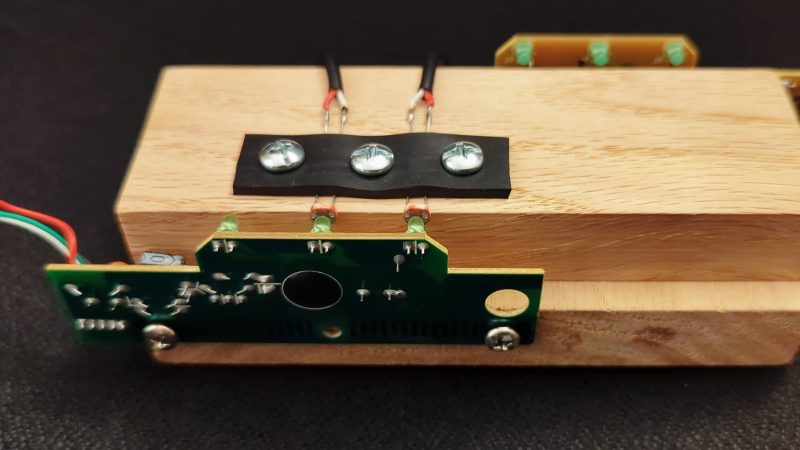
[Nikolay] created what he calls a “unidirectional network” connection via a keyboard. Specifically, he took two Dell SK-8115 keyboards, and stripped them down to their controller PCBs. On one, he soldered photoresistors to a couple of the keyboard matrix pins, such that they’d fire a keypress when lit up. He then placed the other keyboard PCB such that the Num Lock and Caps Lock LEDs are lined up with the photoresistors. This made it possible to have one PC flash the keyboard LEDs in order to “type” on the other machine. This can be used to move data on to it, such as a little program which [Nikolay] prepared which can be made executable and used to further break into the machine and make it easier to pull data across more efficiently in future.

We looked at an earlier version of this hack some time ago. If you’ve been imagining creative ways to talk to airgapped computers, be sure to let us know on the tipsline!

Regain Some Trust In Unknown USB Drives

For how useful USB thumb drives are for quickly toting around and copying files from one computer to another, they can be a bit of a security headache. Programs can be loaded on them with all kinds of malware; they can be obscured in some ways that are difficult to detect, and they can be set up to execute certain programs when they’re plugged in. The general wisdom is to simply avoid untrusted USB devices completely, but that sort of abstinence-only policy rarely works in the real world. If, for some reason, an untrusted USB device absolutely needs to be used, many of these security issues can be mitigated with this tool.

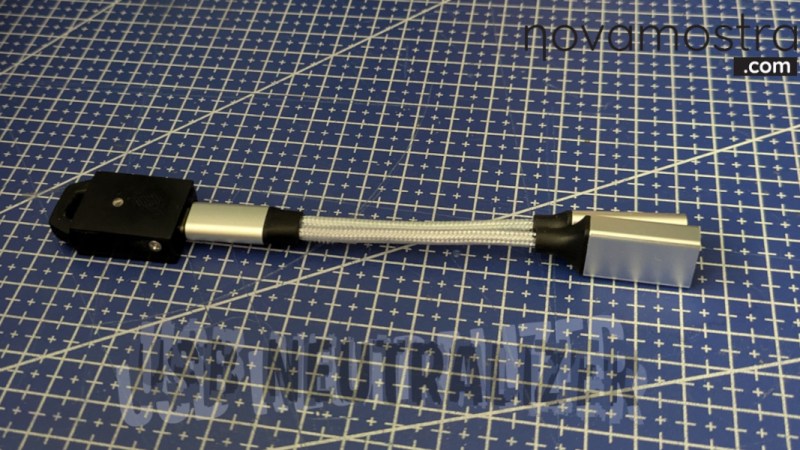
Built by [Novamostra], the device is simple on the surface: it’s a Raspberry Pi Pico mated to a 2-in-1 USB splitter cable. But with the USB Neutralizer software they have written loaded onto the Pico, it automatically destroys the ability of any connected USB thumb drive to load files. The program works by deleting the first and last 34 Logical Block Addressing (LBA) sectors on the drive immediately when it’s plugged in, without doing anything else. This effectively corrupts the drive bad enough to prevent malicious software in the partitions from doing anything, allowing the user to (relatively) safely put the USB drive into their computer and format it for re-use. The code for this tool is also open-source and reviewable on the project’s GitHub page.

Of course, this isn’t a perfect security solution for all USB attacks. It doesn’t erase or replace the firmware on the drive itself, and although firmware-level attacks are rare they’re not out of the question for all users, all the time. It also won’t prevent a malicious physical attack like this high-voltage one, and it may also not stop hidden or obscured partitions or devices programmed for storage and some other nefarious purpose simultaneously, like a USB HID. But still, this solves a great many of the problems associated with getting new drives from semi-untrustworthy sources, like retailers or friends whose computer skills we don’t fully trust.

This Week In Security: AI Is A Mess, Hacking Car Chargers, An OpenSSL DoS, And Factories Under Attack

[Ayush Paul] posts about extracting data from Claude agents while it accesses web data to fulfill user requests.

But it wasn’t that easy. [Ayush] discovered that Anthropic anticipated many of the attacks, and set up guardrails in an attempt to keep the agent from accessing arbitrary web sites. For Claude to access a website, the user has to specify it, it must be the results of a web search, or it must be referenced by a website previously specified by the user or returned in a search.

To convince the Claude agent to navigate a malicious site designed to extract data, Ayush formed a false warning that Cloudflare was blocking the agent for authentication purposes, and asked it to spell out the name of the agents owner by clicking a list of alphabetical links. Of course Claude trusts Cloudflare and wants to be helpful, so it cheerfully completed the task.

Once the agent is trapped in the false authentication loop, it can be interrogated for all sorts of information it knows about the owner: Ayush was able to convince it to disclose employer, and even data about the user that could be linked to security questions, like their home town.

Since Claude can be detected by the user agent (the field attached to web requests that tells the web server what sort of browser is requesting the page) custom information can be fed to the bot while users see a normal website; clicking a link looks completely normal, but asking an agent to summarize the site triggers fooling the bot into spilling the beans.

After reporting the issue, Ayush was told that Anthropic had already identified the issue internally, and eventually prevented the attack for now by preventing the agent from following links on external pages.

Grok sends entire codebases

Cereblab discovered that the Grok coding agent uploaded the entire content of the codebase it’s working with – and all Git history – to xAI servers, almost immediately. Even when told to never upload a file, the agent would reply “OK”, and then begin uploading the code bundle anyway.

If uploading your code to a remote server isn’t bad enough, and this could be extremely bad in some situations involving sensitive company code, including the entire Git history means that previously deleted files, like accidentally committed secrets or authentication credentials and tokens, were also leaked. Attempting to opt out by disabling options to improve the model by uploading code had no effect.

After gaining attention, Grok has added a privacy option to opt out of data retention. xAI has committed to deleting the retained uploaded code, but it is unclear if users will be told when their data has been removed. To actually prevent the agent from uploading local files to the xAI servers, even temporarily, a global flag “disable_codebase_upload” is required. Watch out, the privacy retention flags are only per-session!

Continue reading “This Week In Security: AI Is A Mess, Hacking Car Chargers, An OpenSSL DoS, And Factories Under Attack” →

This Week In Security: Another Record Patch Tuesday, LAME Is More Secure, Secure Boot Is Less Secure, And Milk Malware

Following the reports last week using the Windows Global Device ID (GDID) in tracking a malware operators behavior, here is a comprehensive write-up about what goes into the GDID and how it is used. It’s worth noting that the GDID itself was not used to catch the malware operator, however once a suspect was identified, the GDID was used to correlate behavior across various Microsoft products on the Internet.

The GDID is generated and assigned during a Windows install, but a re-install of Windows will generate a new GDID. Developer [SmtimesIWndr] tracks the generation and tracking of the GDID through the various Windows libraries and services, identifying where it appears to be created and how it is passed to other services like Azure.

Worth noting is your GDID is a unique, personally identifiable piece of information; if you go exploring and extract it from your Windows install, be sure to keep it private!

LAME mp3 updates

Those of us who were around for the dawn of MP3 files may remember the LAME encoder and library. After almost 10 years, there is a new LAME release.

Notably, this includes two security fixes, one for a stack buffer overflow based on malicious input to the Blade encoder, and an integer underflow in the AIFF header parser. Both of the fixed bugs feel very old-school, which seems appropriate given the age of the library and most of the related code.

Buffer overflows impacting the stack are some of the simplest and most direct forms of vulnerabilities, where it is possible to write past the end of a buffer and control how the function returns and instead execute arbitrary code. Integer under-flows, similarly, impact memory management; usually caused by allowing a variable that stores the size of a buffer to go negative. Since sizes are typically unsigned positive numbers, a negative is interpreted as an enormous positive number, writing past the proper buffer length.

Despite the new findings, the LAME codebase has been extremely resilient over the years, and considering the number of programs that likely still use LAME under the covers to process audio, seeing the project wake up with security fixes is great news.

Recovering Passwords from BIOS

Researchers have found a vulnerability in Dell BIOS code that allows extraction of the administrator password from the BIOS flash chips, either with physical access via a flash programmer, or via administrator or root level access to the operating system and reading the contents of the flash chip.

Dell used a 20 byte key to encrypt a 32 byte password field: for any admin password of 12 characters or fewer, the password is stored in completely plaintext. For longer passwords, characters beyond the first 12 are encrypted – but the random bytes are computed from the first character of the password mixed with fixed device data, yielding only 256 possible encryption seeds for the remaining bytes.

Using the BIOS admin password for evil requires local access, so the attack surface is small, however as the researchers note it controls the boot order and may allow an attacker with physical access to then boot an unsigned OS or bypass full-disk encryption, so it’s serious.

Continue reading “This Week In Security: Another Record Patch Tuesday, LAME Is More Secure, Secure Boot Is Less Secure, And Milk Malware” →

This Week In Security: Escaping Linux VMs, Vulnerable Solar, Confusing AI (Again), And Confusing NPM Malware

The Januscape vulnerability allows a user in a guest VM managed by the Linux Kernel Virtual Machine (KVM) to corrupt memory in the host system and break out of isolation.

KVM virtualization is used by major hosting platforms like Amazon AWS, Google GCP, Digital Ocean, and many more. All of the shared hosting platforms count on virtualization to isolate untrusted guest systems from the physical hardware and each other; being able to corrupt memory for all guests or break isolation presents a major threat.

The bug report says the error has been present for 16 years, which is nearly the entire lifetime of the KVM subsystem in Linux. Fixes are available in mainline, and major hosting providers who count on KVM are likely already updating.

Vulnerabilities In Balcony Solar

Micro solar, or “balcony solar”, installs have been gaining traction in Europe as a way to offset rising electrical costs by connecting solar and battery systems to a house or apartment power system.

Vulnerabilities have been found in the popular Hoymiles micro-inverter, which uses a proprietary RF radio protocol to manage the devices. Unfortunately, it looks like this protocol has no encryption or authentication beyond validating the serial number, and the serial number is also available over a wireless probe command.

Armed with a Nordic nRF radio researchers were able to discover nearby inverters in the wild and collect the serial numbers, though of course they stopped short of issuing commands to random users.

The wireless management control allows controlling the device power and output levels, as well as setting a lockout PIN, which the researchers suspect could be used to disable devices and lock the legitimate owners out completely.

There are an estimated 500,000 units in use, and currently the only known mitigation is to unplug the device entirely and disconnect the solar panels, though the team suggests that setting an anti-theft PIN may also help – or at least prevent an unknown PIN being set.

Be sure to check out the link for an in-depth analysis of the protocol and the surprising lack of protection.

Continue reading “This Week In Security: Escaping Linux VMs, Vulnerable Solar, Confusing AI (Again), And Confusing NPM Malware” →

This Week In Security: Windows 10 Gets Another Year, SmartTV Botnets, Hiding Payloads, And LastPass Customer Leak

Unsurprisingly to many of us, app stores for smart televisions are also trash. Perhaps even more full of trash than other app stores due to the smaller ecosystem and fewer reviewers.

Spur analyzed the LG smart TV app store, and found that almost half of the apps available contain proxy software, turning your TV into a node in their proxy network. Are these apps malware? Many of the analyzed apps provided a thin veneer of user consent: they offer you the tradeoff of seeing an ad every 15 seconds, or allowing their “occasional web indexing” to run permanently in the background. Watch the fishtank app for five minutes, join their proxy network for life.

Spur notes that the proxy SDK in use appears to block connections to private network ranges (internal IP ranges like 192.168.x.x and 10.x.x.x), but that the SDK restricting access to those ranges is the only protection against accessing whatever network the TV is connected to.

Amazon and Roku ban proxy apps on their devices. Samsung and LG do not.

Win 10 Security Updates Extended

Microsoft has added another year of security updates to Windows 10. Despite trying to kill the platform, so many users remain on Windows 10 that Microsoft likely has no choice.

The extended support program was previously due to end in October 2026 but has now been pushed to October 2027. The security updates will be available for free in the UI, but users in other regions must activate OneDrive and sync system settings, or pay 1000 Microsoft credits (about $30).

The death of Windows 10 is near, but for those unwilling or unable to let go, it shuffles along.

Signal Phishing Attempts

Bleeping Computer has an article about increased phishing attempts from hacker groups in Russia targeting Signal users.

The phishing messages target politicians, government officials, military, and other high-profile intelligence targets, and claim that Signal is introducing mandatory two-factor authentication, before prompting the target to enable remote Signal backups. A second follow-up phishing attempt then prompts the user to copy the backup authentication tokens from Signal and provide them to the attacker.

Signal remote backups are a relatively recent addition to the messenger, making a backup on the Signal servers of a users messages and images, encrypted with a key known only to the user. While convenient, and likely fundamentally secure given the track record of the Signal team, this phishing campaign highlights a major weakness: once private content is accessible somewhere else, an attacker simply needs to obtain the keys to access it, which is significantly simpler than obtaining the message content directly from the victims phone.

Continue reading “This Week In Security: Windows 10 Gets Another Year, SmartTV Botnets, Hiding Payloads, And LastPass Customer Leak” →