A Portable Serial Terminal That Should Be From The 1970s

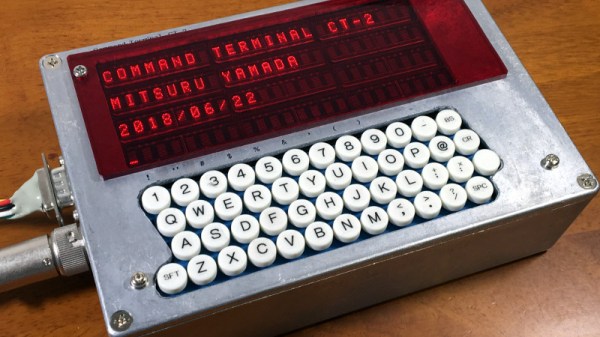
The humble standalone serial terminal might be long gone from the collective computing experience, but in the ghostly form of a software virtual terminal and a serial converter it remains the most basic fall-back and essential tool of the computer hardware hacker. [Mitsuru Yamada] has created the product that should have been made in the serial terminal’s heyday, a standalone handheld terminal using a 6809 microprocessor and vintage HP dot matrix LEDs. In a die-cast box with full push-button keyboard it’s entirely ready to roll up to a DB-25 wall socket and log into the PDP/11 in the basement.

Using today’s parts we might achieve the same feat with a single-chip microcontroller and a small LCD or OLED panel, but with an older microcomputer there is more system-building required. The 6809 is a wise choice from the 1970s arsenal because it has some on-board RAM, thus there’s no need for a RAM chip. Thus the whole thing is achieved with only a 2716 EPROM for the software, a 6850 UART with MAX232 driverĀ  for the serial port, and a few 74 chips for glue logic, chip selects, and I/O ports to handle keyboard and display. There’s no battery in the case, but no doubt that could be easily accommodated. Also there’s not much information on the keyboard itself, but in the video below we catch a glimpse of its wiring as the box is opened.

The value in a terminal using vintage parts lies not only in because you can, but also in something that can’t easily be had with a modern microcontroller. These parts come from a time when a computer system had to be assembled as a series of peripherals round the microprocessor because it had few onboard, leading to a far more in-depth understanding of a computer system. It’s not that a 6809 is a sensible choice in 2020, more that it’s an interesting one.

By comparison, here’s a terminal using technology from today.

Continue reading “A Portable Serial Terminal That Should Be From The 1970s” →
The Gatwick Drone: Finally Someone Who Isn’t Us Asks Whether It Ever Really Existed

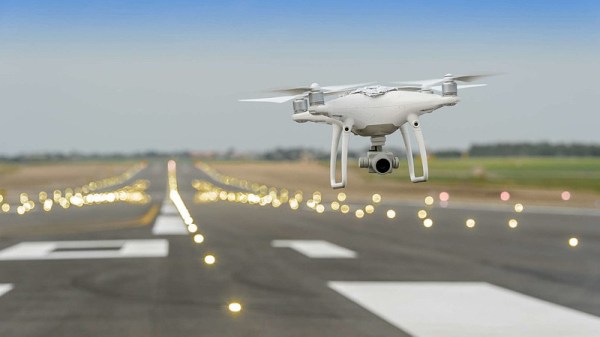
It’s taken two years, but finally it’s happened. Finally a respected national mass-media outlet has asked the question Hackaday were posing shortly after the event: what evidence was there that a drone was actually present in restricted airspace?

The Guardian newspaper in the UK is the outlet looking into the mystery of the Gatwick drone. It was the worldwide story of the moment around this time back in 2018 when the London airport closed down for several days in response to a series of drone reports. The assumption being put forward was that bad actors in the drone community were to blame, but there was significant disquiet in those ranks as the police and media story simply lacked credibility to anyone with knowledge of drones. At no point could they point to evidence that held water, the couple they arrested turned out to be innocent, and eventually a police officer admitted that there might not have been a drone after all. The damage had by then been done, as Received Opinion had it that irresponsible drone enthusiasts had put lives in danger and caused huge economic damage by closing an airport for several days.

The Guardian piece paints a fascinating and detailed picture of the events surrounding the investigation, by bringing the investigative journalism resources of a national newspaper into tracing and interviewing people involved from all sides. They talk to former Gatwick employees, off-the-record police officers with knowledge of the case, a drone specialist journalist, and the drone community including some of its members with significant professional experience in the world of aviation. It talks about the slow drip-feed of freedom of information requests revealing the machinations behind the scenes and furthermore the continuing lack of tangible proof of a drone. It’s very much worth a read, and we hope it will prompt further investigation of the events without the focus being on a non-existent drone.

We’d like to invite you to read Hackaday’s coverage from a few days after the event, and for an overview of the subject including the later Heathrow event, watch the CCCamp talk I presented on the topic in 2019. Then as now, our wish is for competent police investigations, responsible media reporting of drone stories, and credible official investigations of air proximity reports surrounding drones.

Header: Lucy Ingham, CC BY-SA 4.0.

A Brain Transplant For An Uncommon Smart Bulb

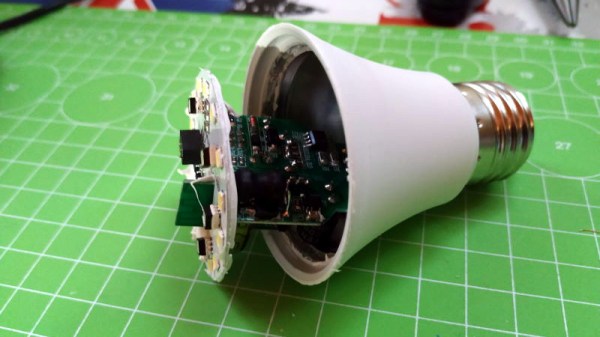
By now it’s a hardware hack that’s become common enough to be unremarkable, taking a smart light bulb or other mains switchable appliance and replacing its firmware with an open-source equivalent such as Tasmota. But what can be done when a new device is found to have a microcontroller unsupported by any open-source equivalents? If you are [Luca Dentella], you don’t throw in the towel and buy another one with a known processor, instead you reverse engineer it enough to give it a brain transplant of an ESP8266 module.

The Fcmila branded smart bulb in question was found to have a relatively unknown Chinese SoC, the Opulinks OPL1000. Since this couldn’t even raise a serial port it was more trouble than it was worth to write software for it, so instead he spent a while reverse engineering its schematic and electrical protocols, before grafting in a Wemos D1 ESP8266 board. He’s made a video about the project which you can see below the break.

Thankfully the majority of smart bulbs on the market seem to use more familiar hardware that can be flashed with relative ease.

Continue reading “A Brain Transplant For An Uncommon Smart Bulb” →

Ground Off Part Number Leads To Chip Detective Work

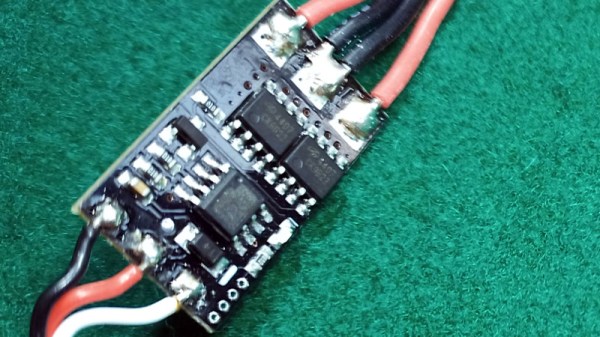
Sometimes when a piece of electronics lands on the bench, you find that its chips have their markings sanded off. The manufacturer is trying to make the task of the reverse engineer less easy, thus protecting their market. [Maurizio Butti] found an unexpected one in an electronic switch designed for remote control systems, it had the simple job of listening to the PWM signal from a receiver in a model aircraft or similar and opening or closing a FET.

From previous experience he suspected it might be a microcontroller from STC based on the location of power, ground, Rx, and Tx pins. This 8051-compatible device could be readily reprogrammed, so he has able to create his own firmware for it. He’s published the code and it’s pretty simple, as it simply replicates the original. He acknowledges that this might seem odd, but makes the point that it is left open for future upgrades such as for example repeatedly cycling the output as in a flashing light.

We don’t see so much of the STC chips here aside from one of their earlier offerings, but the 8051 core features here more regularly as it’s found in Nordic’s NRF24 series of wireless-capable chips.

A Retro Camcorder Upgraded As A Raspberry Pi HQ Camera

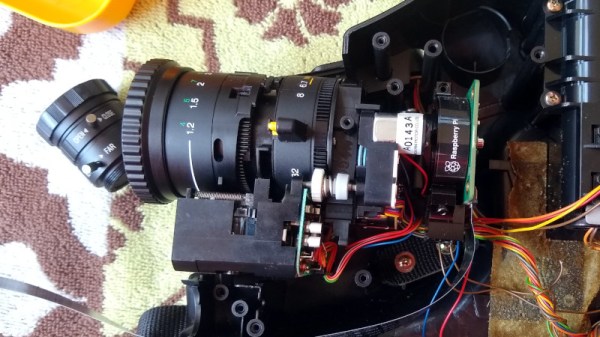
In 2020 when we carry an all-purpose computer and data terminal able to store our every thought and deed on a global computer network, it’s easy to forget that once upon a time we were excited by the simpler things. Take the camcorder for example, back in the 1990s the idea of a complete video recording solution that captured moving images on tape cartridges and fit in the palm of your hand was a very big deal indeed, and camcorders as we called them in those innocent times were a prized posession. Now they’re a $0.50 find a Goodwill, which is how [Dustin] picked up the RCA camcoder he’s converting into something altogether more modern. He’s gutted it and upgraded it by removing the analogue innards and retaining only the case and lens assembly to put around a Raspberry Pi and associated HQ camera module.

Opening the camcorder up reveals a ton of miniaturised analogue circuitry, but once the original assemblies are removed it’s relatively straightforward to put the Pi camera on the rear of the lens unit. There’s plenty of space for the Pi in the box, and he’s putting a touchscreen on the outside.

Sadly the camcorder’s original tiny CRT is no longer working, else that would have been the ultimate retro viewfinder. Still we hope to see some tinkering on that part of the project since those little CRTS make for delightful hacks. The project is very much a work in progress, but should serve that these once ubiquitous devices are now in the realm of the throwaway.

This isn’t the first such conversion we’ve seen with a Raspberry Pi, the original camera module is a handy fit to an 8mm movie camera.

European Right To Repair: Poor Repairability Shamed With Rating System

Happily the right to repair movement is slowly gaining ground, and recently they’ve scored a major success in the European Parliament that includes a requirement that products be labelled with expected lifetime and repairability information, long-term availability of parts, and numerous measures aimed at preventing waste.

… including by requiring improved product information through mandatory labelling on the durability and reparability of a product (expected lifetime, availability of spare parts, etc.), defining durability and reparability as the main characteristics of a product…

Even the UK, whose path is diverging from the EU due to Brexit, appears to have a moment of harmony on this front. This builds upon existing rights to repair in that devices sold in Europe will eventually have to carry a clearly visible repair score to communicate the ease of repairability and supply of spare parts, making a clear incentive for manufacturers to strive for the highest score possible.

We live in an age in which our machines, appliances, and devices are becoming ever more complex, while at the same time ever more difficult to repair. Our community are the masters of fixing things, but even we are becoming increasingly stumped in the face of the latest flashy kitchen appliance or iDevice. The right to repair movement, and this measure in particular, seeks to improve the ability of all consumers, not just us hackers, to makebuying decisions for better products and lower environmental impact.

With a population of around 450 million people spread across 27 member countries, the EU represents a colossal market that no manufacturer can afford to ignore. Therefore while plenty of other regions of the planet have no such legislation this move will have a knock-on effect across the whole planet. Since the same products are routinely sold worldwide it is to be expected that an improvement in repairability for European markets will propagate also to the rest of the world. So when your next phone has a replaceable battery and easier spares availability, thank the EU-based right to repair campaigners and some European lawmakers for that convenience.

European Parliament from EU, CC BY 2.0.

A Straightforward Guide To Unlocking The Nintendo Game And Watch

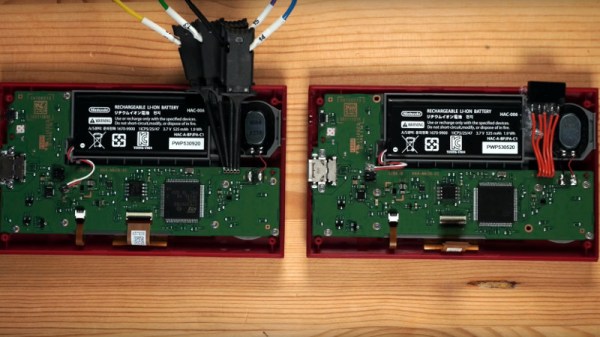
Nintendo’s reborn tiny handheld game has certainly attracted the attention of hardware hackers, and we’ve been treated to a succession of exploits as its secrets have been one by one unlocked. With relatively straightforward hardware it conceals potential far beyond a simple Mario game or two, and it’s now at the stage of having a path to dumping both its SPI Flash and internal Flash, unlocking its processor, and running arbitrary code. The process of unlocking it is now atraightforward enough to warrant a HOWTO video, to which [stacksmashing] has treated us. It’s early days and this is still touted as for developers rather than gamers, but it serves to show where work on this console is going.

The console’s STM32 architecture means that programming hardware is straightforward enough to find, though we’re cautioned against using the cheap AliExpress type we might use with a Blue Pill or similar. Instead the snap-off programmer that comes with an STM Nucleo board is a safer choice that many people are likely to have already.

The relative simplicity of the process as seen in the video below must conceal an immense amount of work from multiple people. It’s a succession of scripts to sequentially unlock and back up the various firmwares with STM payloads for each step. Finally the STM32 itself is unlocked, and the backed-up Nintendo firmware can be returned to the device or instead a custom firmware can be created. Aside from the DOOM we’ve already seen there are work-in-progress NES and Game Boy emulators, and fascinatingly also work on bare-metal games.

Given the lack of custom chips in this console it is easily possible that its hardware could be directly cloned and that Nintendo might have unintentionally created a new general purpose hacker’s handheld gaming platform. There are a few hardware works-in-progress such as increasing the SPI Flash size and finding the unconnected USB pins, so we look forward to more exciting news from this quarter.

Continue reading “A Straightforward Guide To Unlocking The Nintendo Game And Watch” →