Hyperspectral Imaging – Seeing The Unseeable

They say that a picture is worth a thousand words. But what is a picture exactly? One definition would be a perfect reflection of what we see, like one taken with a basic camera. Our view of the natural world is constrained to a bandwidth of 400 to 700 nanometers within the electromagnetic spectrum, so our cameras produce images within this same bandwidth.
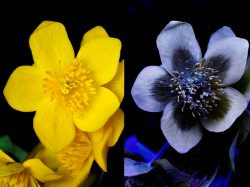
Image via Cosmos Magazine.

For example, if I take a picture of a yellow flower with my phone, the image will look just about how I saw it with my own eyes. But what if we could see the flower from a different part of the electromagnetic spectrum? What if we could see less than 400 nm or greater than 700 nm? A bee, like many other insects, can see in the ultraviolet part of the spectrum which occupies the area below 400 nm. This “yellow” flower looks drastically different to us versus a bee.

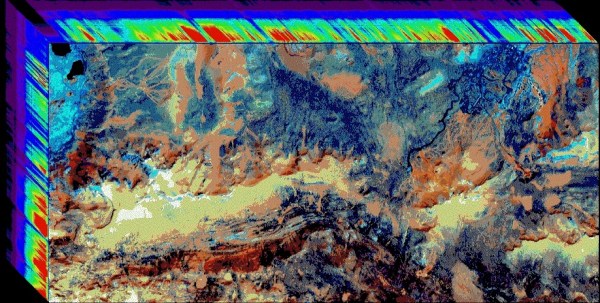
In this article, we’re going to explore how images can be produced to show spectral information outside of our limited visual capacity, and take a look at the multi-spectral cameras used to make them.  We’ll find that while it may be true that an image is worth a thousand words, it is also true that an image taken with a hyperspectral camera can be worth hundreds of thousands, if not millions, of useful data points. Continue reading “Hyperspectral Imaging – Seeing The Unseeable” →
What Makes A Hacker

I think I can sum up the difference between those of us who regularly visit Hackaday and the world of non-hackers. As a case study, here is a story about how necessity is the mother of invention and the people who invent.

Hackaday has overlap with sites like Pinterest and Instructables but there is one vital difference, we choose to create something new and beautiful with the materials at hand. Often these tools and techniques are very simple. We look to make things elegant by reducing the unnecessary clutter, not adding glitter. If something could be built with a 555 timer we will let you know. If there is a better choice for a processor, we will tell you.

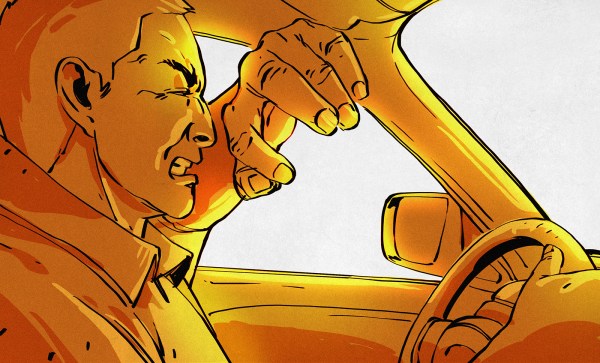
My first real work commute was a forty-minute eastward drive every morning and a forty-minute westward drive every evening. This route pointed my car directly into the sun twice a day. Staring into a miasma of incandescent plasma for an hour and a half a day isn’t fun, and probably isn’t safe, but we can fix that.

Continue reading “What Makes A Hacker” →

Artificial Intelligence At The Top Of A Professional Sport

The lights dim and the music swells as an elite competitor in a silk robe passes through a cheering crowd to take the ring. It’s a blueprint familiar to boxing, only this pugilist won’t be throwing punches.

OpenAI created an AI bot that has beaten the best players in the world at this year’s International championship. The International is an esports competition held annually for Dota 2, one of the most competitive multiplayer online battle arena (MOBA) games.

Each match of the International consists of two 5-player teams competing against each other for 35-45 minutes. In layman’s terms, it is an online version of capture the flag. While the premise may sound simple, it is actually one of the most complicated and detailed competitive games out there. The top teams are required to practice together daily, but this level of play is nothing new to them. To reach a professional level, individual players would practice obscenely late, go to sleep, and then repeat the process. For years. So how long did the AI bot have to prepare for this competition compared to these seasoned pros? A couple of months.

Continue reading “Artificial Intelligence At The Top Of A Professional Sport” →

Spy Tech: Stealing A Moon Probe

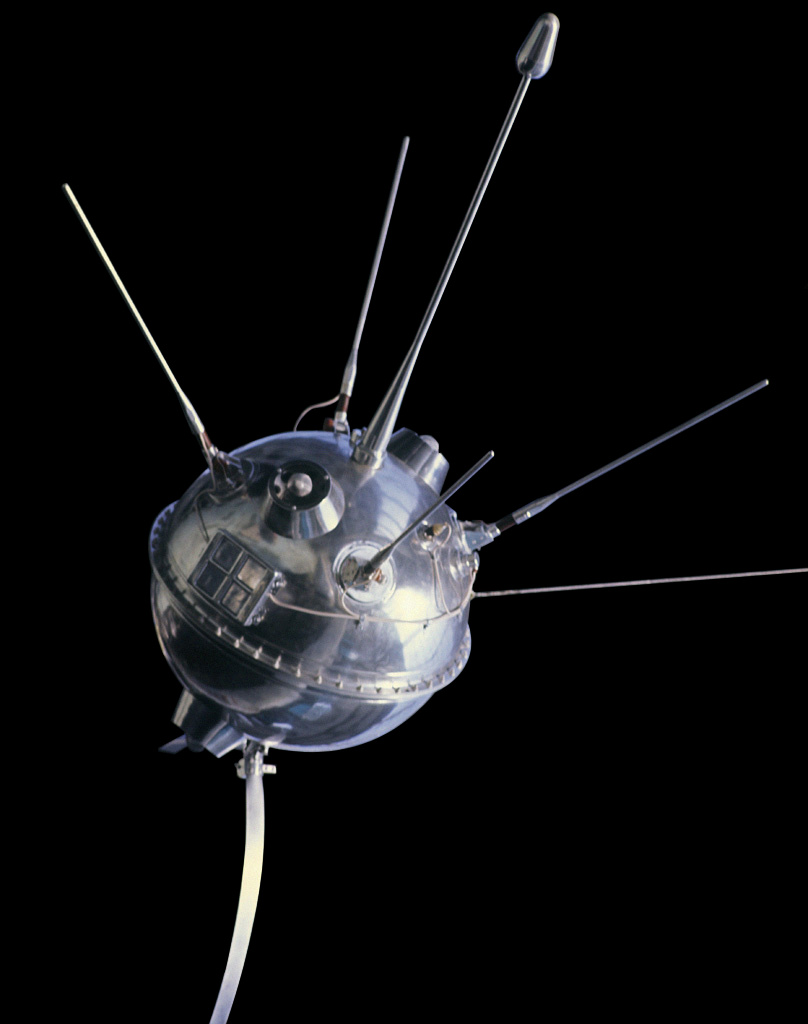
Ever hear of the Soviet Luna program? In the west, it was often called Lunik, if you heard about it at all. Luna was a series of unmanned moon probes launched between 1959 and 1976. There were at least 24 of them, and 15 were successful. Most of the failures were not reported or named. Luna craft have a number of firsts, but the one we are interested in is that it may have been the first space vehicle to be stolen — at least temporarily — in a cold war caper worthy of a James Bond novel.

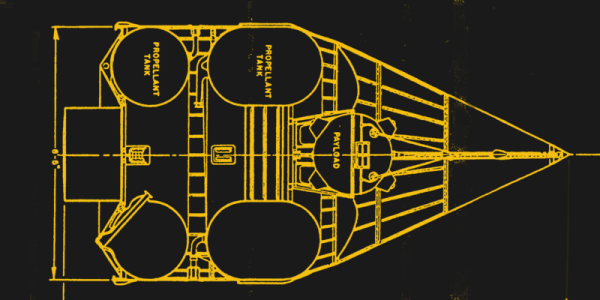
Luna-1 Payload

Around 1960, the Soviet Union toured several countries with exhibits of their industrial and technological accomplishments. One of the items on display was the upper stage of a Luna vehicle with windows cut out to show the payload inside. At first, the CIA suspected the vehicle was just a model. But they wanted to be sure.

The story is laid out in a CIA document from 1967 that was only declassified in 1994. Even then, the document has a lot of redactions in it. The paper is sparse on how they managed it, but when the exhibit closed — somehow — a group of intelligence operatives wound up inside the exhibition hall alone for 24 hours.

What they found was surprising. While the engine and most of the avionics were gone, the vehicle was the real article. They took measurements and photos, hoping that analysis would reveal more about the vehicle’s performance characteristics.

Here’s where you start getting into the redacted material. The team was able to get something from the probe — probably machine tooling marks — but there wasn’t enough detail to identify where and how they were made. They decided to get a team specializing in this kind of analysis to examine it more closely.

Continue reading “Spy Tech: Stealing A Moon Probe” →

Practical Public Key Cryptography

Encryption is one of the pillars of modern-day communications. You have devices that use encryption all the time, even if you are not aware of it. There are so many applications and systems using it that it’s hard to begin enumerating them. Ranging from satellite television to your mobile phone, from smart power meters to your car keys, from your wireless router to your browser, and from your Visa to your Bitcoins — the list is endless.

One of the great breakthroughs in the history of encryption was the invention of public key cryptography or asymmetrical cryptography in the 70’s. For centuries traditional cryptography methods were used, where some secret key or scheme had to be agreed and shared between the sender and the receiver of an encrypted message.

Asymmetric cryptography changed that. Today you can send an encrypted message to anyone. This is accomplished by the use of a pair of keys: one public key and one private key. The key properties are such that when something is encrypted with the public key, only the private key can decrypt it and vice-versa. In practice, this is usually implemented based on mathematical problems that admit no efficient solution like certain integer factorization, discrete logarithm and elliptic curve relationships.

But the game changer is that the public key doesn’t have to be kept secret. This allows cryptography to be used for authentication — proving who someone is — as well as for encryption, without requiring you to have previously exchanged secrets. In this article, I’ll get into the details of how to set yourself up so that anyone in the world is able to send you an e-mail that only you can read.
Continue reading “Practical Public Key Cryptography” →

3D Prints And Food

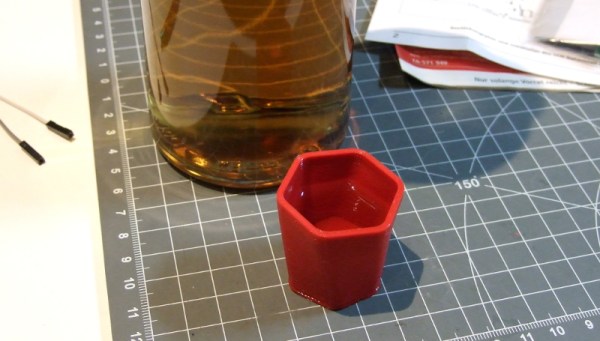
We recently ran a post about a cute little 3D printed elephant that could dispense booze. The design didn’t actually have the plastic touching the liquid — there was a silicone tube carrying the shots. However, it did spark a conversation at the secret Hackaday bunker about how safe it is to use 3D printed objects for food. In particular, when I say 3D printing, I’m talking fused deposition modeling. Yes, there are other technologies, but most of us are printing using filament laid out in layers with a hot nozzle.

There’s a common idea that ABS is bad in general, but that PET and PLA are no problem because there are food-safe versions of those plastics available. However, the plastic is only a small part of the total food safety picture. Let me be clear: I am not a medical professional and although my computers have run a few plastics plants in years past, I am not really an expert on polymer chemistry, either. However, I don’t use 3D printed materials to hold or handle food and while you might not drop dead if you do, you might want to reconsider.

Continue reading “3D Prints And Food” →

Inside Two-Factor Authentication Apps

Passwords are in a pretty broken state of implementation for authentication. People pick horrible passwords and use the same password all over the place, firms fail to store them correctly and then their databases get leaked, and if anyone’s looking over your shoulder as you type it in (literally or metaphorically), you’re hosed. We’re told that two-factor authentication (2FA) is here to the rescue.

Well maybe. 2FA that actually implements a second factor is fantastic, but Google Authenticator, Facebook Code Generator, and any of the other app-based “second factors” are really just a second password. And worse, that second password cannot be stored hashed in the server’s database, which means that when the database is eventually compromised, your “second factor” blows away with the breeze.

Second factor apps can improve your overall security if you’re already following good password practices. We’ll demonstrate why and how below, but the punchline is that the most popular 2FA app implementations protect you against eavesdropping by creating a different, unpredictable, but verifiable, password every 30 seconds. This means that if someone overhears your login right now, they wouldn’t be able to use the same login info later on. What 2FA apps don’t protect you against, however, are database leaks.

Continue reading “Inside Two-Factor Authentication Apps” →