Hackaday Links Column Banner

Hackaday Links: July 26, 2026

At a time when so-called “artificial intelligence” seems inescapable, we were encouraged to see news that Amazon will be cracking down on third-party sellers that use AI-generated images for their product listings. They won’t be prevented from using the images, but they will need to clearly indicate that they don’t represent reality and were produced via artificial means. This comes in response to a recently enacted New York law that requires the disclosure of AI in advertisements.
Will this be the end of the cat sleeping bag?

But it’s not quite a clear cut as it might seem on the surface, as the New York law is actually about AI-generated people rather than products. Specifically, it’s designed to make it clear when a “synthetic performer” has been used in place of a human actor. As such, it would appear that the easiest way for Amazon sellers to dodge the new rule is to simply not include any humans in their AI slop images and videos. In other words, they can continue to post fake pictures of products without having to inform the consumer so long as they don’t show a fake person holding it.

Under normal circumstances we’d leave something like this next one for our weekly security column, but the utter lack of security in the Pope’s official “Click To Pray” mobile application revealed by researcher BobDaHacker on Friday is just too good a story to pass up. For one thing, who knew that there was an “official” prayer app? We don’t dabble in theology around these parts, but we’re fairly sure the good book didn’t mention anything about requiring a smartphone to give praise.
Continue reading “Hackaday Links: July 26, 2026” →

This Week In Security: AI Is A Mess, Hacking Car Chargers, An OpenSSL DoS, And Factories Under Attack

[Ayush Paul] posts about extracting data from Claude agents while it accesses web data to fulfill user requests.

But it wasn’t that easy. [Ayush] discovered that Anthropic anticipated many of the attacks, and set up guardrails in an attempt to keep the agent from accessing arbitrary web sites. For Claude to access a website, the user has to specify it, it must be the results of a web search, or it must be referenced by a website previously specified by the user or returned in a search.

To convince the Claude agent to navigate a malicious site designed to extract data, Ayush formed a false warning that Cloudflare was blocking the agent for authentication purposes, and asked it to spell out the name of the agents owner by clicking a list of alphabetical links. Of course Claude trusts Cloudflare and wants to be helpful, so it cheerfully completed the task.

Once the agent is trapped in the false authentication loop, it can be interrogated for all sorts of information it knows about the owner: Ayush was able to convince it to disclose employer, and even data about the user that could be linked to security questions, like their home town.

Since Claude can be detected by the user agent (the field attached to web requests that tells the web server what sort of browser is requesting the page) custom information can be fed to the bot while users see a normal website; clicking a link looks completely normal, but asking an agent to summarize the site triggers fooling the bot into spilling the beans.

After reporting the issue, Ayush was told that Anthropic had already identified the issue internally, and eventually prevented the attack for now by preventing the agent from following links on external pages.

Grok sends entire codebases

Cereblab discovered that the Grok coding agent uploaded the entire content of the codebase it’s working with – and all Git history – to xAI servers, almost immediately. Even when told to never upload a file, the agent would reply “OK”, and then begin uploading the code bundle anyway.

If uploading your code to a remote server isn’t bad enough, and this could be extremely bad in some situations involving sensitive company code, including the entire Git history means that previously deleted files, like accidentally committed secrets or authentication credentials and tokens, were also leaked. Attempting to opt out by disabling options to improve the model by uploading code had no effect.

After gaining attention, Grok has added a privacy option to opt out of data retention. xAI has committed to deleting the retained uploaded code, but it is unclear if users will be told when their data has been removed. To actually prevent the agent from uploading local files to the xAI servers, even temporarily, a global flag “disable_codebase_upload” is required. Watch out, the privacy retention flags are only per-session!

Continue reading “This Week In Security: AI Is A Mess, Hacking Car Chargers, An OpenSSL DoS, And Factories Under Attack” →

Hackaday Europe 2026: Half Quad, Half Blimp: Test. Fly. Survive.

A great many drones out there, whether homebuilt or store-bought, follow the same basic format. Four motors, some kind of controller, and a lithium-polymer battery supplying the juice to keep everything in the air. It’s a format that produces a remarkably capable air vehicle, suitable for everything from high-speed camera work to urban search and rescue.

With that said, the format does have its limitations. [Suryansh Sharma] has been working on alternative designs for fancy and interesting drones that are half quadcopter and half blimp, and he came to Hackaday Europe 2026 to tell us all about it.

Continue reading “Hackaday Europe 2026: Half Quad, Half Blimp: Test. Fly. Survive.” →

Encryption In The 1790s

For as long as humans have had writing, there’s been a need to send secret messages. It is easy to think that Enigma machines and their immediate predecessors are old tech, but they are much more recent than ancient systems used by the Greeks and Romans. Even Thomas Jefferson, one of the founding fathers of the United States, was interested in encryption and is often said to have invented the Jefferson Disk machine for encryption. The truth is, the device is probably older than Jefferson, but he certainly thought about using it for secret communications.

Simple but Effective

Thomas Jefferson was, apparently, a fan of secret messages

The idea is simple. We make a series of disks. Each disk has a number on it and, around the edge, all the letters of the alphabet. The placement of each wheel with the same number is the same, but, overall, the arrangement is random. That is, all disks marked #5 might start with XCBYG, but all disks marked with #10 could start with FAYQL. You take one set of disks, and I keep the other set.

When we want to send secret messages, we agree to arrange our disks on an axle in the same order. Jefferson used a 36-disk system, so we might agree to go left to right with the odd numbers first and then the even numbers, or any other setup that we could agree on.

Encryption

Once the wheels are in place, encryption is simple. There’s a bar across the device, and you line up your message using a wheel for each letter: ENEMYCOMESBYSEA, for example. Then you look at any different row, which will now read something crazy like: FSRSSXQCGAEEFOR (plus the random letters on the rest of the disks). That’s the message you send.

Continue reading “Encryption In The 1790s” →

The Need For Speed: Internet Speed Measurement (or DIY?)

Car enthusiasts want to know how quickly they can make a quarter mile. Weightlifters are forever trying to add one more plate to the bar. Internet denizens have their own favorite number to brag about: the result from a speed test.

The ritual is familiar. Close a few browser tabs, click the big “Go” button, and watch the needle climb. Perhaps you pay for gigabit service and see 940 megabits per second, which produces a satisfied nod. Perhaps you see 299 megabits and begin obsessing over network hardware. But before you get too excited either way, try another test. There is a fair chance it will give you a different answer.

That does not necessarily mean one test is lying. “Internet speed” is not a single physical quantity waiting to be measured. A speed test measures the performance of a particular device, over a particular local connection, through a particular ISP route, to a particular server, at a particular time using a particular test method. Change any of those things and the answer can change too. Continue reading “The Need For Speed: Internet Speed Measurement (or DIY?)” →

Postal IRCs Are Almost A Thing Of The Past

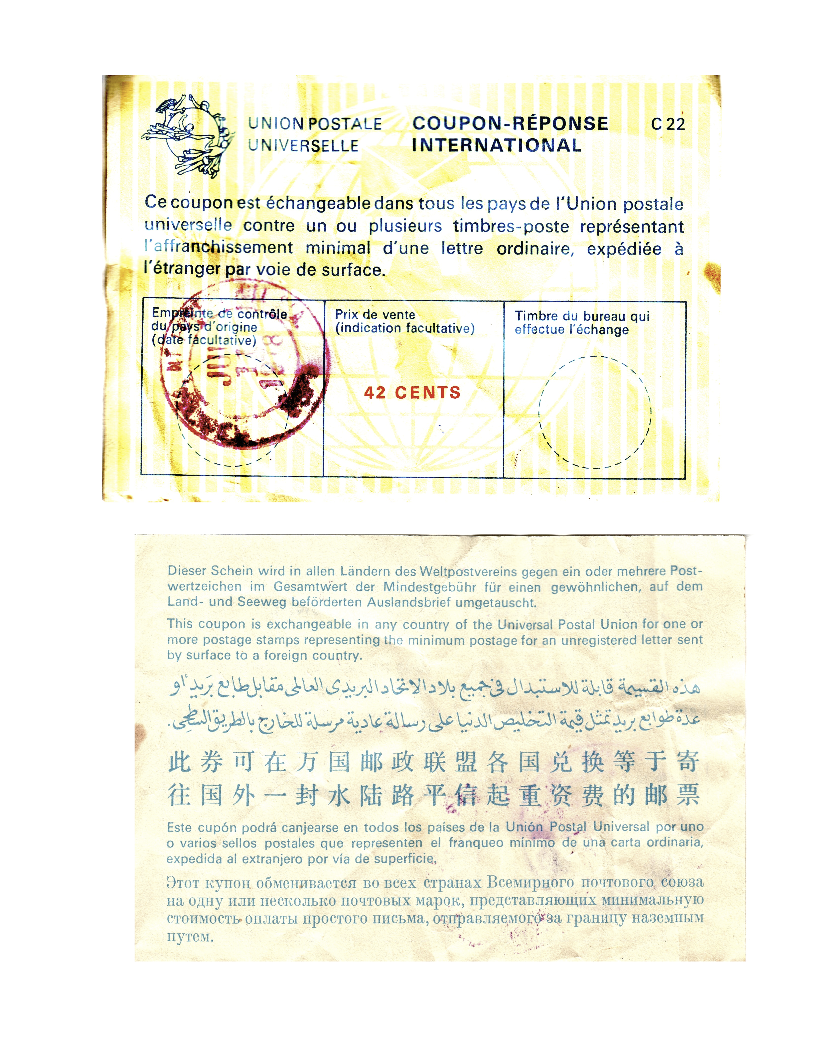
Have you ever found out that something you remember from your youth is now gone, and you didn’t even notice? If you are a certain age, you might feel that way when I deliver the news: You haven’t been able to buy International Reply Coupons (IRCs) at a US Post Office since early 2013. By the end of 2026, you won’t be able to buy them anywhere. The age of the IRC is over.

What’s an IRC?

An IRC from 1978 (public domain).

If that didn’t mean anything to you, you might be too young to remember, or maybe you just weren’t into shortwave listening or ham radio. Although there were other reasons to get IRCs, a radio hobby is the most likely reason a Hackday reader would have bought an IRC.

For radio purposes, here’s the problem. You’ve worked on your station for months, and one winter night, you finally pull in that rare station from Luxembourg. They’ll send you a QSL card to verify that you heard them. You only have to send them a letter telling them what time you heard them, what frequency, and some details about the program you heard. But they probably don’t want to pay the postage required to send hundreds or thousands of cards overseas.

While this is a radio-specific problem, you might find the same issue with pen pals or when trying to buy things from an overseas company.

SASE

If everyone were in the same country, the solution would be easy. Take a stamp, put it on an envelope that has your address on it, and stuff it in with the letter. Or, you could just drop a stamp or two in the letter you sent.

The problem is, US postage won’t help Radio Luxembourg. On the other hand, the effort required for you to buy postage that works in Luxembourg would have been a nightmare.

Enter the UPU

The Universal Postal Union is a UN agency that is effectively an association of post offices in 192 countries. Their charter is to facilitate mailing things worldwide.

The IRCs date back to 1906. The idea is you buy an IRC at your post office. You send it to Radio Luxembourg, or wherever. There, the mail person at the radio station could go to their post office and trade the coupon for enough local postage to send a surface letter worldwide.

Continue reading “Postal IRCs Are Almost A Thing Of The Past” →