Thorough Macbook Charger Teardown Reveals Some Complex Circuitry

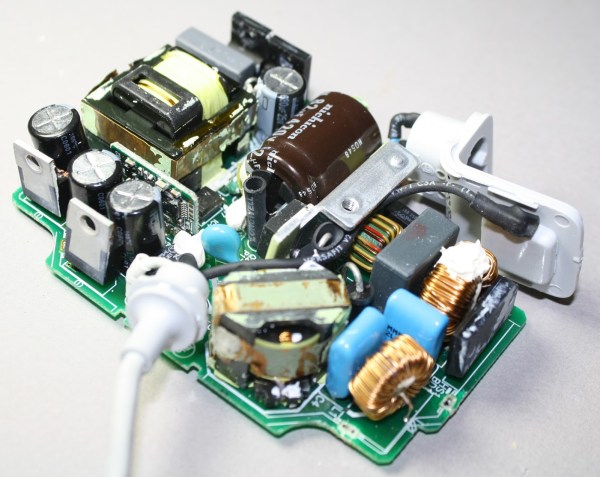
Apple has a reputation in the tech world as being overpriced, and nowhere is that perception more common than in the Hackaday comments. The standard argument, of course, is that for a device with equivalent specs, Apple charges a lot more than its competitors. That argument is not without its flaws, especially when you consider factors other than simple specs like RAM and processor speed, and take into account materials used and build quality. But, as this teardown by [Ken Shirriff] shows, Apple’s attention to detail extends beyond simply machining Macbook bodies out of aluminum.

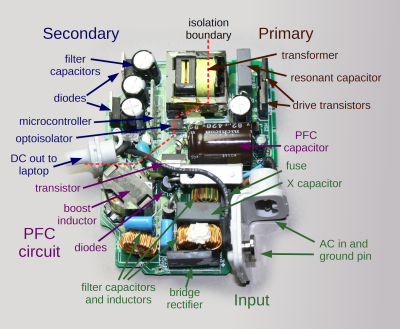
In his teardown, [Ken Shirriff] thoroughly investigates and describes all of the components and circuitry that go into the ubiquitous Macbook charger. Why does it cost $79? Other than the MagSafe connector, what makes it any better than the charger that came with your Toshiba Satellite in the ’90s? Isn’t it just a transformer to convert AC power to DC?
components1

[Ken Shirriff] answers all of this and more, and you may be surprised by what he found. As it turns out, the Macbook charger isn’t just a transformer in a plastic case with a fancy magnetic connector. There is a lot of high-quality circuitry involved to make the power output as clean and stable as possible, and to avoid potential damage to your Macbook that could be caused by dirty power or voltage spikes. Does it justify the costs, even with so many reported failures? That’s for you to decide, but there is no questioning that Apple put more thought into their chargers than simply converting AC to DC.
Fail Of The Week: Dave Jones And The Case Of The Terrible Tablet

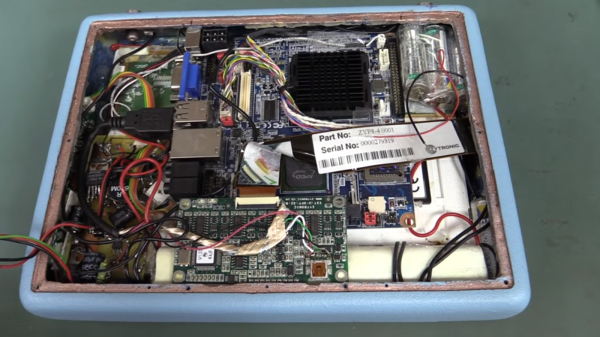
Nothing spices up a quiet afternoon like the righteous indignance of an upset engineer, especially if that engineer is none other than [Dave Jones], on his EEVblog YouTube Channel. This week [Dave] has good reason to be upset. A viewer sent him what looked to be a nondescript 2010 era tablet from a company called Esinomed. From the outside it looked like a standard issue medical device. Opening up the back panel tells a completely different story though. This thing is quite possibly the worst hack job [Dave] (and we) have ever seen. This is obviously some kind of sales demo or trade show model. Even with that in mind, this thing is a fail.

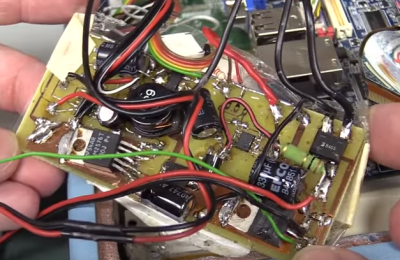
wtf-solderThe tablet is based upon an off-the-shelf embedded PC motherboard and touchscreen controller. [Dave] took some offense at the hacked up USB connector on the touchscreen. We have to disagree with [Dave] a bit here, as the video seems to show that a standard mini-b connector wouldn’t have fit inside the tablet’s case. There’s no excuse for the USB cable shield draped over the bare touch controller board though. Things go downhill from there. The tablet’s power supply is best described as a bizarre mess. Rather than use a premade DC to DC converter, whoever built this spun their own switch mode power supply on a home etched board. The etching job looks good, but everything else, including the solder job, is beyond terrible. All the jumps and oddly placed components make it look like a random board from the junk bin was used to build this supply.
The story gets even worse with the batteries. The tablet has horribly hand soldered NiMH cells shoved here, there and everywhere. Most of the cells show split shrink wrap – a sure sign they have been overheated. It’s hard to tell from the video, but it appears as if a few cells have their top mounted vent holes covered with solder. That’s a great way to turn a simple rechargeable battery into a pipe bomb. Batteries can be safely hand soldered – Radio Controlled modelers did it for decades before LiPo cells took over.

We’ve all hacked projects together at the last minute; that’s one of the things we celebrate here on Hackaday. However, since this is a commercial medical device (with serial number 11 no less) we have to stamp this one as a fail.

Continue reading “Fail Of The Week: Dave Jones And The Case Of The Terrible Tablet” →

The $5 Raspberry Pi Zero

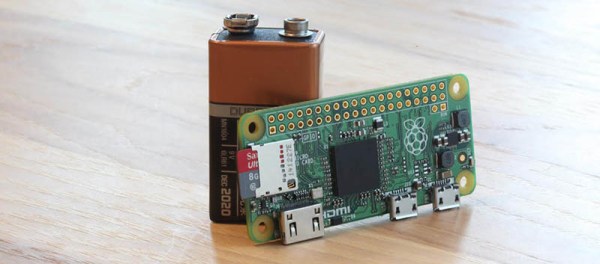
Rumors about a new Raspberry Pi have been circulating around the Internet for the past week or so. Speculation has ranged from an upgraded Model A or compute module to a monster board with Gigabit Ethernet, USB 3.0, SATA and a CPU that isn’t even in production yet. The time is now, and the real news is even more interesting: it’s a $5 Raspberry Pi Zero. It’s the smallest Pi yet, while still keeping the core experience.

Continue reading “The $5 Raspberry Pi Zero” →

Defeating Chip And PIN With Bits Of Wire

One of many ways that Americans are ridiculed by the rest of the world is that they don’t have chip and PIN on their credit cards yet; US credit card companies have been slow to bring this technology to millions of POS terminals across the country. Making the transition isn’t easy because until the transition is complete, the machines have to accept both magnetic stripes and chip and PIN.

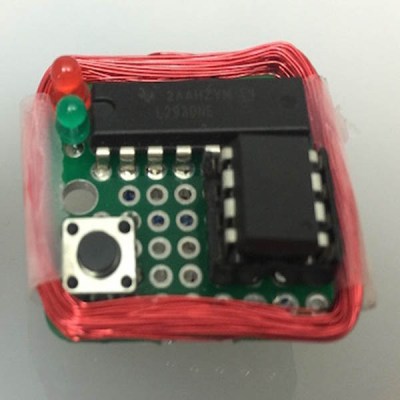
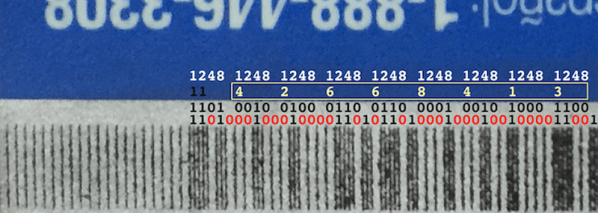
This device can disable chip and PIN, wirelessly, by forcing the downgrade to magstripe. [Samy Kamkar] created the MagSpoof to explore the binary patterns on the magnetic stripe of his AmEx card, and in the process also created a device that works with drivers licenses, hotel room keys, and parking meters.

magspoofThe electronics for the MagSpoof are incredibly simple. Of course a small microcontroller is necessary for this build, and for the MagSpoof, [Samy] used the ATtiny85 for the ‘larger’ version (still less than an inch square). A smaller, credit card-sized version used an ATtiny10. The rest of the schematic is just an H-bridge and a coil of magnet wire – easy enough for anyone with a soldering iron to put together on some perfboard.
By pulsing the H-bridge and energizing the coil of wire, the MagSpoof emulates the swipe of a credit card – it’s all just magnetic fields reversing direction in a very particular pattern. Since the magnetic pattern on any credit card can be easily read, and [Samy] demonstrates that this is possible with some rust and the naked eye anyway, it’s a simple matter to clone a card by building some electronics.

[Samy] didn’t stop there, though. By turning off the bits that state that the card has a chip onboard, his device can bypass the chip and PIN protection. If you’re very careful with a magnetized needle, you could disable the chip and PIN protection on any credit card. [Samy]’s device doesn’t need that degree of dexterity – he can just flip a bit in the firmware for the MagSpoof. It’s all brilliant work, and although the code for the chip and PIN defeat isn’t included in the repo, the documents that show how that can be done exist.

[Samy]’s implementation is very neat, but it stands on the shoulders of giants. In particular, we’ve covered similar devices before (here and here, for instance) and everything that you’ll need for this hack except for the chip-and-PIN-downgrade attack are covered in [Count Zero]’s classic 1992 “A Day in the Life of a Flux Reversal“.

Thanks [toru] for sending this one in. [Samy]’s video is available below.

Continue reading “Defeating Chip And PIN With Bits Of Wire” →

APRS Repeaters Get The Signal Out Of Mammoth Cave

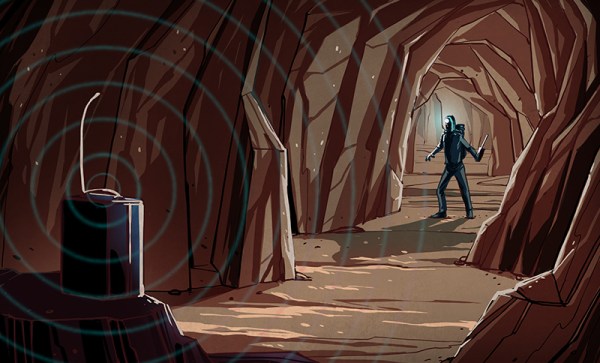
APRS Cave-Link uses the amateur radio’s Automatic Packet Reporting System (APRS) inside caves to get their position data (and other messages) out.

Imagine that you’re coordinating a large scale search-and-rescue mission in a cave. You need to know where all your groups are, and whether or not they’ve found anything. But how do they all communicate to the command center?

You’d guess radio, but you’d guess wrong. Radio doesn’t propagate well at all in a maze of twisty passages, all alike; rocks absorb radio waves, especially in the VHF/UHF range that’s best suited for most small radios. In the past, you’d run wire and transmit along it. This article runs through the options in detail. But adding miles of wire to your already heavy caving and climbing gear is a nuisance or worse.

Continue reading “APRS Repeaters Get The Signal Out Of Mammoth Cave” →

Building The Infinite Matrix Of Tamagotchis

Tamagotchi is a digital pet, living in and cared for through a key-chain size piece of hardware. The mid-90’s toy lives in pop culture, but now it lives well beyond. A limitless network of Tamagachi has been created using some amazing tricks to feed, socialize, and monitor the beast now known as the Tamagachi Singularity.

Last weekend at the Hackaday SuperConference we were graced with a talk by [Jeroen Domburg], a.k.a. [Sprite_tm]. [Sprite] is a favorite of ours and over the years his hacker cred includes everything from reverse engineering hard drive controller chips to putting video games in his keyboard.

[Sprite] is also something of an Architect, and like all Architects he only wants what is best for the system he created. In this case, it’s a Matrix of Tamagotchis. [Sprite] created a hive of Tamagotchis that are able to interact with each other in their own separate world. The best part about this Matrix? There’s no allusions to violating the laws of thermodynamics in the exposition.

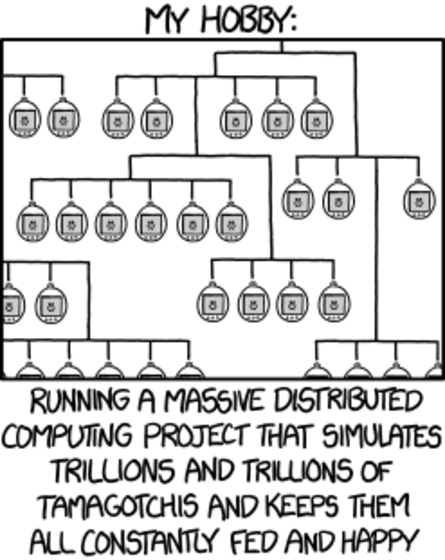
xkcd.com/1546
xkcd.com/1546

Like all good hacks, a Tamagotchi Matrix wasn’t created in a vacuum. A few years ago at 29C3, [Natalie Silvanovich] dumped the ROM in the current generation of Tamagotchis. This is an incredible feat of reverse engineering, that allows anyone to use the full capabilities of the 6502-based microcontroller that controls these digital pets

After [Sprite] figured out how to read and run the code in the Tamagotchi, the next obvious step towards a world of egg-shaped pods containing an entire population of Tamagotchis is virtual Tamagotchis. [Sprite] used a hard-coded state machine that takes care of pooping, flushing, training, feeding, and turning the lights off at bedtime.

With a single Tamagotchi described as a state machine, it’s a simple matter to build another. This is where things get interesting and Matrix-ey. Tamagotchis don’t live alone; they have an IR LED and receiver that allows them to interact with each other, eat, play, marry, and have kids. Emulating a single Tamagotchi is one thing, but controlling multiples is another thing entirely; some sort of protocol was needed to breed Tamagotchis and keep them happy and well-fed.

Continue reading “Building The Infinite Matrix Of Tamagotchis” →

Swans, Pigs, And The CIA: An Unlikely Radio Story

Shortwave radio is boring, right? Maybe not. You never know what intrigue and excitement you might intercept. We recently covered secret number stations, and while no one knows for sure exactly what their purpose is, it is almost surely involving cloaks and daggers. However, there’s been some more obvious espionage radio, like Radio Swan.

The swan didn’t refer to the animal, but rather an island just off of Honduras that, until 1972, was disputed between Honduras and the United States. The island got its name–reportedly–because it was used as a base for a pirate named Swan in the 17th century. This island also had a long history of use by the United States government. The Department of Agriculture used it to quarantine imported beef and a variety of government departments had weather stations there.

You might wonder why the United States claimed a tiny island so far away from its shores. It turns out, it was all about guano. The Guano Islands Act of 1856 allowed the president to designate otherwise unclaimed territory as part of the United States for the purpose of collecting guano which, in addition to being bird excrement, is also important because it contains phosphates used in fertilizer and gunpowder. (Honestly, you couldn’t make this stuff up if you tried.)

However, the most famous occupant of Swan Island was Radio Swan which broadcast on the AM radio band and shortwave. The station was owned by the Gibraltar Steamship Company with offices on Fifth Avenue in New York. Oddly, though, the company didn’t actually have any steamships. What it did have was some radio transmitters that had been used by Radio Free Europe and brought to the island by the United States Navy. Did I mention that the Gibraltar Steamship Company was actually a front for the Central Intelligence Agency (CIA)?

Continue reading “Swans, Pigs, And The CIA: An Unlikely Radio Story” →