We’re Hiring: Come Join Us!

You wake up in the morning, and check Hackaday over breakfast. Then it’s off to work or school, where you’ve already had to explain the Jolly Wrencher to your shoulder-surfing colleagues. And then to a hackspace or back to your home lab, stopping by the skull-and-cross-wrenches while commuting, naturally. You don’t bleed red, but rather #F3BF10. It’s time we talked.

The Hackaday writing crew goes to great lengths to cover all that is interesting to engineers and enthusiasts. We find ourselves stretched a bit thin and it’s time to ask for help. Want to lend a hand while making some extra dough to plow back into your projects? We’re looking for contributors to write a few articles per week and keep the Hackaday flame burning.

Contributors are hired as private contractors and paid for each article. You should have the technical expertise to understand the projects you write about, and a passion for the wide range of topics we feature. You’ll have access to the Hackaday Tips Line, and we count on your judgement to help us find the juicy nuggets that you’d want to share with your hacker friends.

If you’re interested, please email our jobs line (jobs at hackaday dot com) and include:

  • One example article written in the voice of Hackaday. Include a banner image, between 150 and 300 words, the link to the project, and any in-links to related and relevant Hackaday features. We need to know that you can write.
  • Details about your background that make you a valuable addition to the team. What do you like, and what do you do?
  • Links to your blog / project posts / etc. that have been published on the Internet, if any.
  • Or just write us with questions. We’ll be glad to answer.

Ladies and Gentlemen, start your applications!
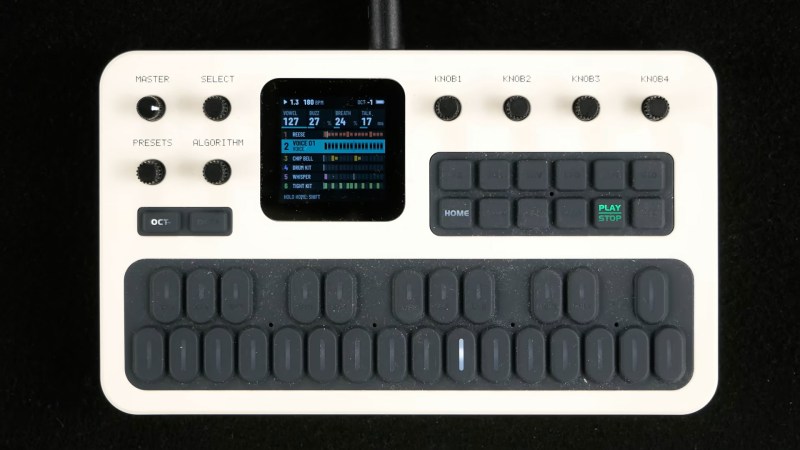
The FM-1: Open Source Hacked Open, Vibe Coding, And Farting Synthesizers

The M-Vave FM-1 was a pretty unremarkable little synthesizer “toy” until the open-source synth hackers took it over. Now, it’s a sweet platform for exploration, the incredible work done by the community has encouraged the manufacturer to release an open SDK, and it has recently taken the global synth nerd community by storm. (It has sadly also gotten about a 50% markup in the last month due to this popularity.)

It’s the perfect storm of inexpensive hardware, vibe-coded software, and easy-to-use tooling that enables synthesizer firmware-hacking for the mainstream. It is also the fashionable box of the moment in a nerdy niche of the synthesizer world at the moment and it’s something that we’re going to see in non-synthesizer contexts as well, so buckle up.

Continue reading “The FM-1: Open Source Hacked Open, Vibe Coding, And Farting Synthesizers” →

How Metal Foam Could Make Cars Safer

Once upon a time, cars were merely designed for performance, comfort, and usability, with little regard to how safe they may or may not be in the event of a collision. In this era, it turned out that most cars were horrific deathtraps, but eventually outside pressure led the industry to try and make cars safer. It was realized that making crashes more survivable with less injuries was generally a good thing.

Ever since, there has been a general push towards making cars ever safer as time goes on. To that end, researchers have been exploring whether the use of metal foams could aid in further crash safety improvements.

Continue reading “How Metal Foam Could Make Cars Safer” →

Hackaday Links Column Banner

Hackaday Links: November 15, 2026

Another Hackaday Supercon is in the history books. The new venue was amazing. We had more attendees than ever and still had room to spare. You can find many of the talks, including the lightning talks, in the live section of our YouTube channel. You can even watch the final badge hacking competition.

Continue reading “Hackaday Links: November 15, 2026” →

Hackaday Podcast Episode 394: Linux In Weird Places, Yet More Hidden SDRs, And A Supercon Wrapup

Hackaday Editors Elliot Williams and Tom Nardi are back from Supercon, and they’ve got plenty of thoughts to share about it. But before they discuss this weekend’s higlights, they’ll cover the recent scuttling of the legendary SS United States, the discovery of even more hidden software-defined radios in everyday gadgets, Linux running on Kindles and microcontrollers, and a Game Boy flash cart that’s not designed for playing games. You’ll also hear about LEGO 3D printers, finding out where a video was recorded by the sound of the airplanes in the background, and a website that lets you listen in on the satellites flying over your house.

Check out the links if you want to follow along, and as always, tell us what you think about this episode in the comments!

Direct download, DRM-free MP3.

Continue reading “Hackaday Podcast Episode 394: Linux In Weird Places, Yet More Hidden SDRs, And A Supercon Wrapup” →

This Week In Security: Four-Digit Patch Tuesday, SSH Exploited, GitBook Breach, Android GhostMap

It’s the second Tuesday of the month, and that means another Microsoft Patch Tuesday. The new normal is that the numbers are hard to believe. Brian Krebs reports that this month’s release fixes nearly 1,100 vulnerabilities, 63 of them rated critical, and over 500 that let an attacker elevate their privileges. Only one is reported as actively exploited: CVE-2026-124194, a spoofing bug in Outlook. Microsoft has now shipped more than 5,100 security fixes this year, after more than 1,400 last month, compared to an average of around 100 a month last year. Obviously AI tools get the credit for the volume of bugs fixed, but also of course for the volume of bugs found.

Everyone else is busy too. Apple pushed out-of-cycle updates for at least nine vulnerabilities across its operating systems, including an iMessage flaw which could let a remote attacker join a group chat and read its messages, and backported the fixes to iOS 18. Chrome 157 fixes CVE-2026-125350, another Chrome zero-day, a week after a Chrome release which fixed more than 200 bugs, Firefox 160 fixes almost 100 CVEs, and Adobe fixed more than 110.

Also since last week, zlib 1.4 shipped with more than a dozen security fixes, eight more vulnerabilities were disclosed in the X.Org server and XWayland, and Microsoft’s own Azure Linux update lists more than 470 CVEs fixed across the open source packages it ships. And for a perfect encapsulation of 2026, last month’s Patch Tuesday included a remote code execution bug in Windows Paint (CVE-2026-83844), though its description admits the code runs locally. So now I guess you can pop Calc through Paint? Does this count as a win?

Despite the absolute firehose of vulnerabilities, the Krebs article notices that of the roughly 95,000 CVEs assigned this year, only around 200 made it into the CISA list of known expoited vulnerabilities (KEV). If you have to pick and choose which updates are the most critical, start there.

Continue reading “This Week In Security: Four-Digit Patch Tuesday, SSH Exploited, GitBook Breach, Android GhostMap” →

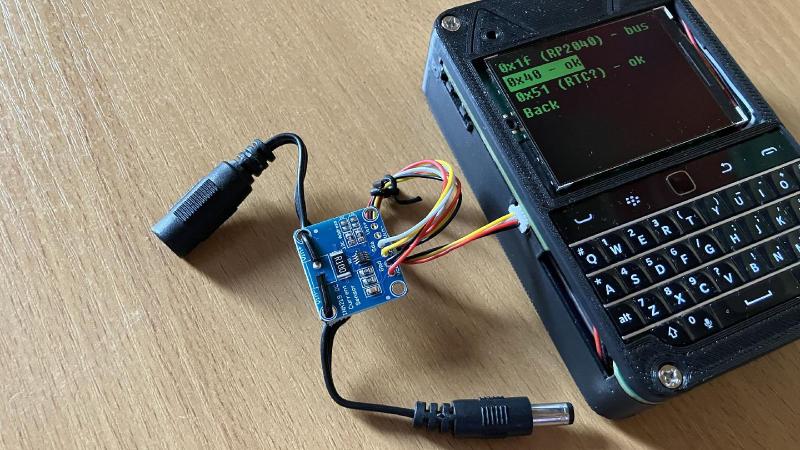
An INA219 board with a QWIIC connector and "female barrel jack to male barrel jack" cable soldered on. the qwiic end is plugged into the side of the Blepis PDA, with the screen showing a device found on the 0x40 address

Just Use QWIIC Already

Years ago, I wrote an article describing different I2C-on-a-connector ecosystems, explaining their strengths, weaknesses, and implementation details, as well as piling on a heap of fun stories. Looking back at it, it’s a great reference article, if I do say so myself. In particular, I highlighted QWIIC, which is a Sparkfun-borne standard for putting 3.3 V I2C on a JST-SH (or compatible) 4-pin connector.

I’ve since implemented a fair bit of QWIIC, and grew to like it so much more. I’m here to explain to you why you ought to be putting those JST-SH connectors in everything you design that touches I2C, all the cool things they let you do, where to buy a lot of cheap cables at once, and all the references you could need. I will also tell you about my USB pinout for QWIIC, something you should definitely know about.

In2ispensable Interconnect

Continue reading “Just Use QWIIC Already” →