New A4 Jailbreak Debacle Puts The Brakes On For IPad

If you’ve been waiting in the wings for the next Jailbreak to be release you should know there’s been a bit of a speed bump. [ChronicDevTeam], which has been working on an exploit for A4-based iOS devices called SHAtter, tweeted last Thursday that the fully tested, untethered, and unpatchable package knows as greenpois0n would be released today. But on Friday [Geohot], who you may remember from the PlayStation 3 Hypervisor exploit, rolled out his own mostly untested and admittedly beta jailbreak called limera1n.

So where does that leave the situation? Because [geohot] used a different exploit, the [ChronicDevTeam] decided not to release greenp0ison. If they did, it would give Apple a chance to block two different exploits. Instead they are working feverishly to incorporate, test, and repackage using the same exploit as limera1n.

If you don’t want to wait, jailbreak now, but you risk problems with an unstable exploit method that is only available for Windows.

[via @ChronicDevTeam]
IPhone Drum Machine Isn’t Synthesized

There was a time when a drummer would grab some sticks and lay out a groove using the items around him as instruments. [Lsa Wilson] would rather not work quite that hard and has chosen to do the same thing by tapping on an iPhone screen. As you can see in the clip after the break, many of the items in the room around him have been fitted with solenoids. Each is connected to an Arduino which is then controlled by Open Sound Control and interfaced with the iPhone via TouchOSC. We love the sounds being created and can’t help being reminded of the Multixylophoniomnibus.

Hexapod Controlled By Android And IPhone

[youtube=http://www.youtube.com/watch?v=NvEBUd_EqbQ]

This video is a blatant example of having too many high-end toys but we love it anyway. [Robert Stephenson] is controlling a rather awesome-looking hexapod via a Bluetooth connection to his HTC Hero. The app allows on-screen selections to decide which portion of the robot will move as a result of accelerometer data from the handheld. The only thing we saw that was missing is a camera feed to the phone.

But this hack doesn’t stop there. The Hero can be used to host a WiFi network while still connected to the hexapod. The second half of the video shows an iPod Touch connecting via WiFi and controlling the bot. Now head on over to the laser cutter to start that hexapod build, and finish up by getting elbow-deep into some Android development.

Make IPhone A Penetration Testing Tool

[Nicholas Petty] has posted a guide to setting up your iPhone as a penetration tester. You already carry it around with you and, although not too beefy, it does have the hardware you need to get the job done. So if you’re not interested in building a drone or carrying around a boxy access point try this out. The first step is to jailbreak your device and setup OpenSSH so that you can tunnel in for the rest of the setup. From there the rest of the setup is just acquiring build tools and compiling pentesting programs like Aircrack-ng, Ettercap, Nikto2, and the Social Engineering Toolkit. You’ll be up to no good testing your wireless security in no time.

Reverse Engineering Apple’s Recharging Scheme

[vimeo=http://vimeo.com/13835359]

[Ladyada] has been hard at work reverse engineering the charging method used by Apple products. This saga takes us through the years as new devices were released and subsequently broke Minty Boost’s charging capabilities. It seems the data lines were gradually adopted as a means for iPhones and iPods to identify the charger that had been connected. By adding voltage dividers to the D+ and D- lines you can instruct the handheld to pull 1 Amp (with data voltages of 2.8v and 2.0v) for wall chargers or 0.5 Amps (2.0v on both data lines) for portable chargers. In the video above [Ladyada] removes the surface mount resistors from a commercial charger in order to measure the voltage divider and discover the secret.

Super Simple Gaming Controller For Android Or IPhone

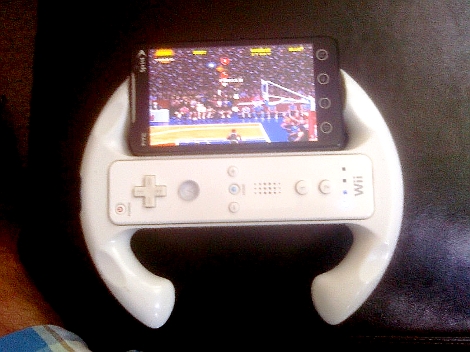
If you’ve got an iPhone or Android device that you use with a Wii remote when gaming, this quick hack will give you the third hand you need to manage all of that hardware. [Syanni85] mounted his Android phone to a Wii wheel for just a few dollars in parts. He ran across the wheel itself at the dollar store, and the phone is held in place using a universal mounting bracket. A small square pad sticks onto the back of any device and mates with a base. He cut off the unnecessary parts of the base and glued it to the back of the wheel.

If you haven’t tried using a Wii remote with your phone yet, find out how to do it with iPhone or with Android.

Solar MintyBoost

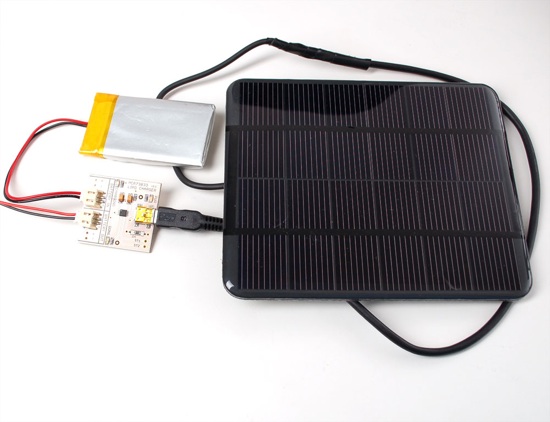
We first wrote about the MintyBoost back in 2006. Today, Adafruit has created a tutorial for making a solar powered MintyBoost. Using a MintyBoost, a solar panel, LiPo battery and a charger, they built on their Solar LiPoly tutorial. They fed the power tap output of the LiPoly charger into the battery input of the MintyBoost to perform the voltage step-up for USB devices. Based on an instructable that used SparkFun parts, this tutorial shows how to use parts that are available from one source. We hear that there will be some evolution of the MintyBoost coming down the line that will including charging capabilities.