Fueling Up For Fusion: MAST’s Super-X, JET’s Deuterium-Tritium Experiments For ITER, And More

We’ve had nuclear fission reactors in operation all over the world for ages, but nuclear fusion always seems to be a decade or two away. While one cannot predict when we’ll reach the goal of sustained nuclear fusion, the cutting edge in test hardware is advancing at a rapid pace that makes us optimistic. Beginning as soon as this month and extending over a few years, we’re living through a very exciting time for nuclear fusion and plasma physics.

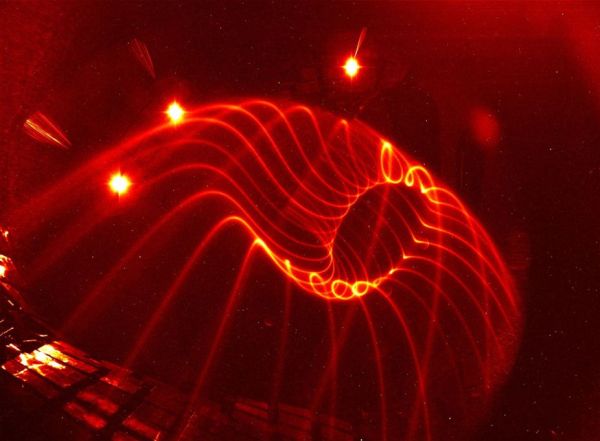
The Mega Ampere Spherical Tokamak (MAST) got a big upgrade to test a new cooled divertor design. JET (Joint European Torus) will be testing the deuterium-tritium fuel mixture that will be powering the ITER (the research project whose name began as an acronym for International Thermonuclear Experimental Reactor but has since been changed to just ITER). And the Wendelstein 7-X stellarator is coming back online with upgraded cooled divertors by next year.

Here the MAST Upgrade’s Super-X divertors have so far shown a ten-fold decrease in the temperature which the divertor is exposed to while carrying thermal energy out of the tokamak reactor. This means a divertor design and ultimately a fusion reactor that will last longer between maintenance sessions. On the stellarator side of things, Wendelstein 7-X’s new divertors may allow it to demonstrate the first continuous operation of a stellarator fusion reactor. Meanwhile, JET’s fuel experiments should allow us to test the deuterium-tritium fuel while ITER is working towards first plasma by 2025.

Continue reading “Fueling Up For Fusion: MAST’s Super-X, JET’s Deuterium-Tritium Experiments For ITER, And More” →

Anti-Gravity, Time Travel, And Teleportation: Dr. Hamming Gives Advice

You may not know the name [Richard Hamming], but you definitely use some of his work. While working for Bell Labs, he developed Hamming codes — the parent of a class of codes that detect, and sometimes correct, errors in everything from error-correcting memory to hard drives. He also worked on the Manhattan Project and was a lecturer at the Naval Postgraduate school.

Turns out [Hamming] has an entire class from the 1990s on YouTube and if you are interested in coding theory or several other topics, you could do worse than watch some of them. However, those videos aren’t what attracted me to the lectures. As the last lecture of his course, [Hamming] used to give a talk called “You and Your Research” and you can see one of the times he delivered it in the video below. You might think that it won’t apply to you because you aren’t a professional academic or researcher, but don’t be too quick to judge.

Turns out, [Hamming’s] advice — even by his own admission — is pretty general purpose for your career or even your life. His premise: As far as we know, you have one life to live, so why shouldn’t it be a worthwhile one by your definition of worthwhile.

Along the way, he has an odd combination of personal philosophy, advice for approaching technical problems, and survival skills for working with others. If you are in the field, you’ll probably recognize at least some of the names he drops and you’ll find some of this technical advice useful. But even if you aren’t, you’ll come away with something. Some of it seems like common sense, but it is different, somehow, to hear it spoken out loud. For example:

If you don’t work on important problems, it’s not likely that you’ll do important work.

One piece of technical advice? Don’t waste time working on problems you have no way to attack. He points out that anti-gravity, time travel, and teleportation would be very lucrative. But why work on them when there appears to be no way to even remotely accomplish them today. Well, at least when he said that. There has been a little progress on a form of teleportation, but that wasn’t what he was talking about anyway.

While not a hack in the traditional sense, examining your life, career, and technical research to improve your own effectiveness is something to take seriously. We were hoping he would throw in a joke about error-correcting your career, but unless we blinked, no such luck.

Hamming’s work on block codes was followed about ten years later by the Reed-Solomon code which is found nearly everywhere now. Hamming is also associated with the term “hamming distance,” something we talked about when discussing Gray code.

Continue reading “Anti-Gravity, Time Travel, And Teleportation: Dr. Hamming Gives Advice” →

Virgin Galactic’s Long Road To Commercial Spaceflight

To hear founder Richard Branson tell it, the first operational flight of Virgin Galactic’s SpaceShipTwo has been 18 months out since at least 2008. But a series of delays, technical glitches, and several tragic accidents have continually pushed the date back to the point that many have wondered if it will ever happen at all. The company’s glacial pace has only been made more obvious when compared with their rivals in the commercial spaceflight field such as SpaceX and Blue Origin, which have made incredible leaps in bounds in the last decade.

Richard Branson watching Unity’s test flight.

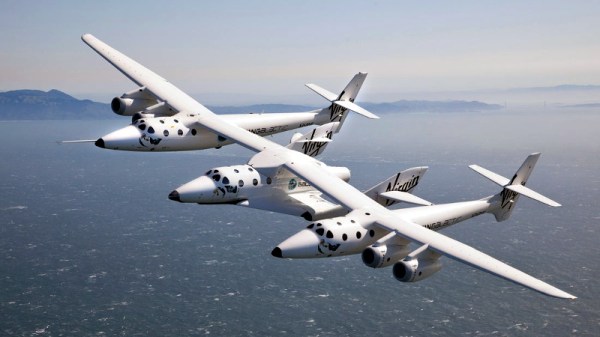
But now, at long last, it seems like Branson’s suborbital spaceplane might finally start generating some income for the fledgling company. Their recent successful test flight, while technically the company’s third to reach space, represents an important milestone on the road to commercial service. Not only did it prove that changes made to Virgin Space Ship (VSS) Unity in response to issues identified during last year’s aborted flight were successful, but it was the first full duration mission to fly from Spaceport America, the company’s new operational base in New Mexico.

The data collected from this flight, which took pilots Frederick “CJ” Sturckow and Dave Mackay to an altitude of 89.23 kilometers (55.45 miles), will be thoroughly reviewed by the Federal Aviation Administration as part of the process to get the vehicle licensed for commercial service. The next flight will have four Virgin Galactic employees join the pilots, to test the craft’s performance when loaded with passengers. Finally, Branson himself will ride to the edge of space on Unity’s final test flight as a public demonstration of his faith in the vehicle.

If all goes according to plan, the whole process should be wrapped up before the end of the year. At that point, between the government contracts Virgin Galactic has secured for testing equipment and training astronauts in a weightless environment, and the backlog of more than 600 paying passengers, the company should be bringing in millions of dollars in revenue with each flight.

Continue reading “Virgin Galactic’s Long Road To Commercial Spaceflight” →

Living Robots: Revisiting BEAM

You’re hit by the global IC shortage, reduced to using stone knives and bearskins, but you still want to make something neat? It’s time to revisit BEAM robots.

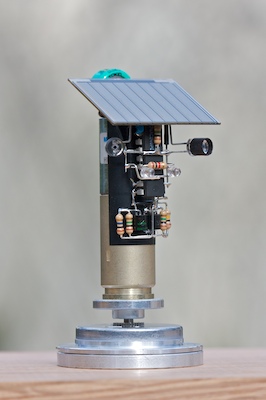
Biology, electronics, aesthetics, and mechanics — Mark Tilden came up with the idea of minimalist electronic creatures that, through inter-coupled weak control systems and clever mechanical setups, could mimic living bugs. And that’s not so crazy if you think about how many nerves something like a cockroach or an earthworm have. Yet their collection of sensors, motors, and skeletons makes for some pretty interesting behavior.

My favorite BEAM bots have always been the solar-powered ones. They move slowly or infrequently, but also inexorably, under solar power. In that way, they’re the most “alive”. Part of the design trick is to make sure they stay near their food (the sun) and don’t get stuck. One of my favorite styles is the “photovore” or “photopopper”, because they provide amazing bang for the buck.

Back in the heyday of BEAM, maybe 15 years ago, solar cells were inefficient and expensive, circuits for using their small current were leaky, and small motors were tricky to come by. Nowadays, that’s all changed. Power harvesting circuits leak only nano-amps, and low-voltage MOSFETs can switch almost losslessly. Is it time to revisit the BEAM principles? I’d wager you’d put the old guard to shame, and you won’t even need any of those newfangled microcontroller thingies, which are out of stock anyway.

If you make something, show us!

Hackaday Podcast 120: Chip Shortage, VGA Glitching, Truly Owning Roku, And Omniballs

Hackaday editors Elliot Williams and Mike Szczys recount a week of awesome hacks. One you might have missed involves a Roku-based smart TV that was rooted and all secrets laid bare for the sole purpose of making an Ambilight setup work with it. We take a look at a creative blade-tracking system for a scrollsaw CNC project, and a robot arm that brings non-flat layers to 3D printing and envisions composite material printing. There’s a great template for video glitching using inexpensive VGA to CGA converter boards, cleanly squeezed into a nice enclosure. We are a bit giddy for the omniwheel robot designs [James Bruton] has been showing off. And we finish out the show with a great conversation happening this week on Hackaday: people from throughout the community share how the chip shortage is affecting their projects.

Take a look at the links below if you want to follow along, and as always, tell us what you think about this episode in the comments!

Direct download (Weighing in around 55 MB.)

Places to follow Hackaday podcasts:

Continue reading “Hackaday Podcast 120: Chip Shortage, VGA Glitching, Truly Owning Roku, And Omniballs” →

This Week In Security: M1RACLES, The Full Half-Double, And Patch Gaps

We occasionally make fun of new security vulnerabilities that have a catchy name and shiny website. We’re breaking new ground here, though, in covering a shiny website that makes fun of itself. So first off, this is a real vulnerability in Apple’s brand-new M1 chip. It’s got CVE-2021-30747, and in some very limited cases, it could be used for something malicious. The full name is M1ssing Register Access Controls Leak EL0 State, or M1RACLES. To translate that trying-too-hard-to-be-clever name to English, a CPU register is left open to read/write access from unprivileged userspace. It happens to be a two-bit register that doesn’t have a documented purpose, so it’s perfect for smuggling data between processes.
Do note that this is an undocumented register. If it turns out that it actually does something important, this vulnerability could get more serious in a hurry. Until then, thinking of it as a two-bit vulnerability seems accurate. For now, however, the most we have to worry about is that two processes can use this to pass information back and forth. This isn’t like Spectre or Rowhammer where one process is reading or writing to an unrelated process, but both of them have to be in on the game.

The discoverer, [Hector Martin], points out one example where this could actually be abused: to bypass permissions on iOS devices. It’s a clever scenario. Third party keyboards have always been just a little worrying, because they run code that can see everything you type, passwords included. The long-standing advice has been to never use such a keyboard, if it asks for network access permissions. Apple has made this advice into a platform rule — no iOS keyboards get network access. What if a device had a second malicious app installed, that did have Internet access permissions? With a covert data channel, the keyboard could shuffle keystrokes off to its sister app, and get your secrets off the device.

So how much should you care about CVE-2021-30747? Probably not much. The shiny site is really a social experiment to see how many of us would write up the vulnerability without being in on the joke. Why go to the hassle? Apparently it was all an excuse to make this video, featuring the appropriate Bad Apple!! music video.

Half-Double’ing Down on Rowhammer

A few days ago, Google announced the details of Half-Double, and the glass is definitely Half-Double full with all the silly puns that come to mind. The concept is simple: If Rowhammer works because individual rows of ram are so physically close together, does further miniaturization enable attacks against bits two rows away? The answer is a qualified yes.

Quick refresher, Rowhammer is an attack first demonstrated against DDR3 back in 2014, where rapid access to one row of memory can cause bit-flip errors in the neighboring row. Since then, there have been efforts by chip manufacturers to harden against Rowhammer, including detection techniques. At the same time, researchers have kept advancing the art through techniques like Double-Sided Rowhammer, randomizing the order of reads, and attempts to synchronize the attack with the ram’s refresh intervals. Half-Double is yet another way to overcome the protections built into modern ram chips.

We start by specifying a particular ram row as the victim (V). The row right beside it will be the near aggressor row (N), and the next row over we call the far aggressor row (F). A normal Rowhammer attack would simply alternate between reading from the near aggressor and a far-off decoy, rapidly toggling the row select line, which degrades the physical charge in neighboring bits. The Half-Double attack instead alternates between the far aggressor and a decoy row for 1000 cycles, and then reads from the near aggressor once. This process is repeated until the victim row has a bit flip, which often happens within a few dozen iterations. Because the hammering isn’t right beside the victim row, the built-in detection applies mitigations to the wrong row, allowing the attack to succeed in spite of the mitigations.

More Vulnerable Windows Servers

We talked about CVE-2021-31166 two weeks ago, a wormable flaw in Windows’ http.sys driver. [Jim DeVries] started wondering something as soon as he heard about the CVE. Was Windows Remote Management, running on port 5985, also vulnerable? Nobody seemed to know, so he took matters into hiis own hands, and confirmed that yes, WinRM is also vulnerable to this flaw. From what I can tell, this is installed and enabled by default on every modern Windows server.

And far from his optimistic assertion that surely no-one would expose that to the Internet… It’s estimated that there over 2 million IPs doing just that.

More Ransomware

On the ransomware front, there is an interesting story out of The Republic of Ireland. The health system there was hit by Conti ransomware, and the price for decryption set at the equivalent of $20 million. It came as a surprise, then, when a decryptor was freely published. There seems to be an ongoing theme in ransomware, that the larger groups are trying to manage how much attention they draw. On the other hand, this ransomware attack includes a threat to release private information, and the Conti group is still trying to extort money to prevent it. It’s an odd situation, to be sure.

Inside Baseball for Security News

I found a series of stories and tweets rather interesting, starting with the May Android updates at the beginning of the month. [Liam Tung] at ZDNet does a good job laying out the basics. First, when Google announced the May Android updates, they pointed out four vulnerabilities as possibly being actively exploited. Dan Goodin over at Ars Technica took umbrage with the imprecise language, calling the announcement “vague to the point of being meaningless”.

Shane Huntley jumped into the fray on Twitter, and hinted at the backstory behind the vague warning. There are two possibilities that really make sense here. The first is that exploits have been found for sale somewhere, like a hacker forum. It’s not always obvious if an exploit has indeed been sold to someone using it. The other possibility given is that when Google was notified about the active exploit, there was a requirement that certain details not be shared publicly. So next time you see a big organization like Google hedge their language in an obvious and seemingly unhelpful way, it’s possible that there’s some interesting situation driving that language. Time will tell.

The Patch Gap

The term has been around since at least 2005, but it seems like we’re hearing more and more about patch gap problems. The exact definition varies, depending on who is using the term, and what product they are selling. A good working definition is the time between a vulnerability being public knowledge and an update being available to fix the vulnerability.

There are more common reasons for patch gaps, like vulnerabilities getting dropped online without any coordinated disclosure. Another, more interesting cause is when an upstream problem gets fixed and publicly announced, and it takes time to get the fix pulled in. The example in question this week is Safari, and a fix in upstream WebKit. The bug in the new AudioWorklets feature is a type confusion that provides an easy way to do audio processing in a background thread. When initializing a new worker thread, the programmer can use their own constructor to build the thread object. The function that kicks off execution doesn’t actually check that it’s been given a proper object type, and the object gets cast to the right type. Code is executed as if it was correct, usually leading to a crash.

The bug was fixed upstream shortly after a Safari update was shipped. It’s thought that Apple ran with the understanding that this couldn’t be used for an actual RCE, and therefore hadn’t issued a security update to fix it. The problem there is that it is exploitable, and a PoC exploit has been available for a week. As is often the case, this vulnerability would need to be combined with at least one more exploit to overcome the security hardening and sandboxing built into modern browsers.

There’s one more quirk that makes this bug extra dangerous, though. On iOS devices, when you download a different browser, you’re essentially running Safari with a different skin pasted on top. As far as I know, there is no way to mitigate against this bug on an iOS device. Maybe be extra careful about what websites you visit for a few days, until this get fixed.

Via Ars Technica

Electric Vehicles Do Battle On Pikes Peak

When we think of electric cars, more often than not we’re drawn to the environmental benefits and the smooth quiet commuter drives they’re so ideally suited for. However, EVs can also offer screaming performance, most notably due to their instant-on torque that gives them a big boost over internal combustion vehicles.

In recent years, this has led to a variety of independent and manufacturer-supported efforts taking on some of motorsport’s classic events. Today, we’re looking at a handful of recent entries that have tackled one of the most gruelling events in motorsport – the Pikes Peak International Hillclimb. Continue reading “Electric Vehicles Do Battle On Pikes Peak” →