Books You Should Read: Exact Constraint: Machine Design Using Kinematic Principles

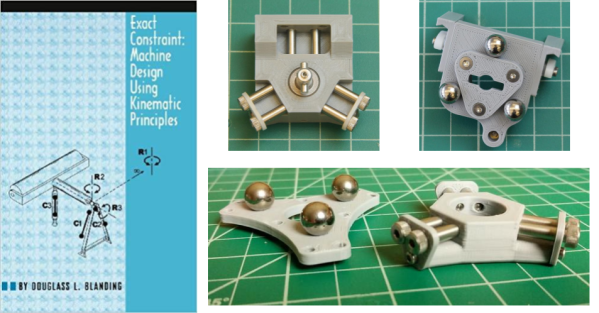
Surely, if you’re reading this website you’ve teased the thought of building your own 3D printer. I certainly did. But from my years of repeated rebuilds of my homebrew laser cutter, I learned one thing: machine design is hard, and parts cost money. Rather than jump the gun and start iterating on a few machine builds like I’ve done before, I thought I’d try to tease out the founding principles of what makes a rock-solid machine. Along the way, I discovered this book: Exact Constraint: Machine Design Using Kinematic Principles by Douglass L. Blanding.

This book is a casual but thorough introduction to the design of machines using the method of exact constraint. This methodology invites us to carefully assess how parts connect and move relative to each other. Rather than exclusively relying on precision parts, like linear guides or bearings, to limit a machine’s degrees of freedom, this book shows us a means of restricting degrees of freedom by looking at the basic kinematic connections between parts. By doing so, we can save ourselves cost by using precision rails and bearings only in the places where absolutely necessary.

While this promise might seem abstract, consider the movements made by a 3D printer. Many styles of this machine rely on motor-driven movement along three orthogonal axes: X, Y, and Z. We usually restrict individual motor movement to a single axis by constraining it using a precision part, like a linear rod or rail. However, the details of how we physically constrain the motor’s movements using these parts is a non-trivial task. Overconstrain the axis, and it will either bind or wiggle. Underconstrain it, and it may translate or twist in unwanted directions. Properly constraining a machine’s degrees of freedom is a fundamental aspect of building a solid machine. This is the core subject of the book: how to join these precision parts together in a way that leads to precision movement only in the directions that we want them.

Part of what makes this book so fantastic is that it makes no heavy expectations about prior knowledge to pick up the basics, although be prepared to draw some diagrams. Concepts are unfolded in a generous step-by-step fashion with well-diagrammed examples. As you progress, the training wheels come loose, and examples become less-heavily decorated with annotations. In this sense, the book is extremely coherent as subsequent chapters build off ideas from the previous. While this may sound daunting, don’t fret! The entire book is only about 140 pages in length.

Continue reading “Books You Should Read: Exact Constraint: Machine Design Using Kinematic Principles” →

Lambdas For C — Sort Of

A lot of programming languages these days feature lambda functions, or what I would be just as happy to call anonymous functions. Some people make a big deal out of these but the core idea is very simple. Sometimes you need a little snippet of code that you only need in one place — most commonly, as a callback function to pass another function — so why bother giving it a name? Depending on the language, there can be more to it that, especially if you get into closures and currying.

For example, in Python, the map function takes a function as an argument. Suppose you have a list and you want to capitalize each word in the list. A Python string has a capitalize method and you could write a loop to apply it to each element in the list. However, map and a lambda can do it more concisely:

map(lambda x: x.capitalize(), ['madam','im','adam'])

The anonymous function here takes an argument x and calls the capitalize method on it. The map call ensures that the anonymous function is called once for each item.

Modern C++ has lambda expressions. However, in C you have to define a function by name and pass a pointer — not a huge problem, but it can get messy if you have a lot of callback functions that you use only one time. It’s just hard to think up that many disposable function names. However, if you use gcc, there are some nonstandard C features you can use to get most of what you want out of lambda expressions.

Continue reading “Lambdas For C — Sort Of” →

Why Ada Is The Language You Want To Be Programming Your Systems With

The Ada programming language was born in the mid-1970s, when the US Department of Defense (DoD) and the UK’s Ministry Of Defence sought to replace the hundreds of specialized programming languages used for the embedded computer systems that increasingly made up essential parts of military projects.  Instead, Ada was designed to be be a single language, capable of running on all of those embedded systems, that offered the same or better level of performance and reliability.

With the 1995 revision, the language also targeted general purpose systems  and added support for object-oriented programming (OOP) while not losing sight of the core values of reliability, maintainability and efficiency. Today, software written in Ada forms the backbone of not only military hardware, but also commercial projects like avionics and air-traffic control systems. Ada code controls rockets like the Ariane 4 and 5, many satellites, and countless other systems where small glitches can have major consequences.

Ada might also be the right choice for your next embedded project. Continue reading “Why Ada Is The Language You Want To Be Programming Your Systems With” →

Sensor Filters For Coders

Anybody interested in building their own robot, sending spacecraft to the moon, or launching inter-continental ballistic missiles should have at least some basic filter options in their toolkit, otherwise the robot will likely wobble about erratically and the missile will miss it’s target.

What is a filter anyway? In practical terms, the filter should smooth out erratic sensor data with as little time lag, or ‘error lag’ as possible. In the case of the missile, it could travel nice and smoothly through the air, but miss it’s target because the positional data is getting processed ‘too late’. The simplest filter, that many of us will have already used, is to pause our code, take about 10 quick readings from our sensor and then calculate the mean by dividing by 10. Incredibly simple and effective as long as our machine or process is not time sensitive – perfect for a weather station temperature sensor, although wind direction is slightly more complicated. A wind vane is actually an example of a good sensor giving ‘noisy’ readings: not that the sensor itself is noisy, but that wind is inherently gusty and is constantly changing direction.

It’s a really good idea to try and model our data on some kind of computer running software that will print out graphs – I chose the Raspberry Pi and installed Jupyter Notebook running Python 3.

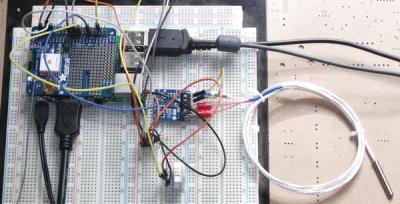
The photo on the left shows my test rig. There’s a PT100 probe with it’s MAX31865 break-out board, a Dallas DS18B20 and a DHT22. The shield on the Pi is a GPS shield which is currently not used. If you don’t want the hassle of setting up these probes there’s a Jupyter Notebook file that can also use the internal temp sensor in the Raspberry Pi. It’s incredibly quick and easy to get up and running.

It’s quite interesting to see the performance of the different sensors, but I quickly ended up completely mangling the data from the DS18B20 by artificially adding randomly generated noise and some very nasty data spikes to really punish the filters as much as possible. Getting the temperature data to change rapidly was effected by putting a small piece of frozen Bockwurst on top of the DS18B20 and then removing it again.

Continue reading “Sensor Filters For Coders” →

This Week In Security: Mass IPhone Compromise, More VPN Vulns, Telegram Leaking Data, And The Hack Of @Jack

In a very mobile-centric installment, we’re starting with the story of a long-running iPhone exploitation campaign. It’s being reported that this campaign was being run by the Chinese government. Attack attribution is decidedly non-trivial, so let’s be cautious and say that these attacks were probably Chinese operations.

In any case, Google’s Project Zero was the first to notice and disclose the malicious sites and attacks. There were five separate vulnerability chains, targeting iOS versions 10 through 12, with at least one previously unknown 0-day vulnerability in use. The Project Zero write-up is particularly detailed, and really documents the exploits.

The payload as investigated by Project Zero doesn’t permanently install any malware on the device, so if you suspect you could have been compromised, a reboot is sufficient to clear you device.

This attack is novel in how sophisticated it is, while simultaneously being almost entirely non-targeted. The malicious code would run on the device of any iOS user who visited the hosting site. The 0-day vulnerability used in this attack would have a potential value of over a million dollars, and these high value attacks have historically been more targeted against similarly high-value targets. While the websites used in the attack have not been disclosed, the sites themselves were apparently targeted at certain ethnic and religious groups inside China.

Once a device was infected, the payload would upload photos, messages, contacts, and even live GPS information to the command & control infrastructure. It also seems that Android and Windows devices were similarly targeted in the same attack.

Telegram Leaking Phone Numbers

“By default, your number is only visible to people who you’ve added to your address book as contacts.” Telegram, best known for encrypted messages, also allows for anonymous communication. Protesters in Hong Kong are using that feature to organize anonymously, through Telegram’s public group messaging. However, a data leak was recently discovered, exposing the phone numbers of members of these public groups. As you can imagine, protesters very much want to avoid being personally identified. The leak is based on a feature — Telegram wants to automatically connect you to other Telegram users whom you already know.

By default, your number is only visible to people who you’ve added to your address book as contacts.

Telegram is based on telephone numbers. When a new user creates an account, they are prompted to upload their contact list. If one of the uploaded contacts has a number already in the Telegram system, those accounts are automatically connected, causing the telephone numbers to become visible to each other. See the problem? An attacker can load a device with several thousand phone numbers, connect it to the Telegram system, and enter one of the target groups. If there is a collision between the pre-loaded contacts and the members of the group, the number is outed. With sufficient resources, this attack could even be automated, allowing for a very large information gathering campaign.

In this case, it seems such a campaign was carried out, targeting the Hong Kong protesters. One can’t help but think of the first story we covered, and wonder if the contact data from compromised devices was used to partially seed the search pool for this effort.

The Hack of @Jack

You may have seen that Twitter’s CEO, Jack [@Jack] Dorsey’s Twitter account was hacked, and a series of unsavory tweets were sent from that account. This seems to be a continuing campaign by [chucklingSquad], who have also targeted other high profile accounts. How did they manage to bypass two factor authentication and a strong password? Cloudhopper. Acquired by Twitter in 2010, Cloudhopper is the service that automatically posts a user’s SMS messages to Twitter.

Rather than a username and password, or security token, the user is secured only by their cell phone number. Enter the port-out and SIM-swap scams. These are two similar techniques that can be used to steal a phone number. The port-out scam takes advantage of the legal requirement for portable phone numbers. In the port-out scam, the attacker claims to be switching to a new carrier. A SIM-swap scam is convincing a carrier he or she is switching to a new phone and new SIM card. It’s not clear which technique was used, but I suspect a port-out scam, as Dorsey hadn’t gotten his cell number back after several days, while a SIM swap scam can be resolved much more quickly.

Google’s Bug Bounty Expanded

In more positive news, Google has announced the expansion of their bounty programs. In effect, Google is now funding bug bounties for the most popular apps on the Play store, in addition to Google’s own code. This seems like a ripe opportunity for aspiring researchers, so go pick an app with over 100 million downloads, and dive in.

An odd coincidence, that 100 million number is approximately how many downloads CamScanner had when it was pulled from the Play store for malicious behavior. This seems to have been caused by a third party advertisement library.

Updates

Last week we talked about Devcore and their VPN Appliance research work. Since then, they have released part 3 of their report. Pulse Secure doesn’t have nearly as easily exploited vulnerabilities, but the Devcore team did find a pre-authentication vulnerability that allowed reading arbitraty data off the device filesystem. As a victory lap, they compromised one of Twitter’s vulnerable devices, reported it to Twitter’s bug bounty program, and took home the highest tier reward for their trouble.

3D Printering: The Search For Better Search

There’s no question that a desktop 3D printer is at its most useful when it’s producing parts of your own design. After all, if you’ve got a machine that can produce physical objects to your exacting specifications, why not give it some? But even the most diligent CAD maven will occasionally defer to an existing design, as there’s no sense spending the time and effort creating their own model if a perfectly serviceable one is already available under an open source license.

But there’s a problem: finding these open source models is often more difficult than it should be. The fact of the matter is, the ecosystem for sharing 3D printable models is in a very sorry state. Thingiverse, the community’s de facto model repository, is antiquated and plagued with technical issues. Competitors such as Pinshape and YouMagine are certainly improvements on a technical level, but without the sheer number of models and designers that Thingiverse has, they’ve been unable to earn much mindshare. When people are looking to download 3D models, it stands to reason that the site with the most models will be the most popular.

It’s a situation that the community is going to have to address eventually. As it stands, it’s something of a minor miracle that Thingiverse still exists. Owned and operated by Makerbot, the company that once defined the desktop 3D printer but is today all but completely unknown in a market dominated by low-cost printers from the likes of Monoprice and Creality, it seems only a matter of time before the site finally goes dark. They say it’s unwise to put all of your eggs in one basket, and doubly so if the basket happens to be on fire.

So what will it take to get people to consider alternatives to Thingiverse before it’s too late? Obviously, snazzy modern web design isn’t enough to do it. Not if the underlying service operates on the same formula. To really make a dent in this space, you need a killer feature. Something that measurably improves the user experience of finding the 3D model you need in a sea of hundreds of thousands. You need to solve the search problem.

Continue reading “3D Printering: The Search For Better Search” →

Hackaday Celebrates 15 Years And Oh How The Hardware Has Changed

Today marks exactly 15 years since Hackaday began featuring one Hack a Day, and we’ve haven’t missed a day since. Over 5,477 days we’ve published 34,057 articles, and the Hackaday community has logged 903,114 comments. It’s an amazing body of work from our writers and editors, a humbling level of involvement from our readers, and an absolutely incredible contribution to open hardware by the project creators who have shared details of their work and given us all something to talk about and to strive for.

What began as a blog is now a global virtual hackerspace. That first 105-word article has grown far beyond project features to include spectacular long-form original content. From our community of readers has grown Hackaday.io, launched in 2014 you’ll now find over 30,000 projects published by 350,000 members. The same year the Hackaday Prize was founded as a global engineering initiative seeking to promote open hardware, offering big prizes for big ideas (and the willingness to share them). Our virtual connections were also given the chance to come alive through the Hackaday Superconference, Hackaday Belgrade, numerous Hackaday Unconferences, and meetups all over the world.

All of this melts together into a huge support structure for anyone who wants to float an interesting idea with a proof of concept where “why” is the wrong question. Together we challenge the limits of what things are meant to do, and collectively we filter through the best ideas and hold them high as building blocks for the next iteration. The Hackaday community is the common link in the collective brain, a validation point for perpetuating great ideas of old, and cataloging the ones of new.

Perhaps the most impressive thing about the last 15 years of Hackaday is how much the technological landscape has changed. Hackaday is still around because all of us have actively changed along with it — always looking for that cutting edge where the clever misuse of something becomes the base for the next transformative change. So we thought we’d take a look back 15 years in tech. Let’s dig into a time when there were no modules for electronics, you couldn’t just whip up a plastic part in an afternoon, designing your own silicon was unheard of, and your parts distributor was the horde of broken electronics in your back room.

Continue reading “Hackaday Celebrates 15 Years And Oh How The Hardware Has Changed” →