This Week In Security: Annoyed Researchers, Dangling DNS, And Hacks That Could Have Been Worse

The author of the BlueHammer exploit, which was released earlier this month and addressed in the last Patch Tuesday, continues to be annoyed with the responses from the Microsoft security research and vulnerability response team, and has released another Windows zero-day attack against Windows Defender.

The RedSun exploit targets a logic and timing error in Windows Defender, convincing it to install the target file in the system, instead of quarantining the file and protecting the system. Not, generally, what you would hope would happen.

Since the RedSun attack requires local access in the first place, it seems unlikely Microsoft will release an out-of-sequence patch for it, however with public code available, we can probably expect to see malware leveraging it to establish higher permissions on an infected system.

Releasing exploits out of spite feels like a return to the late 1990s, and I almost don’t hate it.

University Domains Hijacked

Reported in Bleeping Computer, a group tracked as “Hazy Hawk” has been hijacking unmaintained DNS records of universities and government institutions to serve ad click spam.

The attack seems simple and doesn’t even require compromising the actual institution, using dangling DNS “CNAME” records. A “CNAME” entry in DNS acts essentially as an alias, pointing one domain name at another, which can be used to provide content from an official domain that is hosted on a cloud service where the IP address of the service might change.

A DNS “A” (or “AAAA” if you speak IPv6) record points a hostname – like “foo.example.com” – to an IP address – like “1.1.1.1”. A “CNAME” record points a hostname to another hostname, like “foo.some_cloud_host.com”. Scanning “high value” domains (like Ivy League universities) for “CNAME” records which point to expired domains (or domains on cloud hosted providers which no longer exist) lets anyone able to register that domain (or create an account with the proper naming scheme on the cloud host) to post any content they wish, and still appear to be the original name.

At least 30 educational institutions have been impacted, along with several government agencies including the CDC.
Continue reading “This Week In Security: Annoyed Researchers, Dangling DNS, And Hacks That Could Have Been Worse” →

This Week In Security: Docker Auth, Windows Tools, And A Very Full Patch Tuesday

CVE-2026-34040 lets attackers bypass some Docker authentication plugins by allowing an empty request body. Present since 2024, this bug was caused by a previous fix to the auth workflow. In the 2024 bug, the authentication system could be tricked into passing a zero-length request to the authentication handler. In the modern vulnerability, the system can be tricked into removing a too-large authentication request and passing a zero-length request to the authentication handler.

In both cases, the authentication system may not properly handle the malformed request and allow creation of docker images with access to stored credentials and secrets.

Bugs like these are increasing in visibility because AI agents running in Docker, like OpenClaw, may be tricked via prompt injection into leveraging the vulnerability.

Windows CPU Tools Compromised

videocardz.com notes that the popular Windows monitoring software Cpu-Z and HWMonitor appear to have been compromised. Reports indicate that the download site was compromised, not the actual packages, but that it was redirecting update requests to packages including malware. While the site has been repaired, unfortunately it looks like there is no warning to users that the downloads were compromised for a period of time.

Anecdotally, there has been a rash of Discord account takeovers in the past week, where long-standing accounts in multiple servers have been compromised and turned into spambots. While there is no evidence these events are linked, clearly a new credential or authentication stealing malware is in play, which involves stealing credentials from Discord.

X.Org and XWayland Updated

The X.Org and XWayland servers saw security updates this week, fixing a handful of vulnerabilities involving uninitialized memory use, use-after-free, and reading beyond the end of a buffer.

The vulnerabilities are generally classified as “moderate”, but of course, don’t leave known vulnerabilities when you can avoid it! Fixed releases should find their way into distributions soon.

Continue reading “This Week In Security: Docker Auth, Windows Tools, And A Very Full Patch Tuesday” →

This Week In Security: Flatpak Fixes, Android Malware, And SCADA Was IOT Before IOT Was Cool

Rowhammer attacks have been around since 2014, and mitigations are in place in most modern systems, but the team at gddr6.fail has found ways to apply the attack to current-generation GPUs.

Rowhammer attacks attach the electrical characteristics of RAM, using manipulation of the contents of RAM to cause changes in the contents of adjacent memory cells. Bit values are just voltage levels, after all, and if a little charge leaks across from one row to the next, you can potentially pull a bit high by writing repeatedly to its physical neighbors.

The attack was used to allow privilege escalation by manipulating the RAM defining the user data, and later, to allow reading and manipulation of any page in ram by modifying the system page table that maps memory and memory permissions. By 2015 researchers refined the attack to run in pure JavaScript against browsers, and in 2016 mobile devices were shown to be vulnerable. Mitigations have been put in place in physical memory design, CPU design, and in software. However, new attack vectors are still discovered regularly, with DDR4 and DDR5 RAM as well as AMD and RISC-V CPUs being vulnerable.

The GDDR6-Fail attack targets the video ram of modern graphics cards, and is able to trigger similar vulnerabilities in the graphics card itself, culminating in accessing and changing the memory of the PC via the PCI bus and bypassing protections.

For users who fear they are at risk — most likely larger AI customers or shared hosting environments where the code running on the GPU may belong to untrusted users — enabling error correcting (ECC) mode in the GPU reduces the amount of available RAM, but adds protection by performing checksums on the memory to detect corruption or bit flipping. For the average home user, your mileage may vary – there’s certainly easier ways to execute arbitrary code on your PC – like whatever application is running graphics in the first place!

Continue reading “This Week In Security: Flatpak Fixes, Android Malware, And SCADA Was IOT Before IOT Was Cool” →

This Week In Security: The Supply Chain Has Problems

The biggest story of the week is a new massive supply chain breach, which appears to be unrelated to the previous massive supply chain breaches, this time of the Axios HTTP project.

Axios was created as a more developer-friendly Javascript HTTP interface for node.js, giving a promise-based API instead of the basic callback API. (Promise-based programming allows for simpler coding workflows, where a program can wait for a promise to be fulfilled, instead of the developer having to manage the state of every request manually.) Javascript has since provided a modern Fetch API that provides similar functionality, but Axios remains one of the most popular packages on the node.js NPM repository, with 100 million weekly downloads.

The lead developer of Axios believes he was compromised by a collaboration request – a common tactic for phishing specific targets: a project for an IDE like VS Code can include code that executes on the developers system when the project is run. Even outside a traditional IDE, common development tools like configure scripts and makefiles can easily run commands.

Socket.dev breaks down the attack in detail. Once the attackers had credentials to publish to the Axios NPM, they inserted malware as a new dependency to Axios, instead of modifying Axios itself. This likely helped the attack bypass other security checkers. The dependency – plain-crypto-js – is itself simply a copy of a popular encryption utility library, but one which executes additional code during the post-installation process available to all NPM packages. Continue reading “This Week In Security: The Supply Chain Has Problems” →

Secure Communication, Buried In A News App

Cryptography is a funny thing. Supposedly, if you do the right kind of maths to a message, you can send it off to somebody else, and as long as they’re the only one that knows a secret little thing, nobody else will be able to read it. We have all sorts of apps for this, too, that are specifically built for privately messaging other people.

Only… sometimes just having such an app is enough to get you in trouble. Even just the garbled message itself could be proof against you, even if your adversary can’t read it. Enter The Guardian. The UK-based media outlet has deployed a rather creative and secure way of accepting private tips and information, one which seeks to provide heavy cover for those writing in with the hottest scoops.

Continue reading “Secure Communication, Buried In A News App” →

Simple Device Can Freeze Wi-Fi Camera Feeds

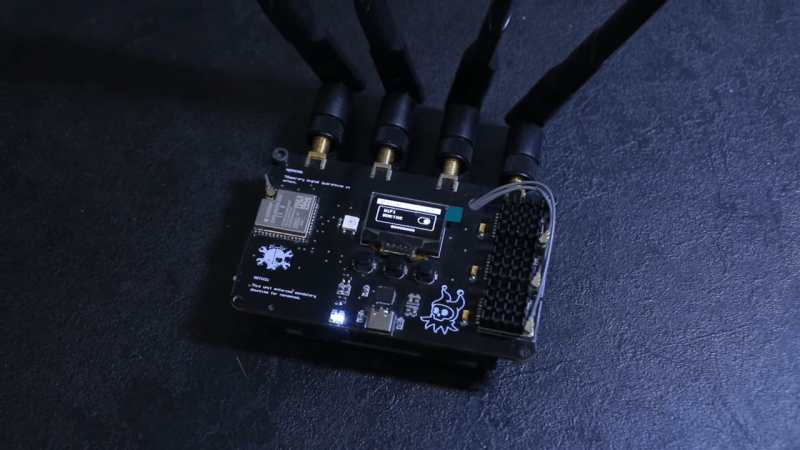
Wi-Fi cameras are everywhere these days, with wireless networking making surveillance systems easier to deploy than ever. [CiferTech] has been recently developing the RF Clown—a tool that can block transmissions from these cameras at some range.

The build is based around an ESP32, with three tactile switches and an OLED display for the user interface. The microcontroller is hooked up to a trio of GT—24 Mini radio modules, which feed a bank of antennas on top of the device. Depending on the mode the device is set to, it will command these modules to jam Bluetooth, BLE, or Wi-Fi traffic in the area with relatively crude transmissions.

The use of multiple radio modules isn’t particularly sophisticated—it just makes it easier to put out more signal on more bands at the same time, flooding the zone and making it less likely legitimate transmissions will get through. Specifically, [CiferTech] demonstrates the use case of taking out a Wi-Fi camera—with the device switched on, the video feed freezes because packets from the camera simply stop making it through.

It’s perhaps impolite to interfere with the operation of somebody else’s cameras, so keep that in mind before you pursue a project like this one. Files are on GitHub for the curious. Video after the break.

Continue reading “Simple Device Can Freeze Wi-Fi Camera Feeds” →

Attack Turns Mouse Into Microphone

As computer hardware gets better and better, most of the benefits are readily apparent to users. Faster processors, less power consumption, and lower cost are the general themes here. But sometimes increased performance comes with some unusual downsides. A research group at the University of California, Irvine found that high-performance mice have such good resolution that they can be used to spy on a user’s speech or other sounds around them.

The mice involved in this theoretical attack need to be in the neighborhood of 20,000 dpi, as well as having a relatively high sampling rate. With this combination it’s possible to sense detail fine enough to resolve speech from the vibrations of the mouse pad. Not only that, but the researchers noted that this also enables motion tracking of people in the immediate vicinity as the vibrations caused by walking can also be decoded. The attack does require a piece of malware to be installed somewhere on the computer, but the group also theorize that this could easily be done since most security suites don’t think of mouse input data as particularly valuable or vulnerable.

Even with the data from the mouse, an attacker needs a sophisticated software suite to be able to decode and filter the data to extract sounds, and the research team could only extract around 60% of the audio under the best conditions. The full paper is available here as well. That being said, mice will only get better from here so this is certainly something to keep an eye on. Mice aren’t the only peripherials that have roundabout attacks like this, either.

Thanks to [Stephen] for the tip!

Continue reading “Attack Turns Mouse Into Microphone” →