Hackaday Podcast 118: Apple AirTag Hacked, Infill Without Perimeters, Hair-Pulling Robots, And Unpacking The 555

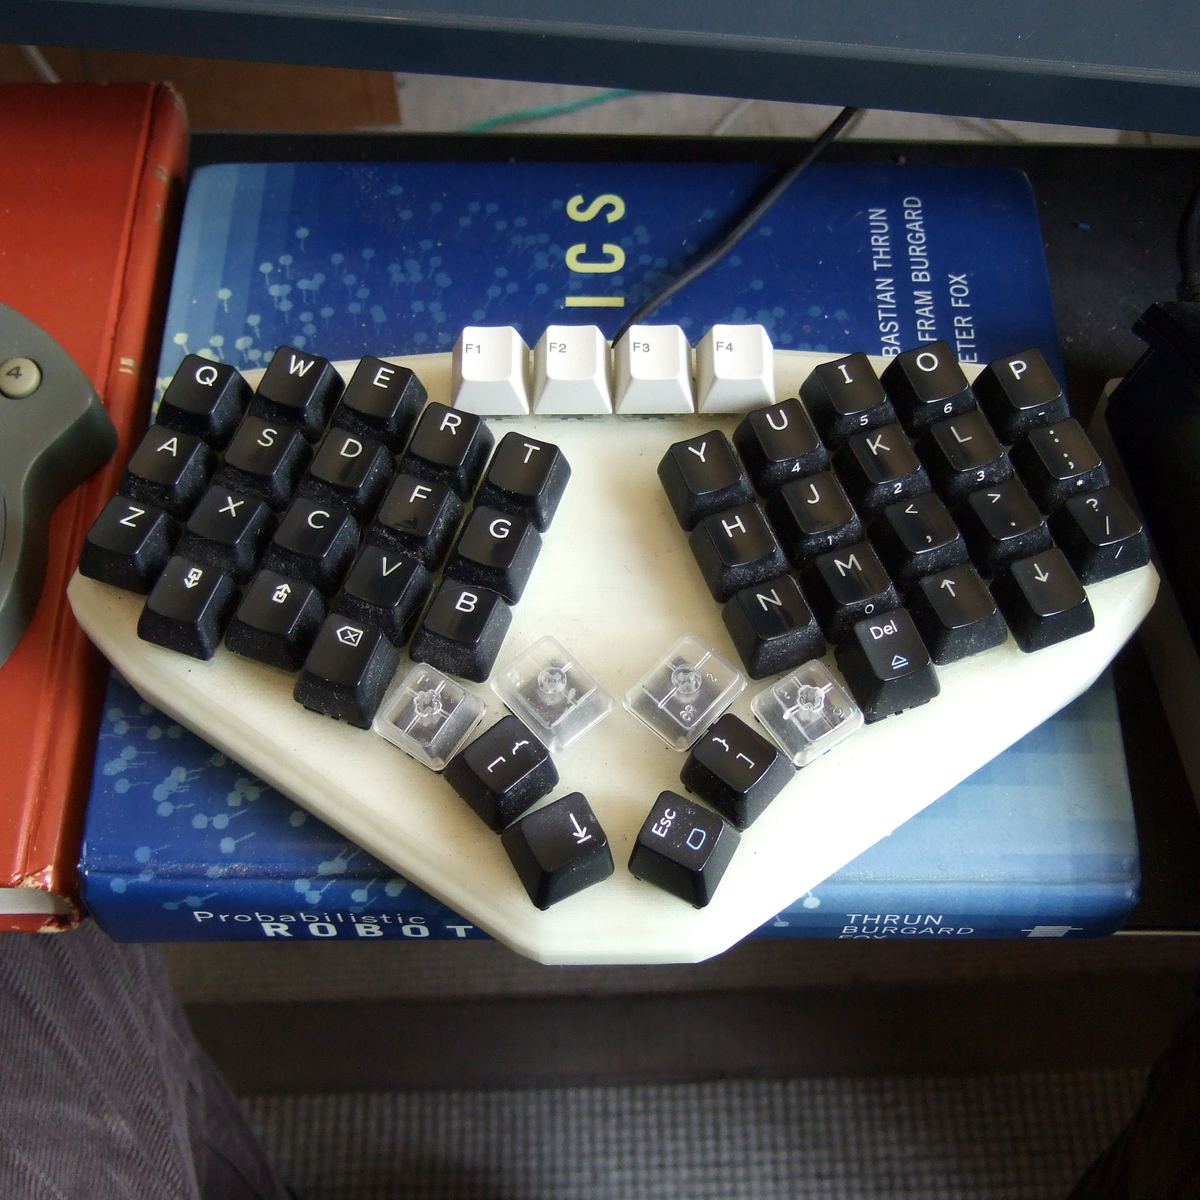
Elliot’s keeb: ortho, offset, thumby.

Hackaday editors Elliot Williams and Mike Szczys gather to ooh and aah over a week of interesting hacks. This week we’re delighted to welcome special guest Kristina Panos to talk about the Inputs of Interest series she has been working on over the last couple of years. In the news is the effort to pwn the new Apple AirTags, with much success over the past week. We look at turning a screenless Wacom tablet into something more using a donor iPad, stare right into the heart of a dozen 555 die shots, and watch what happens when you only 3D print the infill and leave the perimeters out.


Take a look at the links below if you want to follow along, and as always, tell us what you think about this episode in the comments!

Direct download (~55 MB)

Places to follow Hackaday podcasts:

Continue reading “Hackaday Podcast 118: Apple AirTag Hacked, Infill Without Perimeters, Hair-Pulling Robots, And Unpacking The 555” →

This Week In Security: Fragattacks, The Pipeline, Codecov, And IPv6

Some weeks are slow, and the picking are slim when discussing the latest security news. This was not one of those weeks.

First up is Fragattacks, a set of flaws in wireless security protocols, allowing unauthenticated devices to inject packets into the network, and in some cases, read data back out. The flaws revolve around 802.11’s support for packet aggregation and frame fragmentation. The whitepaper is out, so let’s take a look.

Fragmentation and aggregation are techniques for optimizing wireless connections. Packet aggregation is the inclusion of multiple IP packets in a single wireless frame. When a device is sending many small packets, it’s more efficient to send them all at once, in a single wireless frame. On the other hand, if the wireless signal-to-noise ratio is less than ideal, shorter frames are more likely to arrive intact. To better operate in such an environment, long frames can be split into fragments, and recombined upon receipt.
There are a trio of vulnerabilities that are built-in to the wireless protocols themselves. First up is CVE-2020-24588, the aggregation attack. To put this simply, the aggregation section of a wireless frame header is unauthenticated and unencrypted. How to exploit this weakness isn’t immediately obvious, but the authors have done something clever.

First, for the purposes of explanation, we will assume that there is already a TCP connection established between the victim and an attacker controlled server. This could be as simple as an advertisement being displayed on a visited web page, or an image linked to in an email. We will also assume that the attacker is performing a Man in the Middle attack on the target’s wireless connection. Without the password, this only allows the attacker to pass the wireless frames back and forth unmodified, except for the aggregation header data, as mentioned. The actual attack is to send a special IP packet in the established TCP connection, and then modify the header data on the wireless frame that contains that packet.

When the victim tries to unpack what it believes to be an aggregated frame, the TCP payload is interpreted as a discrete packet, which can be addressed to any IP and port the attacker chooses. To put it more simply, it’s a packet within a packet, and the frame aggregation header is abused to pop the internal packet out onto the protected network. Continue reading “This Week In Security: Fragattacks, The Pipeline, Codecov, And IPv6” →

Toyota’s Hydrogen-Burning Racecar Soon To Hit The Track

With the rise of usable electric cars in the marketplace, and markets around the world slowly phasing out the sale of fossil fuel cars, you could be forgiven for thinking that the age of the internal combustion engine is coming to an end. History is rarely so cut and dry, however, and new technologies aim to keep the combustion engine alive for some time yet.

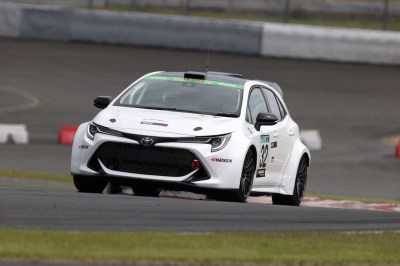
Toyota’s upcoming Corolla Sport-based hydrogen-burning racer. Credit: Toyota media

One of the most interesting technologies in this area are hydrogen-burning combustion engines. In contrast to fuel cell technologies, which combine hydrogen with oxygen through special membranes in order to create electricity, these engines do it the old fashioned way – in flames. Toyota has recently been exploring the technology, and has announced a racecar sporting a three-cylinder hydrogen-burning engine will compete in this year’s Fuji Super TEC 24 Hour race.

Hydrogen Engines?

The benefit of a hydrogen-burning engine is that unlike burning fossil fuels, the emissions from burning hydrogen are remarkably clean. Burning hydrogen in pure oxygen produces only water as a byproduct. When burned in atmospheric air, the result is much the same, albeit with small amounts of nitrogen oxides produced. Thus, there’s great incentive to explore the substitution of existing transportation fuels with hydrogen. It’s a potential way to reduce pollution output while avoiding the hassles of long recharge times with battery electric technologies. Continue reading “Toyota’s Hydrogen-Burning Racecar Soon To Hit The Track” →

Simple Encryption You Can Do On Paper

It’s a concern for Europeans as it is for people elsewhere in the world: there have been suggestions among governments to either outlaw, curtail, or backdoor strong end-to-end encryption. There are many arguments against ruining encryption, but the strongest among them is that encryption can be simple enough to implement that a high-school student can understand its operation, and almost any coder can write something that does it in some form, so to ban it will have no effect on restricting its use among anyone who wants it badly enough to put in the effort to roll their own.

With that in mind, we’re going to have a look at the most basic ciphers, the kind you could put together yourself on paper if you need to.

Continue reading “Simple Encryption You Can Do On Paper” →

The Mysterious Wobble Of Muons

You might think that particle physicists would be sad when an experiment comes up with different results than their theory would predict, but nothing brightens up a field like unexplained phenomena.  Indeed, particle physicists have been feverishly looking for deviations from the Standard Model. This year, there have been tantalizing signs that a long unresolved discrepancy between theory and experiment will be confirmed by new experimental results.

In particular, the quest to measure the magnetic moment of muons started more than 60 years ago, and this has been measured ever more precisely since. From an experiment in 1959 at CERN in Switzerland, to the turn of the century at Brookhaven, to this year’s result at Fermilab, the magnetic moment of the muon seems to be at odds with theoretical predictions.

Although a statistical fluke is basically excluded, this value also relies on complex theoretical calculations that are not all in agreement. Instead of heralding a new era of physics, it might just be another headline too good to be true. But some physicists are mumbling “new particle” in hushed tones. Let’s see what all the fuss is about.

Continue reading “The Mysterious Wobble Of Muons” →

Embedded Rust Hack Chat

Join us on Wednesday, May 12 at noon Pacific for the Embedded Rust Hack Chat with James Munns!

Programming languages, like fashion, are very much a matter of personal taste. Professional developers often don’t have much say in which language they’ll use for a given project, either for legacy or team reasons, but if they did have a choice, they’d probably choose the language that works best with the way they think. Some languages just “fit” different brains better than others, and when everything is in sync between language and developer, code just seems to flow effortlessly through the keyboard and onto the screen.

One language that consistently scores at the top of developers’ “most loved” lists is Rust. For a language that started as a personal project and has only existed for a little more than a decade, that’s really saying something. The emphasis Rust puts on safety and performance probably has a lot to do with that. And thanks to its safe concurrency, its memory safety, and its interoperability with C and other languages, Rust has made considerable in-roads with the embedded development community.

To learn more about Rust in embedded systems, James Munns will stop by the Hack Chat. James is an embedded systems engineer, with a history of working on software for a wide range of systems, including safety-critical avionics, and rapidly prototyped IoT systems. He’s a founding member of the Rust Embedded Working Group, as well as a founder of Ferrous Systems, a consultancy focused on systems development in Rust, with a specialty in embedded systems development. James also used to write for Hackaday, so he must be a pretty cool guy. So swing by the Hack Chat and find out where Rust might be able to help you out with your next embedded project.

join-hack-chatOur Hack Chats are live community events in the Hackaday.io Hack Chat group messaging. This week we’ll be sitting down on Wednesday, May 12 at 12:00 PM Pacific time. If time zones have you tied up, we have a handy time zone converter.

Click that speech bubble to the right, and you’ll be taken directly to the Hack Chat group on Hackaday.io. You don’t have to wait until Wednesday; join whenever you want and you can see what the community is talking about.
Continue reading “Embedded Rust Hack Chat” →

South Australia Vs. Too Much Home Solar

Once upon a time, the consensus was that renewable energy was too expensive and in too sparse supply to be a viable power source to run our proud, electrified societies on. Since then, prices of solar panels have tanked, becoming more efficient along the way, and homeowners have been installing them on their rooftops in droves.

Where once it was thought we’d never have enough solar energy, in some cities, it’s becoming all too much. In South Australia, where solar output can be huge on a sunny day, electricity authorities are facing problems with grid stability, and are taking measures to limit solar output to the grid.

Isn’t More Usually Better?

The problem faced by South Australian utilities is one of how to properly control an electrical grid with many thousands of distributed power sources. Typically, in conventional modern power grids, voltage and frequency is controlled within set limits by carefully matching the supply from major power plants with the demand from users. Fast-response plants can be brought online to meet shortfalls, and switched off when demand drops, and everything hums along nicely.

Unfortunately, solar power isn’t so easy to throttle, and even less so when it’s coming from thousands of separate households each with their own rooftop install and an inverter to feed back into the grid. This has led to authorities contemplating measures such as charging homeowners to export energy to the grid in peak periods in an effort to slow the huge uptake of home solar systems. Export limits have also been proposed for suburbs with the highest concentration of home solar, as substations in certain residential areas struggle to cope under the huge inflows of energy. Continue reading “South Australia Vs. Too Much Home Solar” →