This Week In Security: Mass IPhone Compromise, More VPN Vulns, Telegram Leaking Data, And The Hack Of @Jack

In a very mobile-centric installment, we’re starting with the story of a long-running iPhone exploitation campaign. It’s being reported that this campaign was being run by the Chinese government. Attack attribution is decidedly non-trivial, so let’s be cautious and say that these attacks were probably Chinese operations.

In any case, Google’s Project Zero was the first to notice and disclose the malicious sites and attacks. There were five separate vulnerability chains, targeting iOS versions 10 through 12, with at least one previously unknown 0-day vulnerability in use. The Project Zero write-up is particularly detailed, and really documents the exploits.

The payload as investigated by Project Zero doesn’t permanently install any malware on the device, so if you suspect you could have been compromised, a reboot is sufficient to clear you device.

This attack is novel in how sophisticated it is, while simultaneously being almost entirely non-targeted. The malicious code would run on the device of any iOS user who visited the hosting site. The 0-day vulnerability used in this attack would have a potential value of over a million dollars, and these high value attacks have historically been more targeted against similarly high-value targets. While the websites used in the attack have not been disclosed, the sites themselves were apparently targeted at certain ethnic and religious groups inside China.

Once a device was infected, the payload would upload photos, messages, contacts, and even live GPS information to the command & control infrastructure. It also seems that Android and Windows devices were similarly targeted in the same attack.

Telegram Leaking Phone Numbers

“By default, your number is only visible to people who you’ve added to your address book as contacts.” Telegram, best known for encrypted messages, also allows for anonymous communication. Protesters in Hong Kong are using that feature to organize anonymously, through Telegram’s public group messaging. However, a data leak was recently discovered, exposing the phone numbers of members of these public groups. As you can imagine, protesters very much want to avoid being personally identified. The leak is based on a feature — Telegram wants to automatically connect you to other Telegram users whom you already know.

By default, your number is only visible to people who you’ve added to your address book as contacts.

Telegram is based on telephone numbers. When a new user creates an account, they are prompted to upload their contact list. If one of the uploaded contacts has a number already in the Telegram system, those accounts are automatically connected, causing the telephone numbers to become visible to each other. See the problem? An attacker can load a device with several thousand phone numbers, connect it to the Telegram system, and enter one of the target groups. If there is a collision between the pre-loaded contacts and the members of the group, the number is outed. With sufficient resources, this attack could even be automated, allowing for a very large information gathering campaign.

In this case, it seems such a campaign was carried out, targeting the Hong Kong protesters. One can’t help but think of the first story we covered, and wonder if the contact data from compromised devices was used to partially seed the search pool for this effort.

The Hack of @Jack

You may have seen that Twitter’s CEO, Jack [@Jack] Dorsey’s Twitter account was hacked, and a series of unsavory tweets were sent from that account. This seems to be a continuing campaign by [chucklingSquad], who have also targeted other high profile accounts. How did they manage to bypass two factor authentication and a strong password? Cloudhopper. Acquired by Twitter in 2010, Cloudhopper is the service that automatically posts a user’s SMS messages to Twitter.

Rather than a username and password, or security token, the user is secured only by their cell phone number. Enter the port-out and SIM-swap scams. These are two similar techniques that can be used to steal a phone number. The port-out scam takes advantage of the legal requirement for portable phone numbers. In the port-out scam, the attacker claims to be switching to a new carrier. A SIM-swap scam is convincing a carrier he or she is switching to a new phone and new SIM card. It’s not clear which technique was used, but I suspect a port-out scam, as Dorsey hadn’t gotten his cell number back after several days, while a SIM swap scam can be resolved much more quickly.

Google’s Bug Bounty Expanded

In more positive news, Google has announced the expansion of their bounty programs. In effect, Google is now funding bug bounties for the most popular apps on the Play store, in addition to Google’s own code. This seems like a ripe opportunity for aspiring researchers, so go pick an app with over 100 million downloads, and dive in.

An odd coincidence, that 100 million number is approximately how many downloads CamScanner had when it was pulled from the Play store for malicious behavior. This seems to have been caused by a third party advertisement library.

Updates

Last week we talked about Devcore and their VPN Appliance research work. Since then, they have released part 3 of their report. Pulse Secure doesn’t have nearly as easily exploited vulnerabilities, but the Devcore team did find a pre-authentication vulnerability that allowed reading arbitraty data off the device filesystem. As a victory lap, they compromised one of Twitter’s vulnerable devices, reported it to Twitter’s bug bounty program, and took home the highest tier reward for their trouble.
3D Printering: The Search For Better Search

There’s no question that a desktop 3D printer is at its most useful when it’s producing parts of your own design. After all, if you’ve got a machine that can produce physical objects to your exacting specifications, why not give it some? But even the most diligent CAD maven will occasionally defer to an existing design, as there’s no sense spending the time and effort creating their own model if a perfectly serviceable one is already available under an open source license.

But there’s a problem: finding these open source models is often more difficult than it should be. The fact of the matter is, the ecosystem for sharing 3D printable models is in a very sorry state. Thingiverse, the community’s de facto model repository, is antiquated and plagued with technical issues. Competitors such as Pinshape and YouMagine are certainly improvements on a technical level, but without the sheer number of models and designers that Thingiverse has, they’ve been unable to earn much mindshare. When people are looking to download 3D models, it stands to reason that the site with the most models will be the most popular.

It’s a situation that the community is going to have to address eventually. As it stands, it’s something of a minor miracle that Thingiverse still exists. Owned and operated by Makerbot, the company that once defined the desktop 3D printer but is today all but completely unknown in a market dominated by low-cost printers from the likes of Monoprice and Creality, it seems only a matter of time before the site finally goes dark. They say it’s unwise to put all of your eggs in one basket, and doubly so if the basket happens to be on fire.

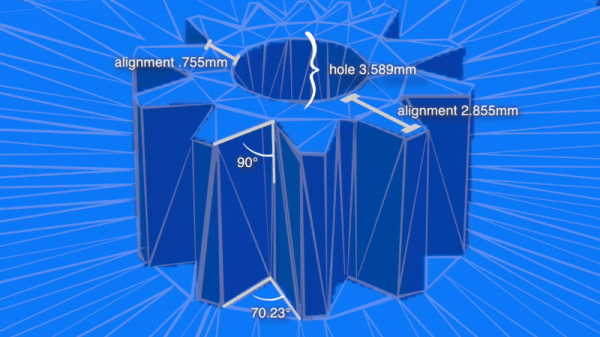
So what will it take to get people to consider alternatives to Thingiverse before it’s too late? Obviously, snazzy modern web design isn’t enough to do it. Not if the underlying service operates on the same formula. To really make a dent in this space, you need a killer feature. Something that measurably improves the user experience of finding the 3D model you need in a sea of hundreds of thousands. You need to solve the search problem.

Continue reading “3D Printering: The Search For Better Search” →

Hackaday Celebrates 15 Years And Oh How The Hardware Has Changed

Today marks exactly 15 years since Hackaday began featuring one Hack a Day, and we’ve haven’t missed a day since. Over 5,477 days we’ve published 34,057 articles, and the Hackaday community has logged 903,114 comments. It’s an amazing body of work from our writers and editors, a humbling level of involvement from our readers, and an absolutely incredible contribution to open hardware by the project creators who have shared details of their work and given us all something to talk about and to strive for.

What began as a blog is now a global virtual hackerspace. That first 105-word article has grown far beyond project features to include spectacular long-form original content. From our community of readers has grown Hackaday.io, launched in 2014 you’ll now find over 30,000 projects published by 350,000 members. The same year the Hackaday Prize was founded as a global engineering initiative seeking to promote open hardware, offering big prizes for big ideas (and the willingness to share them). Our virtual connections were also given the chance to come alive through the Hackaday Superconference, Hackaday Belgrade, numerous Hackaday Unconferences, and meetups all over the world.

All of this melts together into a huge support structure for anyone who wants to float an interesting idea with a proof of concept where “why” is the wrong question. Together we challenge the limits of what things are meant to do, and collectively we filter through the best ideas and hold them high as building blocks for the next iteration. The Hackaday community is the common link in the collective brain, a validation point for perpetuating great ideas of old, and cataloging the ones of new.

Perhaps the most impressive thing about the last 15 years of Hackaday is how much the technological landscape has changed. Hackaday is still around because all of us have actively changed along with it — always looking for that cutting edge where the clever misuse of something becomes the base for the next transformative change. So we thought we’d take a look back 15 years in tech. Let’s dig into a time when there were no modules for electronics, you couldn’t just whip up a plastic part in an afternoon, designing your own silicon was unheard of, and your parts distributor was the horde of broken electronics in your back room.

Continue reading “Hackaday Celebrates 15 Years And Oh How The Hardware Has Changed” →

Dian Fossey, Gorilla Girl

Few people sacrifice themselves as completely as Dian Fossey did for the mountain gorillas of Africa. She fought tirelessly to protect them from poachers, cattle herders, zoo kidnappers, corrupt governments, and tourists. Dian left a comfortable life behind to make the misty slopes of an extinct volcano her home and headquarters. There, she patiently sought out the gorillas, mimicking their facial expressions and actions until they grew curious about her. Eventually, she had their complete trust and friendship, and considered them her family.

Dian spent eighteen years on and off living among the gorillas. She continually risked her health, life, and reputation to raise awareness of their plight and save them from extinction. While the mountain gorilla remains an endangered species, Dian’s research and conservation efforts have greatly contributed to their increased population in the years since her death.

Continue reading “Dian Fossey, Gorilla Girl” →

3D Printing May Be The Key To Practical Scramjets

The first scramjet, an airbreathing jet engine capable of pushing an aircraft beyond Mach 5, was successfully flown in the early 1990s. But while pretty much any other technology you could imagine has progressed by leaps and bounds in the nearly 30 years that have passed, the state-of-the-art in hypersonic scramjets hasn’t moved much. We still don’t have practical hypersonic aircraft, military or otherwise, and any missiles that travel at those sort of speeds are rocket powered.

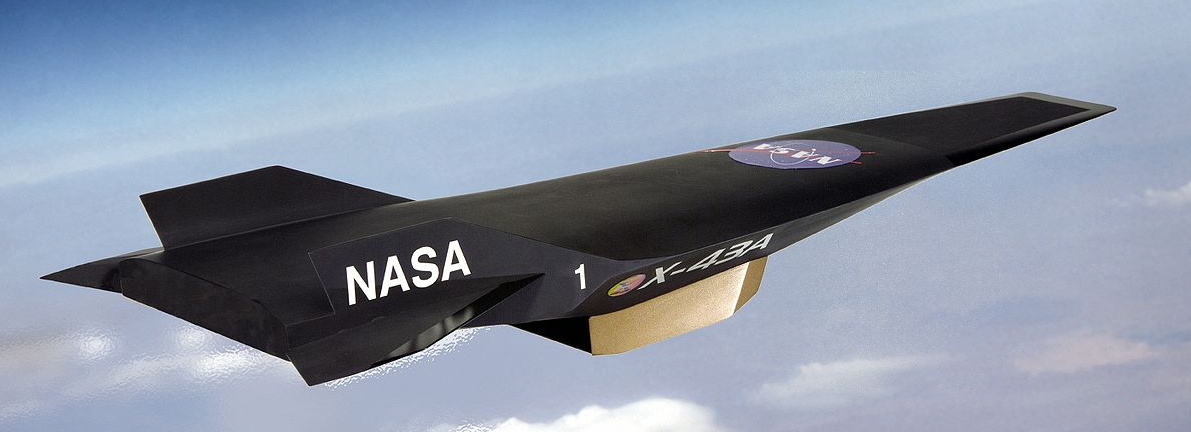
NASA’s X-43 hit Mach 9.6 in 2004

This is somewhat surprising since, at least on paper, the operating principle of the scramjet is simplicity itself. Air rushing into the engine is compressed by the geometry of the inlet, fuel is added, the mixture is ignited, and the resulting flow of expanded gases leaves the engine faster than it entered. There aren’t even any moving parts inside of a scramjet, it’s little more than a carefully shaped tube with fuel injectors and ignitors in it.

Unfortunately, pulling it off in practice is quite a bit harder. Part of the problem is that a scramjet doesn’t actually start working until the air entering the engine’s inlet is moving at around Mach 4, which makes testing them difficult and expensive. It’s possible to do it in a specially designed wind tunnel, but practically speaking, it ends up being easier to mount the engine to the front of a conventional rocket and get it up to speed that way. The downside is that such flights are one-way tickets, and end with the test article crashing into the ocean once it runs out of fuel.

But the bigger problem is that the core concept is deceptively simple. It’s easy to say you’ll just squirt some jet fuel into the stream of compressed air and light it up, but when that air is moving at thousands of miles per hour, keeping it burning is no small feat. Because of this, the operation of a scramjet has often been likened to trying to light a match in a hurricane; the challenge isn’t in the task, but in the environment you’re trying to perform it in.

Now, both Aerojet Rocketdyne and Northrop Grumman think they may have found the solution: additive manufacturing. By 3D printing their scramjet engines, they can not only iterate through design revisions faster, but produce them far cheaper than they’ve been able to in the past. Even more importantly, it enables complex internal engine geometries that would have been more difficult to produce via traditional manufacturing.

Continue reading “3D Printing May Be The Key To Practical Scramjets” →

This Week In Security: VPN Gateways, Attacks In The Wild, VLC, And An IP Address Caper

We’ll start with more Black Hat/DEFCON news. [Meh Chang] and [Orange Tsai] from Devcore took a look at Fortinet and Pulse Secure devices, and found multiple vulnerabilities. (PDF Slides) They are publishing summaries for that research, and the summary of the Fortinet research is now available.

It’s… not great. There are multiple pre-authentication vulnerabilities, as well as what appears to be an intentional backdoor.

CVE-2018-13379 abuses an snprintf call made when requesting a different language for the device login page. Snprintf is an alternative to sprintf, but intended to prevent buffer overflows by including the maximum string length to write to the target buffer, which sounds like a good idea but can lead to malicious truncation.

The code in question looks like snprintf(s, 0x40, "/migadmin/lang/%s.json", lang);.
When loading the login page, a request is made for a language file, and the file is sent to the user. At first look, it seems that this would indeed limit the file returned to a .json file from the specified folder. Unfortunately, there is no further input validation on the request, so a language of ../../arbitrary is considered perfectly legitimate, escaping the intended folder.  This would leak arbitrary json files, but sincesnprintf doesn’t fail if it exceeds the specified length, sending a request for a lang that’s long enough results in the “.json” extension not being appended to the request either.

A metasploit module has been written to test for this vulnerability, and it requests a lang of /../../../..//////////dev/cmdb/sslvpn_websession. That’s just long enough to force the json extension to fall off the end of the string, and it is Unix convention is to ignore the extra slashes in a path. Just like that, the Fortigate is serving up any file on its filesystem just for asking nice.

More worrying than the snprintf bug is the magic value that appears to be an intentional backdoor. A simple 14 character string sent as an http query string bypasses authentication and allows changing any user’s password — without any authentication. This story is still young, it’s possible this was intended to have a benign purpose. If it’s an honest mistake, it’s a sign of incompetence. If it’s an intentional backdoor, it’s time to retire any and all Fortinet equipment you have.

Pulse Secure VPNs have a similar pre-auth arbitrary file read vulnerability. Once the full report is released, we’ll cover that as well.

Exploitation in the Wild

But wait, there’s more. Hide your kids, hide your wife. Webmin, Pulse Secure, and Fortigate are already being exploited actively in the wild, according to ZDNet. Based on reports from Bad Packets, the Webmin backdoor was being targeted in scans within a day of announcement, and exploited within three days of the announcement. There is already a botnet spreading via this backdoor. It’s estimated that there are around 29,000 vulnerable Internet-facing servers.

Both Pulse Secure and Fortinet’s Fortigate VPN appliances are also being actively targeted. Even though the vulnerabilities were reported first to the vendors, and patched well in advance of the public disclosure, thousands of vulnerable devices remain. Apparently routers and other network appliance hardware are fire-and-forget solutions, and often go without important security updates.

VLC is Actually Vulnerable This Time

The VLC media player has released a new update, fixing 11 CVEs. These CVEs are all cases of mishandling malformed media files, and are only exploitable by opening a malicious file with VLC. Be sure to go update VLC if you have it installed. Even though no arbitrary code execution has been demonstrated for any of these issues, it’s likely that it will eventually happen.

Gray Market IP Addresses

With the exhaustion of IPv4 addresses, many have begun using alternative methods to acquire address space, including the criminal element. Krebs on Security details his investigation into one such story: Residential Networking Solutions LLC (Resnet). It all started with an uptick in fraudulent transactions originating from Resnet residential IP addresses. Was this a real company, actually providing internet connectivity, or a criminal enterprise?

Kilopower: NASA’s Offworld Nuclear Reactor

Here on Earth, the ability to generate electricity is something we take for granted. We can count on the sun to illuminate solar panels, and the movement of air and water to spin turbines. Fossil fuels, for all their downsides, have provided cheap and reliable power for centuries. No matter where you may find yourself on this planet, there’s a way to convert its many natural resources into electrical power.

But what happens when humans first land on Mars, a world that doesn’t offer these incredible gifts? Solar panels will work for a time, but the sunlight that reaches the surface is only a fraction of what the Earth receives, and the constant accumulation of dust makes them a liability. In the wispy atmosphere, the only time the wind could potentially be harnessed would be during one of the planet’s intense storms. Put simply, Mars can’t provide the energy required for a human settlement of any appreciable size.

The situation on the Moon isn’t much better. Sunlight during the lunar day is just as plentiful as it is on Earth, but night on the Moon stretches for two dark and cold weeks. An outpost at the Moon’s South Pole would receive more light than if it were built in the equatorial areas explored during the Apollo missions, but some periods of darkness are unavoidable. With the lunar surface temperature plummeting to -173 °C (-280 °F) when the Sun goes down, a constant supply of energy is an absolute necessity for long-duration human missions to the Moon.

Since 2015, NASA and the United States Department of Energy have been working on the Kilopower project, which aims to develop a small, lightweight, and extremely reliable nuclear reactor that they believe will fulfill this critical role in future off-world exploration. Following a series of highly successful test runs on the prototype hardware in 2017 and 2018, the team believes the miniaturized power plant could be ready for a test flight as early as 2022. Once fully operational, this nearly complete re-imagining of the classic thermal reactor could usher in a whole new era of space exploration.

Continue reading “Kilopower: NASA’s Offworld Nuclear Reactor” →