Get Your Glitch On With A PicoEMP And A 3D Printer

We’re not sure what [Aaron Christophel] calls his automated chip glitching setup built from a 3D printer, but we’re going to go ahead and dub it the “Glitch-o-Matic 9000.” Has a nice ring to it.

Of course, this isn’t a commercial product, or even a rig that’s necessarily intended for repeated use. It’s more of a tactical build, which is still pretty cool if you ask us. It started with a proof-of-concept exploration, summarized in the first video below. That’s where [Aaron] assembled and tested the major pieces, which included a PicoEMP, the bit that actually generates the high-voltage pulses intended to scramble a running microcontroller temporarily, along with a ChipWhisperer and an oscilloscope.

The trouble with the POC setup was that glitching the target chip, an LPC2388 microcontroller, involved manually scanning the business end of the PicoEMP over the package. That’s a tedious and error-prone process, which is perfect for automation. In the second video below, [Aaron] has affixed the PicoEMP to his 3D printer, giving him three-axis control of the tip position. That let him build up a heat map of potential spots to glitch, which eventually led to a successful fault injection attack and a clean firmware dump.

It’s worth noting that the whole reason [Aaron] had to resort to such extreme measures in the first place was the resilience of the target chip against power supply-induced glitching attacks. You might not need to build something like the Glitch-o-Matic, but it’s good to keep in mind in case you run up against such a hard target. Continue reading “Get Your Glitch On With A PicoEMP And A 3D Printer” →
Supercon 2023: Bringing Arcade Classics To New Hardware

The processing power of modern game consoles is absolutely staggering when compared to the coin-op arcade machines of the early 1980s. Packed with terabytes of internal storage and gigabytes of RAM, there’s hardly a comparison to make with the Z80 cabinets that ran classics like Pac-Man. But despite being designed to pump out lifelike 4K imagery without breaking a virtual sweat, occasionally even these cutting-edge consoles are tasked with running one of those iconic early games like Dig Dug or Pole Position. Nostalgia is a hell of a drug…

As long as there are still demand for these genre-defining games, developers will have to keep figuring out ways to bring them to newer — and vastly more complex — systems. Which is precisely the topic of Bob Hickman’s 2023 Supercon talk, The Bits and Bytes of Bringing Arcade Classics to Game Consoles. Having spent decades as a professional game developer, he’s got plenty of experience with the unique constraints presented by both consoles and handhelds, and what it takes to get old code running on new silicon.

Continue reading “Supercon 2023: Bringing Arcade Classics To New Hardware” →

Hacking An IP Camera To Run Your Own Software

Ah, generic unbranded IP cameras. Safe, secure? Probably not. [Alex] has been hacking around with one of his very own, and he’s recently busted the thing wide open.

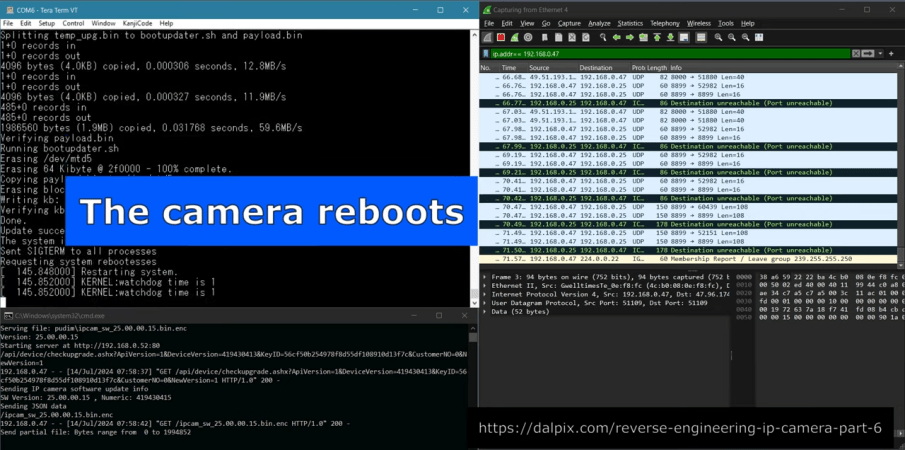
Determining that the camera had a software update function built in, [Alex] saw an opening for hijinks. The first issue was that the camera only accepts encrypted update packages, which complicates things somewhat. However, through some smart reverse engineering, the format of the updates and their encryption method became obvious to [Alex]. Oh, and partly because there was a GitHub repository online featuring the source code used by the manufacturer to encrypt their updates. That definitely helped. It also led [Alex] to suspect the manufacturer may not have properly respected the open source license of some of the routines involved.

In the demo of the exploit, [Alex] has the camera reach out to www.pudim.com.br instead of the servers of the original manufacturer. That’s a pretty clear way to show that the camera has been owned.

We first featured [Alex]’s work in this space all the way back in 2019. It’s come a long way since then!

Continue reading “Hacking An IP Camera To Run Your Own Software” →

Ticketmaster SafeTix Reverse-Engineered

Ticketmaster is having a rough time lately. Recently, a hacker named [Conduition] managed to reverse-engineer their new “safe” electronic ticket system. Of course, they also had the recent breach where more than half a billion accounts had personal and financial data leaked without any indication of whether or not the data was fully encrypted. But we’re going to focus on the former, as it’s more technically interesting.

Ticketmaster’s stated goals for the new SafeTix system — which requires the use of a smartphone app — was to reduce fraud and ticket scalping. Essentially, you purchase a ticket using their app, and some data is downloaded to your phone which generates a rotating barcode every 15 seconds. When [Conduition] arrived at the venue, cell and WiFi service was totally swamped by everyone trying to load their barcode tickets. After many worried minutes (and presumably a few choice words) [Conduition] managed to get a cell signal long enough to update the barcode, and was able to enter, albeit with a large contingent of similarly annoyed fans trying to enter with their legally purchased tickets.

Continue reading “Ticketmaster SafeTix Reverse-Engineered” →

Hackable Ham Radio Gives Up Its Mechanical Secrets

Reverse-engineered schematics are de rigeur around these parts, largely because they’re often the key to very cool hardware hacks. We don’t get to see many mechanical reverse-engineering efforts, though, which is a pity because electronic hacks often literally don’t stand on their own. That’s why these reverse-engineered mechanical diagrams of the Quansheng UV-K5 portable amateur radio transceiver really caught our eye.

Part of the reason for the dearth of mechanical diagrams for devices, even one as electrically and computationally hackable as the UV-K5, is that mechanical diagrams are a lot less abstract than a schematic or even firmware. Luckily, this fact didn’t daunt [mdlougheed] from putting a stripped-down UV-K5 under a camera for a series of images to gather the raw data needed by photogrammetry package RealityCapture. The point cloud was thoughtfully scaled to match the dimensions of the radio’s reverse-engineered PC board, so the two models can work together.

The results are pretty impressive, especially for a first effort, and should make electromechanical modifications to the radio all the easier to accomplish. Hats off to [mdlougheed] for the good work, and let the mechanical hacks begin.

Toyota Heater Switches Learn New Tricks

The look, the feel, the sound — there are few things more satisfying in this world than a nice switch. If you’re putting together a device that you plan on using frequently, outfitting it with high-quality switches is one of those things that’s worth the extra cost and effort.

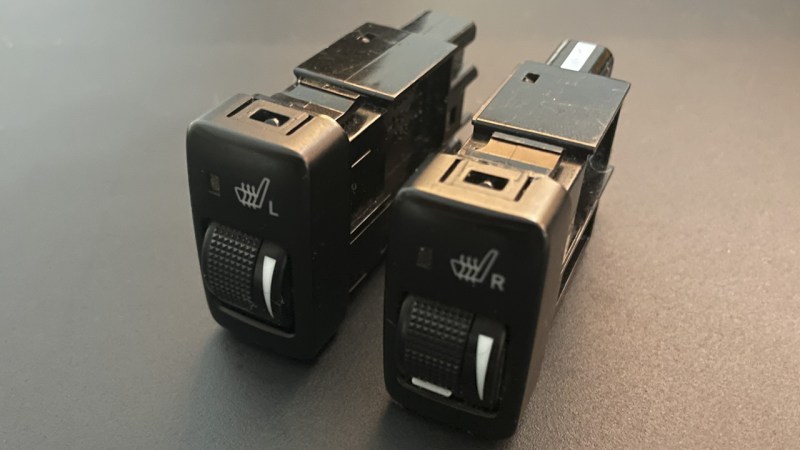
So we understand completely why [STR-Alorman] went to such great lengths to get the aftermarket seat heaters he purchased working with the gorgeous switches Toyota used in the 2006 4Runner. That might not sound like the kind of thing that would involve reverse engineering hardware, creating a custom PCB, or writing a bit of code to tie it all together. But of course, when working on even a halfway modern automobile, it seems nothing is ever easy.

The process started with opening up the original Toyota switches and figuring out how they work. The six-pin units have a lot going on internally, with a toggle, a rheostat, and multiple lights packed into each one. Toyota has some pretty good documentation, but it still took some practical testing to distill it down into something a bit more manageable. The resulting KiCad symbol for the switch helps explain what’s happening inside, and [STR-Alorman] has provided a chart that attributes each detent on the knob with the measured resistance.

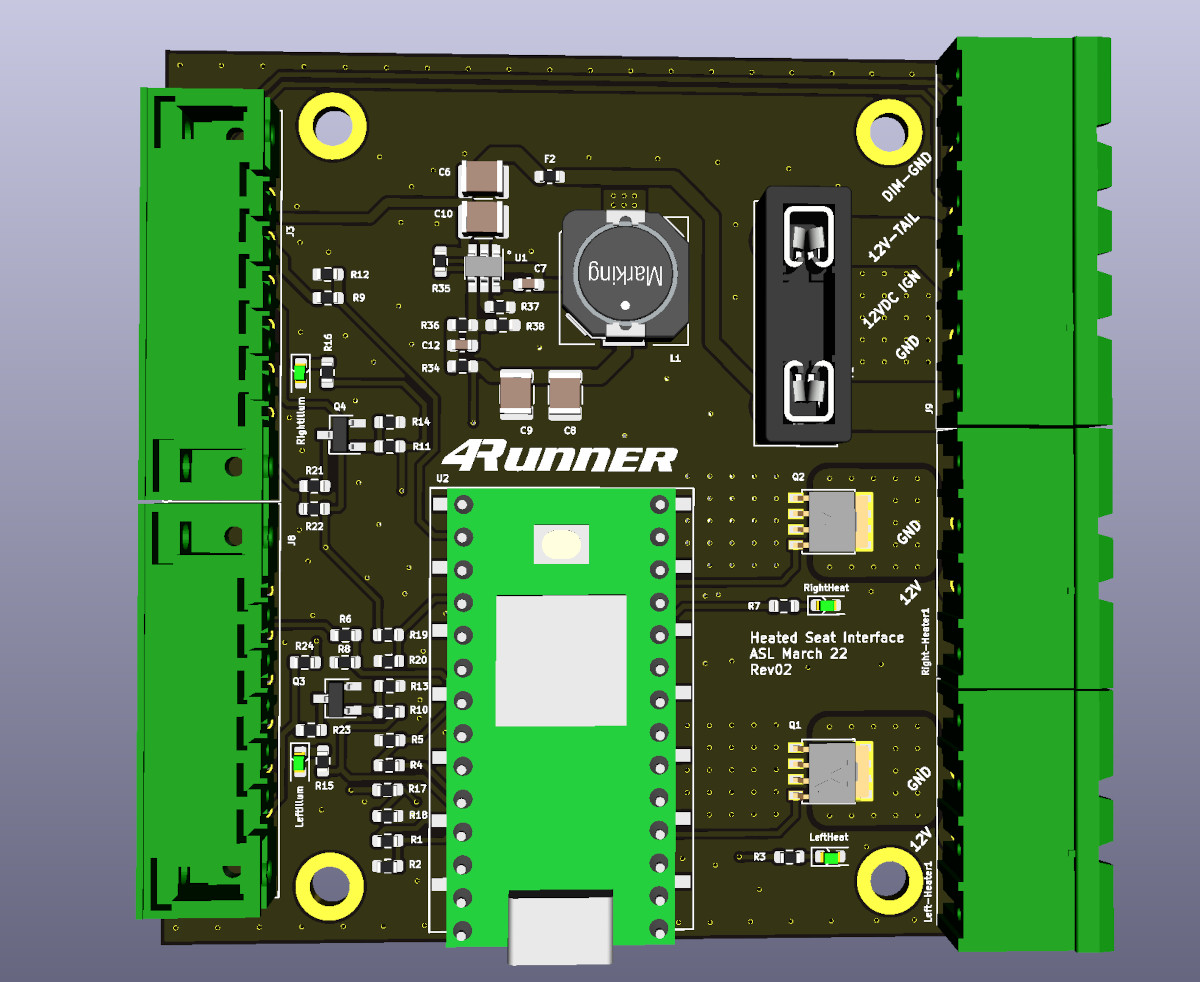
But understanding how the switches worked was only half the battle. The aftermarket seat heaters were only designed to work with simple toggles, so [STR-Alorman] had to develop a controller that could interface with the Toyota switches and convince the heaters to produce the desired result. The custom PCB hosts a Teensy 3.2 that reads the information from both the left and right seat switches, and uses that to control a pair of beefy MOSFETs. An interesting note here is the use of very slow pulse-width modulation (PWM) used to flip the state of the MOSFET due to the thermal inertia of the heater modules.

We love the effort [STR-Alorman] put into documenting this project, going as far as providing the Toyota part numbers for the switches and the appropriate center-console panel with the appropriate openings to accept them. It’s an excellent resource if you happen to own a 4Runner from this era, and a fascinating read for the rest of us.

Smartwatch Snitches On Itself And Enables Reverse Engineering

If something has a “smart” in its name, you know that it’s talking to someone else, and the topic of conversation is probably you. You may or may not like that, but that’s part of the deal when you buy these things. But with some smarts of your own, you might be able to make that widget talk to you rather than about you.

Such an opportunity presented itself to [Benjamen Lim] when a bunch of brand X smartwatches came his way. Without any documentation to guide him, [Benjamen] started with an inspection, which revealed a screen of debug info that included a mysterious IP address and port. Tearing one of the watches apart — a significant advantage to having multiple units to work with — revealed little other than an nRF52832 microcontroller along with WiFi and cellular chips. But the luckiest find was JTAG pins connected to pads on the watch face that mate with its charging cradle. That meant talking to the chip was only a spliced USB cable away.

Once he could connect to the watch, [Benjamen] was able to dump the firmware and fire up Ghidra. He decided to focus on the IP address the watch seemed fixated on, reasoning that it might be the address of an update server, and that patching the firmware with a different address could be handy. He couldn’t find the IP as a string in the firmware, but he did manage to find a sprintf-like format string for IP addresses, which led him to a likely memory location. Sure enough, the IP and port were right there, so he wrote a script to change the address to a server he had the keys for and flashed the watch.

So the score stands at [Benjamen] 1, smartwatch 0. It’s not clear what the goal of all this was, but we’d love to see if he comes up with something cool for these widgets. Even if there’s nothing else, it was a cool lesson in reverse engineering.