NASA’s “Green” Fuel Seeks Safer Spaceflight By Finally Moving Off Toxic Hydrazine

Spaceflight is inherently dangerous. It takes a certain type of person to willingly strap into what’s essentially a refined bomb and hope for the best. But what might not be so obvious is that the risks involved aren’t limited to those who are personally making the trip. The construction and testing of space-bound vehicles poses just as much danger to engineers here on the ground as it does to the astronauts in orbit. Arguably, more so. Far more individuals have given their lives developing rocket technology than have ever died in the cockpit of one of them.
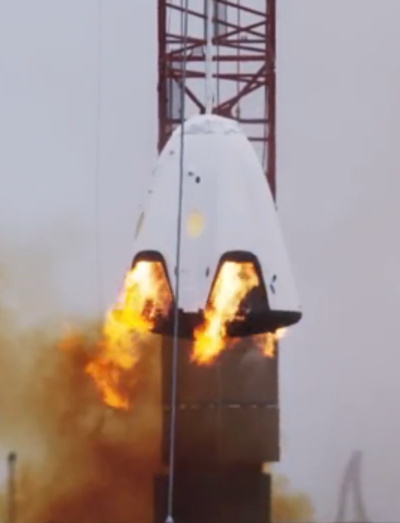
Reddish brown exhaust of hydrazine thrusters

Ultimately, this is because of the enormous amount of energy stored in the propellants required to make a rocket fly. Ground support personnel need to exercise great care even when dealing with “safe” propellants, such as the classic combination of kerosene and liquid oxygen. On the other end of the spectrum you have chemicals that are so unstable and toxic that they can’t be handled without special training and equipment.

One of the most dangerous chemicals ever used in rocket propulsion is hydrazine; and yet from the Second World War to the present day, it’s been considered something of an occupational hazard of spaceflight. While American launch vehicles largely moved away from using it as a primary propellant, hydrazine is still commonly used for smaller thrusters on spacecraft.

When SpaceX’s Crew Dragon exploded in April during ground tests, the release of approximately one and a half tons of hydrazine and nitrogen tetroxide propellants required an environmental cleanup at the site.

But soon, that might change. NASA has been working on a project they call the Green Propellant Infusion Mission (GPIM) which is specifically designed to reduce modern spacecraft’s dependency on hydrazine. In collaboration with the Air Force Research Laboratory at California’s Edwards Air Force Base, the space agency has spearheaded the development of a new propellant that promises to not just replace hydrazine, but in some scenarios even outperform it.

So what’s so good about this new wonder fuel, called AF-M315E? To really understand why NASA is so eager to power future craft with something new, we first have to look at the situation we’re in currently.

Continue reading “NASA’s “Green” Fuel Seeks Safer Spaceflight By Finally Moving Off Toxic Hydrazine” →
Building A Foam Machine From A Leaf Blower And A Water Pump

Imagine a tub overflowing with bubble bath, except it’s a club dancefloor and music is pumping all night. This is what is known as a “foam party” — a wild and exciting concept that nonetheless many are yet to experience. The concept exploded in popularity in Ibiza in the 1990s, and foam parties are regularly held at nightclubs and festivals the world over.

Foam is generated with the obviously-named foam machine, and these can be readily purchased or hired for anyone wishing to host such an event. However, that’s not the hacker way. If you’re a little ingenious and take heed of the safety precautions, here’s how you can do it yourself.

Continue reading “Building A Foam Machine From A Leaf Blower And A Water Pump” →

Reverse Engineering Cyclic Redundancy Codes

Cyclic redundancy codes (CRC) are a type of checksum commonly used to detect errors in data transmission. For instance, every Ethernet packet that brought you the web page you’re reading now carried with it a frame check sequence that was calculated using a CRC algorithm. Any corrupted packets that failed the check were discarded, and the missing data was detected and re-sent by higher-level protocols. While Ethernet uses a particularly common CRC, there are many, many different possibilities. When you’re reverse-engineering a protocol that contains a CRC, although it’s not intended as a security mechanism, it can throw a wrench in your plans. Luckily, if you know the right tool, you can figure it out from just a few sample messages.

A case in point was discussed recently on the hackaday.io Hack Chat, where [Thomas Flayols] came for help reverse engineering the protocol for some RFID tags used for race timing. Let’s have a look at the CRC, how it is commonly used, and how you can reverse-engineer a protocol that includes one, using [Thomas’] application as an example.

Continue reading “Reverse Engineering Cyclic Redundancy Codes” →

What’s The Deal With Square Traces On PCBs

When designing a printed circuit board, there are certain rules. You should place decoupling capacitors near the power pins to each chip. Your ground planes should be one gigantic fill of copper; two ground planes connected by a single trace is better known as an antenna. Analog sections should be kept separate from digital sections, and if you’re dealing with high voltage, that section needs to be isolated.

One that I hear a lot is that you must never put a 90-degree angle on a trace. Some fear the mere sight of a 90-degree angle on a PCB tells everyone you don’t know what you’re doing. But is there is really no greater sin than a 90-degree trace on a circuit board?

This conventional wisdom of eschewing 90-degree traces is baked into everything we know about circuit board design. It is the first thing you’re taught, and it’s the first thing you’ll criticize when you find a board with 90-degree traces. Do square traces actually matter? The short answer is no, but there’s still a reason we don’t do it.

Continue reading “What’s The Deal With Square Traces On PCBs” →

Impersonate The President With Consumer-Grade SDR

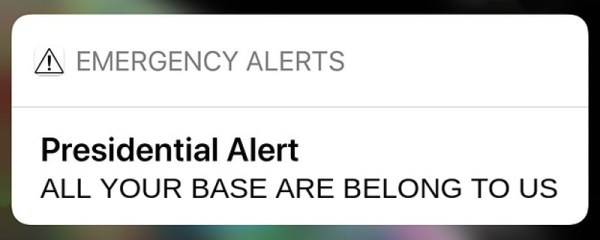
In April of 2018, the Federal Emergency Management Agency sent out the very first “Presidential Alert”, a new class of emergency notification that could be pushed out in addition to the weather and missing child messages that most users were already familiar with. But while those other messages are localized in nature, Presidential Alerts are intended as a way for the Government to reach essentially every mobile phone in the country. But what if the next Presidential Alert that pops up on your phone was actually sent from somebody with a Software Defined Radio?

According to research recently released by a team from the University of Colorado Boulder, it’s not as far-fetched a scenario as you might think. In fact, given what they found about how the Commercial Mobile Alert Service (CMAS) works, there might not be a whole lot we can even do to prevent it. The system was designed to push out these messages in the most expedient and reliable way possible, which meant that niceties like authentication had to take a backseat.

The thirteen page report, which was presented at MobiSys 2019 in Seoul, details their findings on CMAS as well as their successful efforts to send spoofed Presidential Alerts to phones of various makes and models. The team used a BladeRF 2.0 and USRP B210 to perform their mock attacks, and even a commercially available LTE femtocell with modified software. Everything was performed within a Faraday cage to prevent fake messages from reaching the outside world.

So how does the attack work? To make a long story short, the team found that phones will accept CMAS messages even if they are not currently authenticated with a cell tower. So the first phase of the attack is to spoof a cell tower that provides a stronger signal than the real ones in the area; not very difficult in an enclosed space. When the phone sees the stronger “tower” it will attempt, but ultimately fail, to authenticate with it. After a few retries, it will give up and switch to a valid tower.

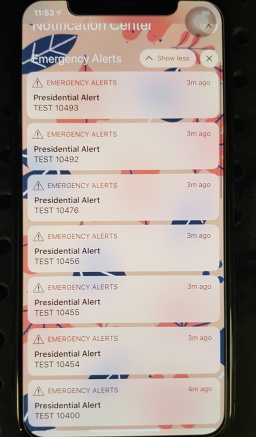
This negotiation takes around 45 seconds to complete, which gives the attacker a window of opportunity to send the fake alerts. The team says one CMAS message can be sent every 160 milliseconds, so there’s plenty of time to flood the victim’s phone with hundreds of unblockable phony messages.

The attack is possible because the system was intentionally designed to maximize the likelihood that users would receive the message. Rather than risk users missing a Presidential Alert because their phones were negotiating between different towers at the time, the decision was made to just push them through regardless. The paper concludes that one of the best ways to mitigate this attack would be to implement some kind of digital signature check in the phone’s operating system before the message gets displayed to the user. The phone might not be able to refuse the message itself, but it can at least ascertain it’s authentic before showing it to the user.

All of the team’s findings have been passed on to the appropriate Government agencies and manufacturers, but it will likely be some time before we find out what (if any) changes come from this research. Considering the cost of equipment that can spoof cell networks has dropped like a rock over the last few years, we’re hoping all the players can agree on a software fix before we start drowning in Presidential Spam.

You’re Sitting On An Engineering Masterpiece: Chairs As A Design Challenge

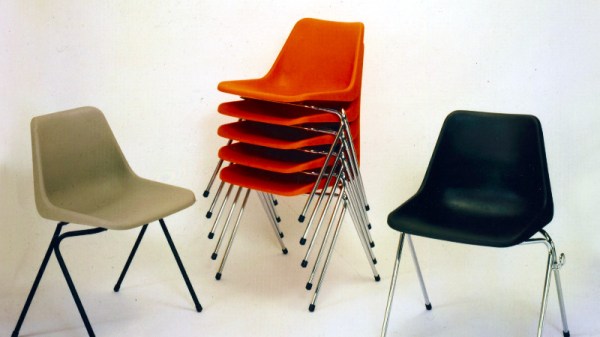
If you move as a hardware hacker through the sometimes surprisingly similar world of artists, craftspeople, designers, blacksmiths, and even architects, there’s one piece of work that you will see time and time again as an object that exerts a curious fascination. It seems that designing and building a chair is a rite of passage, and not just a simple chair, but in many cases an interesting chair.

An American-made Windsor chair from the turn of the 19th century. Los Angeles County Museum of Art [Public domain]
Some of the most iconic seating designs that you will be instantly familiar with through countless mass-produced imitations began their lives as one-off design exercises. Yet we rarely see them in our community of hackers and makers, a search turns up only a couple of examples. This is surprising, not least because there is more than meets the eye to this particular piece of furniture. Your simple seat can be a surprisingly complex challenge.

Moving Charis From Artisan to Mass Market

The new materials and mass production techniques of the 19th and 20th centuries have brought high-end design into the hands of the masses, but while wealthy homes in earlier centuries had high-quality bespoke furniture in the style of the day, the traditional furniture of the masses was hand-made in the same way for centuries often to a particular style dependent on the region in which it was produced.

Continue reading “You’re Sitting On An Engineering Masterpiece: Chairs As A Design Challenge” →

The Future Of Space Is Tiny

While recent commercial competition has dropped the cost of reaching orbit to a point that many would have deemed impossible just a decade ago, it’s still incredibly expensive. We’ve moved on from the days where space was solely the domain of world superpowers into an era where multi-billion dollar companies can join on on the fun, but the technological leaps required to reduce it much further are still largely relegated to the drawing board. For the time being, thing’s are as good as they’re going to get.

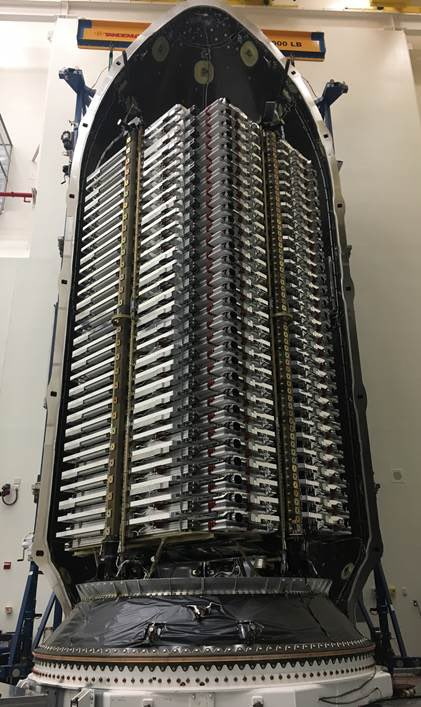
Starlink satellites ready for launch

If we can’t count on the per pound cost of an orbital launch to keep dropping over the next few years, the next best option would logically be to design spacecraft that are smaller and lighter. Thankfully, that part is fairly easy. The smartphone revolution means we can already pack an incredible amount sensors and processing power into something that can fit in the palm of your hand. But there’s a catch: the Tsiolkovsky rocket equation.

Often referred to as simply the “rocket equation”, it allows you to calculate (among other things) the ratio of a vehicle’s useful cargo to its total mass. For an orbital rocket, this figure is very small. Even with a modern launcher like the Falcon 9, the payload makes up less than 5% of the liftoff weight. In other words, the laws of physics demand that orbital rockets are huge.

Unfortunately, the cost of operating such a rocket doesn’t scale with how much mass it’s carrying. No matter how light the payload is, SpaceX is going to want around $60,000,000 USD to launch the Falcon 9. But what if you packed it full of dozens, or even hundreds, of smaller satellites? If they all belong to the same operator, then it’s an extremely cost-effective way to fly. On the other hand, if all those “passengers” belong to different groups that split the cost of the launch, each individual operator could be looking at a hundredfold price reduction.

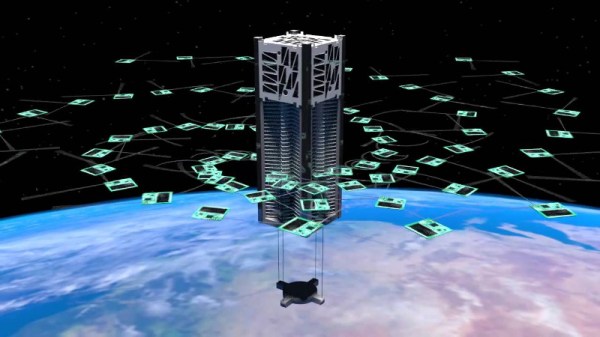
SpaceX has already packed 60 of their small and light Starlink satellites into a single launch, but even those craft are massive compared to what other groups are working on. We’re seeing the dawn of a new era of spacecraft that are even smaller than CubeSats. These tiny spacecraft offer exciting new possibilities, but also introduce unique engineering challenges.

Continue reading “The Future Of Space Is Tiny” →