Rusting An E-scooter (In A Good Way)

It is a classic Hackaday situation. You have an Egret GT E-scooter. It has a screen that shows the usual dash stats, but that led to an annoyance. You could accidentally enter firmware update mode and, from there, enter operational mode without the security PIN. [Ben] couldn’t let that stand, so he reverse-engineered the protocol and rewrote the firmware in Rust. As he put it, “… because I have to break… everything I own…” We get it.

The mobile app was useful for some basic info, since sniffing Bluetooth is fairly easy and analyzing mobile code is, more or less, straightforward. Analysis revealed some data that doesn’t show on the display and that several things are sent back to home base tagged with the scooter’s unique ID — another reason to gut the existing firmware.

Continue reading “Rusting An E-scooter (In A Good Way)”

A Tool For Testing CANopen Networks

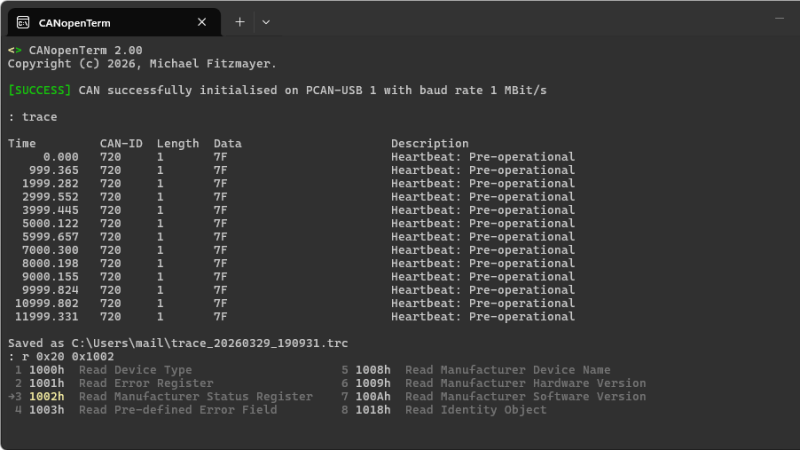
If you find yourself working with CANopen CC networks, you might find yourself in need of a tool for monitoring what’s happening on the wire. [Michael Fitzmayer] whipped up a piece of software to fulfil just that role. 

CANopenTerm might be named after the CANopen standard, but it’s really a terminal-driven tool for working with CAN buses in general. The software is built for real-time use, allowing sniffing raw frames on the wire, tracing, and probing of nodes, all from within the console. It’s also possible to add scripting via Lua or Python for more advanced work, as well as do protocol-aware inspection if that’s relevant to your use case. The key idea of the software is to be fast and scriptable to suit a given need, rather than bogging everything down with a heavy GUI interface that’s slower to work with.

If you aren’t afraid of getting into the nitty gritty with CAN and like lightweight text-based interfaces, this might be the tool for you. We’ve also explored some other CAN visualization tools lately, as well. Ultimately, there is a lot of machinery out there running on some variant of CAN or other, so it pays to know how to work with it. If you’ve got your own projects cooking up in this space, don’t hesitate to let us know on the tipsline!

CAN Bus Analyzer Runs In Your Browser

If you’ve got a modern car, truck, or tractor, it’s probably got a CAN bus or three that is bouncing data all around the vehicle. Listening in on these transmissions can enlighten you to what’s going on with sensors and modules which can aid in troubleshooting. You might find [Chanchal]’s latest work to be helpful in this regard — a CAN bus visualizer that runs right in your browser.

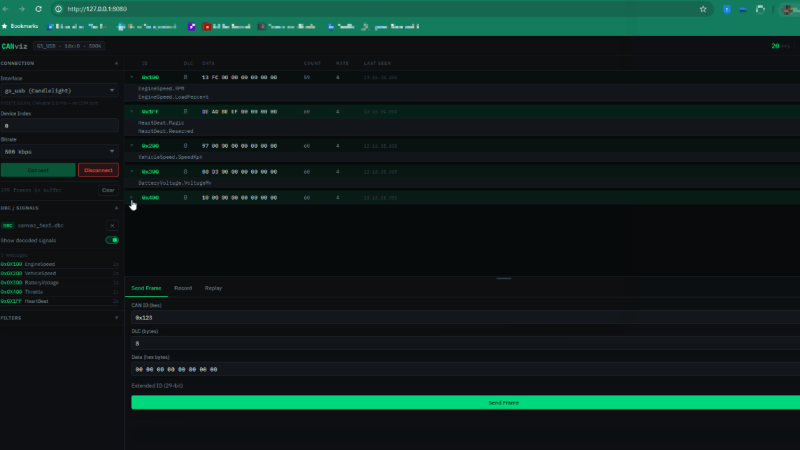
CANviz, as the project is known, is designed to work with any one of a number of cheap USB CAN reader modules. To use it, you simply run the Python “pip” tool to install it, and then you have a live CAN bus frame analyzer running on your local machine. Point your browser to localhost:8080 and you can see the data pouring in from whatever you happen to be hooked up to. The tool supports decoding CAN DBC files to make better sense of the raw data coming off the bus, and you can also record sessions for later analysis and even send CAN frames yourself if you need to. You can also run the tool on a remote single-board PC if so desired and access it over a network connection from another machine.

We’ve explored CAN hacking tools before and tools for visualization as well. Often, the latter is important when trying to debug and investigate dynamic issues. Meanwhile, if you’re working on your own automotive interface hacks, don’t hesitate to notify the tipsline!

HRV Gets Home Automation Upgrades

In our modern semi-dystopia, it seems like most companies add automation features to their products to lock them down and get consumers to buy even more proprietary, locked-down components. The few things that are still user-upgradable are getting fewer and farther between, but there are still a few things that can be modified and improved to our own liking like this control panel for a heat recovery ventilator (HRV).

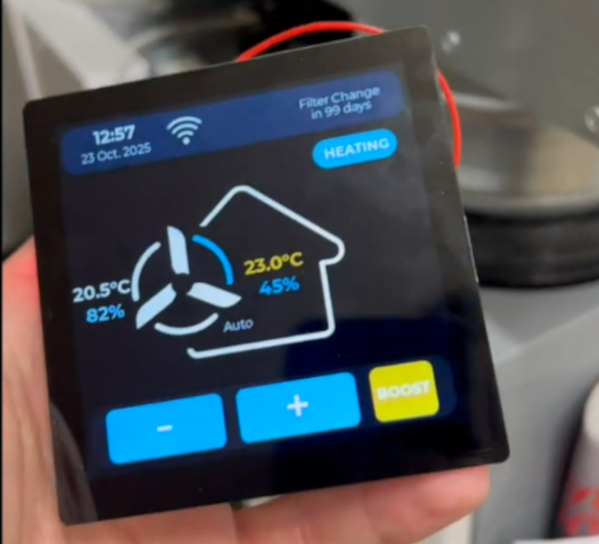
HRVs are systems that exchange fresh, outside air with stale, inside air while passing them both through a heat exchanger to keep from wasting energy. Many systems run continuously but they aren’t always needed, so some automation is beneficial. This upgrade from [vincentmakes] improves the default display for a Zehnder Comfoair Q350 HRV with a color display as well as adding it in to a home automation system, letting a user control fan speeds remotely as well as alerting the user when it’s time for filter replacements and providing up-to-date information from all the sensors in the HRV.

The project builds on a previous project which adapted an ESP32 to interact with the CAN bus used on these devices. With these upgrades the user can forgo the $300 proprietary upgrade that would be needed to get the same functionality otherwise. It’s also fully open-source so all that’s needed is to flash the firmware, replace the display, and enjoy the fresh air. There’s other modern HVAC equipment that can benefit from new controllers and a bit of automation as well.

Continue reading “HRV Gets Home Automation Upgrades”

Printed Robotic Arm Pumps Up With Brushless Motors

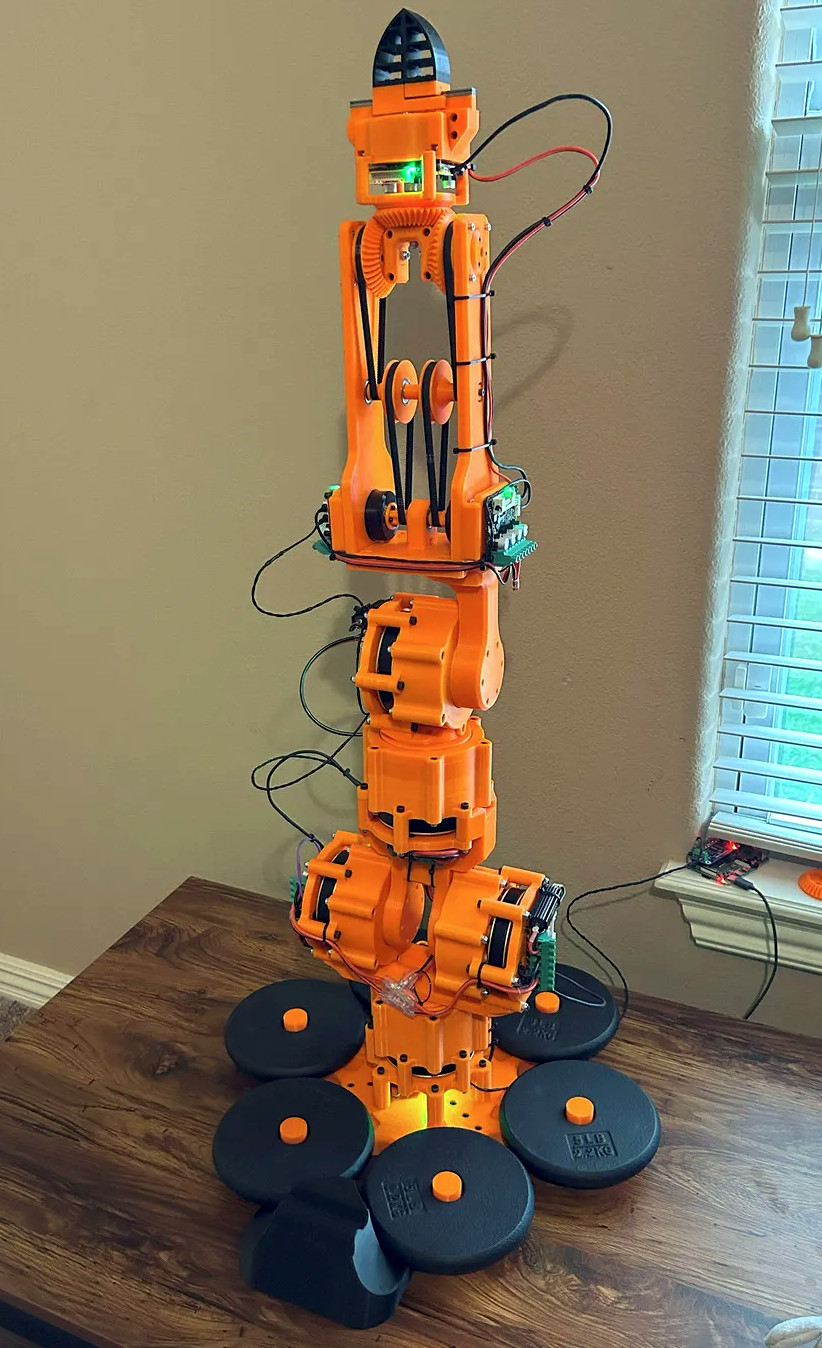
[JesseDarr] recently wrote in to tell us about their dynamic Arm for Robitc Mischief (dARM), a mostly 3D printed six degrees of freedom (6DOF) robotic arm that’s designed to be stronger and more capable than what we’ve seen so far from the DIY community.
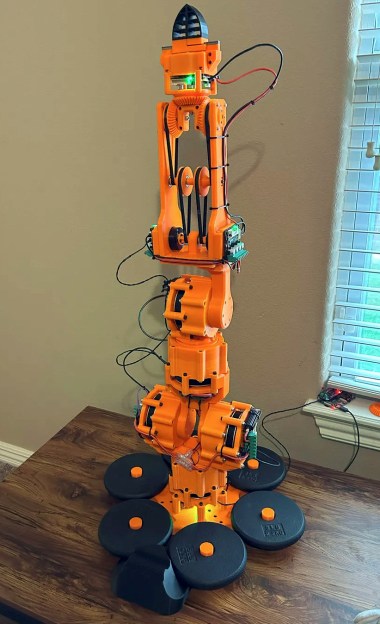
The secret? Rather than using servos, dARM uses brushless DC (BLDC) motors paired with ODrive S1 controllers. He credits [James Bruton] and [Skyentific] (two names which regular Hackaday readers are likely familiar with) for introducing him to not only the ODrive controllers, but the robotics applications for BLDCs in the first place.

dARM uses eight ODrive controllers on a CAN bus, which ultimately connect up to a Raspberry Pi 4B with a RS485 CAN Hat. The controllers are connected to each other in a daisy chain using basic twisted pair wire, which simplifies the construction and maintenance of the modular arm.

As for the motors themselves, the arm uses three different types depending on where they are located, with three Eaglepower 8308 units for primary actuators, a pair of GB36-2 motors in the forearm, and finally a GM5208-24 for the gripper. Together, [JesseDarr] says the motors and gearboxes are strong enough to lift a 5 pound (2.2 kilogram) payload when extended in a horizontal position.

The project’s documentation includes assembly instructions for the printed parts, a complete Bill of Materials, and guidance on how to get the software environment setup on the Raspberry Pi. It’s not exactly a step-by-step manual, but it looks like there’s more than enough information here for anyone who’s serious about building a dARM for themselves.

If you’d like to start off by putting together something a bit easier, we’ve seen considerably less intimidating robotic arms that you might be interested in.

Continue reading “Printed Robotic Arm Pumps Up With Brushless Motors”

Supercon 2024: Yes, You Can Use The Controller Area Network Outside Of Cars

Ah, the CAN bus. It’s become a communication standard in the automotive world, found in a huge swathe of cars built from the mid-1990s onwards. You’ll also find it in aircraft, ships, and the vast majority of modern tractors and associated farm machines, too.

As far as [Randy Glenn] is concerned, though, the CAN bus doesn’t have to be limited to these contexts. It can be useful far beyond its traditional applications with just about any hardware platform you care to use! He came down to tell us all about it at the 2024 Hackaday Supercon.

Continue reading “Supercon 2024: Yes, You Can Use The Controller Area Network Outside Of Cars”

Extracting SecOC Keys From A 2021 Toyota RAV4 Prime

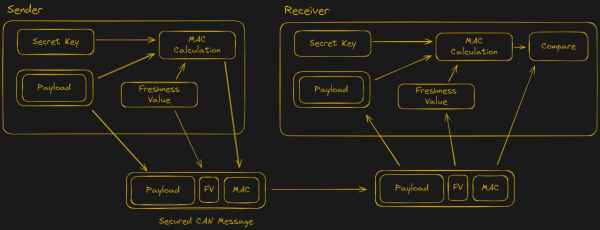
With the recently introduced SecOC (Secure Onboard Communication) standard, car manufacturers seek to make the CAN bus networks that form the backbone of modern day cars more secure. This standard adds a MAC (message authentication code) to the CAN messages, which can be used to validate that these messages come from a genuine part of the car, and not from a car thief or some third-party peripheral.

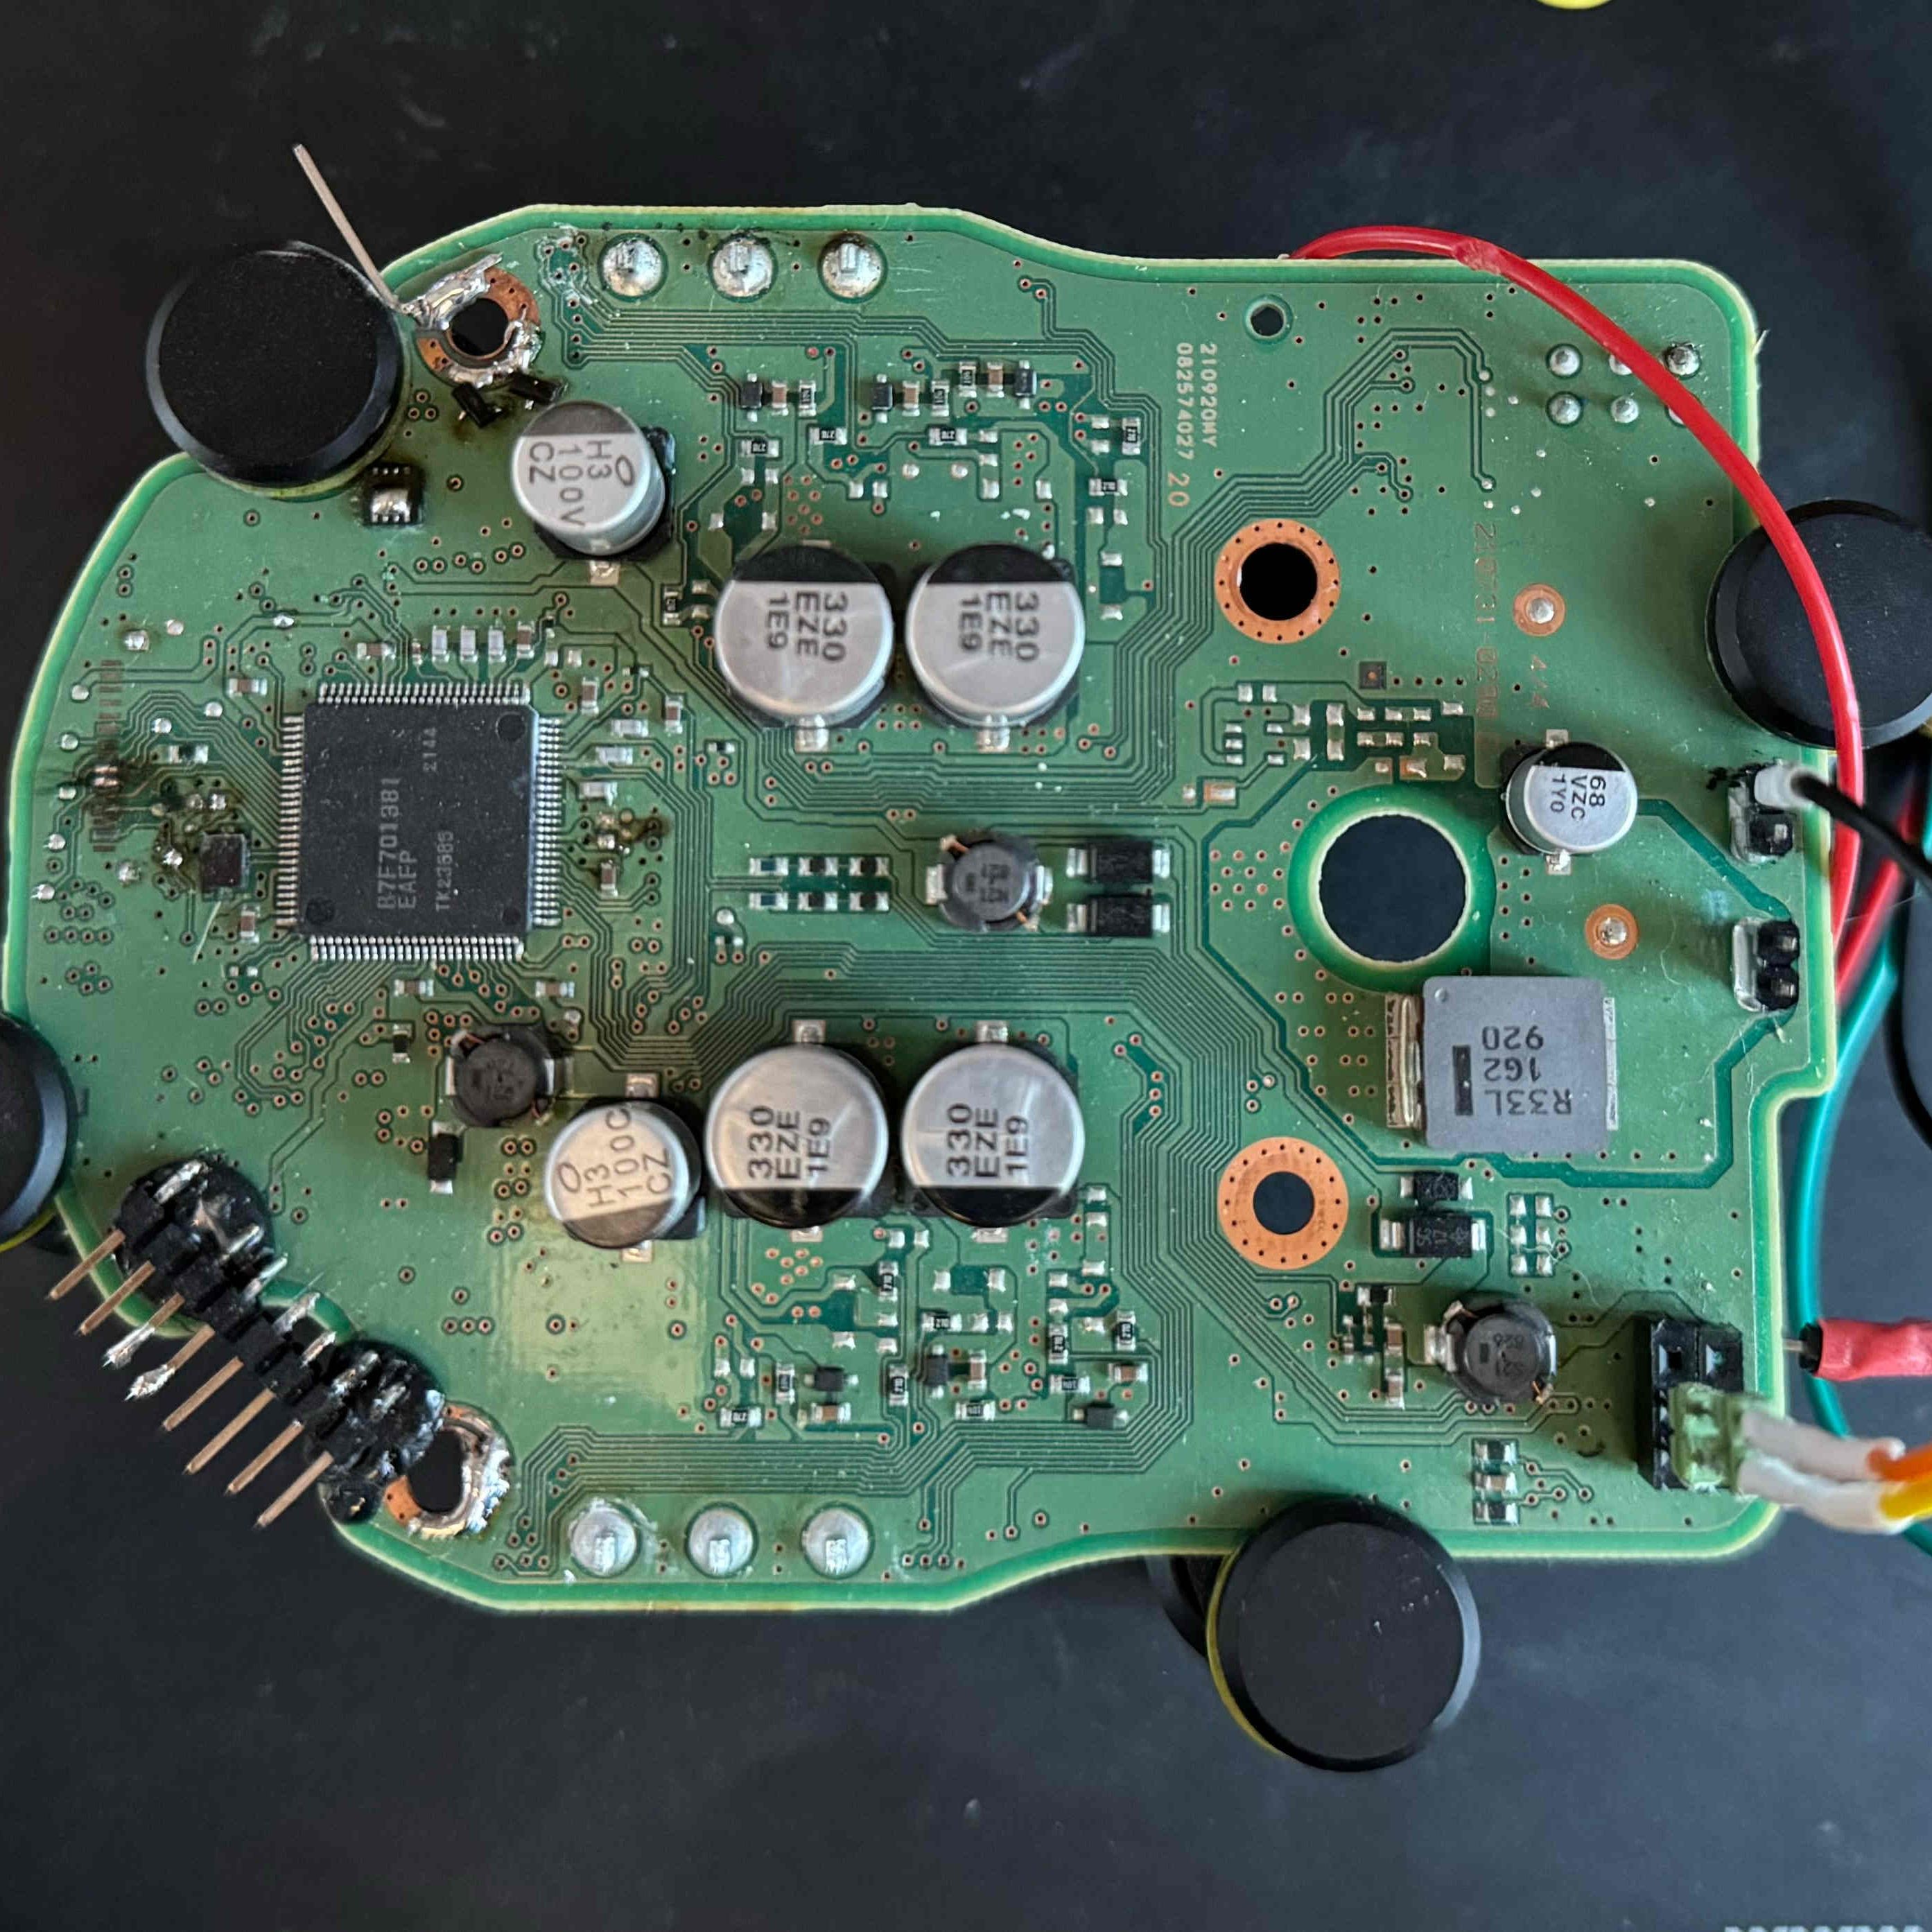
To check that it isn’t possible to circumvent SecOC, [Willem Melching] and [Greg Hogan] got their hands on the power steering (EPS) unit of a Toyota RAV4 Prime, as one of the first cars to implement this new security standard.

The 2021 Toyota RAV4 Prime's power steering unit on the examination bench. (Credit: Willem Melching)
The 2021 Toyota RAV4 Prime’s power steering unit on the examination bench. (Credit: Willem Melching)

As noted by [Willem], the ultimate goal is to be able to run the open source driver assistance system openpilot on these SecOC-enabled cars, which would require either breaking SecOC, or following the official method of ‘rekeying’ the SecOC gateway.

After dumping the firmware of the EPS Renesas RH850/P1M-E MCU via a voltage fault injection, the AES-based encryption routines were identified, but no easy exploits found in the main application. This left the bootloader as the next target.

Ultimately they managed to reverse-engineer the bootloader to determine how the update procedure works, which enabled them to upload shellcode. This script then enabled them to extract the SecOC keys from RAM and send these over the CAN bus. With these keys the path is thus opened to allow any device to generate CAN messages with valid SecOC MACs, effectively breaking encryption. Naturally, there are many caveats with this discovery.

Continue reading “Extracting SecOC Keys From A 2021 Toyota RAV4 Prime”