The phones! They were one of the basic utilities of the 20th century, and were just about as reliable as death and taxes. Even when then power grid went down, you still had a fair shot of getting a phone call through thanks to the reliability of the Plain Old Telephone Service.
Typically, when you’re sitting on a plane on the tarmac, you switch your phone to flight mode while you’re sitting through yet another “quirky” (boring) safety video. You’ll watch some inflight entertainment, read the airline magazine if you get really desperate, and wonder if anyone ever buys those random watches for sale in the “duty free” section. Then, finally, upon landing, you’ll be connected back to the Internet and you’ll finally feel like you can breathe again.
Only, this time, you forgot to set your phone to flight mode. You’re sitting at 30,000 feet, and… your phone has signal? You’re online, and you’re getting notifications and emails just like you’re on the ground. You’ve accidentally discovered that your flight has an on-board cell tower.
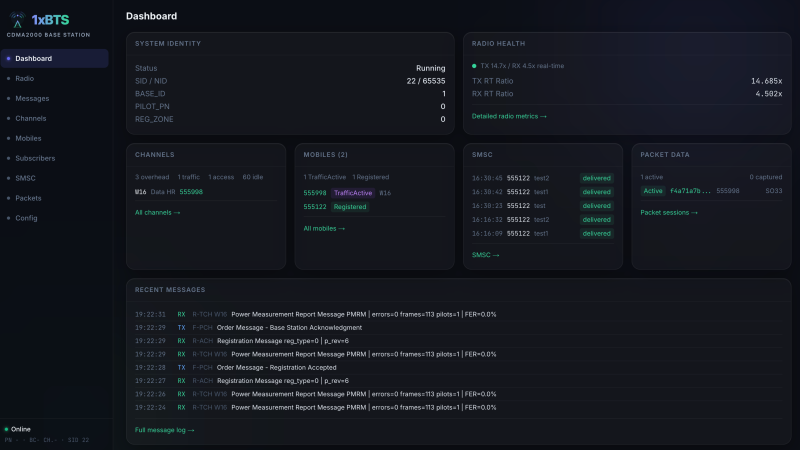
CDMA2000 was one of the protocols defined for 3G networks and is now years out of date and being phased out worldwide. Nevertheless, there are still vast numbers of phones that will happily connect to it, creating an opportunity for hackers seeking to run their own cellular networks. [Chrismoos] recently made this endeavour significantly easier by releasing 1xBTS, a Rust implementation of the lower three layers of a CDMA2000 network.
The lowest layer of the stack is an SDR for the actual radio communications. It’s been tested with the USRP B200 and B210, the LimeSDR Mini 2, and the BladeRF Micro 2.0. The code might work with certain other SDRs using the SoapySDR abstraction layer. The SDR is controlled by the base station (BTS) software, which, in turn, is controlled by the base station controller (BSC) over an Abis link. The BSC manages channels and mobile device associations, and exchanges frames with the mobile switching center (MSC), which handles message switching.
The fifth generation mobile communications protocol (5G) is perhaps the most complicated wireless protocol ever made. Featuring wildly fast download speeds, beam forming base stations, and of course non-standard additions, it’s rather daunting prospect to analyze for the home hacker and researcher alike. But this didn’t stop the ASSET Research Group from developing a 5G sniffer and downlink injector.
The crux of the project is focused around real-time sniffing using one of two Universal Software Radio Peripheral (USRP) software-defined radios (SDRs), and a substantial quantity of compute power. This sniffed data can even be piped into Wireshark for filtering. The frequency is hard-coded into the sniffer for improved performance with the n78 and n41 bands having been tested as of writing. While we expect most of you don’t have the supported USRP hardware, they provided a sample capture file for anyone to analyze.
The other main feature of the project is an exploitation framework with numerous attack vectors developed by ASSET and others. By turning an SDR into a malicious 5G base station, numerous vulnerabilities and “features” can be exploited to with results ranging from downgrading the connection to 4G, fingerprinting and much more. It even includes an attack method we preciously covered called 5Ghull which can cause device failure requiring removal of the SIM Card. These vulnerabilities offer a unique look inside the inner workings of 5G.
These days, if you’re walking around with a cellphone, you’ve basically fitted an always-on tracking device to your person. That’s even more the case if there happens to be an eavesdropping device in your vicinity. To combat this, the Electronic Frontier Foundation has created Rayhunter as a warning device.
Rayhunter is built to detect IMSI catchers, also known as Stingrays in the popular lexicon. These are devices that attempt to capture your phone’s IMSI (international mobile subscriber identity) number by pretending to be real cell towers. Information on these devices is tightly controlled by manufacturers, which largely market them for use by law enforcement and intelligence agencies.
Rayhunter in use.
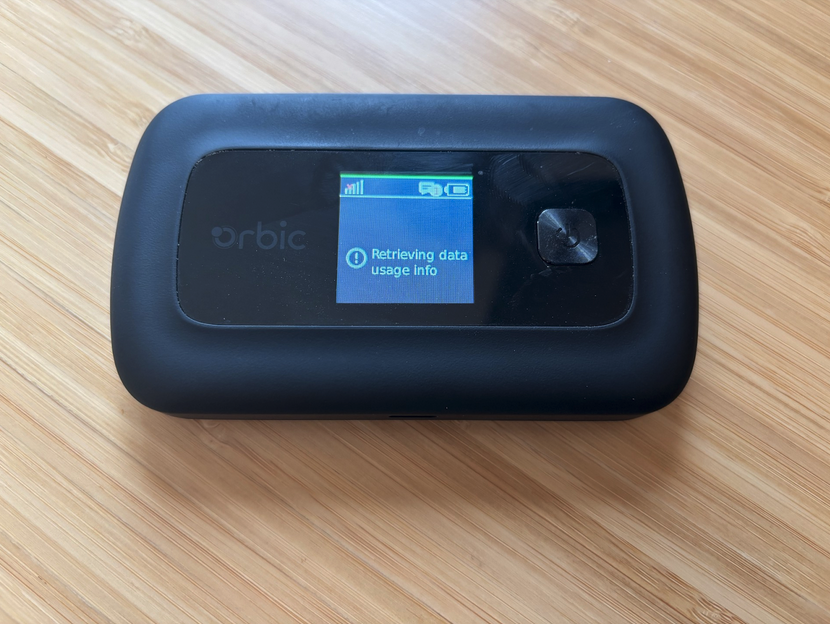
To run Rayhunter, all you need is an Orbic RC400L mobile hotspot, which you can currently source for less than $30 USD online. Though experience tells us that could change as the project becomes more popular with hackers. The project offers an install script that will compile the latest version of the software and flash it to the device from a computer running Linux or macOS — Windows users currently have to jump through a few extra hoops to get the same results.
Rayhunter works by analyzing the control traffic between the cell tower and the hotspot to look out for hints of IMSI-catcher activity. Common telltale signs are requests to switch a connection to less-secure 2G standards, or spurious queries for your device’s IMSI. If Rayhunter notes suspicious activity, it turns a line on the Orbic’s display red as a warning. The device’s web interface can then be accessed for more information.
It might seem quaint through the lends of history we have the luxury of looking through, but in the mid 1980s it was a major symbol of status to be able to communicate on-the-go. Car phones and pagers were cutting-edge devices of the time, and even though there were some mobile cellular telephones, they were behemoths compared to anything we would recognize as a cell phone today. It wasn’t until 1985 that a cell phone was able to fit in a pocket, and that first device wasn’t just revolutionary because of its size. It made a number of technological advancements that were extremely impressive for its time, and [Janus Cycle] takes us through some of those in this teardown video.
The Technophone came to us from Great Britain by way of a former Ericsson engineer named Nils Mårtensson. It was able to achieve its relatively small stature using a surface-mount PCB, which was a cutting-edge manufacturing process for the time. Not only did it use surface-mount components and boards, but the PCB itself has 12 layers and two sides and hosts two custom Technophone chips. The phone is relatively modular as well, with the screen, battery pack, and other components capable of easily disconnecting from the main board. Continue reading “A Mobile Phone From 1985”→
You’ve got a machine hooked up to the Internet via a shiny new cellular modem, which you plan to administer remotely. You do a quick check on the external IP, and try and log in from another PC. Try as you might, SSH simply won’t connect. What gives?
The reality of the modern internet is that most clients no longer get their own unique IPv4 address. There simply aren’t enough to go around anymore. Instead, most telecommunications operators use Carrier Grade Network Address Translation which allows a single external address to be shared by many customers. This can get in the way of direct connection attempts from the outside world. Even if that’s not the case, most cellular operators tend to block inbound connections by default. However, there is a way around this quandary – using a VPN. Continue reading “Basics Of Remote Cellular Access: Connecting Via VPN”→