[Ben Krasnow] Gasses MEMS Chips, For Science

Why in the world does helium kill iPhones and other members of the Apple ecosystem? Enquiring minds want to know, and [Ben Krasnow] has obliged with an investigation of the culprit: the MEMS oscillator. (YouTube, embedded below.)

When we first heard about this, courtesy in part via a Hackaday post on MRI-killed iPhones, we couldn’t imagine how poisoning a micro-electromechanical system (MEMS) part could kill a phone. We’d always associated MEMS with accelerometers and gyros, important sensors in the smartphone suite, but hardly essential. It turns out there’s another MEMS component in many Apple products: an SiT 1532 oscillator, a tiny replacement for quartz crystal oscillators.

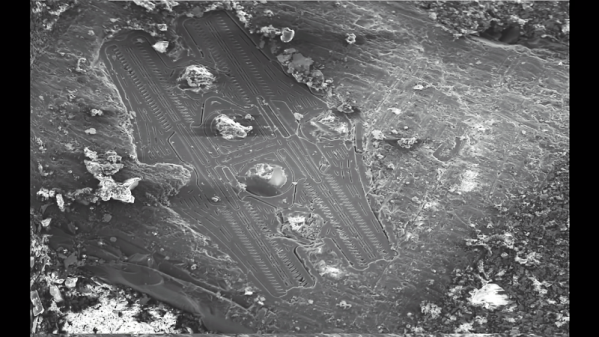
[Ben] got a few from DigiKey and put them through some tests in a DIY gas chamber. He found that a partial pressure of helium as low as 2 kPa, or just 2% of atmospheric pressure, can kill the oscillator. To understand why, and because [Ben] has a scanning electron microscope, he lapped down some spare MEMS oscillators to expose their intricate innards. His SEM images are stunning but perplexing, raising questions about how such things could be made which he also addresses.

The bottom line: helium poisons MEMS oscillators in low enough concentrations that the original MRI story is plausible. As a bonus, we now understand MEMS devices a bit better, and have one more reason never to own an iPhone.

Continue reading “[Ben Krasnow] Gasses MEMS Chips, For Science” →
Of Roach Killer And Rust Remover: Sam Zeloof’s Garage-Made Chips

A normal life in hacking, if there is such a thing, seems to follow a predictable trajectory, at least in terms of the physical space it occupies. We generally start small, working on a few simple projects on the kitchen table, or if we start young enough, perhaps on a desk in our childhood bedroom. Time passes, our skills increase, and with them the need for space. Soon we’re claiming an unused room or a corner of the basement. Skills build on skills, gear accumulates, and before you know it, the garage is no longer a place for cars but a place for pushing back the darkness of our own ignorance and expanding our horizons into parts unknown.

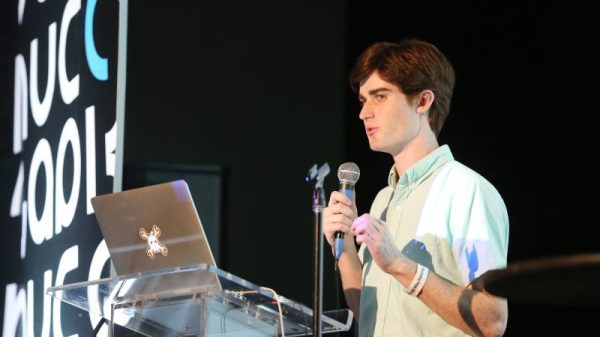
It appears that Sam Zeloof’s annexation of the family garage occurred fairly early in life, and to a level that’s hard to comprehend. Sam seems to have caught the hacking bug early, and by the time high school rolled around, he was building out a remarkably well-equipped semiconductor fabrication lab at home. Sam has been posting his progress regularly on his own blog and on Twitter, and he dropped by the 2018 Superconference to give everyone a lesson on semiconductor physics and how he became the first hobbyist to produce an integrated circuit using lithographic processes.

Continue reading “Of Roach Killer And Rust Remover: Sam Zeloof’s Garage-Made Chips” →

How The Xbox Was Hacked

The millennium: a term that few had any use for before 1999, yet seemingly overnight it was everywhere. The turning of the millenium permeated every facet of pop culture. Unconventional popstars like Moby supplied electronica to the mainstream airwaves while audiences contemplated whether computers were the true enemy after seeing The Matrix. We were torn between anxiety — the impending Y2K bug bringing the end of civilization that Prince prophesied — and anticipation: the forthcoming release of the PlayStation 2.

Sony was poised to take control of the videogame console market once again. They had already sold more units of the original PlayStation than all of their competition combined. Their heavy cloud of influence over gamers meant that the next generation of games wasn’t going to start in until the PS2 was on store shelves. On the tail of Sony announcing the technical specs on their machine, rumors of a new competitor entering the “console wars” began to spread. That new competitor was Microsoft, an American company playing in a Japanese company’s game.
Continue reading “How The Xbox Was Hacked” →

Hack My House: Opening Raspberry Pi To The Internet, But Not The Whole World

If you’ve followed along with our series so far, you know we’ve set up a network of Raspberry Pis that PXE boot off a central server, and then used Zoneminder to run a network of IP cameras. Now that some useful services are running in our smart house, how do we access those services when away from home, and how do we keep the rest of the world from spying on our cameras?

Before we get to VPNs and port forwarding, there is a more fundamental issue: Do you trust your devices? What exactly is the firmware on those cheap cameras really doing? You could use Wireshark and a smart switch with port mirroring to audit the camera’s traffic. How much traffic would you need to inspect to feel confident the camera never sends your data off somewhere else?

Thankfully, there’s a better way. One of the major features of surveillance software like Zoneminder is that it aggregates the feeds from the cameras. This process also has the effect of proxying the video feeds: We don’t connect directly to the cameras in order to view them, we connect to the surveillance software. If you don’t completely trust those cameras, then don’t give them internet access. You can make the cameras a physically separate network, only connected to the surveillance machine, or just set their IP addresses manually, and don’t fill in the default route or DNS. Whichever way you set it up, the goal is the same: let your surveillance software talk to the cameras, but don’t let the cameras talk to the outside world.

Edit: As has been pointed out in the comments, leaving off a default route is significantly less effective than separate networks. A truly malicious peice of hardware could easily probe for the gateway.

This idea applies to more than cameras. Any device that doesn’t need internet access to function, can be isolated in this way. While this could be considered paranoia, I consider it simple good practice. Join me after the break to discuss port forwarding vs. VPNs.

Continue reading “Hack My House: Opening Raspberry Pi To The Internet, But Not The Whole World” →

Mechanisms: Lead Screws And Ball Screws

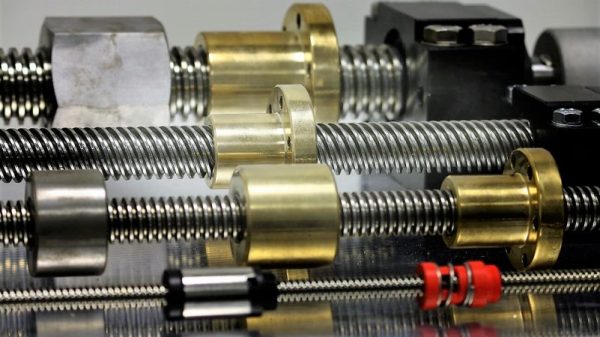
Translating rotary motion to linear motion is a basic part of mechatronic design. Take a look at the nearest 3D-printer or CNC router — at least the Cartesian variety — and you’ll see some mechanism that converts the rotation of the the motor shafts into the smooth linear motion needed for each axis.

Hobby-grade machines are as likely as not to use pulleys and timing belts to achieve this translation, and that generally meets the needs of the machine. But in some machines, the stretchiness of a belt won’t cut it, and the designer may turn to some variety of screw drive to do the job.

Continue reading “Mechanisms: Lead Screws And Ball Screws” →

Alice Evans: Brucellosis, Or Why We Pasteurize Milk

It’s easy to forget how much illness and death was caused by our food and drink just one hundred years ago. Our modern food systems, backed by sound research and decent regulation, have elevated food safety to the point where outbreaks of illness are big news. If you get sick from a burger, or a nice tall glass of milk, it’s no longer a mystery what happened. Instead we ask why, and “who screwed up?”

In the early 20th century though, many food-borne illnesses were still a mystery, and microbiology was a scientific endeavor that was just getting started. Alice Catherine Evans was an unlikely figure to make a dent in this world at the time, but through her research at the United States Department of Agriculture’s (USDA), and later at the Hygienic Laboratory (now the National Institute of Health) she had a huge impact on the field of bacteriology, the dairy industry, and consumer safety. Continue reading “Alice Evans: Brucellosis, Or Why We Pasteurize Milk” →

Hello, And Please Don’t Hang Up: The Scourge Of Robocalls

Over the last few months, I’ve noticed extra calls coming in from local numbers, and if you live in the US, I suspect maybe you have too. These calls are either just dead air, or recordings that start with “Please don’t hang up.” Out of curiosity, I’ve called back on the number the call claims to be from. Each time, the message is that this number has been disconnected and is no longer in service. This sounds like the plot of a budget horror movie, how am I being called from a disconnected number? Rather than a phantom in the wires, this is robocalling, combined with caller ID spoofing.

Continue reading “Hello, And Please Don’t Hang Up: The Scourge Of Robocalls” →