Linux Fu: Easier File Watching

In an earlier installment of Linux Fu, I mentioned how you can use inotifywait to efficiently watch for file system changes. The comments had a lot of alternative ways to do the same job, which is great. But there was one very easy-to-use tool that didn’t show up, so I wanted to talk about it. That tool is entr. It isn’t as versatile, but it is easy to use and covers a lot of common use cases where you want some action to occur when a file changes.

Continue reading “Linux Fu: Easier File Watching” →

AI On Raspberry Pi With The Intel Neural Compute Stick

I’ve always been fascinated by AI and machine learning. Google TensorFlow offers tutorials and has been on my ‘to-learn’ list since it was first released, although I always seem to neglect it in favor of the shiniest new embedded platform.

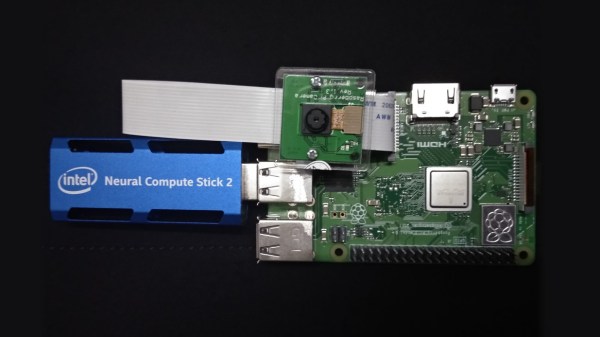
Last July, I took note when Intel released the Neural Compute Stick. It looked like an oversized USB stick, and acted as an accelerator for local AI applications, especially machine vision. I thought it was a pretty neat idea: it allowed me to test out AI applications on embedded systems at a power cost of about 1W. It requires pre-trained models, but there are enough of them available now to do some interesting things.

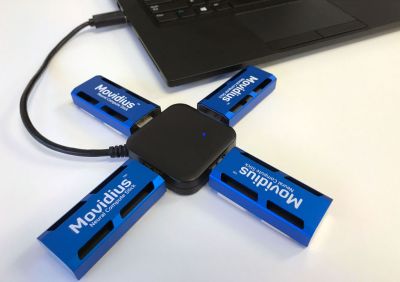
You can add a few of them in a hub for parallel tasks. Image credit Intel Corporation.

I wasn’t convinced I would get great performance out of it, and forgot about it until last November when they released an improved version. Unambiguously named the ‘Neural Compute Stick 2’ (NCS2), it was reasonably priced and promised a 6-8x performance increase over the last model, so I decided to give it a try to see how well it worked.


I took a few days off work around Christmas to set up Intel’s OpenVino Toolkit on my laptop. The installation script provided by Intel wasn’t particularly user-friendly, but it worked well enough and included several example applications I could use to test performance. I found that face detection was possible with my webcam in near real-time (something like 19 FPS), and pose detection at about 3 FPS. So in accordance with the holiday spirit, it knows when I am sleeping, and knows when I’m awake.

That was promising, but the NCS2 was marketed as allowing AI processing on edge computing devices. I set about installing it on the Raspberry Pi 3 Model B+ and compiling the application samples to see if it worked better than previous methods. This turned out to be more difficult than I expected, and the main goal of this article is to share the process I followed and save some of you a little frustration.

Continue reading “AI On Raspberry Pi With The Intel Neural Compute Stick” →

AI Patent Trolls Now On The Job For Drug Companies

Love it or loathe it, the pharmaceutical industry is really good at protecting its intellectual property. Drug companies pour billions into discovering new drugs and bringing them to market, and they do whatever it takes to make sure they have exclusive positions to profit from their innovations for as long a possible. Patent applications are meticulously crafted to keep the competition at bay for as long as possible, which is why it often takes ages for cheaper generic versions of blockbuster medications to hit the market, to the chagrin of patients, insurers, and policymakers alike.

Drug companies now appear poised to benefit from the artificial intelligence revolution to solidify their patent positions even further. New computational methods are being employed to not only plan the synthesis of new drugs, but to also find alternative pathways to the same end product that might present a patent loophole. AI just might change the face of drug development in the near future, and not necessarily for the better.

Continue reading “AI Patent Trolls Now On The Job For Drug Companies” →

How To Make Your Own Springs For Extruded Rail T-Nuts

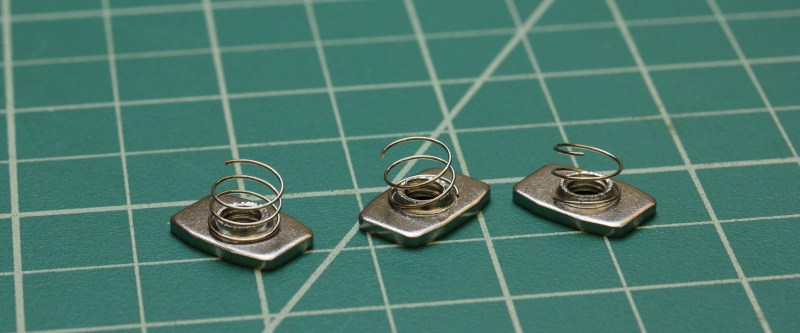
Open-Source Extruded Profile systems are a mature breed these days. With Openbuilds, Makerslide, and Openbeam, we’ve got plenty of systems to choose from; and Amazon and Alibaba are coming in strong with lots of generic interchangeable parts. These open-source framing systems have borrowed tricks from some decades-old industry players like Rexroth and 80/20. But from all they’ve gleaned, there’s still one trick they haven’t snagged yet: affordable springloaded T-nuts.

I’ve discussed a few tricks when working with these systems before, and Roger Cheng came up with a 3D printed technique for working with T-nuts. But today I’ll take another step and show you how to make our own springs for VSlot rail nuts.

Continue reading “How To Make Your Own Springs For Extruded Rail T-Nuts” →

Don’t Toss That Bulb, It Knows Your Password

Whether it was here on Hackaday or elsewhere on the Internet, you’ve surely heard more than a few cautionary tales about the “Internet of Things” by now. As it turns out, giving every gadget you own access to your personal information and Internet connection can lead to unintended consequences. Who knew, right? But if you need yet another example of why trusting your home appliances with your secrets is potentially a bad idea, [Limited Results] is here to make sure you spend the next few hours doubting your recent tech purchases.

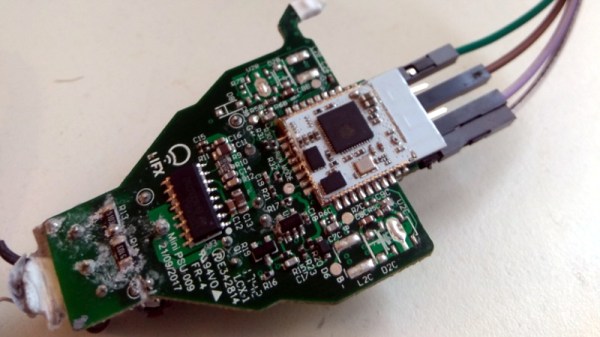
In a series of posts on the [Limited Results] blog, low-cost “smart” bulbs are cracked open and investigated to see what kind of knowledge they’ve managed to collect about their owners. Not only was it discovered that bulbs manufactured by Xiaomi, LIFX, and Tuya stored the WiFi SSID and encryption key in plain-text, but that recovering said information from the bulbs was actually quite simple. So next time one of those cheapo smart bulb starts flickering, you might want to take a hammer to it before tossing it in the trash can; you never know where it, and the knowledge it has of your network, might end up.
Regardless of the manufacturer of the bulb, the process to get one of these devices on your network is more or less the same. An application on your smartphone connects to the bulb and provides it with the network SSID and encryption key. The bulb then disconnects from the phone and reconnects to your home network with the new information. It’s a process that at this point we’re all probably familiar with, and there’s nothing inherently wrong with it.

The trouble comes when the bulb needs to store the connection information it was provided. Rather than obfuscating it in some way, the SSID and encryption key are simply stored in plain-text on the bulb’s WiFi module. Recovering that information is just a process of finding the correct traces on the bulb’s PCB (often there are test points which make this very easy), and dumping the chip’s contents to the computer for analysis.

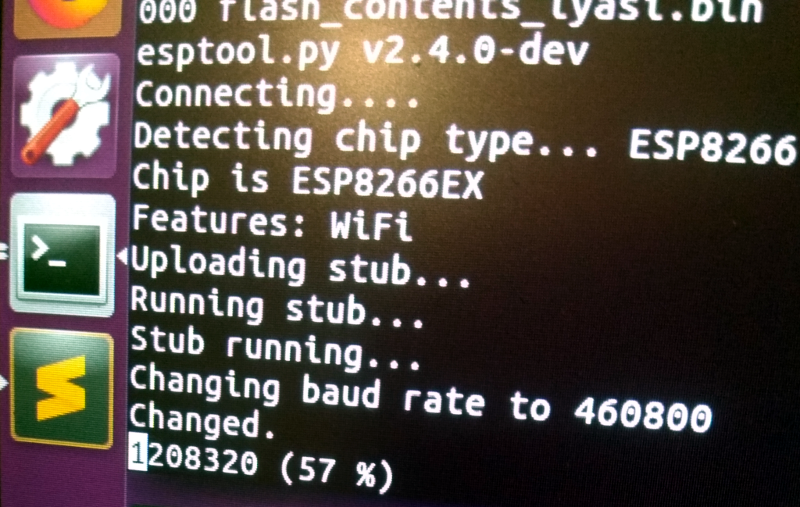
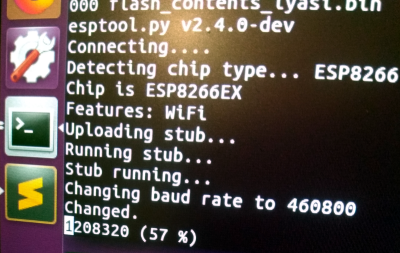
It’s not uncommon for smart bulbs like these to use the ESP8266 or ESP32, and [Limited Results] found that to be the case here. With the wealth of information and software available for these very popular WiFi modules, dumping the firmware binary was no problem. Once the binary was in hand, a little snooping around with a hex editor was all it took to identify the network login information. The firmware dumps also contained information such as the unique hardware IDs used by the “cloud” platforms the bulbs connect to, and in at least one case, the root certificate and RSA private key were found.

On the plus side, being able to buy cheap smart devices that are running easily hackable modules like the ESP makes it easier for us to create custom firmware for them. Hopefully the community can come up with slightly less suspect software, but really just keeping the things from connecting to anything outside the local network would be a step in the right direction.

(Some days later…)

[Limited Results] had hinted to us that he had previously disclosed some vulnerabilities to the bulb’s maker, but that until they fixed them, he didn’t want to make them public. They’re fixed now, and it appears that the bulbs were sending everything over the network unencrypted — your data, OTA firmware upgrades, everything.  They’re using TLS now, so good job [Limited Results]! If you’re running an old version of their lightbulbs, you might have a look.

On WiFi credentials, we were told: “In the case where sensitive information in the flash memory wasn’t encrypted, the new version will include encrypted storage processing, and the customer will be able to select this version of the security chips, which can effectively avoid future security problems.” Argue about what that actually means in the comments.

The Cyborgs Among Us: Exoskeletons Go Mainstream

Every technological advancement seems to have a sharp inflection point, a time before which it seems like any early adopters are considered kooks, but beyond which the device or service quickly becomes so mainstream that non-adopters become the kooky ones. Take cell phones, for example – I clearly remember a news report back in the 1990s about some manufacturers crazy idea to put a digital camera in a phone. Seemingly minutes later, you couldn’t buy a phone without a camera.

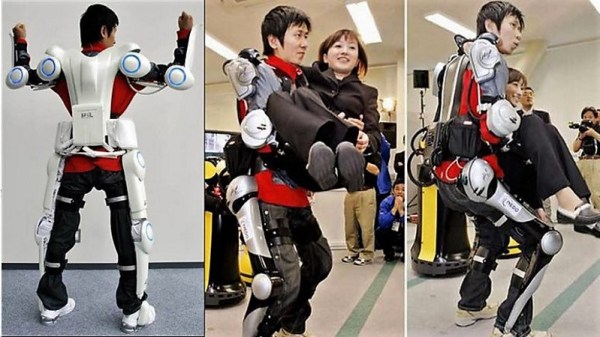
It seems like we may be nearing a similar inflection point with a technology far more complex and potentially far more life-altering than cameras in cell phones: powered exoskeletons. With increasing numbers of news stories covering advancements in exoskeletal assistants for the elderly, therapeutic applications for those suffering from spinal cord injuries and neurodegenerative diseases, and penetration into the workplace – including the battlefield – as amplifiers of human effort, it’s worth taking a look at where we are with exoskeletons before seeing someone using one in public becomes so commonplace as to go unnoticed.

Continue reading “The Cyborgs Among Us: Exoskeletons Go Mainstream” →

Drone Sightings, A New British Comedy Soap Opera

There’s a new soap opera that I can’t stop watching. Actually, I wish I could change the channel but this is unfortunately happening in real life. It’s likely the ups and downs of drone sightings would be too far fetched for fiction anyway.

If you aren’t British, maybe you will know a little of our culture through the medium of television. We don’t all live in stately homes like Downton Abbey of course, instead we’re closer to the sometimes comedic sets, bad lighting, and ridiculously complicated lives of the residents of Coronation Street or of Albert Square in Eastenders that you may have flashed past late at night on a high-number channel.

Our new comedy soap lacks the regional accents of Emmerdale or Hollyoaks, but has no less of the farce about it. Here at Hackaday we’ve brought you news of the UK’s peculiar habit of bad reporting and shoddy investigation of questionable drone sightings several times over the last year or two. Most recently we covered a series of events before Christmas that closed Gatwick, London’s second airport for several days over what turned out to be nothing of substance.

Unfortunately it didn’t end there. We’re back once more to catch up with the latest events down on the tarmac, and come away with a fresh set of reasonable questions unanswered by the popular coverage of the matter.

Continue reading “Drone Sightings, A New British Comedy Soap Opera” →