Malicious Component Found On Server Motherboards Supplied To Numerous Companies

This morning Bloomberg is reporting a bombshell for hardware security. Companies like Amazon and Apple have found a malicious chip on their server motherboards. These are not counterfeit chips. They are not part of the motherboard design. These were added by the factory at the time of manufacture. The chip was placed among other signal conditioning components and is incredibly hard to spot as the nature of these motherboards includes hundreds of minuscule components.

Though Amazon and Apple have denied it, according to Bloomberg, a private security contractor in Canada found the hidden chip on server motherboards. Elemental Technologies, acquired by Amazon in 2015 for its video and graphics processing hardware, subcontracted Supermicro (Super Micro Computer, Inc.) to manufacture their server motherboards in China. It is unknown how many of the company’s products have this type of malicious hardware in them, equipment from Elemental Technologies has been supplied to the likes of government contractors as well as major banks and even reportedly used in the CIA’s drone operations.

How the Hack Works

The attacks work with the small chip being implanted onto the motherboard disguised as signal couplers. It is unclear how the chip gains access to the peripherals such as memory (as reported by Bloomberg) but it is possible it has something to do with accessing the bus. The chip controls some data lines on the motherboard that likely provide an attack vector for the baseboard management controller (BMC).

Hackaday spoke with Joe FitzPatrick (a well known hardware security guru who was quoted in the Bloomberg article). He finds this reported attack as a very believable approach to compromising servers. His take on the BMC is that it’s usually an ARM processor running an ancient version of Linux that has control over the major parts of the server. Any known vulnerability in the BMC would be an attack surface for the custom chip.

Data centers house thousands of individual servers that see no physical interaction from humans once installed. The BMC lets administrators control the servers remotely to reboot malfunctioning equipment among other administrative tasks. If this malicious chip can take control of the BMC, then it can provide remote access to whomever installed the chip. Reported investigations have revealed the hack in action with brief check-in communications from these chips though it’s difficult to say if they had already served their purpose or were being saved for a future date.

What Now?

Adding hardware to a design is fundamentally different than software-based hacking: it leaves physical evidence behind. Bloomberg reports on US government efforts to investigate the supply chain attached to these parts. It is worth noting though that the article doesn’t include any named sources while pointing the finger at China’s People’s Liberation Army.

The solution is not a simple one if servers with this malicious chip were already out in the field. Even if you know a motherboard has the additional component, finding it is not easy. Bloomberg also has unconfirmed reports that the next-generation of this attack places the malicious component between layers of the circuit board. If true, an x-ray would be required to spot the additional part.

A true solution for high-security applications will require specialized means of making sure that the resulting product is not altered in any way. This hack takes things to a whole new level and calls into question how we validate hardware that runs our networks.

Update: We changed the penultimate paragraph to include the word if: “…simple one if servers with…” as it has not been independently verified that servers were actually out in the field and companies have denied Bloomberg’s reporting that they were.

[Note: Image is a generic photo and not the actual hardware]
The Modular Connector And How It Got That Way

They adorn the ends of Cat5 network patch cables and the flat satin cables that come with all-in-one printers that we generally either toss in the scrap bin or throw away altogether. The blocky rectangular plugs, molded of clear plastic and holding gold-plated contacts, are known broadly as modular connectors. They and their socket counterparts have become ubiquitous components of the connected world over the last half-century or so, and unsurprisingly they had their start where so many other innovations began: from the need to manage the growth of the telephone network and reduce costs. Here’s how the modular connector got that way.

Continue reading “The Modular Connector And How It Got That Way” →

Bitcoin’s Double Spending Flaw Was Hush-Hush During Rollout

For a little while it was possible to spend Bitcoin twice. Think of it like a coin on a string, you put it into the vending machine to get a delicious snack, but if you pull the string quickly enough you could spend it again on some soda too. Except this coin is worth something like eighty-grand.

On September 20, the full details of the latest fix for the Bitcoin Core were published. This information came two days after the fix was actually released. Two vulnerabilities were involved; a Denial of Service vulnerability and a critical inflation vulnerability, both covered in CVE-2018-17144. These were originally reported to several developers working on Bitcoin Core, as well as projects supporting other cryptocurrencies, including ABC and Unlimited.

Let’s take a look at how this worked, and how the network was patched (while being kept quiet) to close up this vulnerability.

Continue reading “Bitcoin’s Double Spending Flaw Was Hush-Hush During Rollout” →

Remember When Blockbuster Video Tried Burning Game Cartridges On Demand?

By the onset of the 1990s one thing was clear, the future was digital. Analog format sales for music were down, CD sales were up; and it was evident, at least in the US, that people were bringing more computing devices into their homes. At the beginning of the decade, roughly 1 in 3 American households had a Nintendo Entertainment System in them, according to this Good Morning America segment.

With all those consoles out there, every shopping season became a contest of “who could wait in line the longest” to pickup the newest titles. This left last minute shoppers resorting to taking a rain check or return home empty handed. Things didn’t have to be this way. The digital world had emerged and physical media just needed to catch up. It would take an unlikely alliance of two disparate companies for others to open their minds.

Continue reading “Remember When Blockbuster Video Tried Burning Game Cartridges On Demand?” →

Laser Noob: Getting Started With The K40 Laser

Why spend thousands on a laser cutter/engraver when you can spend as little as $350 shipped to your door? Sure it’s not as nice as those fancy domestic machines, but the plucky K40 is the little laser that can. Just head on down to Al’s Laser Emporium and pick one up.  Yes, it sounds like a used car dealership ad, but how far is it from the truth? Read on to find out!

Laser cutting and engraving machines have been around for decades. Much like 3D printers, they were originally impossibly expensive for someone working at home. The closest you could get to a hobbyist laser was Epilog laser, which would still cost somewhere between $10,000 and $20,000 for a small laser system. A few companies made a go with the Epilog and did quite well – notably Adafruit used to offer laptop laser engraving services.

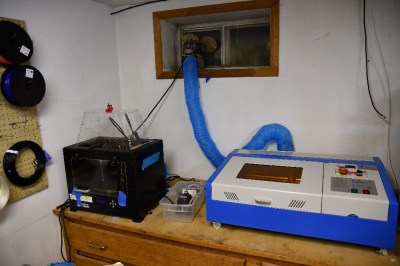
Over the last decade or so things have changed. China got involved, and suddenly there were cheap lasers on the market. Currently, there are several low-cost laser models available in various power levels. The most popular is the smallest – a 40-watt model, dubbed the K40. There are numerous manufacturers and there have been many versions over the years. They all look about the same though: A blue sheet metal box with the laser tube mounted along the back. The cutting compartment is on the left and the electronics are on the right. Earlier versions came with Moshidraw software and a parallel interface.
Continue reading “Laser Noob: Getting Started With The K40 Laser” →

Can You “Take Back” Open Source Code?

It seems a simple enough concept for anyone who’s spent some time hacking on open source code: once you release something as open source, it’s open for good. Sure the developer might decide that future versions of the project close up the source, it’s been known to happen occasionally, but what’s already out there publicly can never be recalled. The Internet doesn’t have a “Delete” button, and once you’ve published your source code and let potentially millions of people download it, there’s no putting the Genie back in the bottle.

But what happens if there are extenuating circumstances? What if the project turns into something you no longer want to be a part of? Perhaps you submitted your code to a project with a specific understanding of how it was to be used, and then the rules changed. Or maybe you’ve been personally banned from a project, and yet the maintainers of said project have no problem letting your sizable code contributions stick around even after you’ve been kicked to the curb?

Due to what some perceive as a forced change in the Linux Code of Conduct, these are the questions being asked by some of the developers of the world’s preeminent open source project. It’s a situation which the open source community has rarely had to deal with, and certainly never on a project of this magnitude.

Is it truly possible to “take back” source code submitted to a project that’s released under a free and open source license such as the GPL? If so, what are the ramifications? What happens if it’s determined that the literally billions of devices running the Linux kernel are doing so in violation of a single developer’s copyright? These questions are of grave importance to the Internet and arguably our way of life. But the answers aren’t as easy to come by as you might think.

Continue reading “Can You “Take Back” Open Source Code?” →

Building A Hardware Store Faraday Cage

Most Hackaday readers are no doubt familiar with the Faraday cage, at least in name, and nearly everyone owns one: if you’ve ever stood watching a bag of popcorn slowly revolve inside of a microwave, you’be seen Michael Faraday’s 1836 invention in action. Yet despite being such a well known device, the average hacker still doesn’t have one in their arsenal. But why?

It could be that there’s a certain mystique about Faraday cages, an assumption that their construction requires techniques or materials outside the realm of the home hacker. While it’s true that building a perfect Faraday cage for a given frequency involves math and careful attention to detail, putting together a simple model for general purpose use and experimentation turns out to be quick and easy.

As an exercise in minimalist hacking I recently built a basic Faraday cage out of materials sourced from Home Depot, and thought it would be interesting to not only describe its construction but give some ideas as to how one can put it to practical use in the home lab. While it’s hardly a perfect specimen, it clearly works, and it didn’t take anything that can’t be sourced locally pretty much anywhere in the world.

Continue reading “Building A Hardware Store Faraday Cage” →