I Ate A Robot Hamburger Before The Restaurant Went Out Of Business

The future is upon us and the robots will soon take over. Automated cars will put Uber drivers and cabbies alike out of work. Low-wage workers, like the people working behind the counter at McDonalds, will be replaced by burger-flipping robots. The entire operation of Spacely Space Sprockets, Inc. is run by a single man, pressing a single button, for four hours a day. This cartoon future is so fully automated that most people are unemployed, and all productive work is done by robots.

The first jobs to be replaced will be the first jobs teenagers get. These are low skill jobs, and when you think about low skill jobs (certainly not low-effort jobs, by the way), you think of flipping burgers. That’s where Creator comes in. They’re a culinary robotics company with a restaurant in San Francisco. They’ve been profiled by NPR, by Business Insider, and by CNBC. TechCrunch got a sneak preview proclaiming this as the future of the six dollar burger. It is a marvel of engineering prowess with a business model that I don’t think checks out. This is not the robot that will take your job, and I’m proud to say I ate a robot hamburger before the restaurant went out of business.

Continue reading “I Ate A Robot Hamburger Before The Restaurant Went Out Of Business” →

This Year’s Nobel Prizes Are Straight Out Of Science Fiction

In the 1966 science fiction movie Fantastic Voyage, medical personnel are shrunken to the size of microbes to enter a scientist’s body to perform brain surgery. Due to the work of this year’s winners of the Nobel Prize in Physics, laser tools now do work at this scale.

Arthur Ashkin won for his development of optical tweezers that use a laser to grip and manipulate objects as small a molecule. And Gérard Mourou and Donna Strickland won for coming up with a way to produce ultra-short laser pulses at a high-intensity, used now for performing millions of corrective laser eye surgeries every year.

Here is a look at these inventions, their inventors, and the applications which made them important enough to win a Nobel.

Continue reading “This Year’s Nobel Prizes Are Straight Out Of Science Fiction” →

Google Discovers Google+ Servers Are Still Running

Google is pulling the plug on their social network, Google+. Users still have the better part of a year to say their goodbyes, but if the fledgling social network was a ghost town before, news of its imminent shutdown isn’t likely to liven the place up. A quick check of the site as of this writing reveals many users are already posting their farewell messages, and while there’s some rallying behind petitions to keep the lights on, the majority realize that once Google has fallen out of love with a project there’s little chance of a reprieve.

To say that this is a surprise would be disingenuous. We’d wager a lot of you already thought it was gone, honestly. It’s no secret that Google’s attempt at a “Facebook Killer” was anything but, and while there was a group of dedicated users to be sure, it never attained anywhere near the success of its competition.

According to a blog post from Google, the network’s anemic user base isn’t the only reason they’ve decided to wind down the service. A previously undisclosed security vulnerability also hastened its demise, a revelation which will particularly sting those who joined for the privacy-first design Google touted. While this fairly transparent postmortem allows us to answer what ended Google’s grand experiment in social networking, there’s still one questions left unanswered. Where are the soon to be orphaned Google+ users supposed to go?

Continue reading “Google Discovers Google+ Servers Are Still Running” →

Hack My House: Running Raspberry Pi Without An SD Card

Many of us have experienced the pain that is a Raspberry Pi with a corrupted SD card. I suspect the erase-on-write nature of flash memory is responsible for much of the problem. Regardless of the cause, one solution is to use PXE booting with the Raspberry Pi 3. That’s a fancy way to say we’ll be booting the Raspberry Pi over the network, instead of from an SD card.

What does this have to do with Hacking My House? As I discussed last time, I’m using Raspberry Pi as Infrastructure by building them into the walls of every room in my house. You don’t want to drag out a ladder and screwdriver to swap out a misbehaving SD card, so booting over the network is a really good solution. I know I promised we’d discuss cabling and cameras. Think of this as a parenthetical article — we’ll talk about Ethernet and ZoneMinder next time.

So let’s dive in and see what the Preboot Execution Environment (PXE) is all about and how to use PXE with Raspberry Pi.

Continue reading “Hack My House: Running Raspberry Pi Without An SD Card” →

Will Drones And Planes Be Treated As Equals By FAA?

Soon, perhaps even by the time you read this, the rules for flying remote-controlled aircraft in the United States will be very different. The Federal Aviation Authority (FAA) is pushing hard to repeal Section 336, which states that small remote-controlled aircraft as used for hobby and educational purposes aren’t under FAA jurisdiction. Despite assurances that the FAA will work towards implementing waivers for hobbyists, critics worry that in the worst case the repeal of Section 336 might mean that remote control pilots and their craft may be held to the same standards as their human-carrying counterparts.

Section 336 has already been used to shoot down the FAA’s ill-conceived attempt to get RC pilots to register themselves and their craft, so it’s little surprise they’re eager to get rid of it. But they aren’t alone. The Commercial Drone Alliance, a non-profit association dedicated to supporting enterprise use of Unmanned Aerial Systems (UAS), expressed their support for repealing Section 336 in a June press release:

Basic ‘rules of the road’ are needed to manage all this new air traffic. That is why the Commercial Drone Alliance is today calling on Congress to repeal Section 336 of the FAA Modernization and Reform Act of 2012, and include new language in the 2018 FAA Reauthorization Act to enable the FAA to regulate UAS and the National Airspace in a common sense way.

With both the industry and the FAA both pushing lawmakers to revamp the rules governing small remote-controlled aircraft, things aren’t looking good for the hobbyists who operate them. It seems likely those among us with a penchant for airborne hacking will be forced to fall in line. But what happens then?

Continue reading “Will Drones And Planes Be Treated As Equals By FAA?” →

How Precise Is That Part? Know Your GD&T

How does a design go from the computer screen to something you hold in your hand? Not being able to fully answer this question is a huge risk in manufacturing because . One of the important tools engineers use to ensure success is Geometric Dimensioning and Tolerancing (GD&T).

A good technical drawing is essential for communicating your mechanical part designs to a manufacturer. Drafting, as a professional discipline, is all about creating technical drawings that are as unambiguous as possible, and that means defining features explicitly. The most basic implementation of that concept is dimensioning, where you state the distance or angle between features. A proper technical drawing will also include tolerances for those dimensions, and I recently explained how to avoid the pitfall of stacking those tolerances.

Dimensions and tolerances alone, however, don’t tell the complete story. On their own, they don’t specify how closely the geometric form of the manufactured part needs to adhere to your perfect, nominal representation. That’s what we’re going to dig into today with GD&T.

Continue reading “How Precise Is That Part? Know Your GD&T” →

Malicious Component Found On Server Motherboards Supplied To Numerous Companies

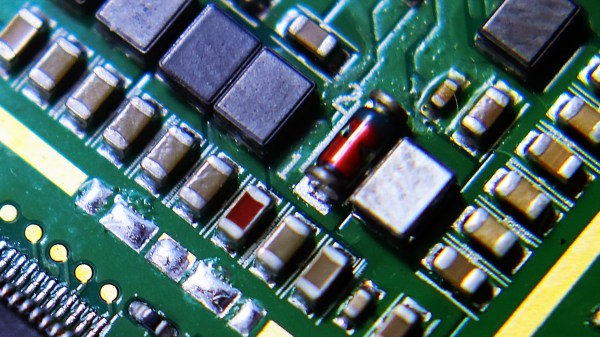
This morning Bloomberg is reporting a bombshell for hardware security. Companies like Amazon and Apple have found a malicious chip on their server motherboards. These are not counterfeit chips. They are not part of the motherboard design. These were added by the factory at the time of manufacture. The chip was placed among other signal conditioning components and is incredibly hard to spot as the nature of these motherboards includes hundreds of minuscule components.

Though Amazon and Apple have denied it, according to Bloomberg, a private security contractor in Canada found the hidden chip on server motherboards. Elemental Technologies, acquired by Amazon in 2015 for its video and graphics processing hardware, subcontracted Supermicro (Super Micro Computer, Inc.) to manufacture their server motherboards in China. It is unknown how many of the company’s products have this type of malicious hardware in them, equipment from Elemental Technologies has been supplied to the likes of government contractors as well as major banks and even reportedly used in the CIA’s drone operations.

How the Hack Works

The attacks work with the small chip being implanted onto the motherboard disguised as signal couplers. It is unclear how the chip gains access to the peripherals such as memory (as reported by Bloomberg) but it is possible it has something to do with accessing the bus. The chip controls some data lines on the motherboard that likely provide an attack vector for the baseboard management controller (BMC).

Hackaday spoke with Joe FitzPatrick (a well known hardware security guru who was quoted in the Bloomberg article). He finds this reported attack as a very believable approach to compromising servers. His take on the BMC is that it’s usually an ARM processor running an ancient version of Linux that has control over the major parts of the server. Any known vulnerability in the BMC would be an attack surface for the custom chip.

Data centers house thousands of individual servers that see no physical interaction from humans once installed. The BMC lets administrators control the servers remotely to reboot malfunctioning equipment among other administrative tasks. If this malicious chip can take control of the BMC, then it can provide remote access to whomever installed the chip. Reported investigations have revealed the hack in action with brief check-in communications from these chips though it’s difficult to say if they had already served their purpose or were being saved for a future date.

What Now?

Adding hardware to a design is fundamentally different than software-based hacking: it leaves physical evidence behind. Bloomberg reports on US government efforts to investigate the supply chain attached to these parts. It is worth noting though that the article doesn’t include any named sources while pointing the finger at China’s People’s Liberation Army.

The solution is not a simple one if servers with this malicious chip were already out in the field. Even if you know a motherboard has the additional component, finding it is not easy. Bloomberg also has unconfirmed reports that the next-generation of this attack places the malicious component between layers of the circuit board. If true, an x-ray would be required to spot the additional part.

A true solution for high-security applications will require specialized means of making sure that the resulting product is not altered in any way. This hack takes things to a whole new level and calls into question how we validate hardware that runs our networks.

Update: We changed the penultimate paragraph to include the word if: “…simple one if servers with…” as it has not been independently verified that servers were actually out in the field and companies have denied Bloomberg’s reporting that they were.

[Note: Image is a generic photo and not the actual hardware]