This Week In Security: Chrome Bugs And Non-bugs, Kr00k, And Letsencrypt

Google Chrome minted a new release to fix a trio of bugs on Monday, with exploit code already in the wild for one of them. The first two bugs don’t have much information published yet. They are an integer-overflow problem in Unicode internationalization, and a memory access issue in streams. The third issue, type confusion in V8, was also fixed quietly, but a team at Exodus Intel took the time to look at the patches and figure out what the problem was.

The actual vulnerability dives into some exotic Javascript techniques, but to put it simply, it’s possible to change a data-type without V8 noticing. This allows malicious code to write into the header area of the attacked variable. The stack, now corrupted, can be manipulated to the point of arbitrary code execution. The researchers make the point that even with Google’s fast-paced release schedule, a determined attacker could have several days of virtual zero-day exploitation of a bug mined from code changes. Story via The Register.

The Chrome Problem that Wasn’t

A second Chrome story came across my desk this week: Chrome 80 introduces a new feature, ScrollToTextFragment. This useful new feature allows you to embed a string of text in a URL, and when loading that address, Chrome will scroll the page to make that text visible. For certain use cases, this is an invaluable feature. Need to highlight a specific bit of text in a big document online?

The following bookmarklet code by [Paul Kinlan] is the easy way to start using this feature. Paste this code into the URL of a bookmark, put it on the bookmark bar, highlight some text in a webpage, and then run the bookmarklet. It should open a new tab with the new URL, ready to use or send to someone.

javascript:(function()%7Bconst%20selectedText%20%3D%20getSelection().toString()%3Bconst%20newUrl%20%3D%20new%20URL(location)%3BnewUrl.hash%20%3D%20%60%3A~%3Atext%3D%24%7BencodeURIComponent(selectedText)%7D%60%3Bwindow.open(newUrl)%7D)()

Since we’re talking about it in the security column, there must be more to the story. A privacy guru at Brave, [Peter Snyder], raised concerns about privacy implications of the feature. His argument has been repeated and misrepresented in a few places. What argument was he making? Simply put, that it’s not normal user behavior to immediately scroll to an exact position on the page. Because modern web pages and browsers do things like deferred loading of images, it could be possible to infer where in the page the link was pointing. He gives the example of a corporate network where DNS is monitored. This isn’t suggesting that the entire URL is leaked over DNS, but rather that DNS can indicate when individual components of a page are loaded, particularly when they are embedded images from other sites.

While this concern isn’t nonsensical, it seems to me to be a very weak argument that is being over-hyped in the press.

Whatsapp Groups Searchable on Google
It’s not new for search engines to index things that weren’t intended to be public. There is a bit of mystery surrounding how Google finds URLs to index, and StackExchange is full of plenty of examples of webadmins scratching their heads at their non-public folders showing up in a Google search.

That said, a story made the rounds in the last few days, that WhatsApp and Telegram group invites are being indexed by Google. So far, the official word is that all the indexed links must have been shared publicly, and Google simply picked them up from where they were publicly posted.

It appears that WhatsApp has begun marking chat invitation links as “noindex”, which is a polite way to ask search engines to ignore the link.

If it’s shown that links are getting indexed without being posted publicly online, then we have a much bigger story. Otherwise, everything is working as expected.

Letsencrypt Makes Attacks Harder

Letsencrypt has rolled out an invisible change to their validation process that makes a traffic redirection attack much harder. The new feature, Multi-Perspective Validation, means that when you verify your domain ownership, Letsencrypt will test that verification from multiple geographic regions. It might be possible to spoof ownership of a domain through a BGP attack, but that attack would be much harder to pull off against traffic originating from another country, or multiple countries simultaneously. Letsencrypt is currently using different regions of a single cloud, but plans to further diversify and use multiple cloud providers for even stronger validation.

Kr00k

Brought to us by the researchers at Eset, Krook (PDF) is a simple flaw in certain wireless chips. So far, the flaw seems to be limited to WPA2 traffic sent by Broadcom and Cypress chips. They discovered Kr00k while doing some followup research on KRACK.
Let’s talk about WPA2 for a moment. WPA2 has a 4-way handshake process that securely confirms that both parties have the shared key, and then establishes a shared Temporal Key, also known as a session key. This key is private between the two devices that performed the handshake, meaning that other devices on the same wireless network can’t sniff traffic sent by other devices.

When a device disconnects, or disassociates, that session key is reset to all 0s, and no packets should be sent until another handshake is performed. Here’s the bug: The packets already in the output buffer are still sent, but are encrypted with the zeroed key, making them trivially decrypted. As it’s simple to trigger deauthentication events, an attacker can get a sampling of in-the-clear packets. The ubiquity of TLS is a saving grace here, but any unencrypted traffic is vulnerable. Eset informed vendors about the flaw in 2019, and at least some devices have been patched.

Exchange

Microsoft Exchange got a security patch this past Tuesday that addressed a pair of bugs that together resulted in a remote code execution vulnerability. The first bug was an encryption key that is generated on Exchange server installation. That generation seemed to lack a good source of entropy, as apparently every Exchange install uses the the exact same key.

The second half of this bug is a de-serialization problem, where an encrypted payload can contain a command to run. Because the encryption key is known, any user can access the vulnerable endpoint. The process of exploitation is so trivial, be sure to patch your server right away.

TODO: Remove Vulnerabilities

This one is just humorous. An Intel virtualization feature appears to have been pushed into the Linux kernel before it was finished. Know what unfinished code tends to contain? Bugs and vulnerabilities. CVE-2020-2732, in this case. It’s unclear how exactly an exploit would work, but the essence is that a virtual guest is allowed to manipulate system state in unintended ways.
Astra Readies Secretive Silicon Valley Rocket; Firm Exits Stealth Mode, Plans Test Launch

After the end of the Second World War the United States and the Soviet Union started working feverishly to perfect the rocket technology that the Germans developed for the V-2 program. This launched the Space Race, which thankfully for everyone involved, ended with boot prints on the Moon instead of craters in Moscow and DC. Since then, global tensions have eased considerably. Today people wait for rocket launches with excitement rather than fear.

That being said, it would be naive to think that the military isn’t still interested in pushing the state-of-the-art forward. Even in times of relative peace, there’s a need for defensive weapons and reconnaissance. Which is exactly why the Defense Advanced Research Projects Agency (DARPA) has been soliciting companies to develop a small and inexpensive launch vehicle that can put lightweight payloads into Earth orbit on very short notice. After all, you never know when a precisely placed spy satellite can make the difference between a simple misunderstanding and all-out nuclear war.

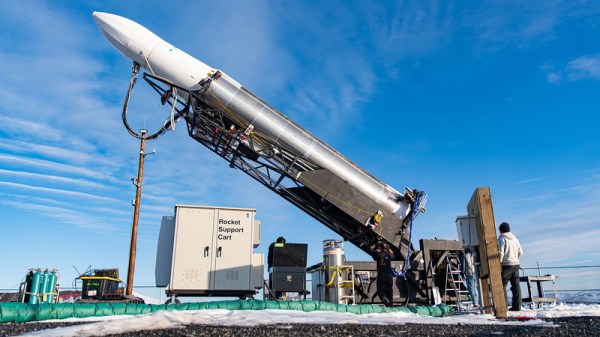
More than 50 companies originally took up DARPA’s “Launch Challenge”, but only a handful made it through to the final selection. Virgin Orbit entered their air-launched booster into the competition, but ended up dropping out of contention to focus on getting ready for commercial operations. Vector Launch entered their sleek 12 meter long rocket into the competition, but despite a successful sub-orbital test flight of the booster, the company ended up going bankrupt at the end of 2019. In the end, the field was whittled down to just a single competitor: a relatively unknown Silicon Valley company named Astra.

Should the company accomplish all of the goals outlined by DARPA, including launching two rockets in quick succession from different launch pads, Astra stands to win a total of $12 million; money which will no doubt help the company get their booster ready to enter commercial service. Rumored to be one of the cheapest orbital rockets ever built and small enough to fit inside of a shipping container, it should prove to be an interesting addition to the highly competitive “smallsat” launcher market.

Continue reading “Astra Readies Secretive Silicon Valley Rocket; Firm Exits Stealth Mode, Plans Test Launch”

Hands-On: Smarty Cat Is Junior’s First Slide Rule

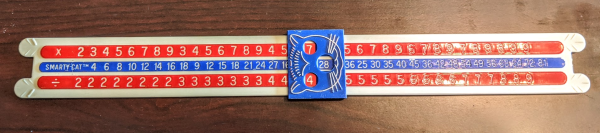
You may remember that I collect slide rules. If you don’t, it probably doesn’t surprise you. I have a large number of what I think of as normal slide rules. I also have the less common circular and cylindrical slide rules. But I recently picked up a real oddity that I had to share: the Smarty Cat. It isn’t exactly a slide rule but it sort of is if you stretch the definition a bit.

Real Slide Rules

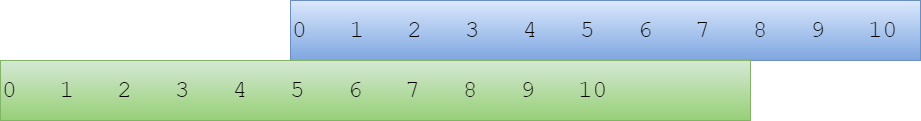
A regular slide rule takes advantage of the fact that you can multiply and divide by adding logarithms. Imagine having two rulers marked in inches or centimeters — it doesn’t matter (see the adjoining image). Suppose you want to add 5 and 3. You count off 5 marks on one ruler and line it with up the zero inch mark on the other ruler. Now you count off 3 marks on the second ruler and that position on the first ruler will indicate the result. Here it lines up with the 8 mark, which is, of course, the correct answer.

That’s a simple addition. But if you can convert your numbers into logarithms, add the logarithms, and then back out to a regular number, you can multiply.

Continue reading “Hands-On: Smarty Cat Is Junior’s First Slide Rule”

Recording Video In The Era Of CRTs: The Video Camera Tube

We have all watched videos of concerts and events dating back to the 1950s, but probably never really wondered how this was done. After all, recording moving images on film had been done since the late 19th century. Surely this is how it continued to be done until the invention of CCD image sensors in the 1980s? Nope.

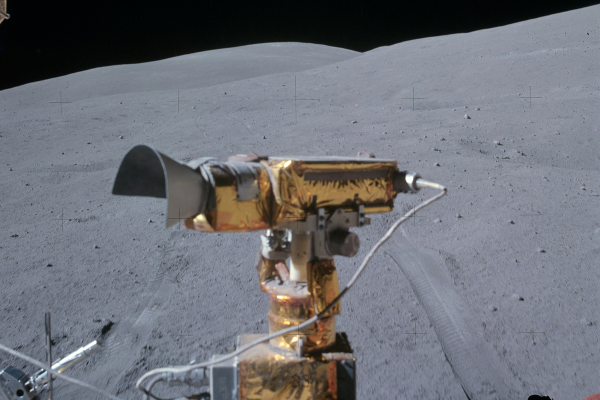
Although film was still commonly used into the 1980s, with movies and even entire television series such as Star Trek: The Next Generation being recorded on film, the main weakness of film is the need to move the physical film around. Imagine the live video feed from the Moon in 1969 if only film-based video recorders had been a thing.

Let’s look at the video camera tube: the almost forgotten technology that enabled the broadcasting industry. Continue reading “Recording Video In The Era Of CRTs: The Video Camera Tube”

Parking Meters That Were A Bit Too Smart For Their Own Good

A common sight in automobile-congested cities such as New York are parking meters lining the curbs next to parking spots. They’re an autonomous way for the city to charge for the space taken by cars parked along the sidewalk near high-traffic commercial areas, incentivizing people to wrap up their business and move their vehicle out of a costly or time-limited parking space.

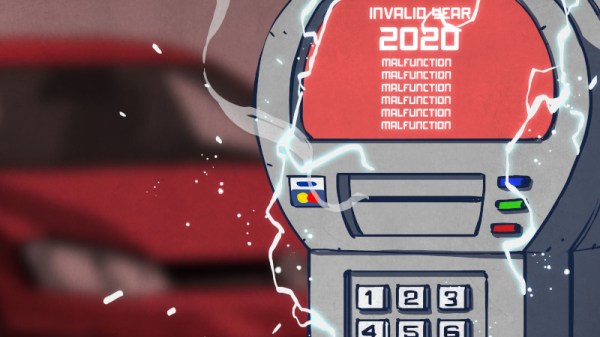
The parking meter is such a mundane device most people wouldn’t look at them twice, but on the inside it’s fascinating to see how they’re engineered, how that’s changed through the years, and how a software bug handicapped thousands of digital meters at the start of 2020.

The Origin Of The Parking Meter

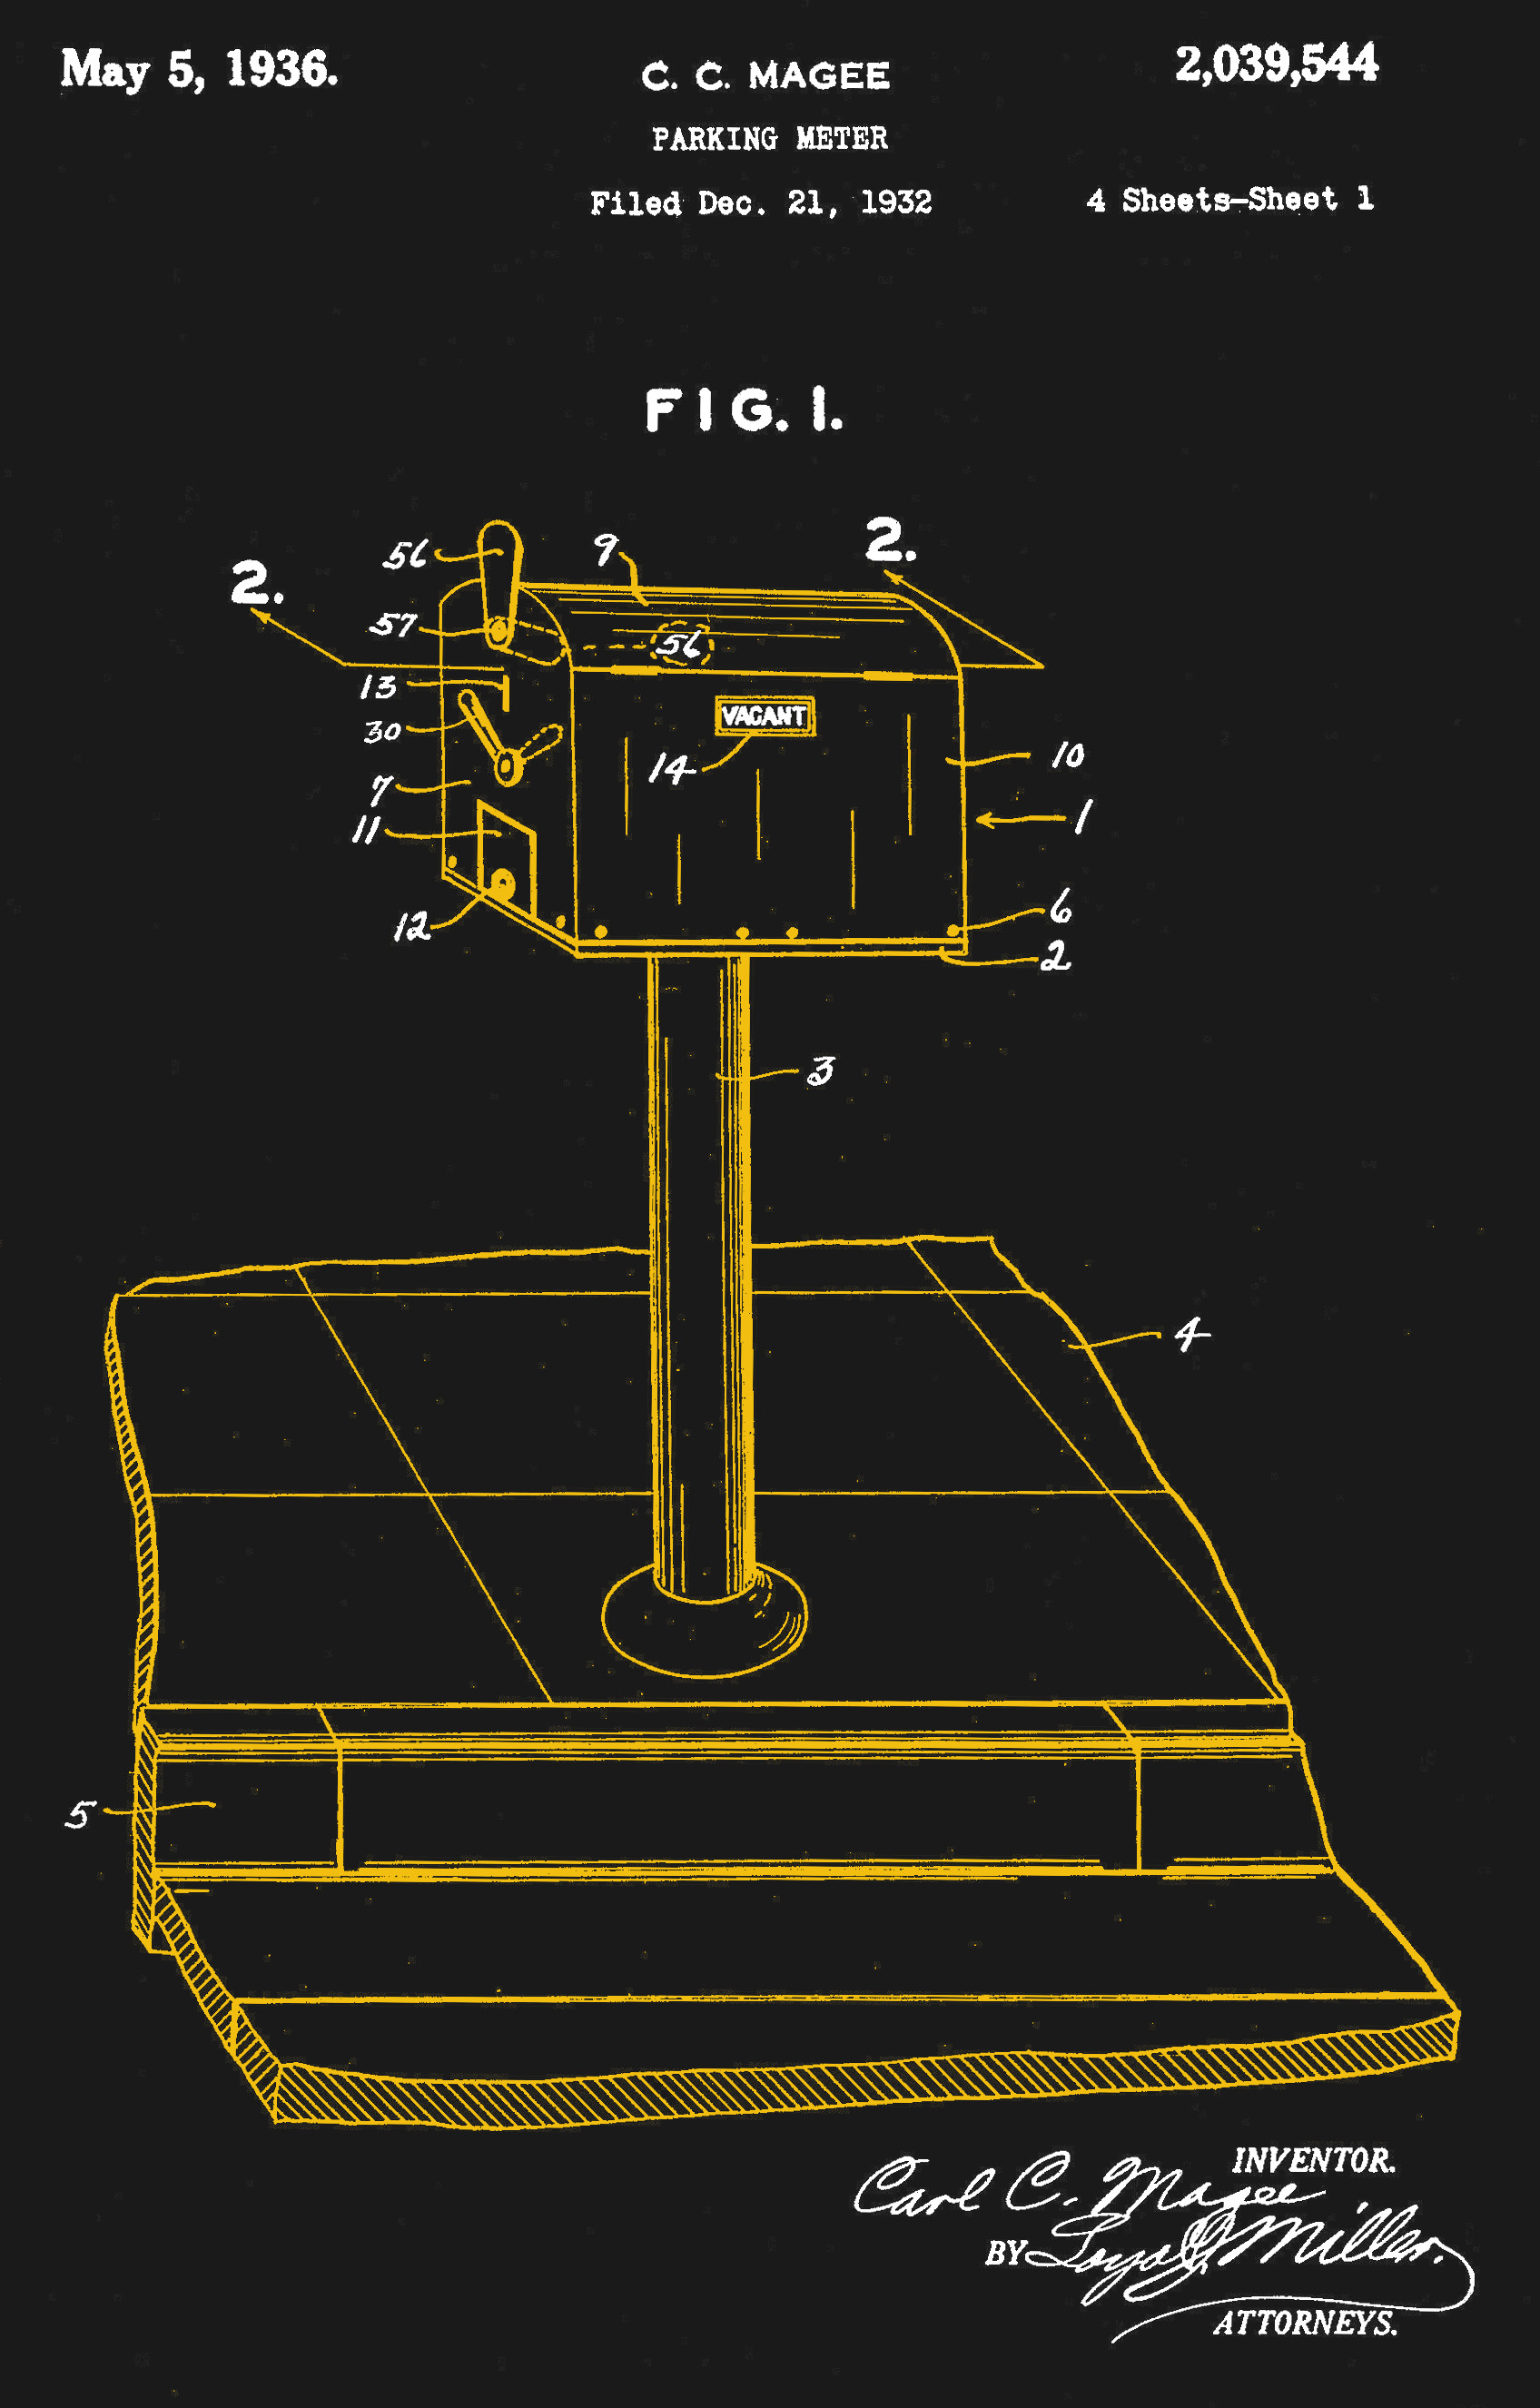
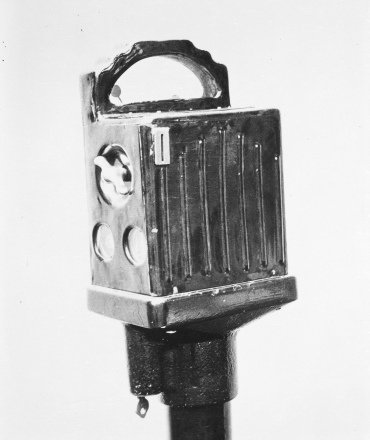
One of Carl C. Magee’s earliest parking meter designs, filed for patent in 1932.

Parking meters were originally commissioned in the 1930s by the government of Oklahoma City, due to the rapidly increasing number of automobiles, and therefore demand for parking space. Up until then, the city used patrolling policemen to regulate parking space, but they couldn’t keep up with the pace of the increased traffic and the lack of available parking space made business drop around downtown shops.

The first widely-adopted parking meter was dubbed “Black Maria”, a machine patented in 1935 by Carl C. Magee and Gerald Hale and first installed in the city in July of that year. This was a completely automated mechanical device made to solve the problem of regulating the time a driver can park their car in a given spot. It would take a nickel as payment, inserted into the mechanism by rotating a handle which also served to wind a clock spring. This clock would then tick down the remaining time the user could remain parked there, which could range from 15 minutes to an hour depending on the location.

An early Black Maria design, circa 1933.

Within days store owners noticed a positive effect in their profits thanks to the increase in customers with the regulated parking. What’s more, the coins collected from the meters also generated revenue for the city, and so, parking meters started spreading throughout the city. And as decades went, the mechanics were improved upon. A window was added into which a patrolling officer could easily look to check if the right amount of money (or money at all) was inserted. Separate panels for the coins to be easily collected without risking damage to the rest of the internal clockwork were also added.

The evolution of parking meters eventually passed through meters that could take care of parking spaces on either side of it, halving the amount of necessary poles per sidewalk. Electronic models starting appearing in the 1990s and eventually connectivity added. With meters all hooked up to the same network, the symbiotic connection between the parking meter and your spot was severed. It didn’t matter where your car was parked anymore; you could simply take your printed ticket and put it on your dashboard to be legally parked. Further advancements led to numbers spots that can be paid from any kiosk in the city, or though a smartphone app. But those digital advancements don’t always translate into reliability…

Continue reading “Parking Meters That Were A Bit Too Smart For Their Own Good”

A Farewell To Hackaday’s Favorite Falcon 9 Booster

With the notable exception of the Space Shuttle, rockets and spacecraft have always been considered disposable. It’s a slow and expensive way to travel, akin to building a new airliner for every flight, but it was the easiest option. These vehicles have always represented the pinnacle of engineering and material science of their time, and just surviving the trip to space once was an incredible accomplishment. To have another go around would have been asking too much of the technology. Even looking back on the Space Shuttle program, there’s plenty of debate about whether or not the reusable design really paid off in the end.

So SpaceX’s ability to land, refurbish, and refly the first stage of their Falcon 9 booster is no small accomplishment. After demonstrating the idea was possible in 2017, the company made numerous changes to the latest iteration of the rocket with reusability in mind. Known as Block 5, this version of the Falcon 9 is designed to be more survivable and require minimal servicing between flights. The company says its cheaper and faster to reuse the Block 5 than it would be to build a new one for each flight, allowing the company to approach spaceflight more like commercial aviation.

Falcon 9 launch and landing streaks
Falcon 9 launch and landing streaks. (Source: SpaceX)

With a fleet of Block 5 boosters now in rotation, SpaceX has given them serial numbers not unlike an airplane’s tail number. It might not be the kind of thing the general public would normally be aware of, but these serial numbers have allowed a dedicated community of space aficionados to keep track of the missions each booster has flown.

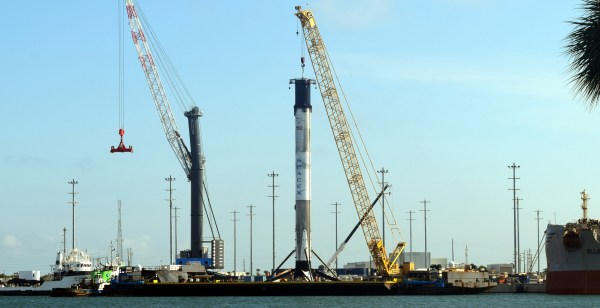
Unfortunately the story of one of these rockets, officially referred to as “Cores” in SpaceX parlance, was recently cut short. Core B1056, returning from the Starlink 4 mission on February 17th, failed to land on the autonomous spaceport drone ship (ASDS) Of Course I Still Love You and splashed down in the ocean. It’s still unclear what condition the booster was in after its soft landing in the water, but when the recovery ships returned to port empty handed, there was no question as to the fate of B1056.

From a purely business standpoint, the failure of any of SpaceX’s boosters means lost time and revenue. But in some ways B1056 had established itself as the vanguard of the fleet, managing to either set or break a number of records in its relatively short life. The destruction of the most thoroughly flight proven Block 5 booster is a stark reminder that there’s very little about spaceflight that could be called routine.

Continue reading “A Farewell To Hackaday’s Favorite Falcon 9 Booster”

New Part Day: Ooh, The Things You Can Do With A CLUE

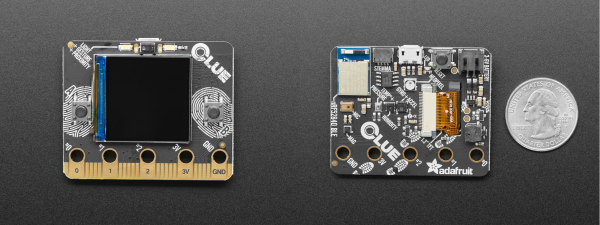
There’s a new development board in town from Adafruit, and it’s called the CLUE. This tiny board can be programmed in Arduino or CircuitPython, and it is absolutely stuffed with sensors and functionality, including Bluetooth. It’s essentially a BBC Micro:bit with more sensors, a screen, and a much beefier processor. Sound interesting? Let’s get out the magnifying glass and take a look, shall we?

(Editor’s note: Adafruit ran out of the first alpha run of the hardware. While we didn’t run into any bugs, the next versions will presumably have even fewer, but will also cost $40 instead of $30. That said, they’re giving out 3,000 of them to attendants of PyCon in April, so you might also get your hands on one that way.)

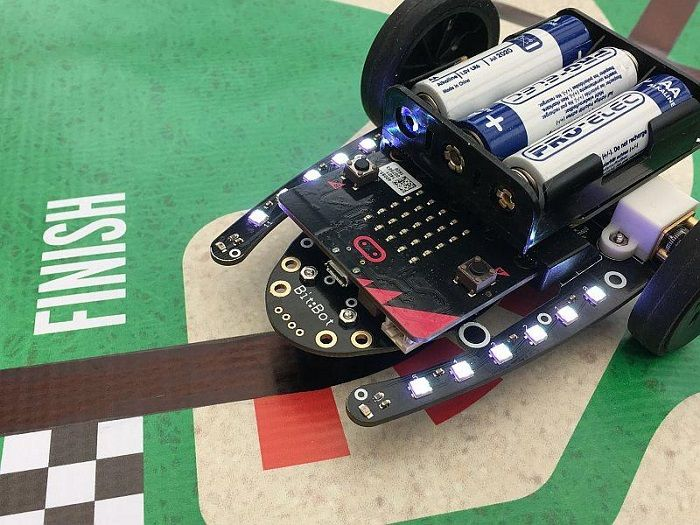
And Bit:Bot takes the checkered flag! Image via Seeed Studio

First and foremost, there’s the form factor — if that bottom edge looks familiar, that’s because the CLUE is designed to work with micro:bit robot kits and anything else with that edge connector, like the CRICKIT for micro:bit, or the Bit:Bot from Seeed Studios. This is big news for the micro:bit ecosystem, and not just because the CLUE brings tons of sensors and a screen to the scene, although a 1.3″ screen at 240×240 resolution is nothing to sneeze at.

The main brain is a Nordic nRF52840, so you can pair it to your phone and stream your collected data. Or, use it to get two CLUE boards talking to each other. This is a major upgrade from the micro:bit’s nRF51822 — the CLUE is four times faster, has four times the flash memory, and has sixteen times as much RAM. We hope someone can find a way to make them into short-range messaging machines with Q10 keyboards.

Continue reading “New Part Day: Ooh, The Things You Can Do With A CLUE”