This Week In Security: What’s Up With Whatsapp, Windows XP Patches, And Cisco Is Attacked By The Thrangrycat

Whatsapp allows for end-to-end encrypted messaging, secure VoIP calls, and until this week, malware installation when receiving a call. A maliciously crafted SRTCP connection can trigger a buffer overflow, and execute code on the target device. The vulnerability was apparently found first by a surveillance company, The NSO Group. NSO is known for Pegasus, a commercial spyware program that they’ve marketed to governments and intelligence agencies, and which has been implicated in a number of human rights violations and even the assassination of Jamal Khashoggi. It seems that this Whatsapp vulnerability was one of the infection vectors used by the Pegasus program. After independently discovering the flaw, Facebook pushed a fixed client on Monday.

Windows XP Patched Against Wormable Vulnerability

What year is it!? This Tuesday, Microsoft released a patch for Windows XP, five years after support for the venerable OS officially ended. Reminiscent of the last time Microsoft patched Windows XP, when Wannacry was the crisis. This week, Microsoft patched a Remote Desktop Protocol (RDP) vulnerability, CVE-2019-0708. The vulnerability allows an attacker to connect to the RDP service, send a malicious request, and have control over the system. Since no authentication is required, the vulnerability is considered “wormable”, or exploitable by a self-replicating program.

Windows XP through Windows 7 has the flaw, and fixes were rolled out, though notably not for Windows Vista. It’s been reported that it’s possible to download the patch for Server 2008 and manually apply it to Windows Vista. That said, it’s high time to retire the unsupported systems, or at least disconnect them from the network.

The Worst Vulnerability Name of All Time

Thrangrycat. Or more accurately, “😾😾😾” is a newly announced vulnerability in Cisco products, discovered by Red Balloon Security. Cisco uses secure boot on many of their devices in order to prevent malicious tampering with device firmware. Secure boot is achieved through the use of a secondary processor, a Trust Anchor module (TAm). This module ensures that the rest of the system is running properly signed firmware. The only problem with this scheme is that the dedicated TAm also has firmware, and that firmware can be attacked. The TAm processor is actually an FPGA, and researchers discovered that it was possible to modify the FPGA bitstream, totally defeating the secure boot mechanism.

The name of the attack, thrangrycat, might be a satirical shot at other ridiculous vulnerability names. Naming issues aside, it’s an impressive bit of work, numbered CVE-2019-1649. At the same time, Red Balloon Security disclosed another vulnerability that allowed command injection by an authenticated user.

Odds and Ends

See a security story you think we should cover? Drop us a note in the tip jar!
Integrated Circuits Can Be Easy To Understand With The Right Teachers

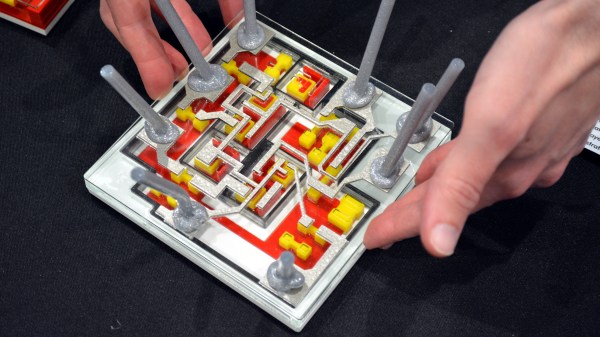
For years I’ve been trying to wrap my mind around how silicon chips actually work. How does a purposefully contaminated shard of glass wield control over electrons? Every once in a while, someone comes up with a learning aid that makes these abstract concepts really easy to understand, and this was the case with one of the booths at Maker Faire Bay Area. In addition to the insight it gave me (and hundreds of Faire-goers), here is an example of the best of what Maker Faire stands for. You’ll find a video of their presentation embedded below, along with closeup images of the props used at the booth.

The Uncovering the Silicon booth had a banner and a tablecloth, but was otherwise so unassuming that many people I spoke with missed it. Windell Oskay, Lenore Edman, Eric Schlepfer, John McMaster, and Ken Shirriff took a 50-year-old logic chip and laid it bare for anyone who cared to stop and ask what was on display. The Fairchild μL914 is a dual NOR gate, and it’s age matters because the silicon is not just simple, it’s enormous by today’s standards making it relatively easy to peer inside with tools available to the individual hacker.

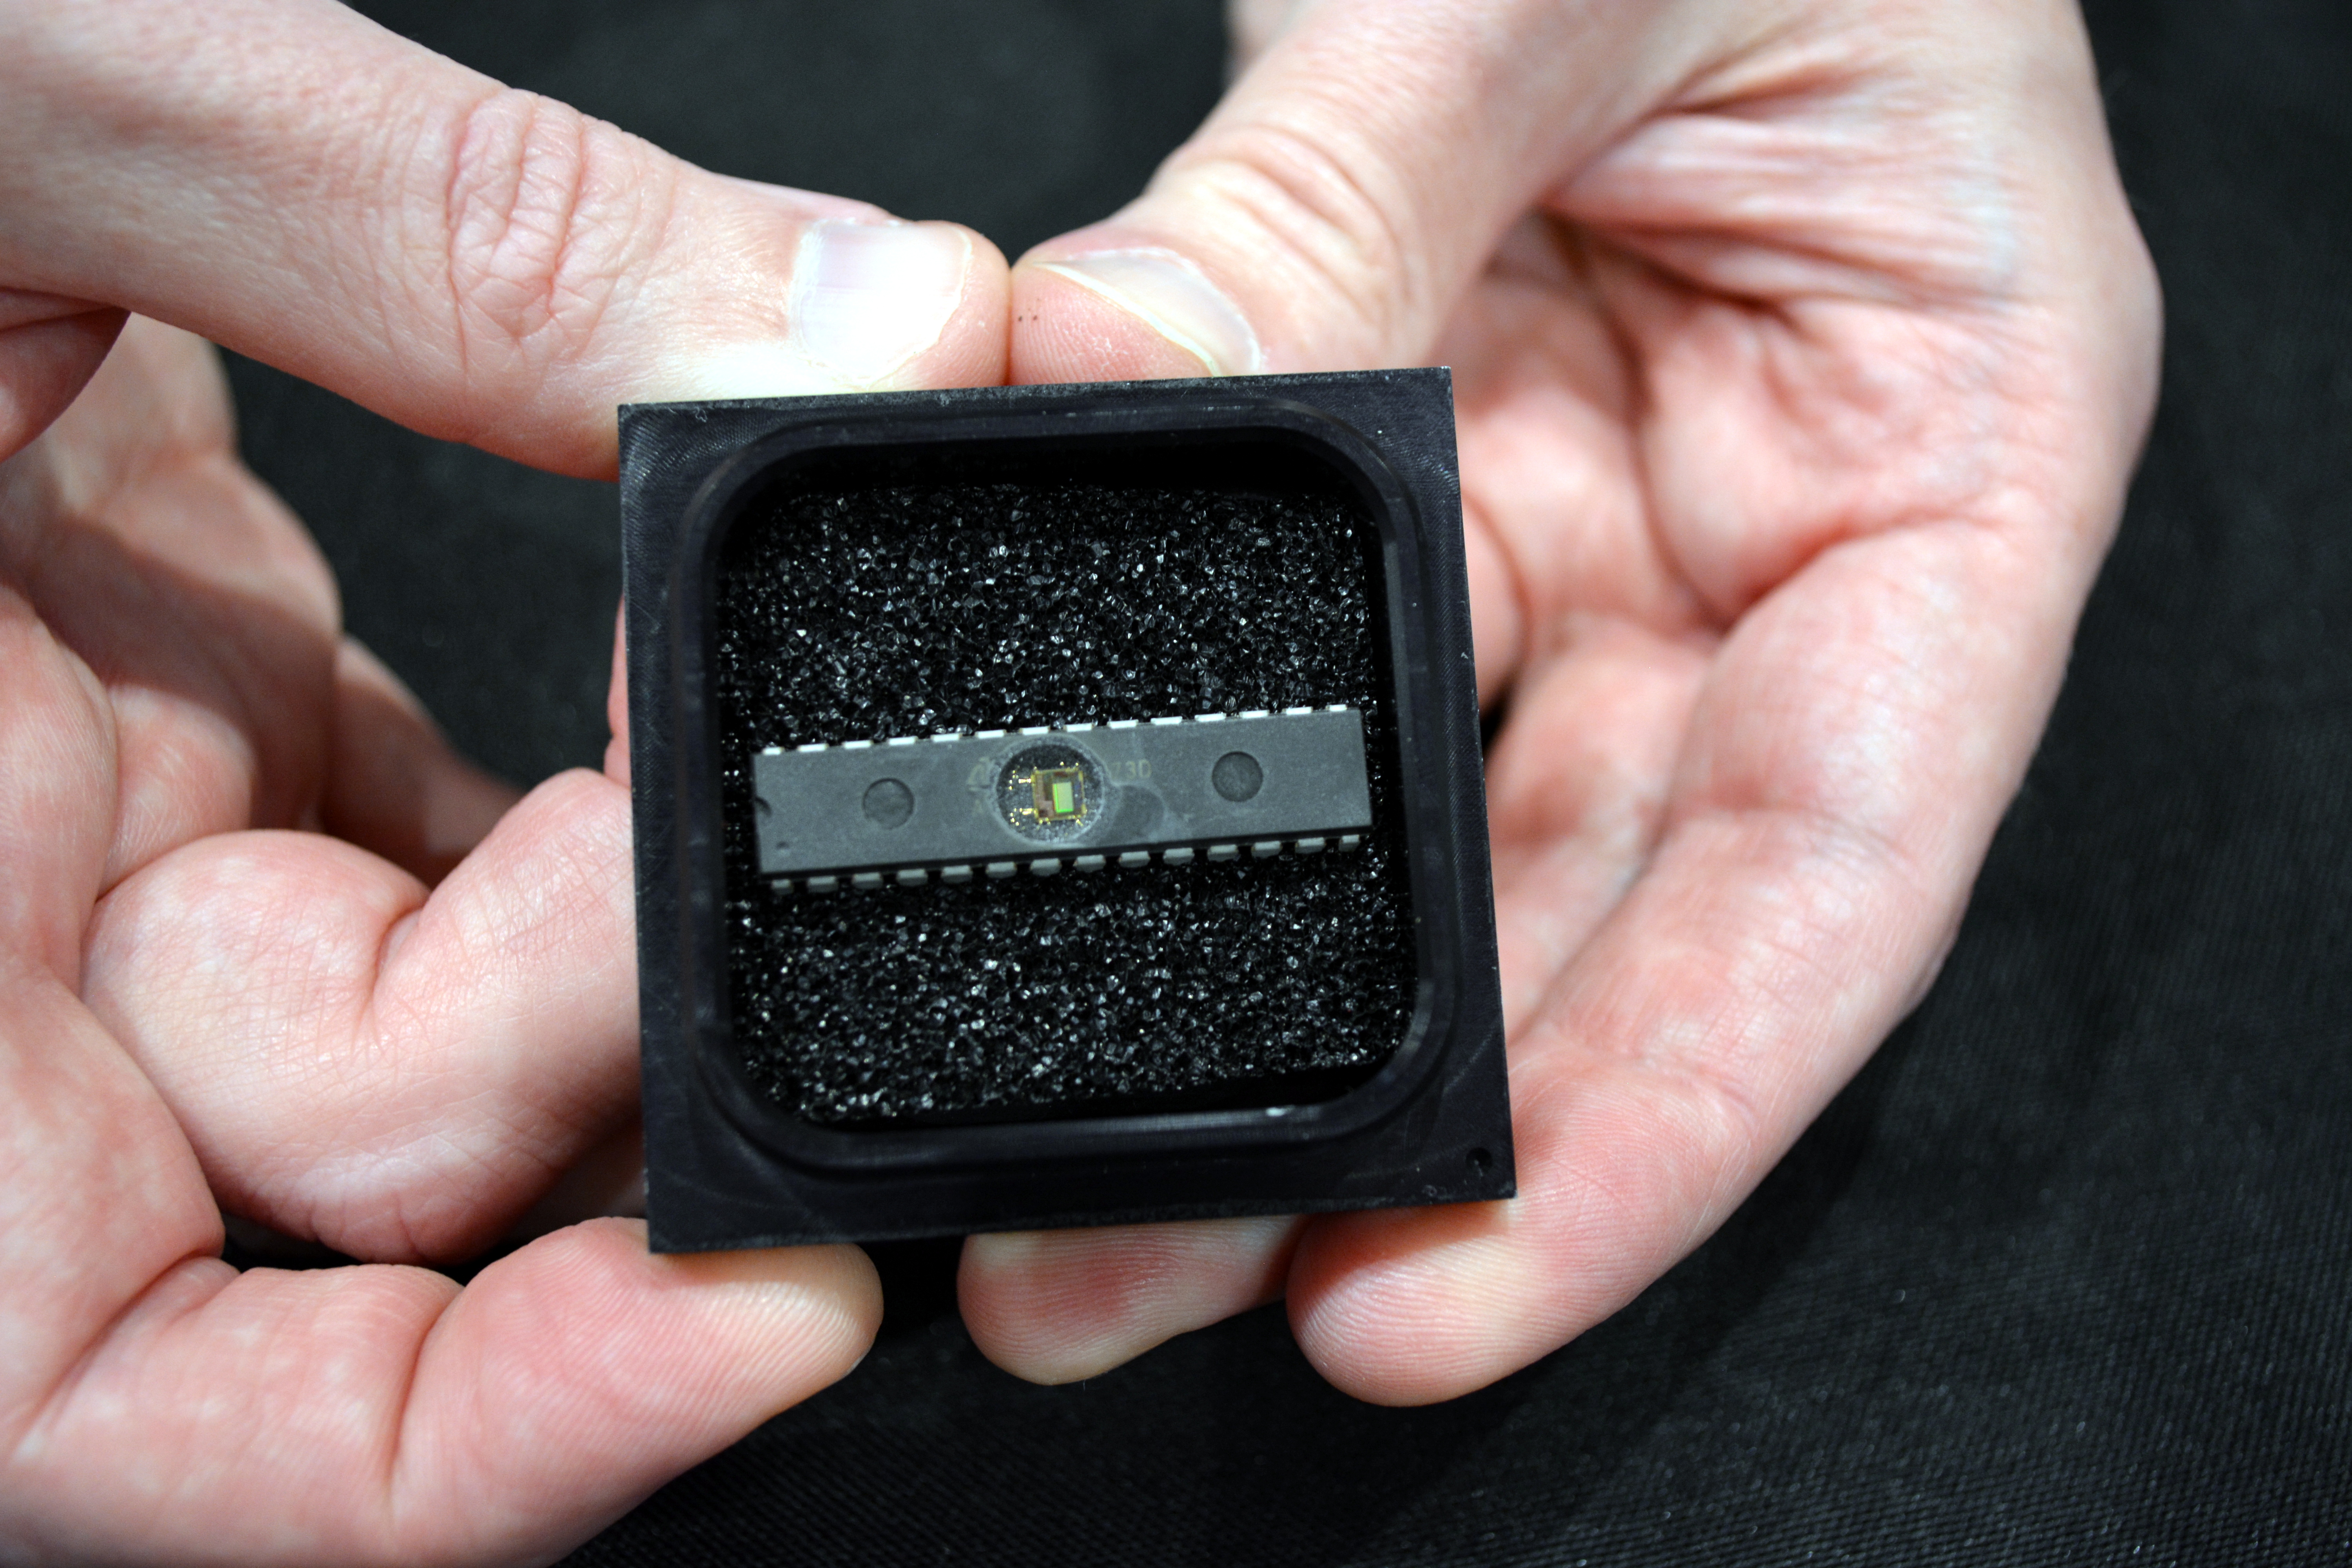
ATmega328 decapped by John McMaster was also on display at this booth

The first challenge is just getting to the die itself. This is John McMaster’s specialty, and you’re likely familiar from his Silicon Pr0n website. He decapped the chip (as well as an ATmega328 which was running the Arduino blink sketch with it’s silicon exposed). Visitors to the booth could look through the microscope and see the circuit for themselves. But looking doesn’t mean understanding, and that’s where this exhibit shines.

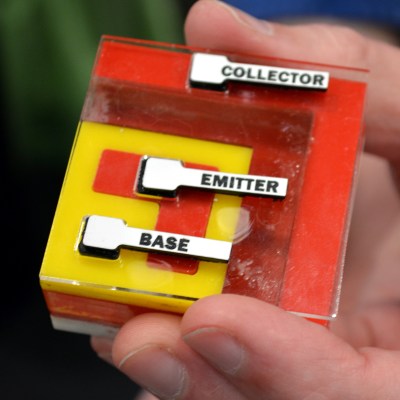
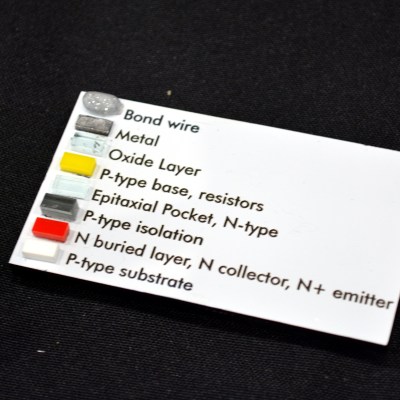
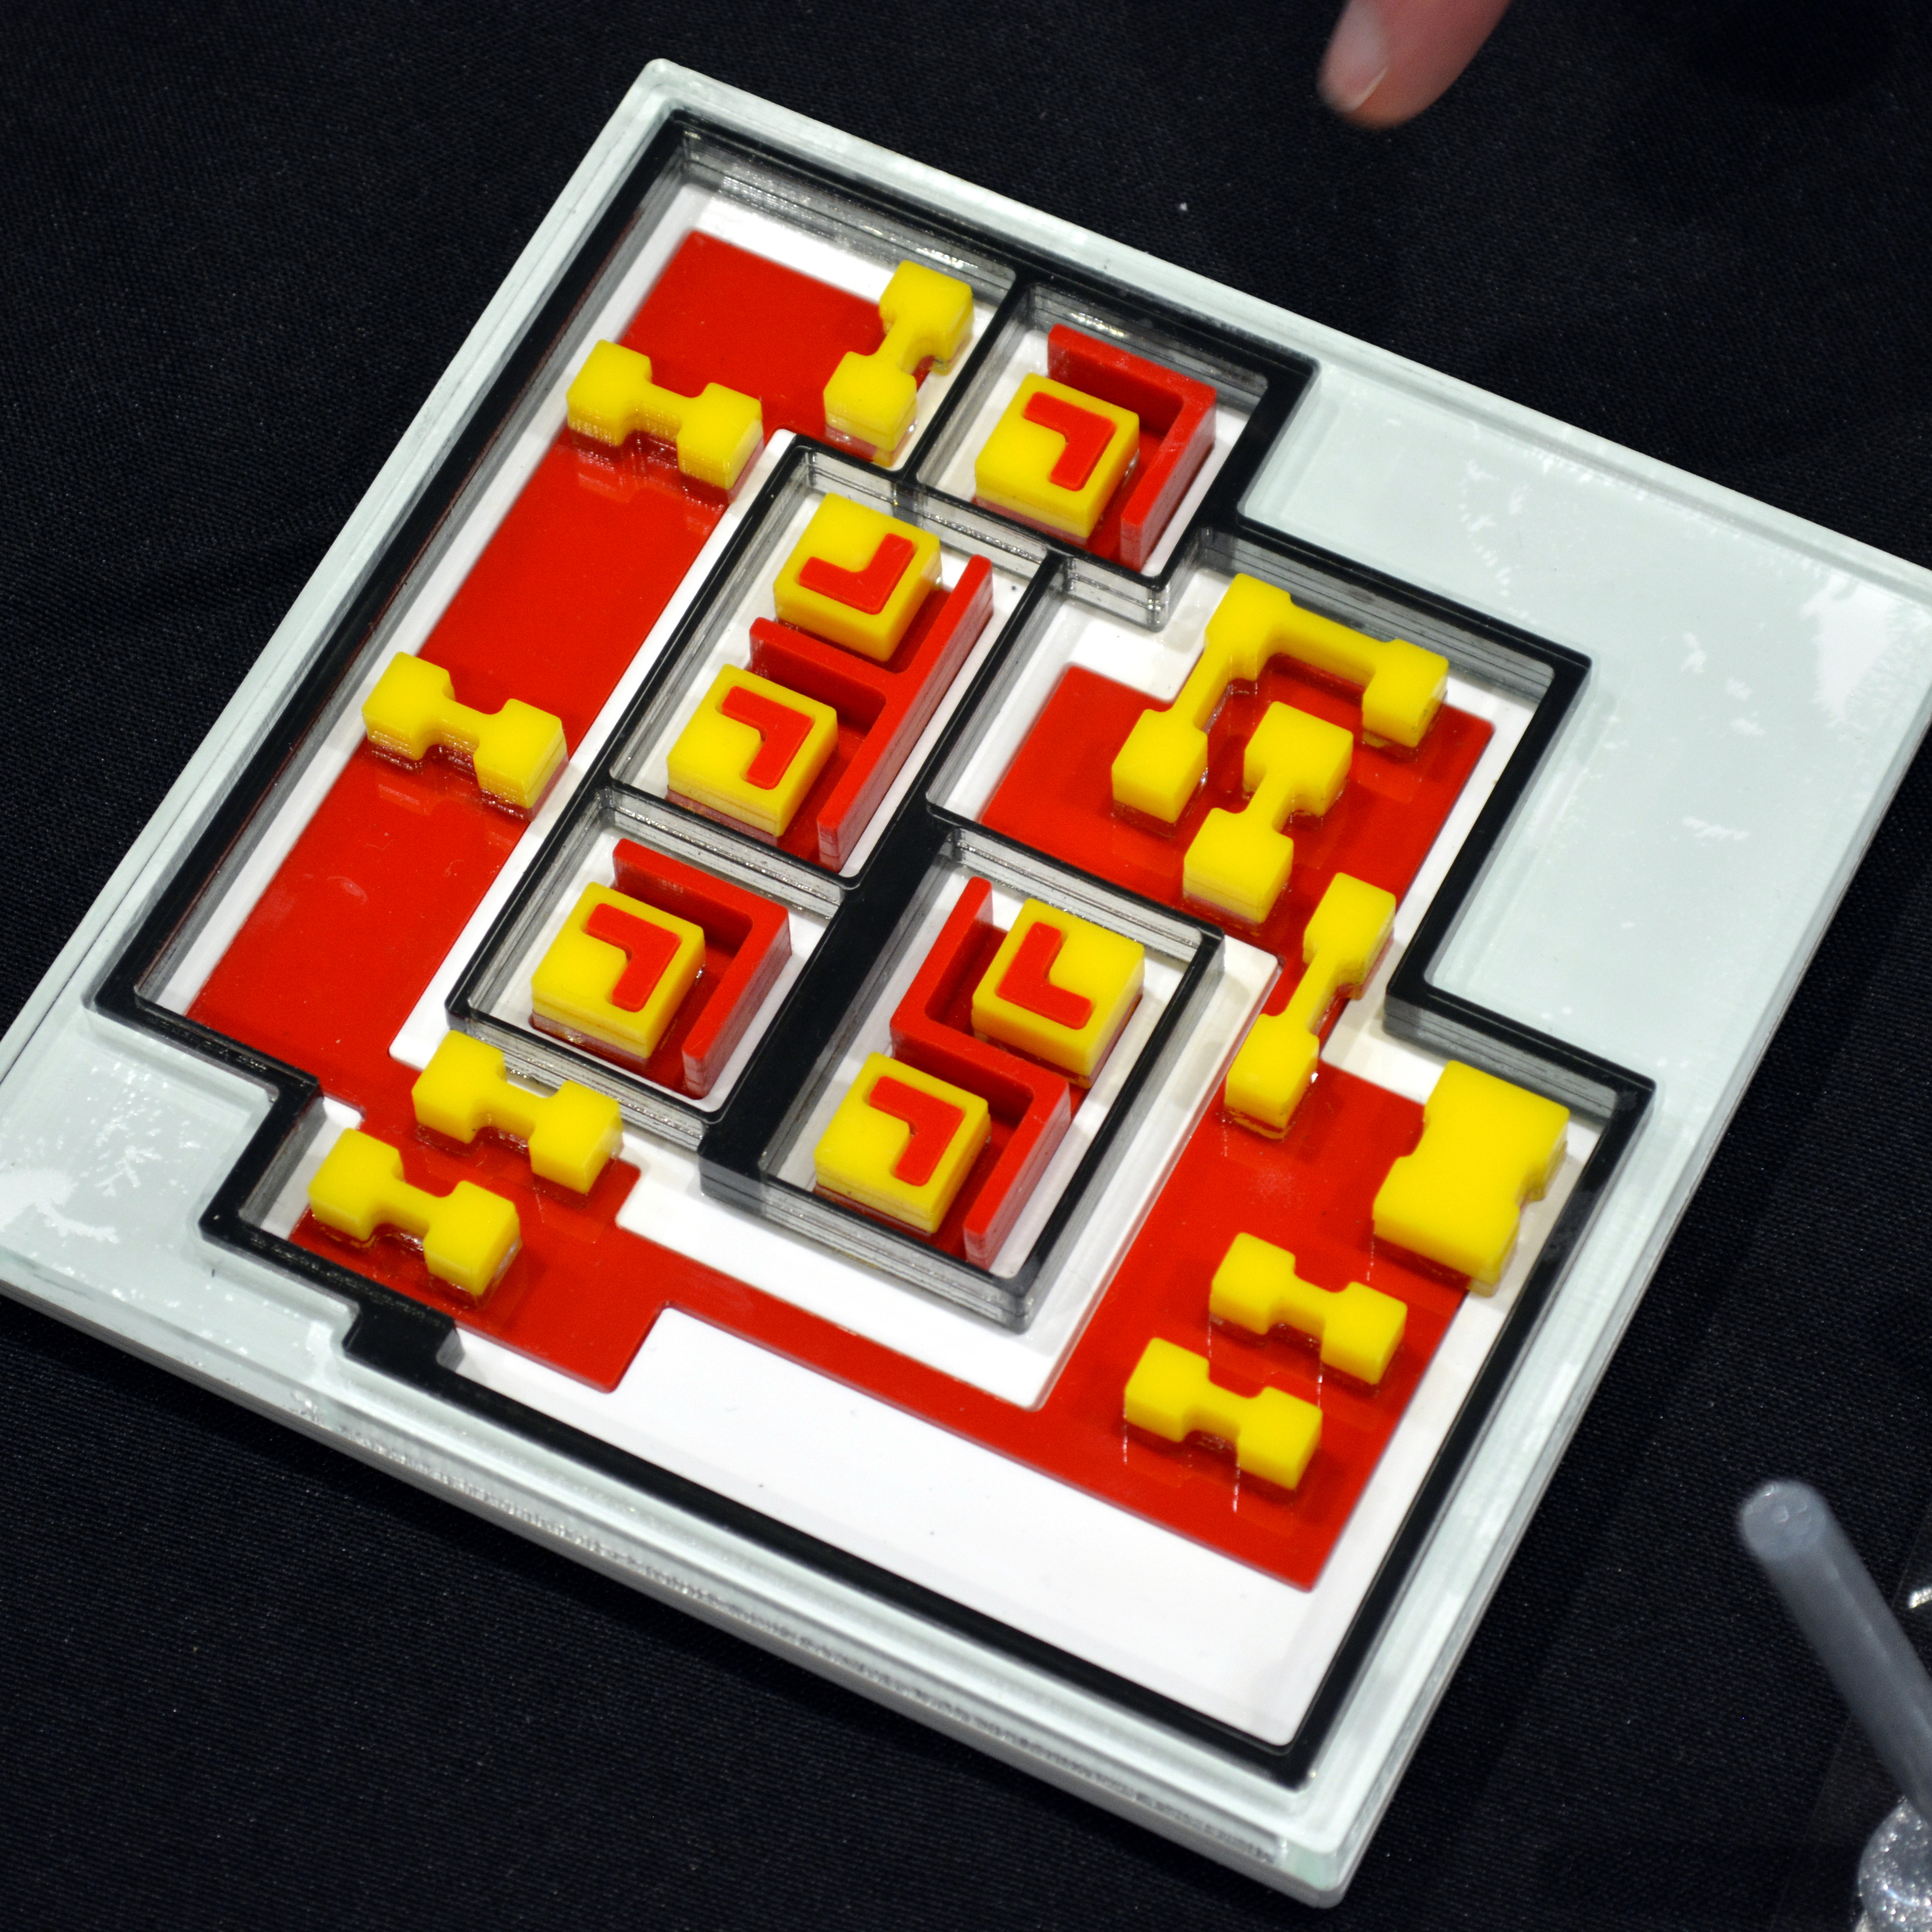
To walk us through how this chip works, a stack-up of laser-cut acrylic demonstrates the base, emitter, and collector of a single transistor. The color coding and shape of this small model makes it easy to pick out the six transistors of the 941 on a full model of the chip. This lets you begin to trace out the function of the circuit.

For me, a real ah-ha moment was the resistors in the design. A resistive layer is produced by doping the semiconductor with impurities, making it conduct more poorly. But how do you zero-in on the desired resistance for each part? It’s not by changing the doping, that remains the same. The trick is to make the resistor itself take up a larger footprint. More physical space for the electrons to travel means a lower resistance, and in the model you can see a nice fat resistor in the lower right. The proof for these models was the final showpiece of the exhibit as the artwork of the silicon die was laid out as a circuit board with discrete transistors used to recreate the functionality of the original chip.

Windell takes us through the booth presentation in the video below. I think you’ll be impressed by the breakdown of these concepts and how well they aid in understanding. This was a brilliant concept for an exhibit; it brought together interdisciplinary experts whom I respect and whose work I follow, and sought to invite everyone to gain a better understanding of the secrets hiding in the chips that underpin this technological age. This is exactly the kind of thing I love to see at a Maker Faire.

Continue reading “Integrated Circuits Can Be Easy To Understand With The Right Teachers” →

That Super Mario Bros. C64 Port Was Too Good For This World

It was foolish to think that the adventure of the Mario Bros. would ever exist outside of the castle walls of the Nintendo Entertainment System. Except for that one time it did. The Hudson Soft company was a close collaborator with Nintendo, and parlayed that favor into being tasked with bringing Super Mario Bros. to platforms beyond the NES. The result of that collaboration would be 1986’s Super Mario Special, a port for the NEC PC-88 line of desktop computers. What ended up on that 5.25″ floppy sounded reminiscent of the Famicom original, but with a grand total of four colors (including black) and not a single scrolling screen in sight; Super Mario Special felt decidedly less than spectacular to play. Those eternally flickering sprites mixed with jarring blank screen transitions would never make it outside of Japan, so for a large swath of the world Mario would remain constrained to a gray plastic cartridge for years to come.

There are no shortage of ways to play Super Mario Bros. these days. Emulation in all of its various official and unofficial forms has taken care of that. Virtually everything with a processor more capable than the NES’s 6502 can play host to the Mushroom Kingdom, however, machines more contemporary with the NES still lacked access to the iconic title.

Enter the 2019 port of Super Mario Bros. for the Commodore 64 by [ZeroPaige]. A culmination of seven years work to port the game onto one of the most prolific computers of the eighties was a clear feat of brilliance and an amazing bit of programming that would have taken 1986 by storm. No pale imitation, this was Mario on the C64. Despite all of the nuance in recreating the jump-and-run model of the original paired with enveloping all eight sound channels of a dual SID chip setup, Nintendo saw fit to stifle the proliferation of this incredible 170 kB of software because they claim it infringes on their copyright.

Continue reading “That Super Mario Bros. C64 Port Was Too Good For This World” →

Repairing A Catastrophic Failure: The Oroville Dam Update

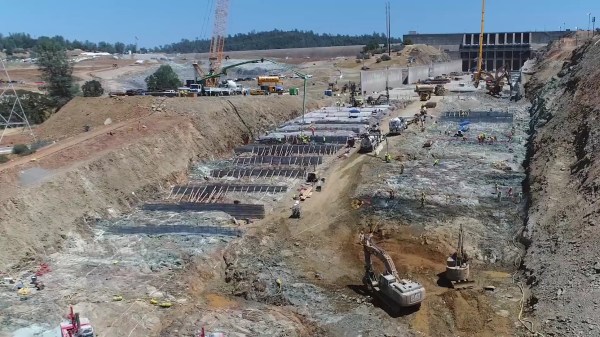
More than two years ago, the largest dam in the United States experienced a catastrophic failure of its main spillway, the primary means by which operators of the dam prevent the lake from cresting its pen. The spillway failure caused so much erosion that the hydroelectric plant could not operate, further worsening the situation. In a few days, the dam was finally put to its design limitations, and water began flowing down an emergency spillway that had never been used, prompting the evacuation of 188,000 people living in downstream communities.

Since the time that this crisis came to a head, crews have been working around the clock to repair the main and emergency spillways in order to ensure that one of the largest pieces of infrastructure in the wealthiest country in the world does not suffer a complete failure. The dam’s spillways were reopened recently on April 2, in time for this year’s snow melting, and so far everything looks good.

The repair work was a true feat of engineering, and perhaps a logistics miracle as well. The video below goes over a lot of the raw materials inputs that were needed, but the one that stuck out the most was that a dump truck full of roller-compacted concrete was emptied every five minutes over the entire course of the repair — enough to build a sidewalk from the Oroville Dam to Texas. Part of the reason for the use of such an incredible amount of concrete was that it wasn’t just used to repair the main spillway. An enormous “splash pad” for the emergency spillway was also constructed to limit erosion in the event that it must be used again. But the full change goes beyond concrete and rebar. Join me after the break as I try to wrap my mind around the full scope of the Oroville Dam repair.

Continue reading “Repairing A Catastrophic Failure: The Oroville Dam Update” →

Fun With Negative Resistance II: Unobtanium Russian Tunnel Diodes

In the first part of this series, we took a look at a “toy” negative-differential-resistance circuit made from two ordinary transistors. Although this circuit allows experimentation with negative-resistance devices without the need to source rare parts, its performance is severely limited. This is not the case for actual tunnel diodes, which exploit quantum tunneling effects to create a negative differential resistance characteristic. While these two-terminal devices once ruled the fastest electronic designs, their use has fallen off dramatically with the rise of other technologies. As a result, the average electronics hacker probably has never encountered one. That ends today.

Due to the efficiencies of the modern on-line marketplace, these rare beasts of the diode world are not completely unobtainable. Although new-production diodes are difficult for individuals to get their hands on, a wide range of surplus tunnel diodes can still be found on eBay for as little as $1 each in lots of ten. While you’d be better off with any number of modern technologies for new designs, exploring the properties of these odd devices can be an interesting learning experience.

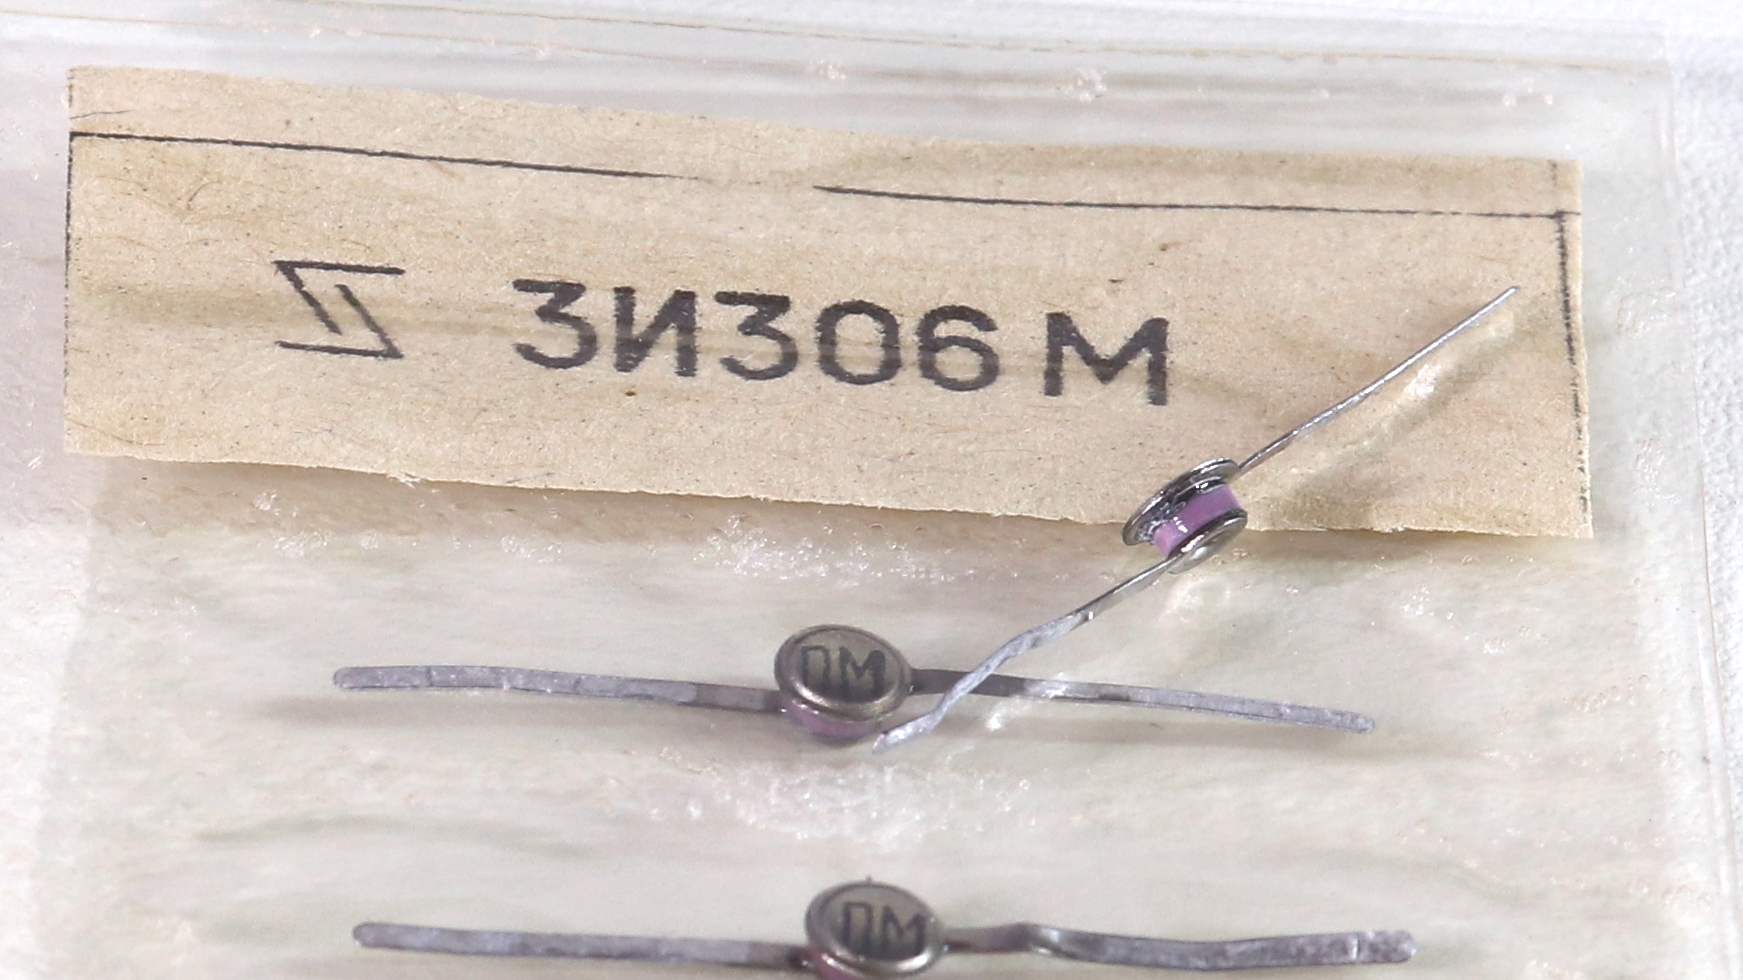
For this installment, I dug deep into my collection of semiconductor exotica for some Russian 3И306M gallium arsenide tunnel diodes that I purchased a few years ago. Let’s have a look at what you can do with just a diode — if it’s the right kind, that is.

[Note: the images are all small in the article; click them to get a full-sized version]

Continue reading “Fun With Negative Resistance II: Unobtanium Russian Tunnel Diodes” →

It Is ‘Quite Possible’ This Could Be The Last Bay Area Maker Faire

The Bay Area Maker Faire is this weekend, and this might be the last one. This report comes from the San Francisco Chronicle, and covers the continuing problems of funding and organizing what has been called The Greatest Show and Tell on Earth. According to Maker Media CEO Dale Dougherty, “it is ‘quite possible’ that the event could be the Bay Area’s last Maker Faire.”

Maker Faire has been drawing artists, craftspeople, inventors, and engineers for more than a decade. In one weekend you can see risque needlepoint, art cars meant for the playa, custom racing drones, science experiments, homebrew computers, gigantic 3D printers, interactive LED art, and so much more. This is a festival built around a subculture defined by an act of creation; if you do something with your hands, if you build something, or if you make something, Maker Faire has something for you. However you define it, this is the Maker Movement and since 2006, there has been a Maker Faire, a festival to celebrate these creators.

It’s sad to learn the future of this event is in peril. Let’s take a look at how we got here and what the future might hold.

Continue reading “It Is ‘Quite Possible’ This Could Be The Last Bay Area Maker Faire” →

The Great Ohio Key Fob Mystery, Or “Honey, I Jammed The Neighborhood!”

Hack long enough and hard enough, and it’s a pretty safe bet that you’ll eventually cause unintentional RF emissions. Most of us will likely have our regulatory transgression go unnoticed. But for one unlucky hacker in Ohio, a simple project ended up with a knock at the door by local authorities and pointed questions to determine why key fobs and garage door remotes in his neighborhood and beyond had suddenly been rendered useless, and why his house seemed to be at the center of the disturbance.

Few of us want this level of scrutiny for our projects, so let’s take a more in-depth look at the Great Ohio Key Fob Mystery, along with a look at the Federal Communications Commission regulations that govern what you can and cannot do on the airwaves. As it turns out, it’s easy to break the law, and it’s easy to get caught.

Continue reading “The Great Ohio Key Fob Mystery, Or “Honey, I Jammed The Neighborhood!”” →